How to integrate cve.now MCP with Hermes

Connect Hermes to cve.now MCP. Check lodash 4.17.20 for known vulnerabilities, look up cve-2024-3094 and summarize impact, and more using natural language, with authentication handled for you.

cve.now MCP logocve.now MCP
No Auth

cve.now is a free public vulnerability feed and lookup service for CVEs, GHSAs, OSVs, and package versions. It provides fast, exact vulnerability checks against an indexed catalog without requiring authentication.

3 Tools

Introduction

Hermes is a 24/7 autonomous agent that lives on your computer or server — it remembers what it learns and evolves as your usage grows.

This guide explains the easiest and most robust way to connect your cve.now account to Hermes. You can do this through either Composio Connect CLI or Composio Connect MCP. For personal use we recommend the CLI, but you won't go wrong with MCP either.

Also integrate cve.now MCP with

What is Composio Connect?

Composio Connect is a consumer offering that lets anyone plug 1,500+ applications directly into their agent harness — including Hermes. It can:

  • Search and load tools from relevant toolkits on-demand, reducing context usage.
  • Chain multiple tools to accomplish complex workflows via a remote workbench, without excessive back-and-forth with the LLM.
  • Manage app authentication end-to-end with zero manual overhead.

Integrating cve.now with Hermes

Using Composio Connect CLI

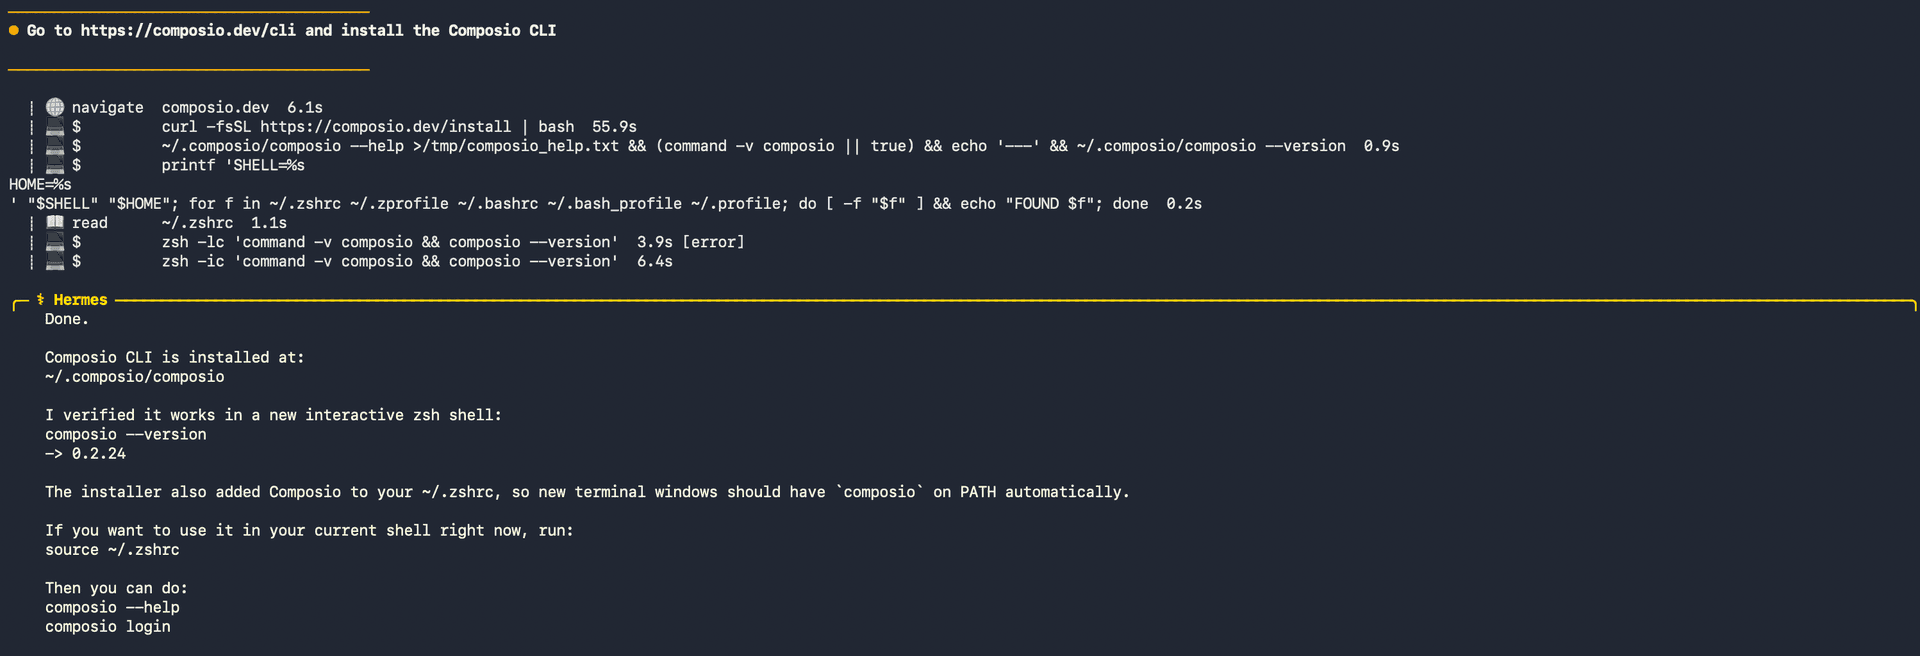
1. Install the Composio CLI

Run the install script directly, or paste https://composio.dev/hermes into your Hermes chat box to have it installed for you.

bash
curl -fsSL https://composio.dev/install | bash
Hermes authenticating with Composio

2. Authenticate

Once the CLI is installed, ask Hermes to authenticate with Composio.

3. Connect to cve.now

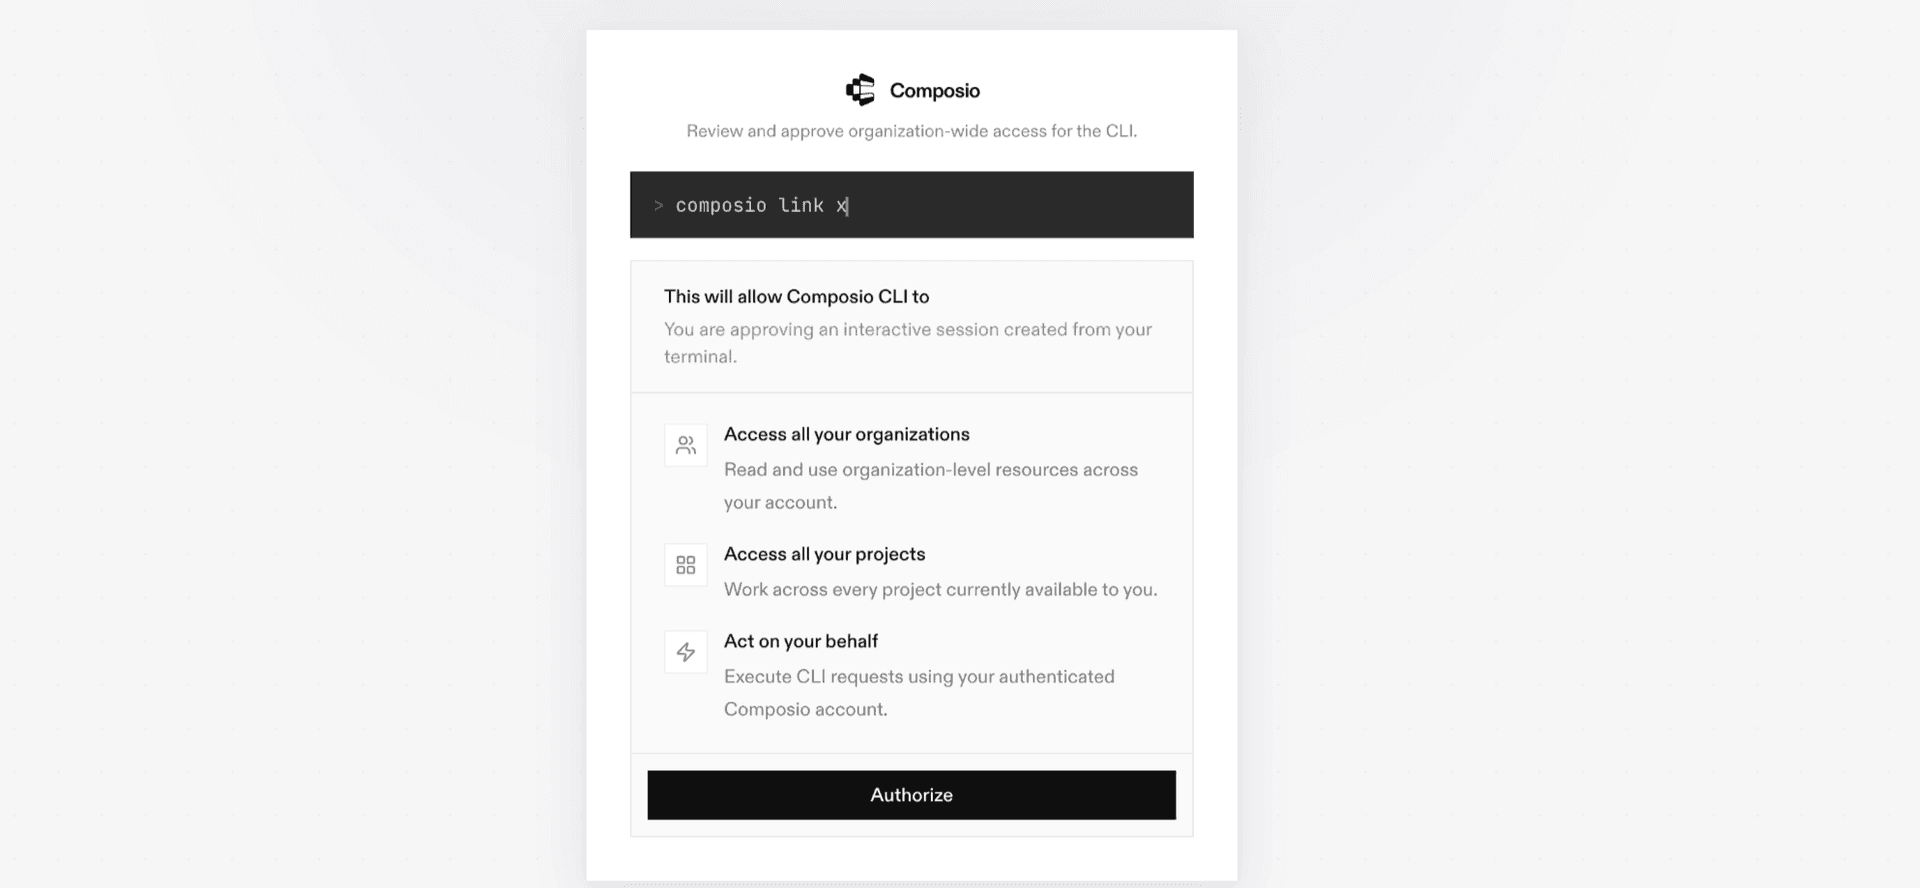
Ask your agent to connect to cve.now, or simply request any cve.now-related task. Hermes will prompt you to authenticate and authorize access.

4. Done. You're all set with a new cve.now connection.


Using Composio Connect MCP

1. Get your MCP URL and API Key

Go to dashboard.composio.dev and copy your Connect MCP URL and API key.

Copy MCP URL and API key from Composio dashboard

2. Open the Hermes config file

bash
nano ~/.hermes/config.yaml

3. Add the Composio Connect MCP server

bash
mcp_servers:
  composio:
    url: "https://connect.composio.dev/mcp"
    headers:
      x-consumer-api-key: "YOUR_COMPOSIO_API_KEY"
    connect_timeout: 60
    timeout: 180

Save with Ctrl + O, Enter, then exit with Ctrl + X.

4. Restart your Hermes agent

Once restarted, ask your agent to connect to cve.now or request any cve.now-related task. It will prompt you to authenticate and authorize access.

5. Done!

What is the cve.now MCP server, and what's possible with it?

The cve.now MCP server is an implementation of the Model Context Protocol that connects your AI agent and assistants like Claude, Cursor, etc directly to cve.now. It provides structured and secure access to vulnerability feeds, vulnerability records, and package-version checks, so your agent can check dependencies, look up CVE, GHSA, and OSV entries, review the newest feed items, and find vulnerabilities affecting a specific package version on your behalf.

  • Dependency vulnerability checks: Have your agent check a lockfile or package list against cve.now's indexed catalog and identify matching vulnerabilities for exact package versions.
  • Vulnerability lookups: Direct your agent to retrieve a vulnerability entry by its CVE, GHSA, or OSV reference.
  • Latest vulnerability feeds: Let the agent review new items from the critical, all, or KEV feeds to help track recently published risks.
  • Technology and ecosystem monitoring: Instruct your agent to list feed items for a specific technology or package ecosystem.
  • Responsible result interpretation: Have your agent explain that no catalog matches do not guarantee safety and distinguish model-written summaries from upstream vulnerability data.

Way Forward

With cve.now connected, Hermes can now act on your behalf whenever it detects a relevant task or you ask it to.

From here, you can extend Hermes further:

  • Connect more apps: Calendar, Slack, Notion, Linear, and hundreds of others are available through the same Composio Connect setup. Each new integration compounds what Hermes can do for you.
  • Build workflows across tools: Once multiple apps are connected, Hermes can chain actions together — turn an email into a calendar invite, a Slack message into a Linear ticket, or a meeting note into a follow-up draft.
  • Let it learn your patterns: The more you use Hermes, the better it gets at anticipating how you'd handle recurring tasks. Give it feedback on drafts and decisions, and it will adapt.

If you run into trouble or want to share what you've built, join the community or check out the Docs for deeper configuration options.

TOOLS

Supported Tools

Every cve.now MCP action and event your agent gets out of the box.

Check stack

Check exact package versions against cve.

Get vulnerability

Get one vulnerability entry by CVE, GHSA or OSV id, as JSON.

List feed

List the newest items in a cve.

FAQ

Frequently asked questions

With a standalone cve.now MCP server, the agents and LLMs can only access a fixed set of cve.now tools tied to that server. However, with the Composio Tool Router, agents can dynamically load tools from cve.now and many other apps based on the task at hand, all through a single MCP endpoint.

Yes, you can. Hermes fully supports MCP integration. You get structured tool calling, message history handling, and model orchestration while Tool Router takes care of discovering and serving the right cve.now tools.

Yes, absolutely. You can configure which cve.now scopes and actions are allowed when connecting your account to Composio. You can also bring your own OAuth credentials or API configuration so you keep full control over what the agent can do.

All sensitive data such as tokens, keys, and configuration is fully encrypted at rest and in transit. Composio is SOC 2 Type 2 compliant and follows strict security practices so your cve.now data and credentials are handled as safely as possible.

Start with cve.now MCP.It takes 30 seconds.

Managed auth, hosted MCP servers, and every cve.now MCP tool your agent needs.Free to start.

Start building