



Composio connects AI agents to Microsoft Word, helping teams turn documents into action. With Composio, developers can build agents that create, read, and update Word documents stored in OneDrive and SharePoint as part of automated workflows.
Access is always limited to the permissions approved during sign-in, so users stay in full control of what each agent can see and do.
This guide walks you through registering your own app in Microsoft Entra ID (Azure), generating OAuth credentials, and using them to set up a custom auth config for the Microsoft Word toolkit in Composio.
Part 1: Register your app in Microsoft Azure
In this section, we’ll register an application in the Azure portal and get the credentials Composio needs.
NOTE: If you already have an Azure app registration with the permissions below and access to its Client ID and Client Secret, you can skip this section.
Step 1: Create an App Registration
1. Sign in to the Azure portal. From the home page, open Microsoft Entra ID or search for App registrations.
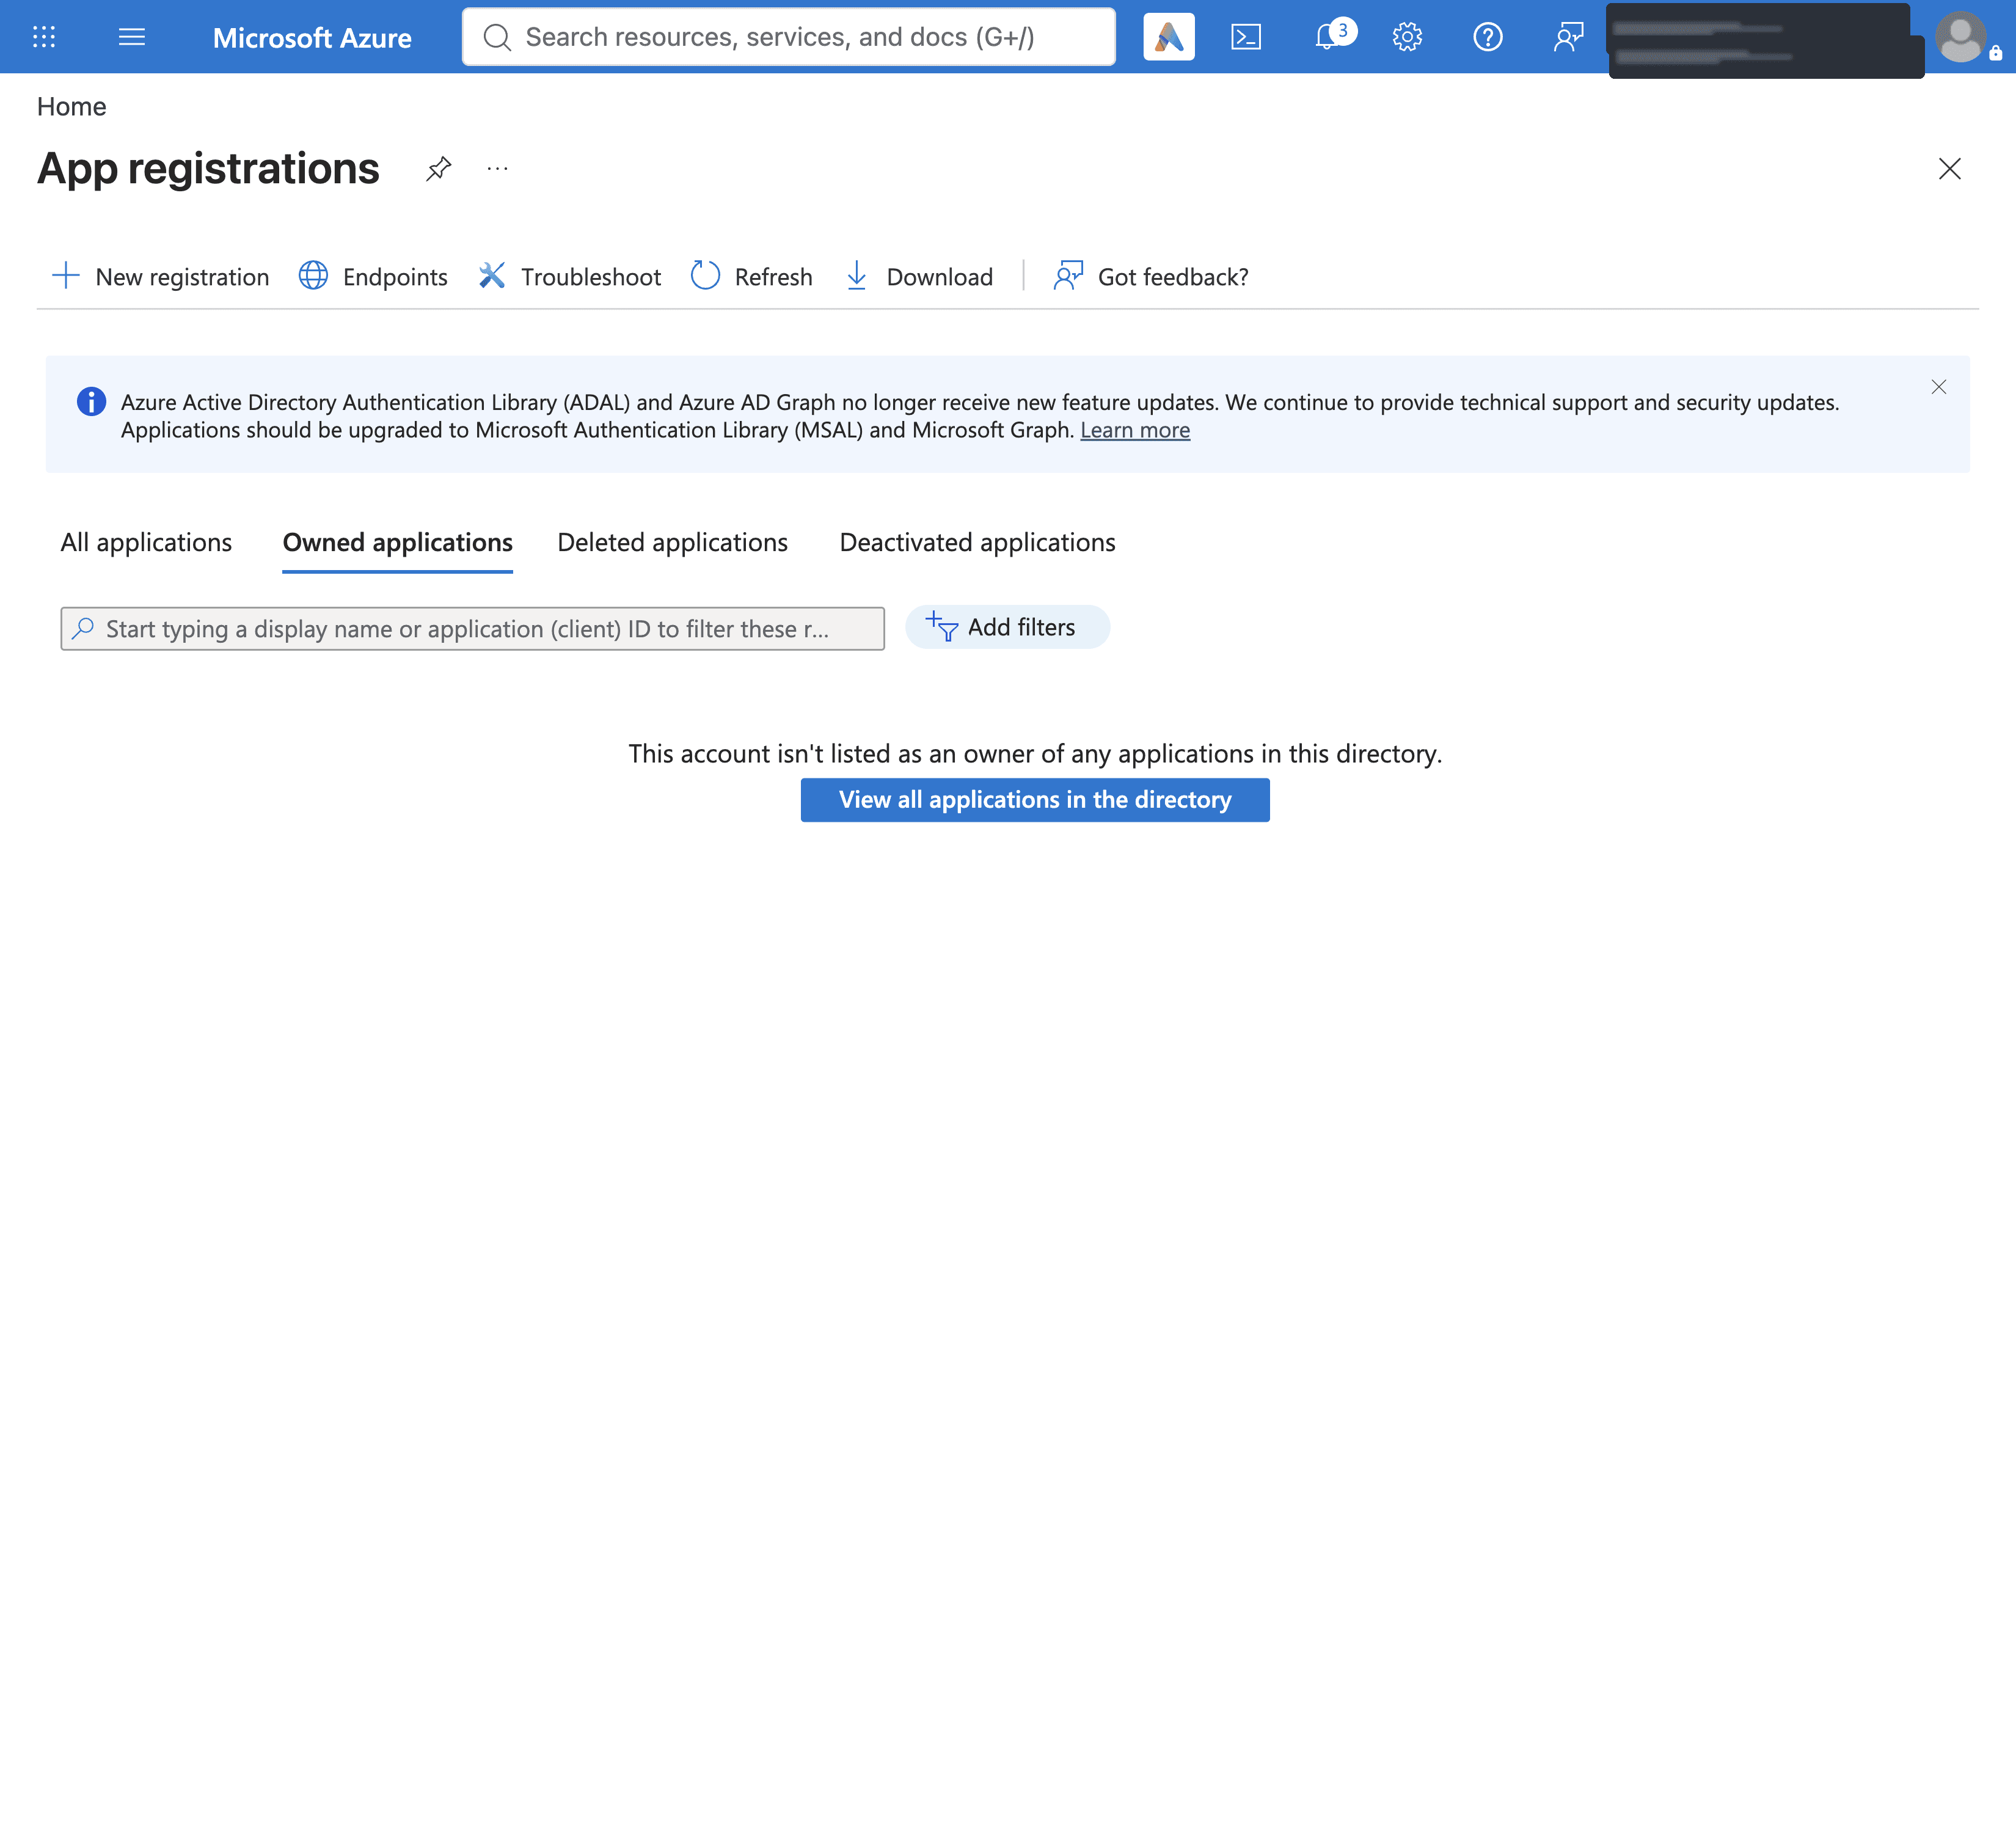
2. Click New registration.
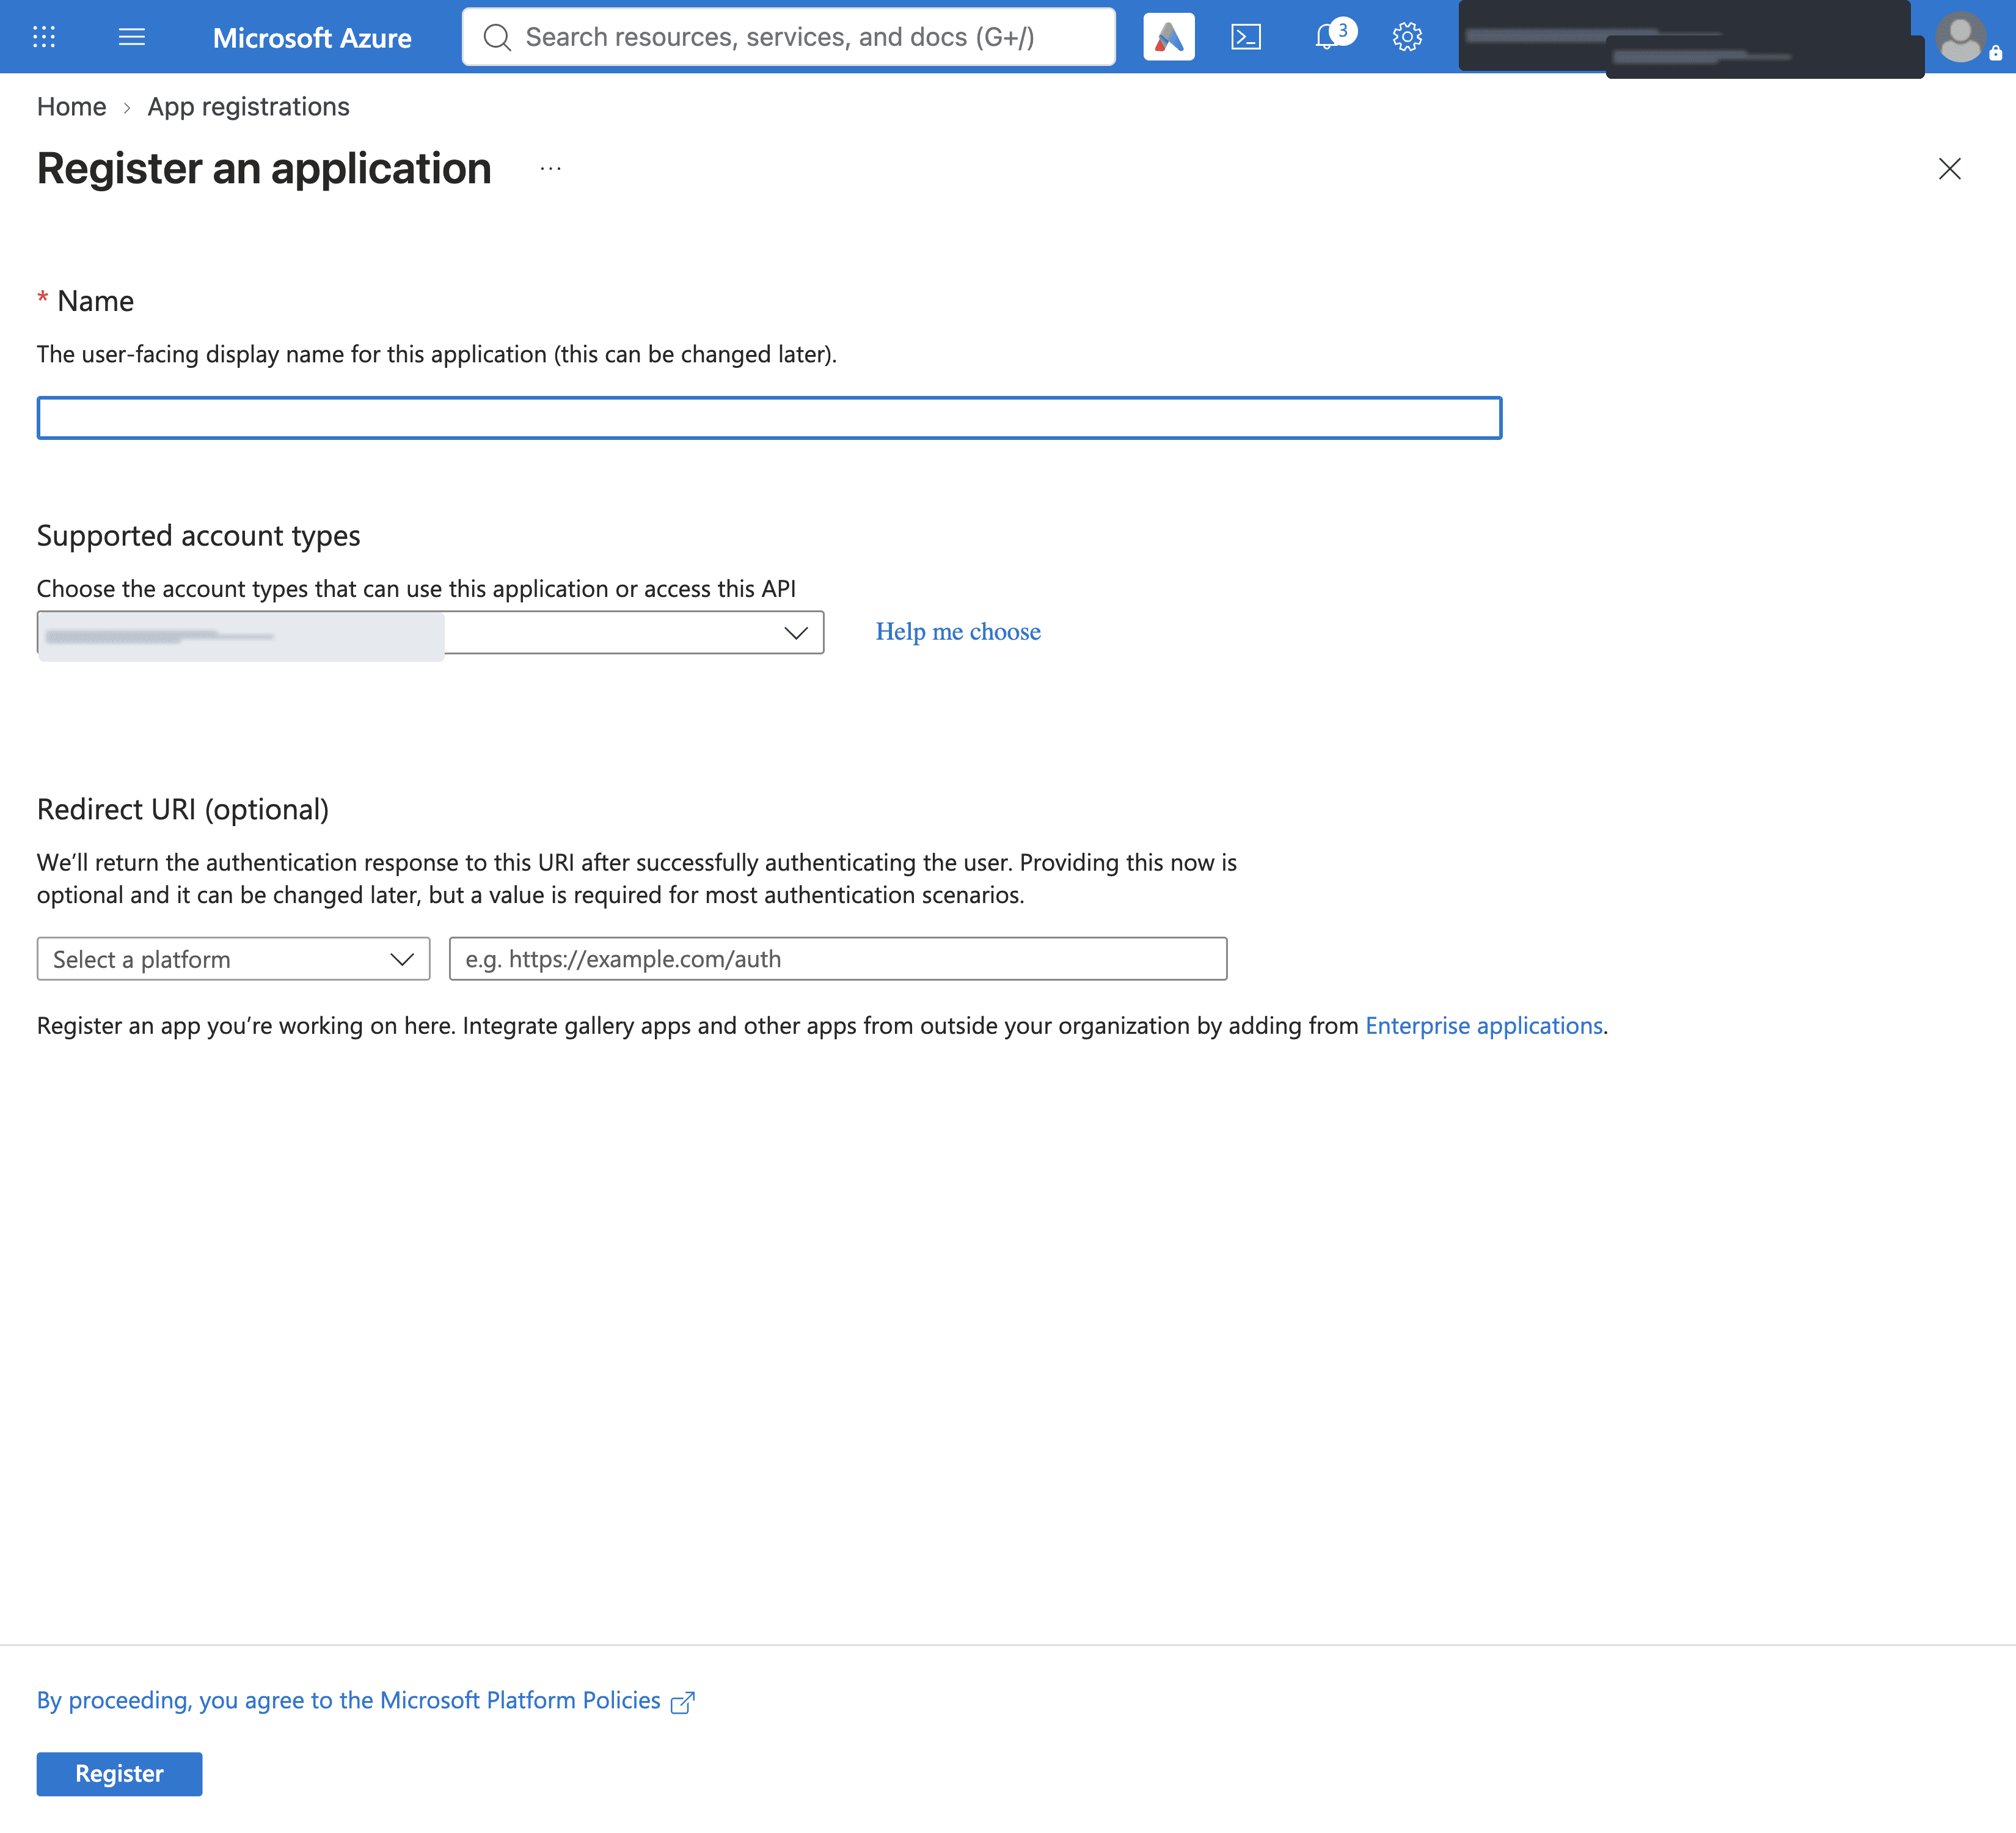
3. Enter a Name for your app (e.g., Composio Word Guide), choose Any Entra ID Tenant + Personal Microsoft accounts under Supported account types, select Web as the Redirect URI platform, paste Composio’s callback URL, and click Register.
https://backend.composio.dev/api/v1/auth-apps/add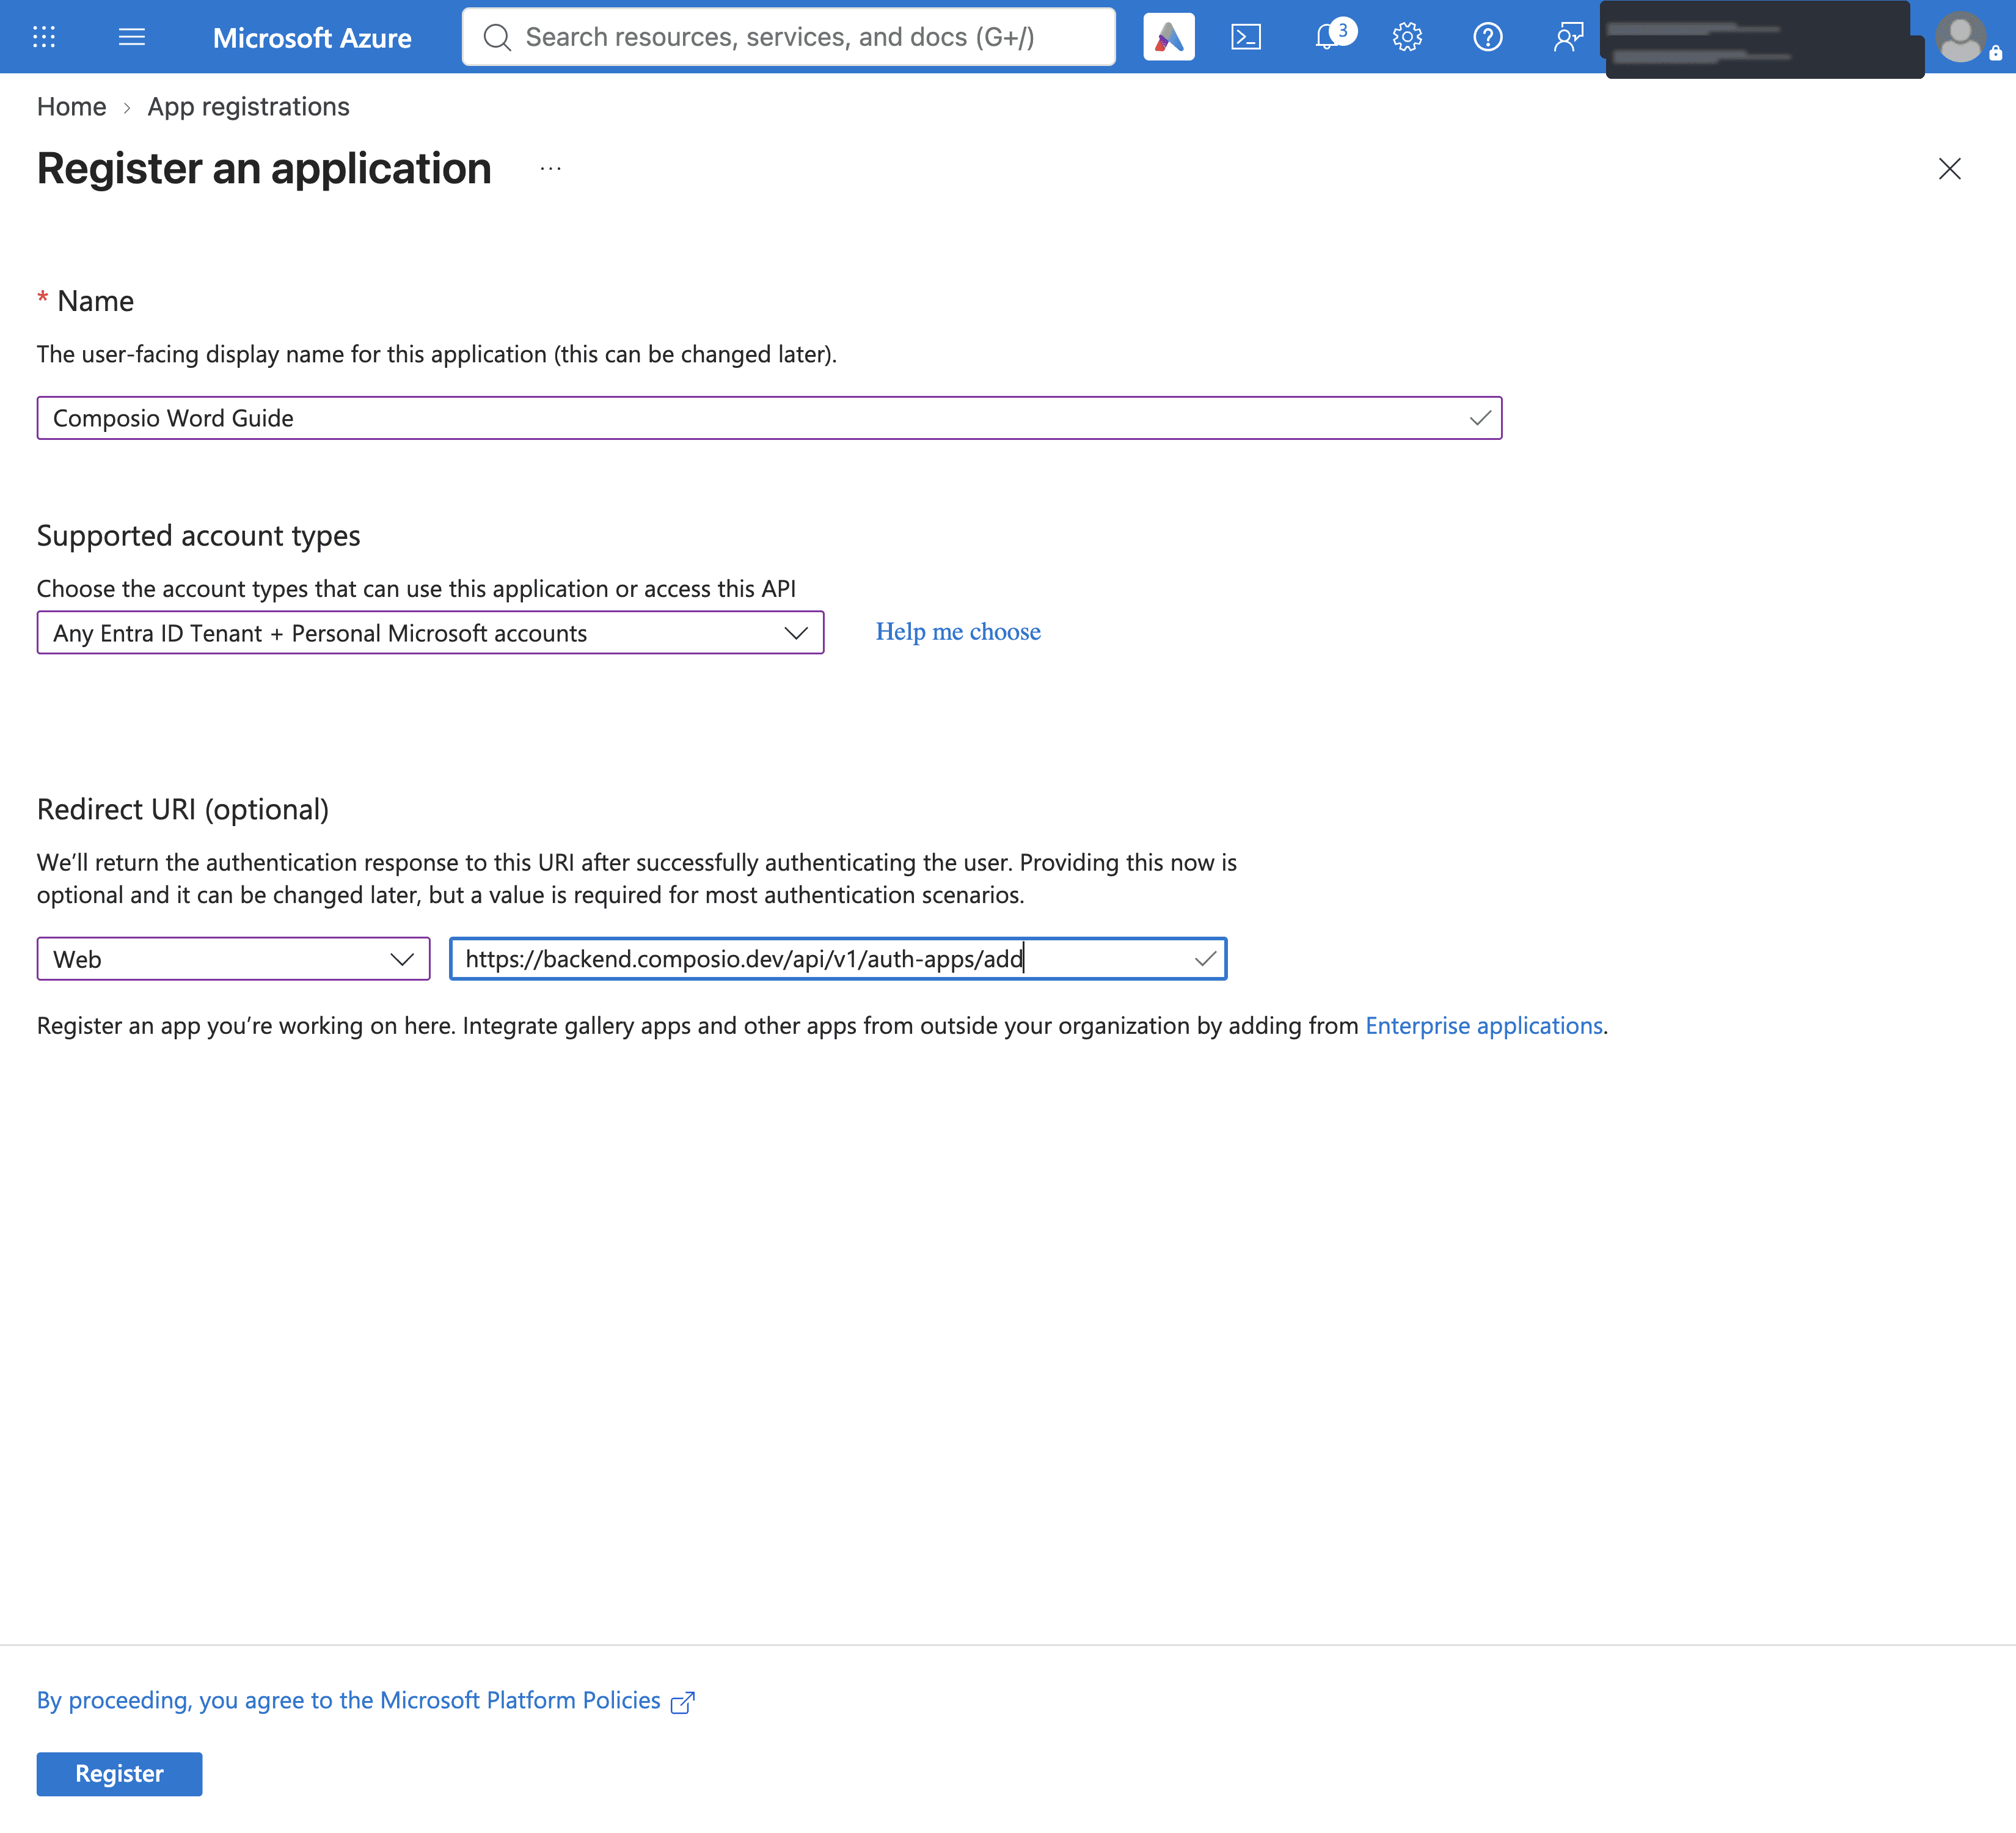
4. Your app is created. On the Overview page, copy the Application (client) ID. This is your Client ID.
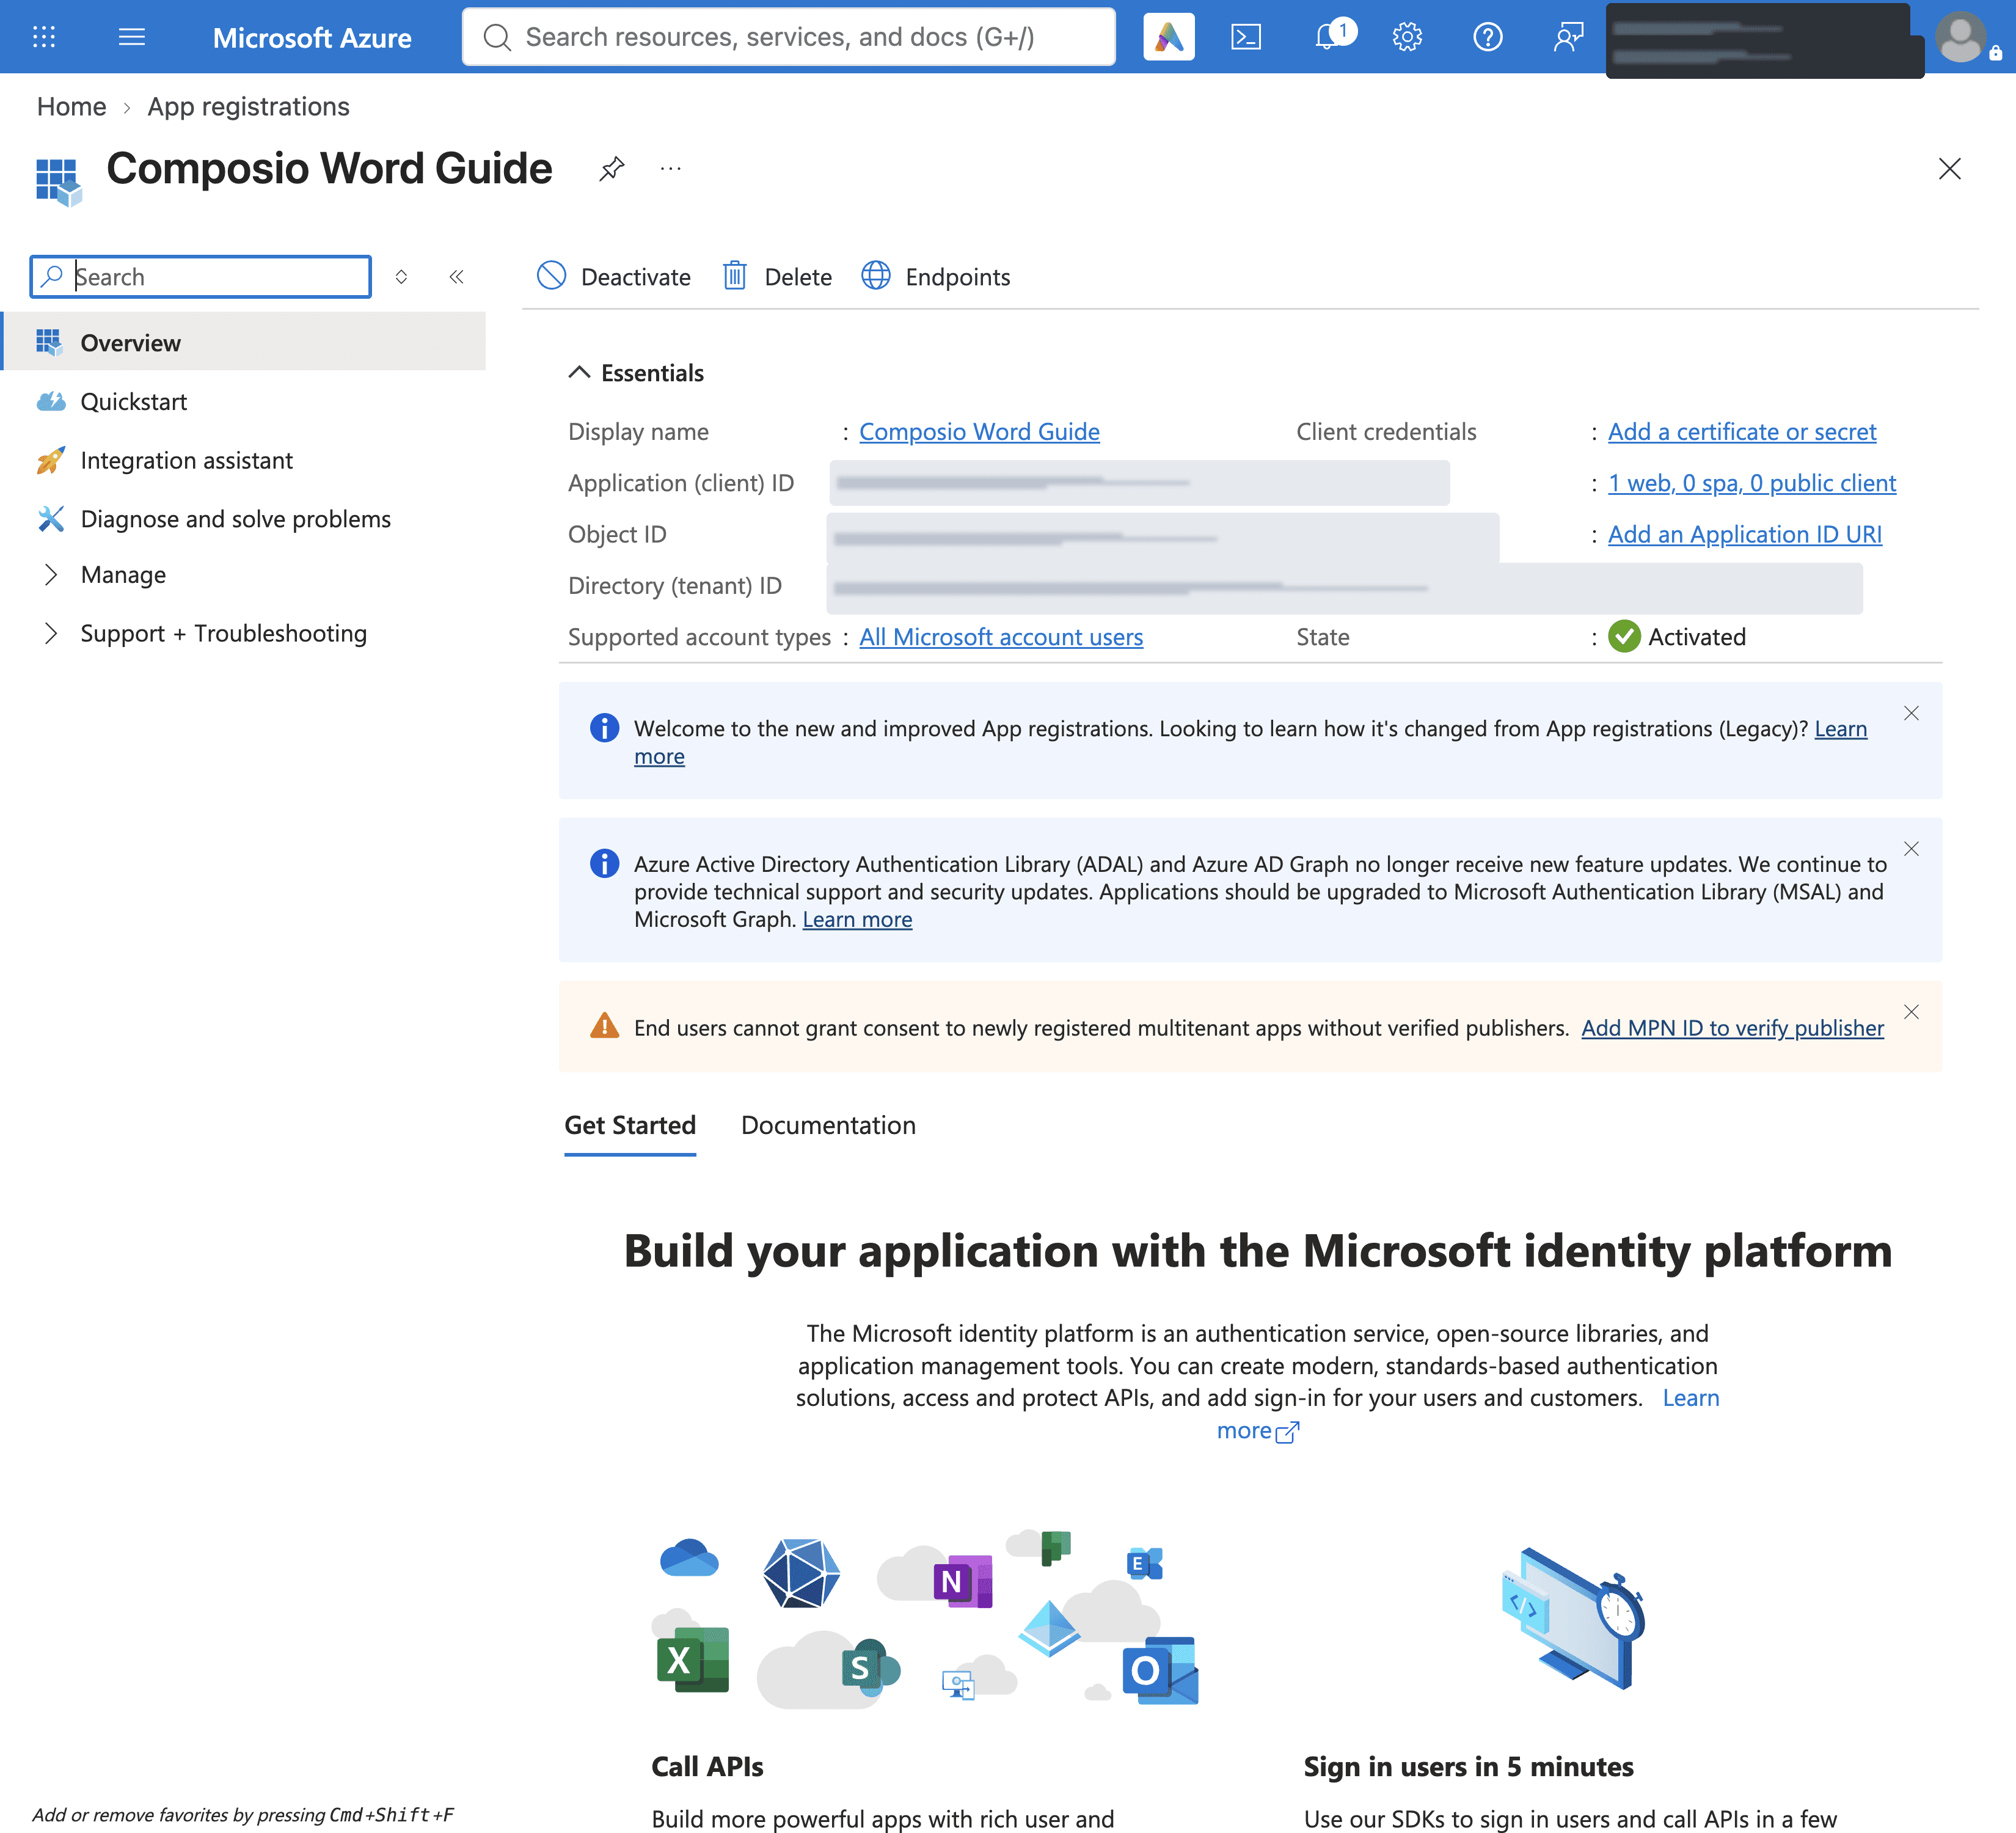
Step 2: Create a Client Secret
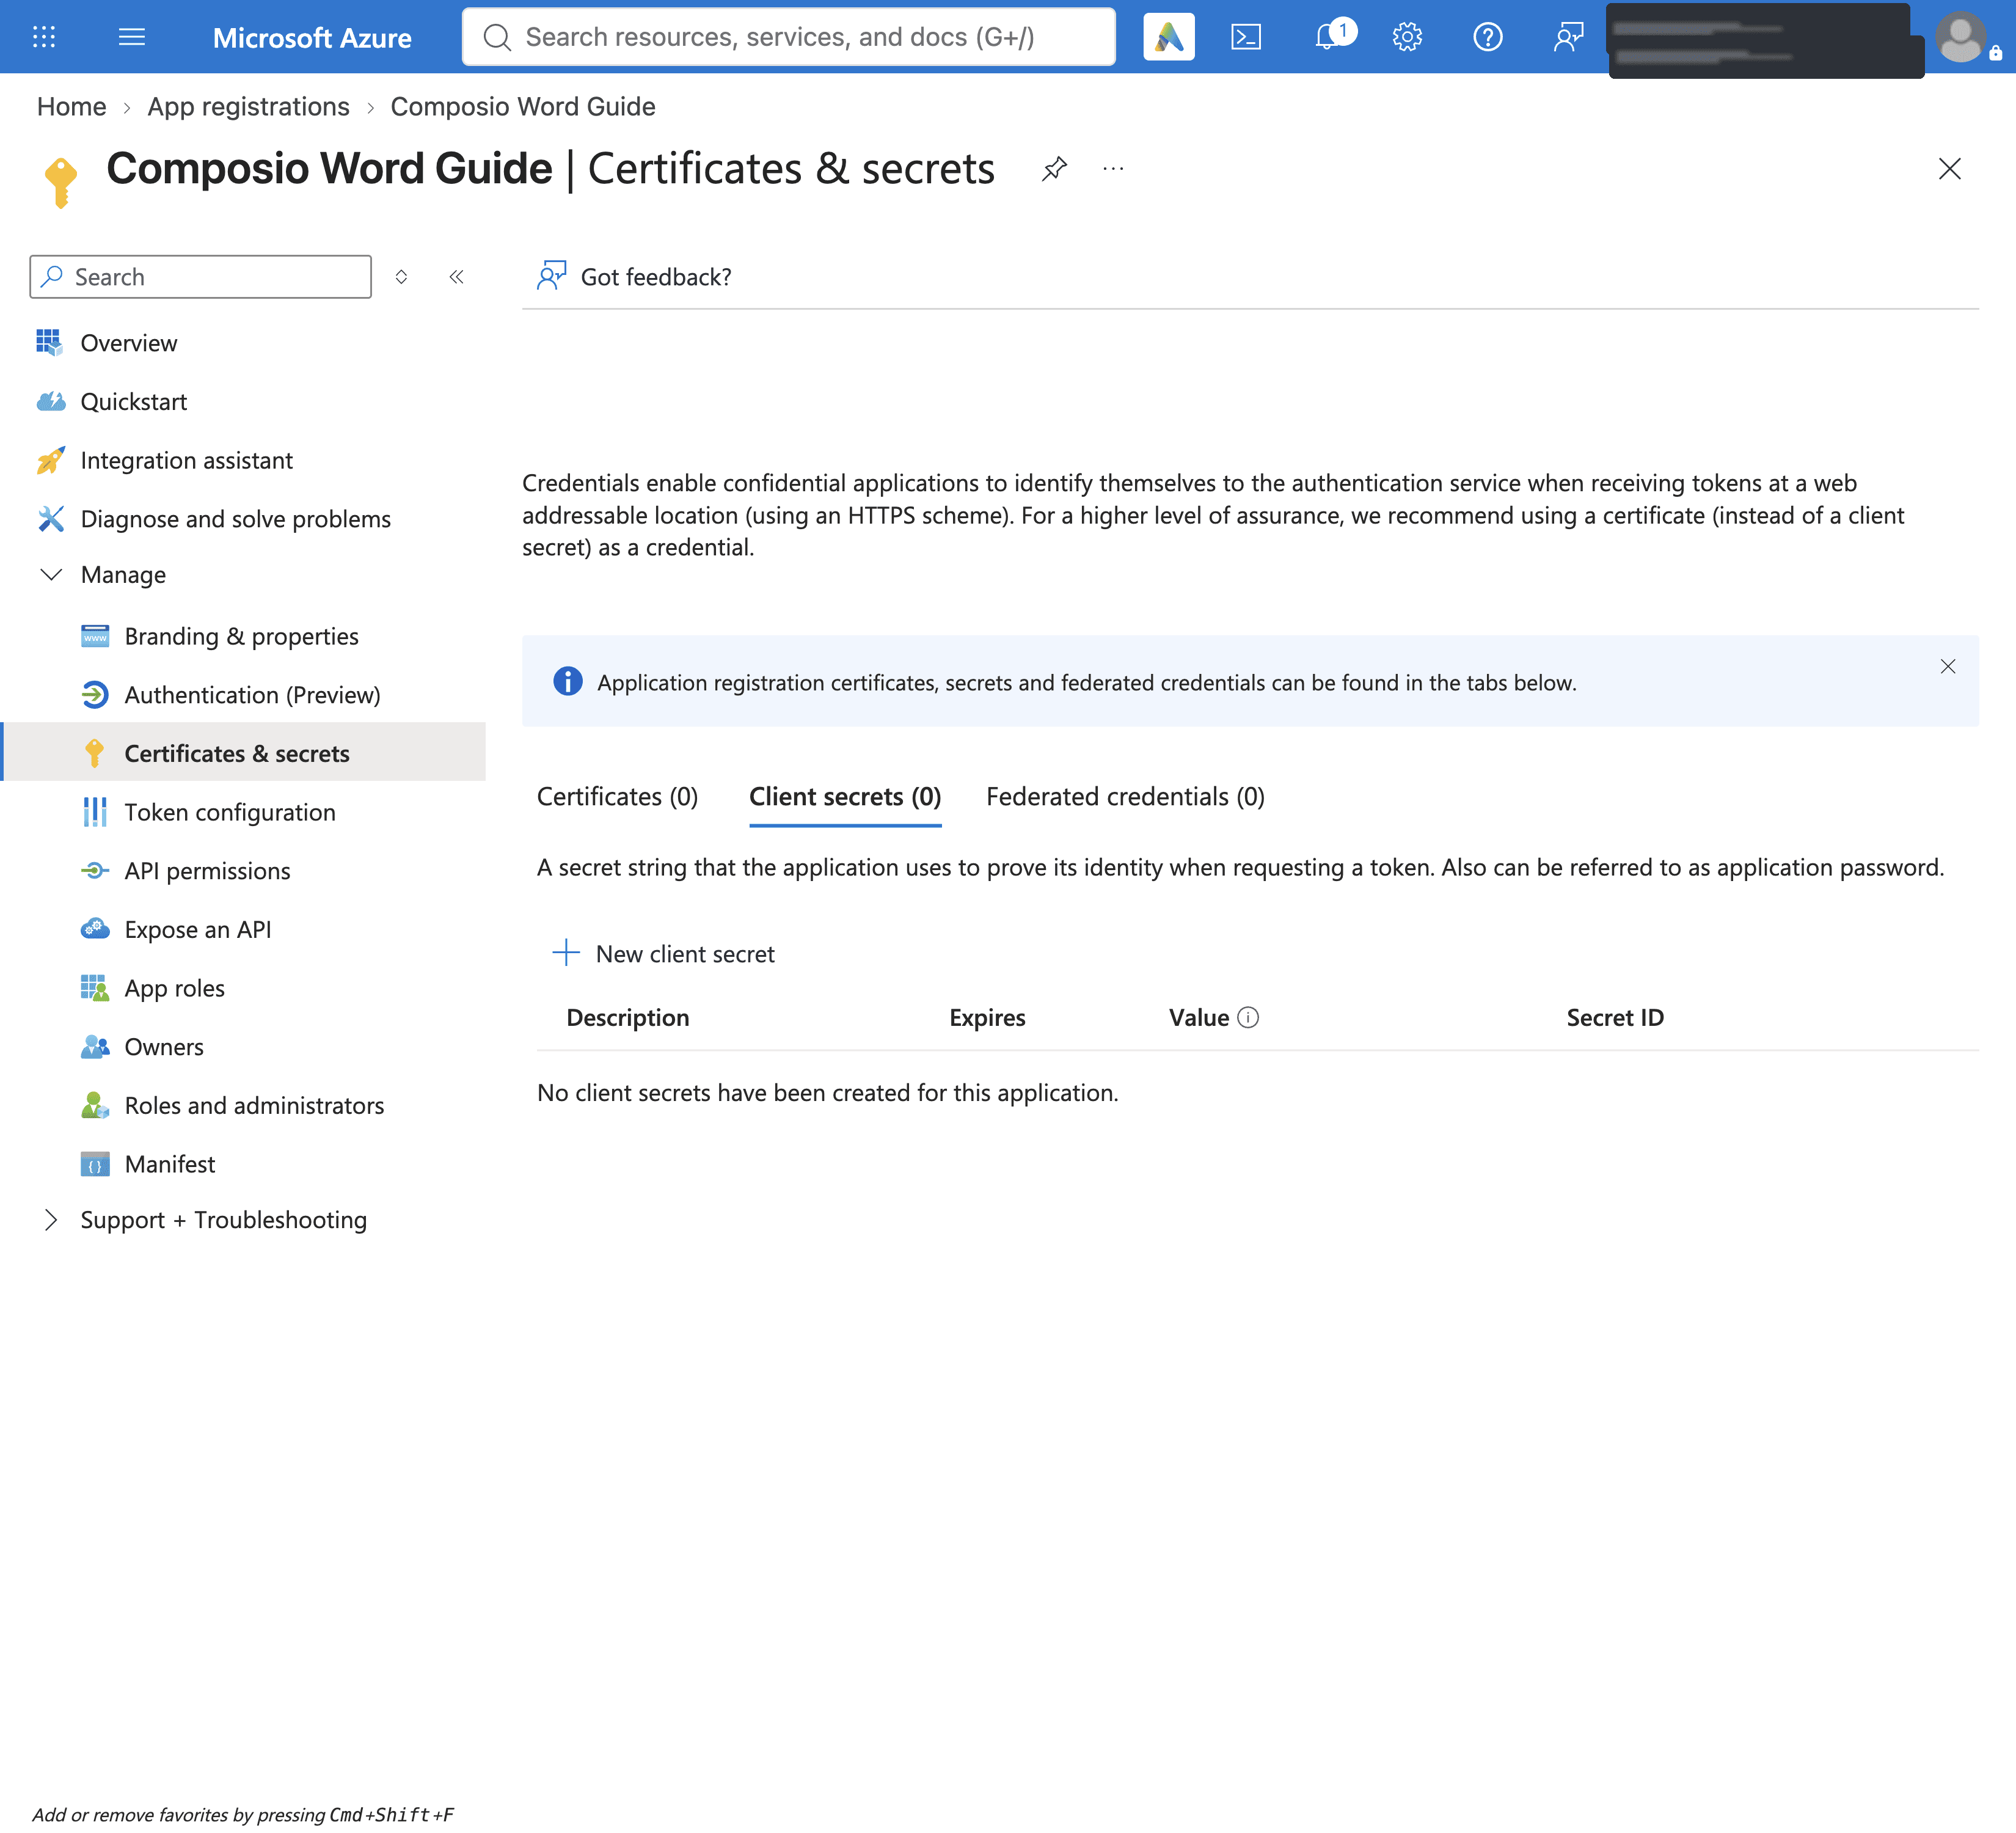
1. Open Certificates & secrets and click New client secret.
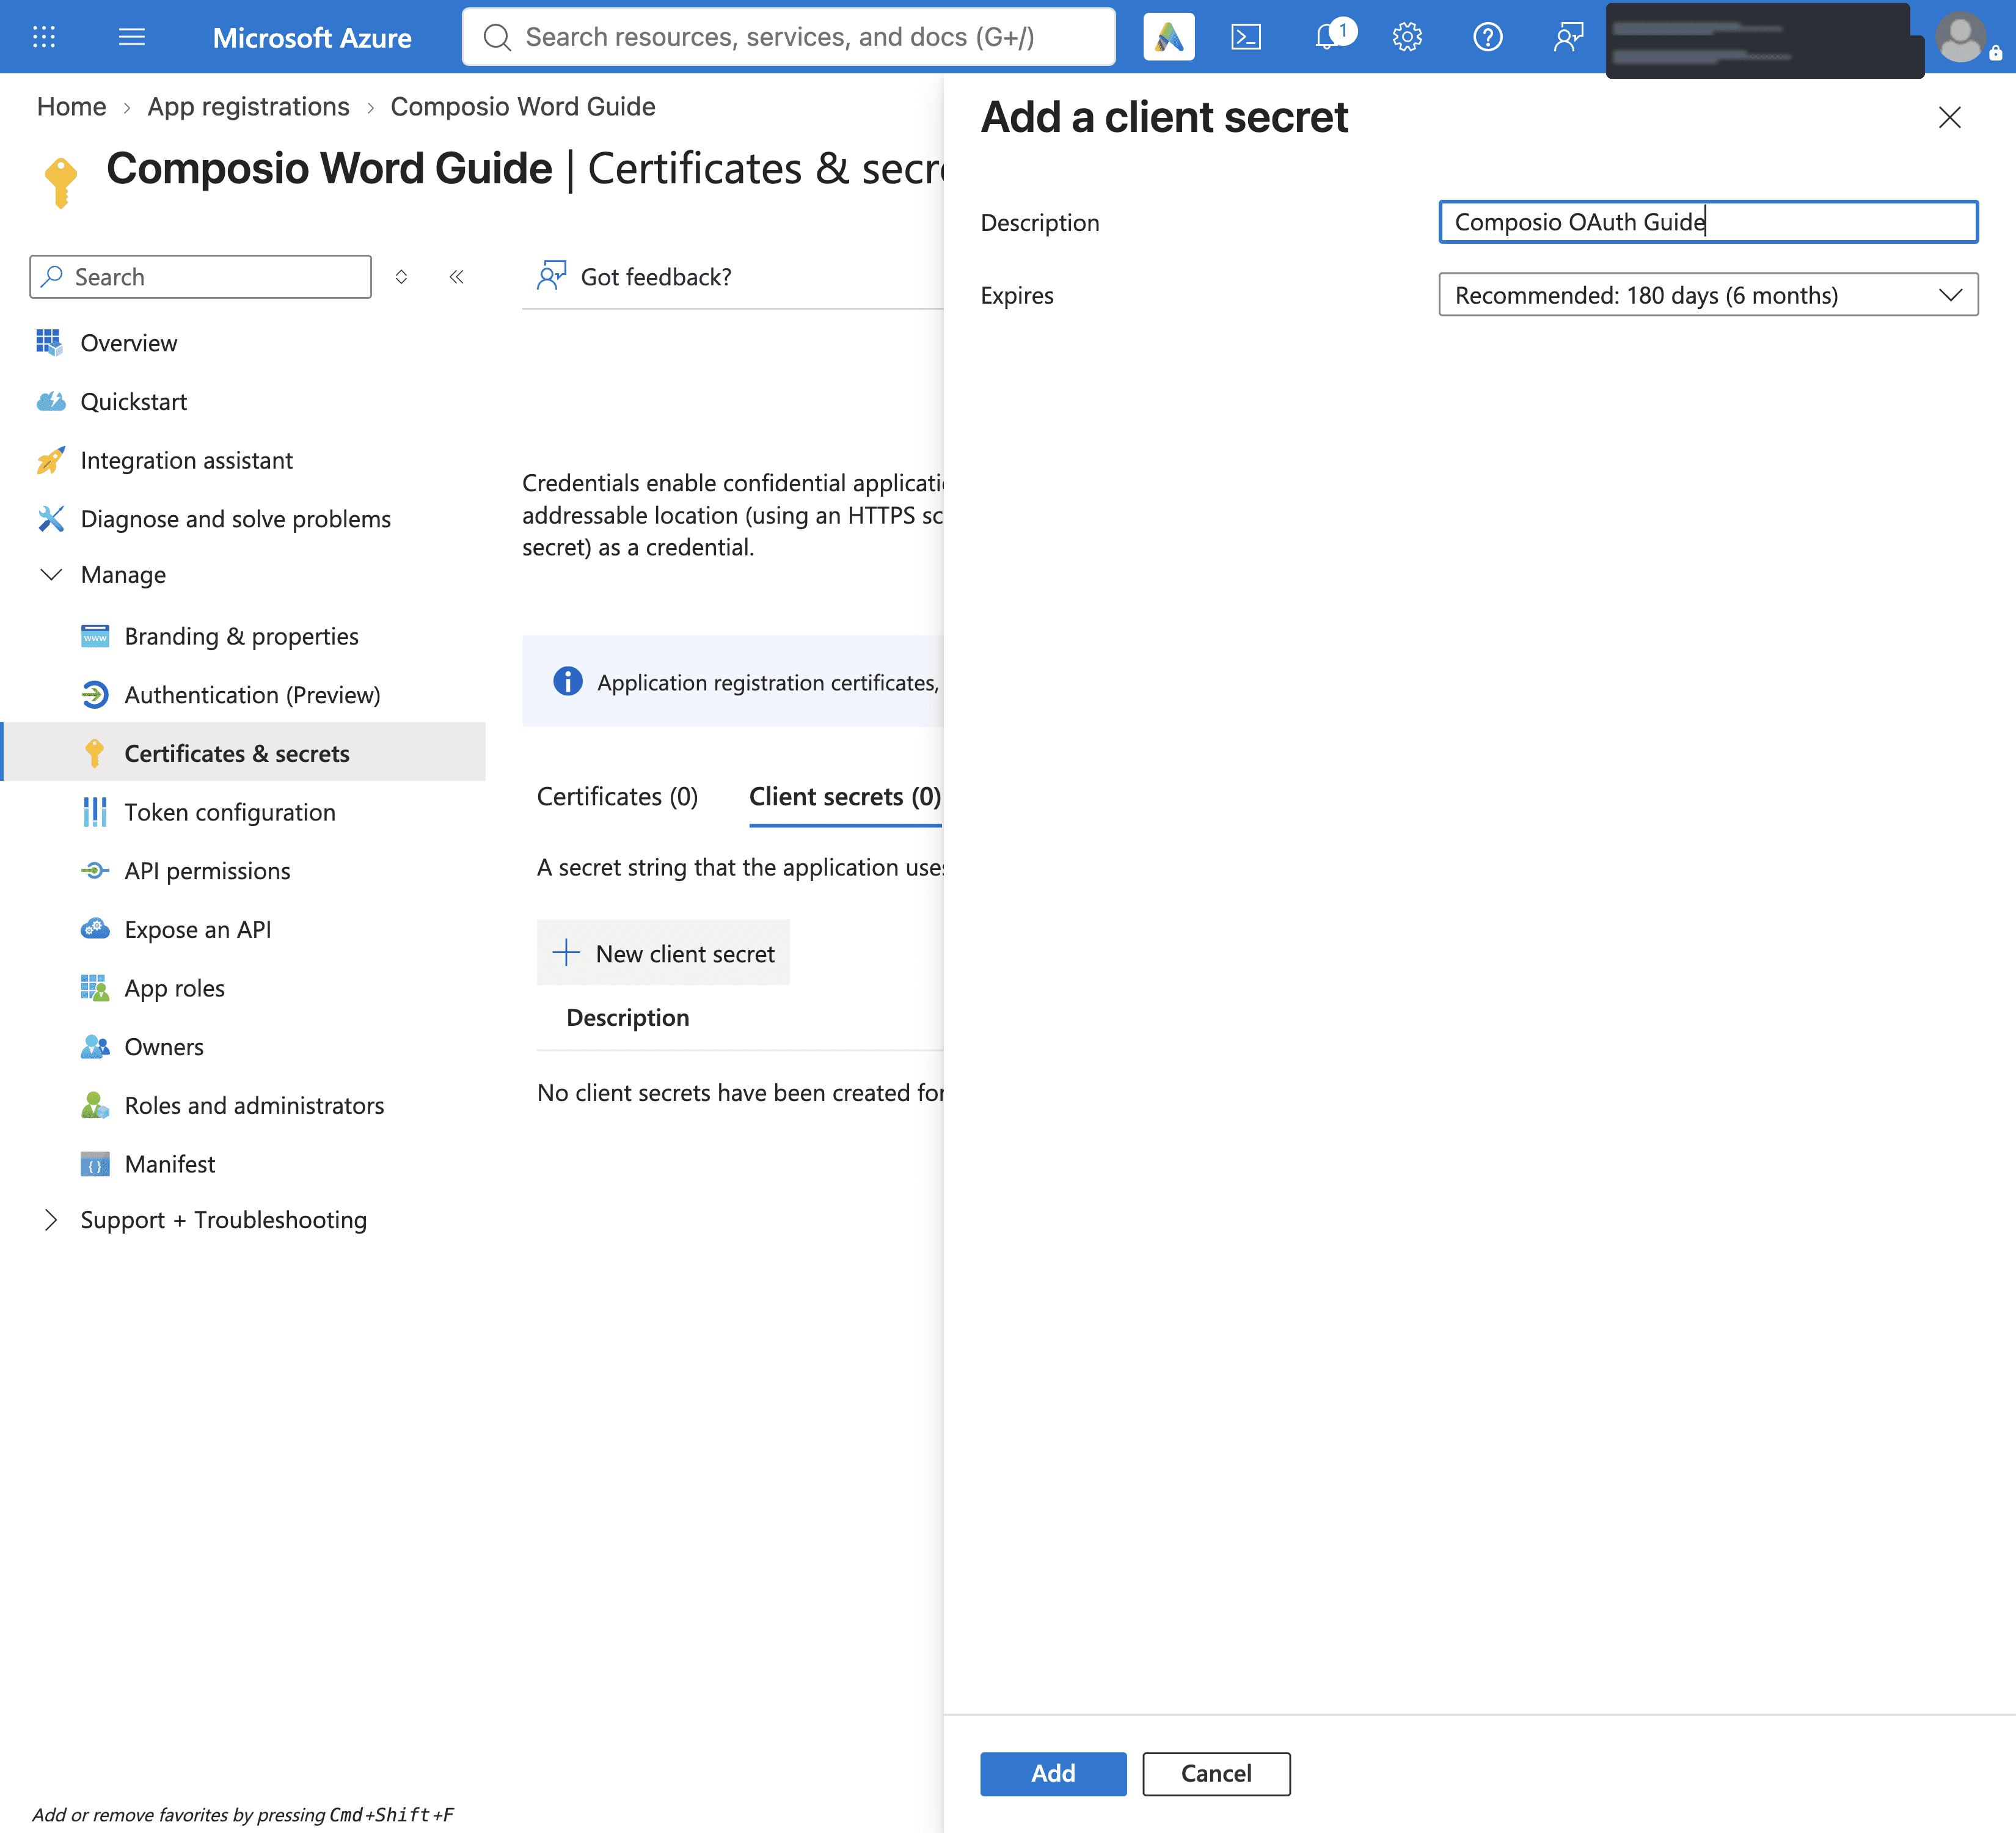
2. Add a description, choose an expiry, and click Add.
3. Copy the secret Value right away. This is your Client Secret, and Azure only shows it once.

Step 3: Confirm the Redirect URI
Open Authentication in the left sidebar and make sure a Web redirect URI is added with Composio’s callback URL. It must match the Redirect URI shown in your Composio auth config exactly:
https://backend.composio.dev/api/v1/auth-apps/add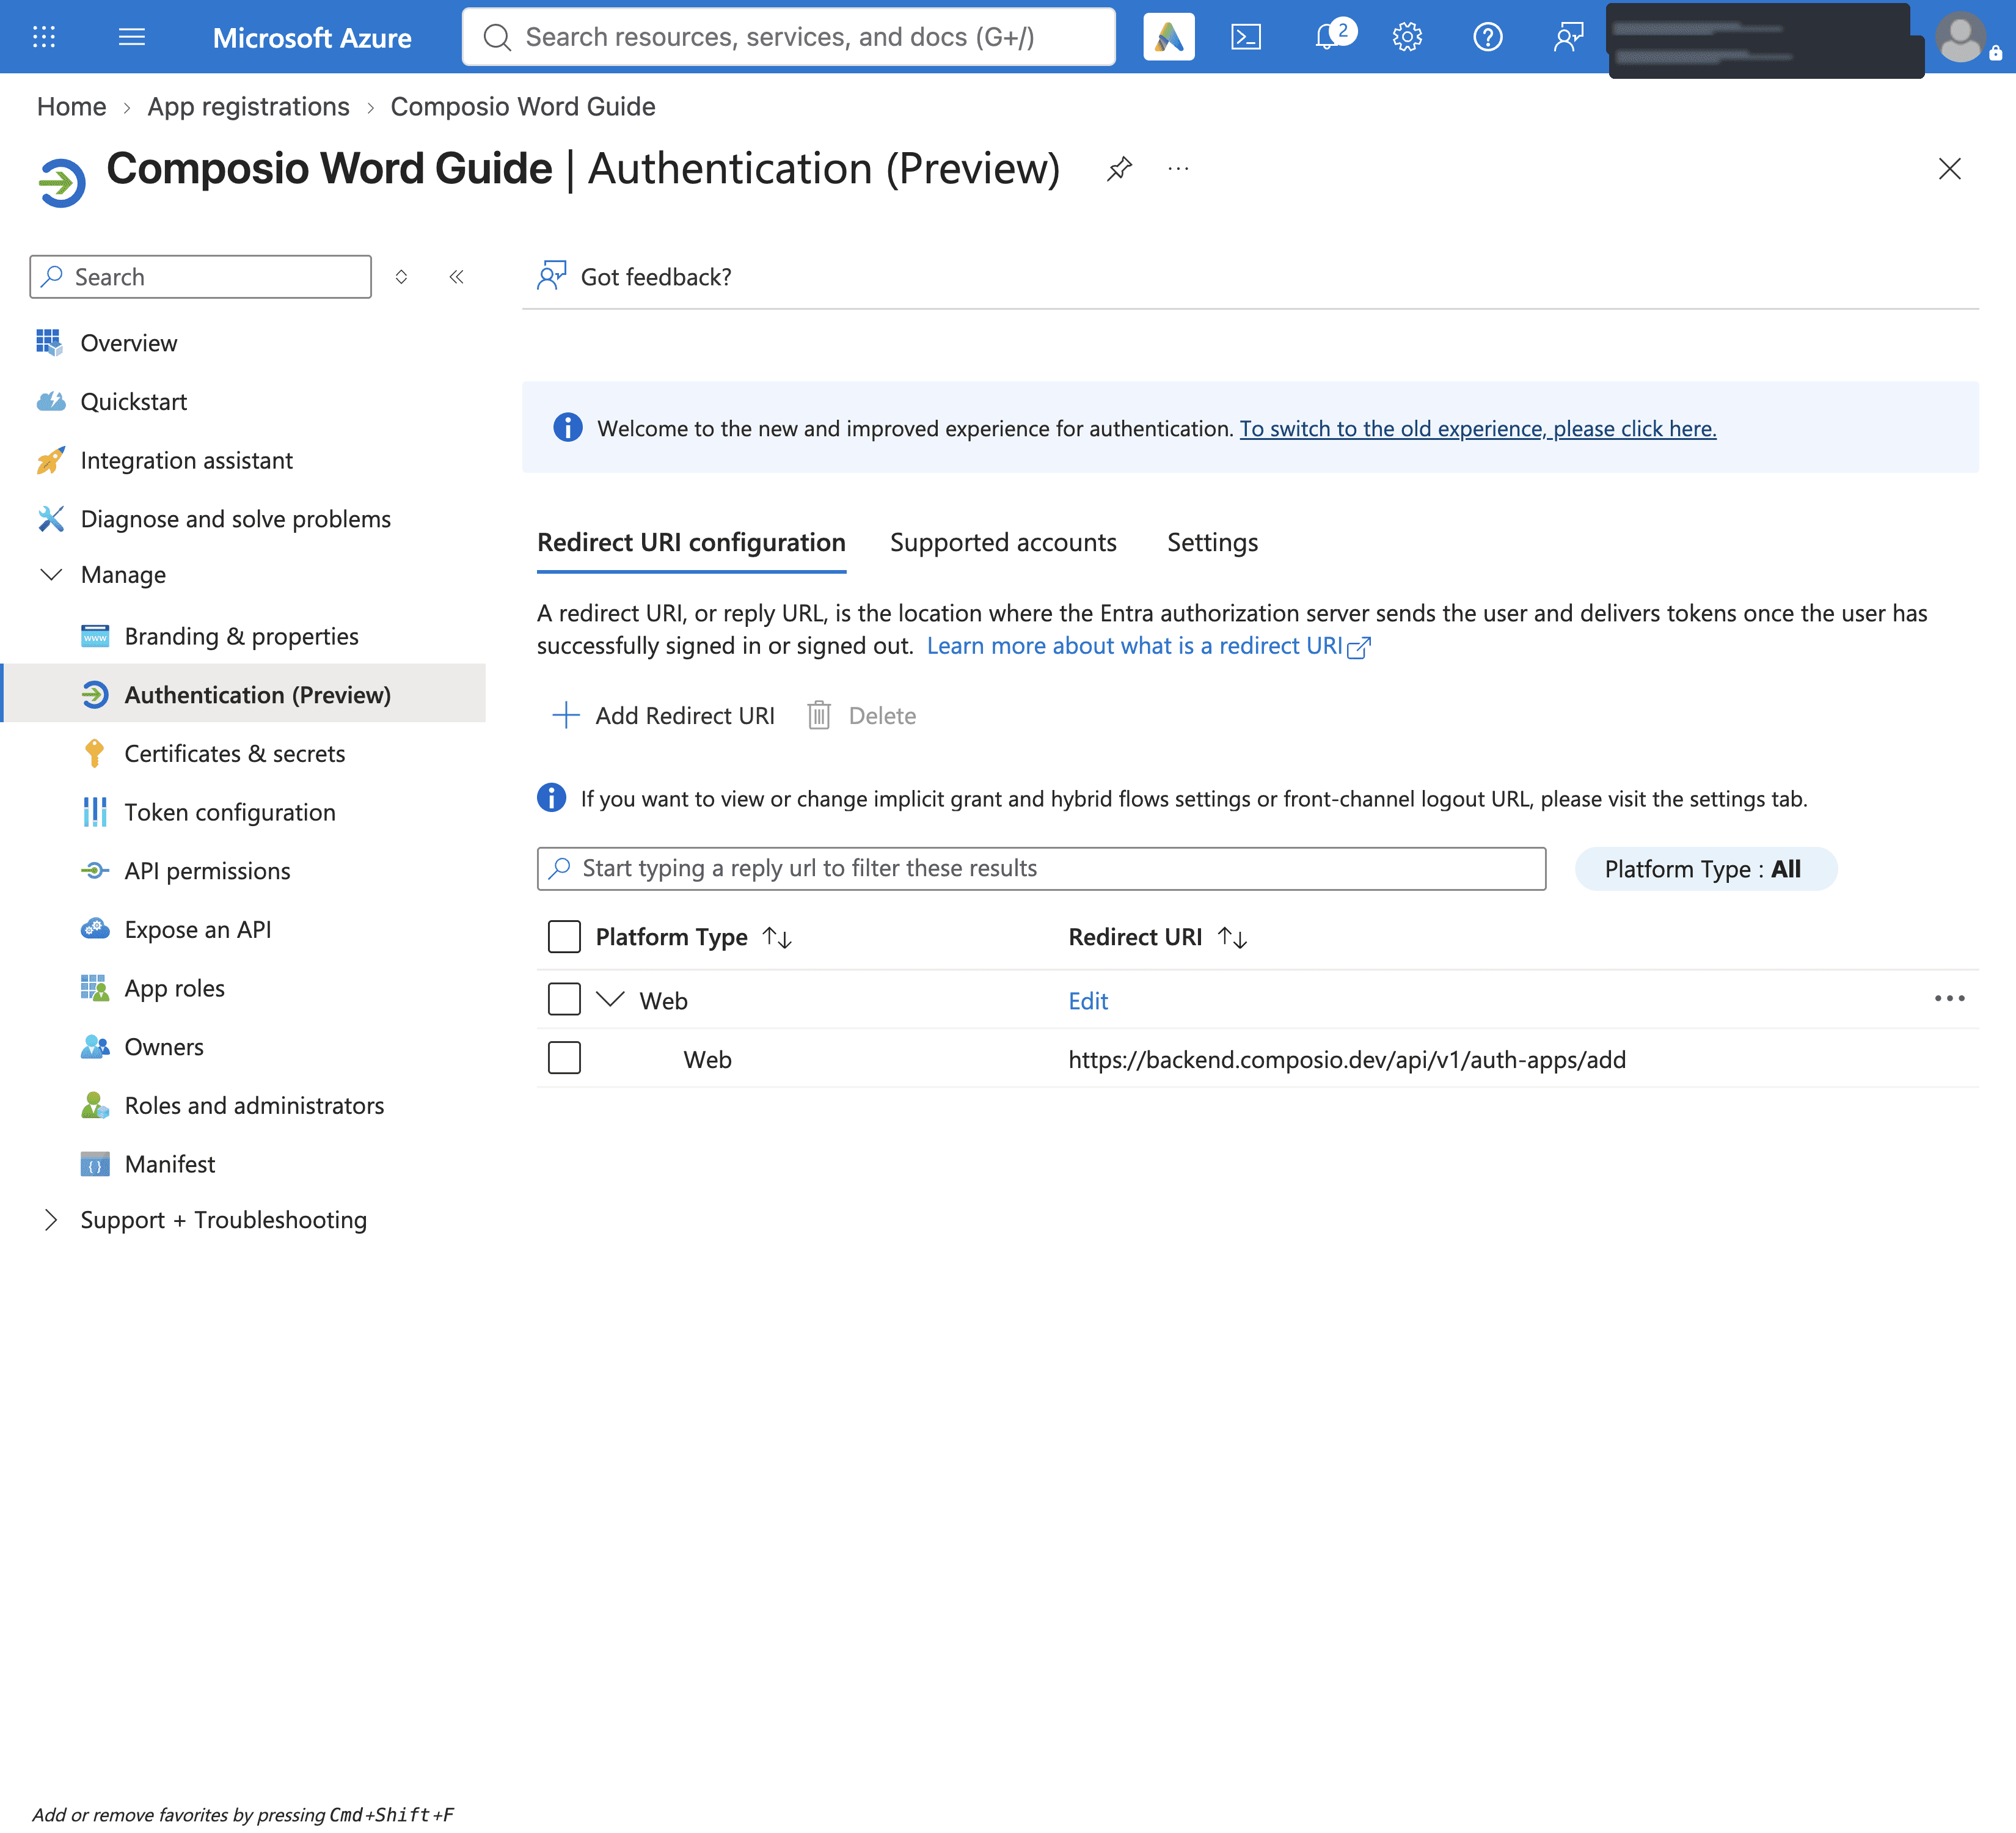
Step 4: Add Word API Permissions
1. Open API permissions and click Add a permission.

2. Select Microsoft Graph.

3. Choose Delegated permissions, so the app acts on behalf of the signed-in user.

4. Search for and select Files.ReadWrite.All so the app can create, read, and edit Word documents.
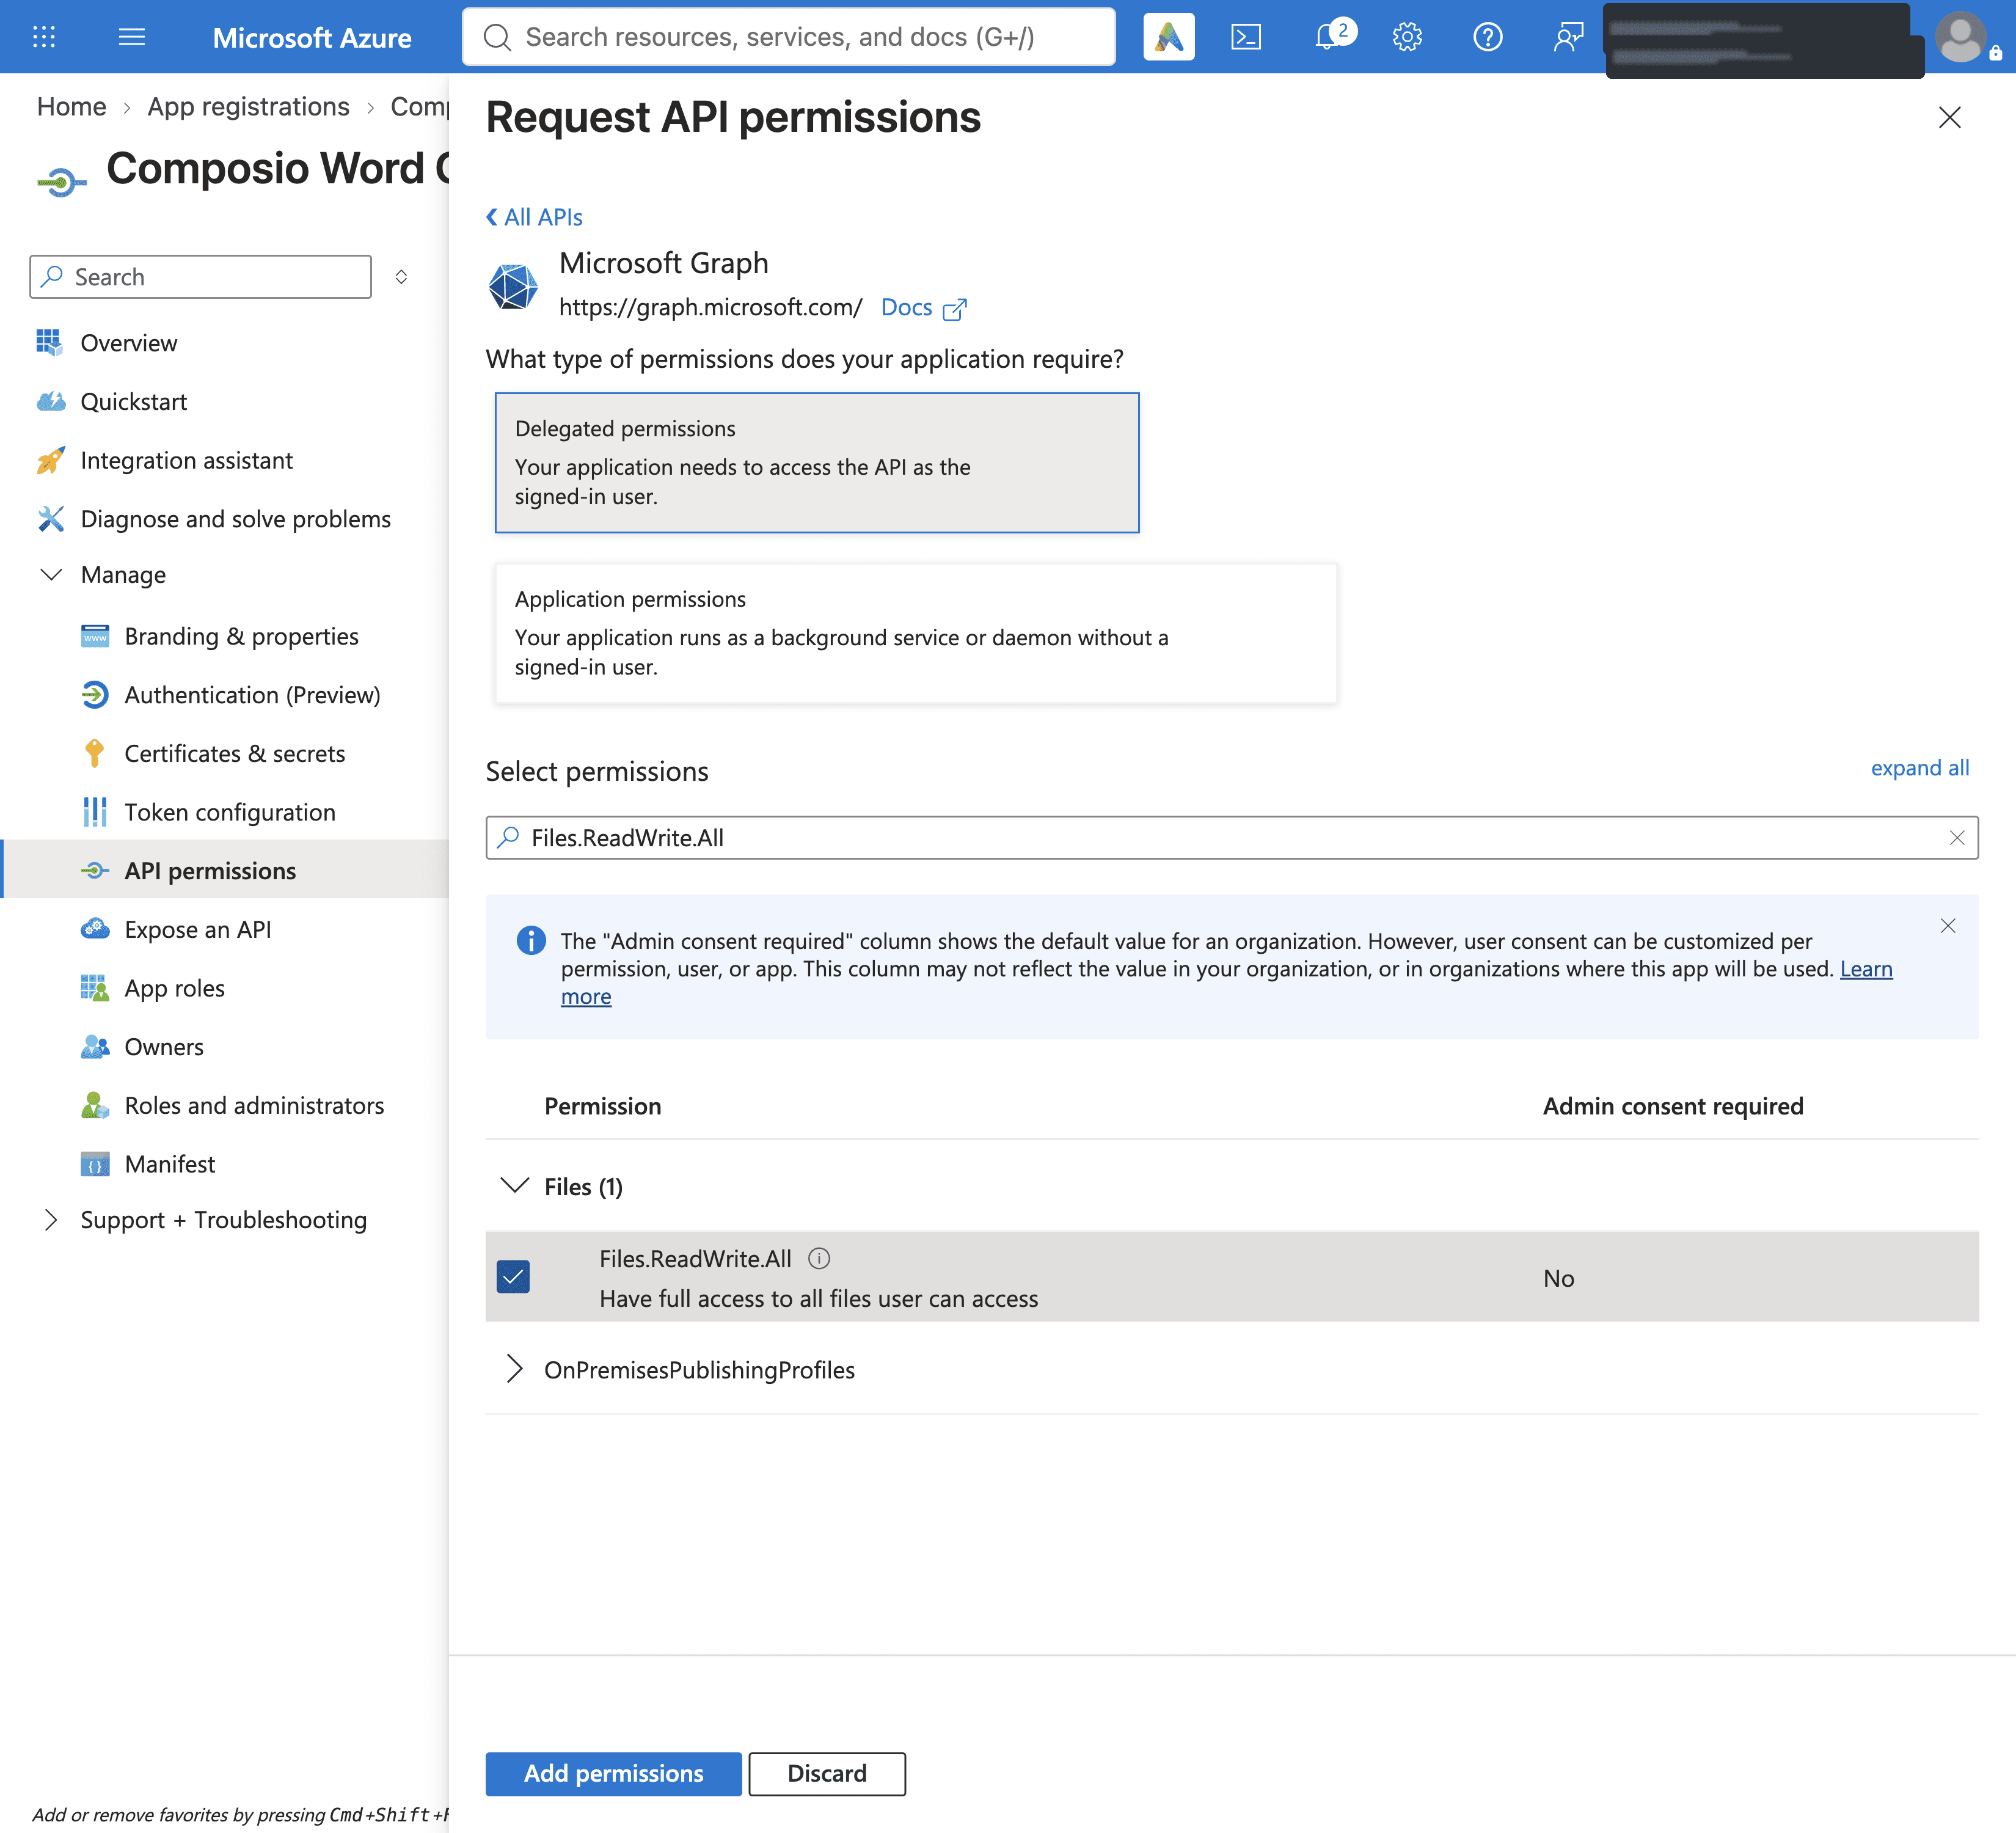
5. Search for and select Sites.Read.All so the app can read documents stored in SharePoint sites.

6. Also select offline_access so Composio can refresh tokens, then click Add permissions.

7. Your configured permissions should now include Files.ReadWrite.All, Sites.Read.All, offline_access, and User.Read.
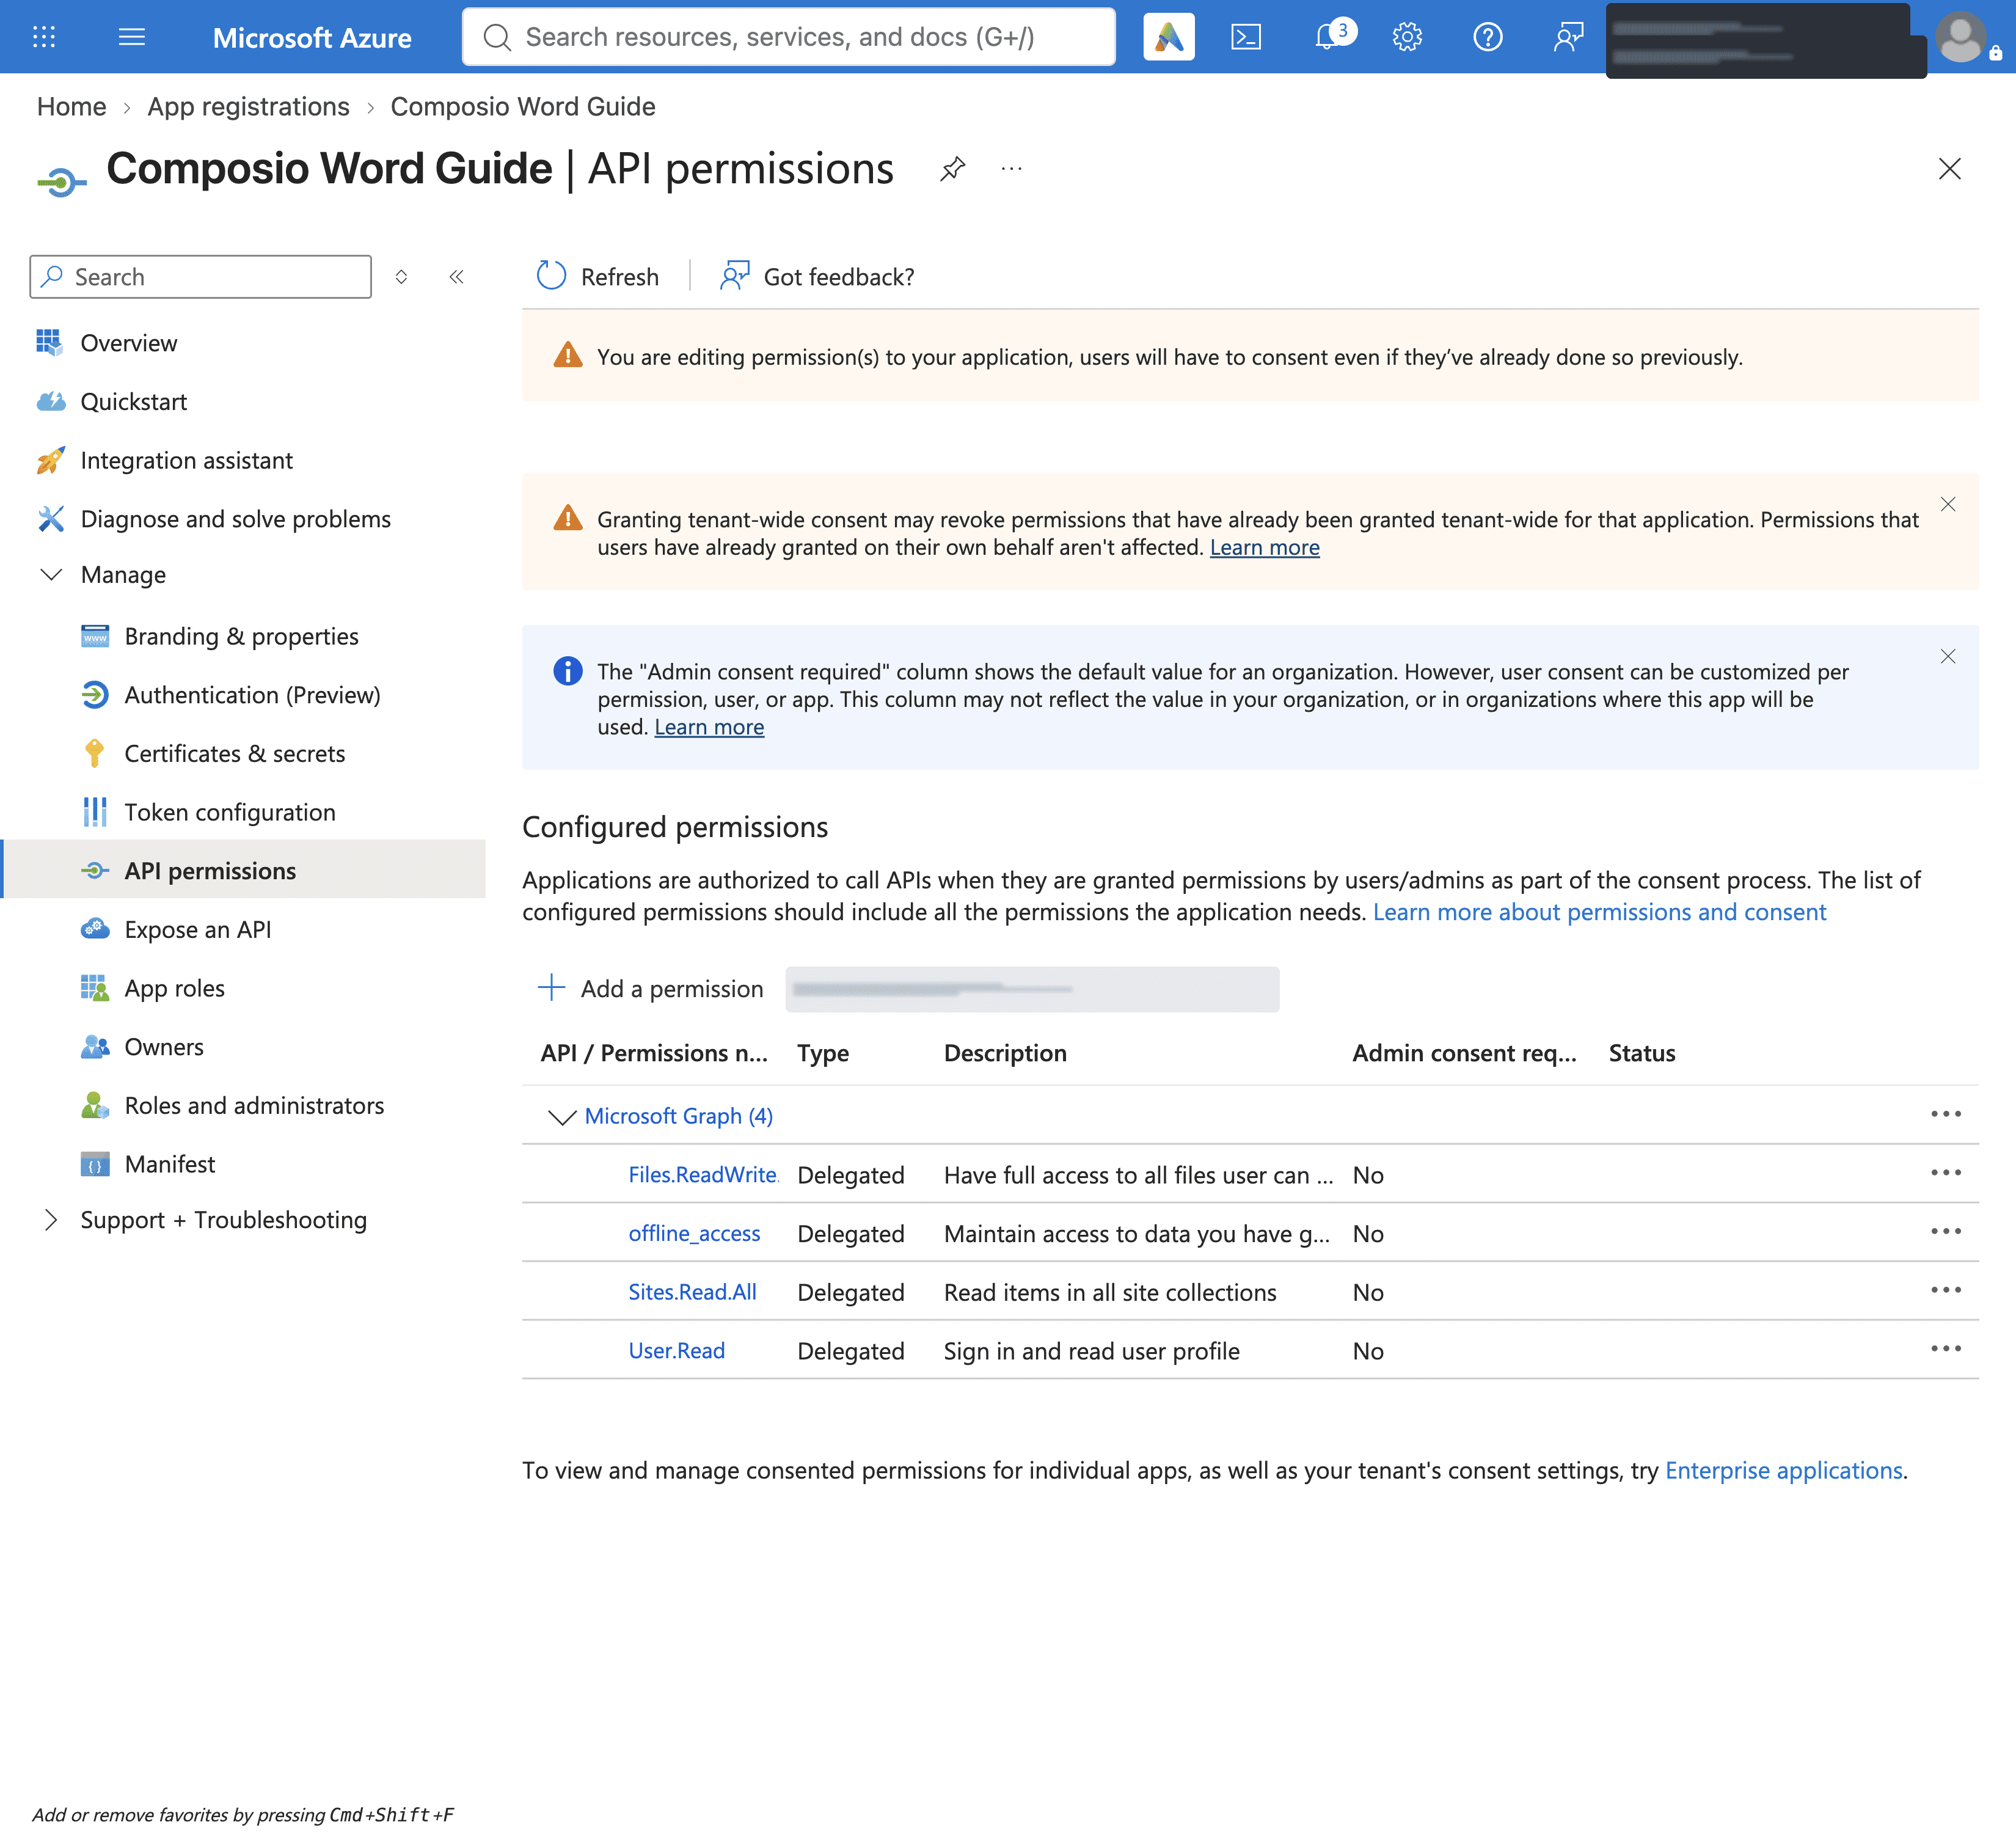
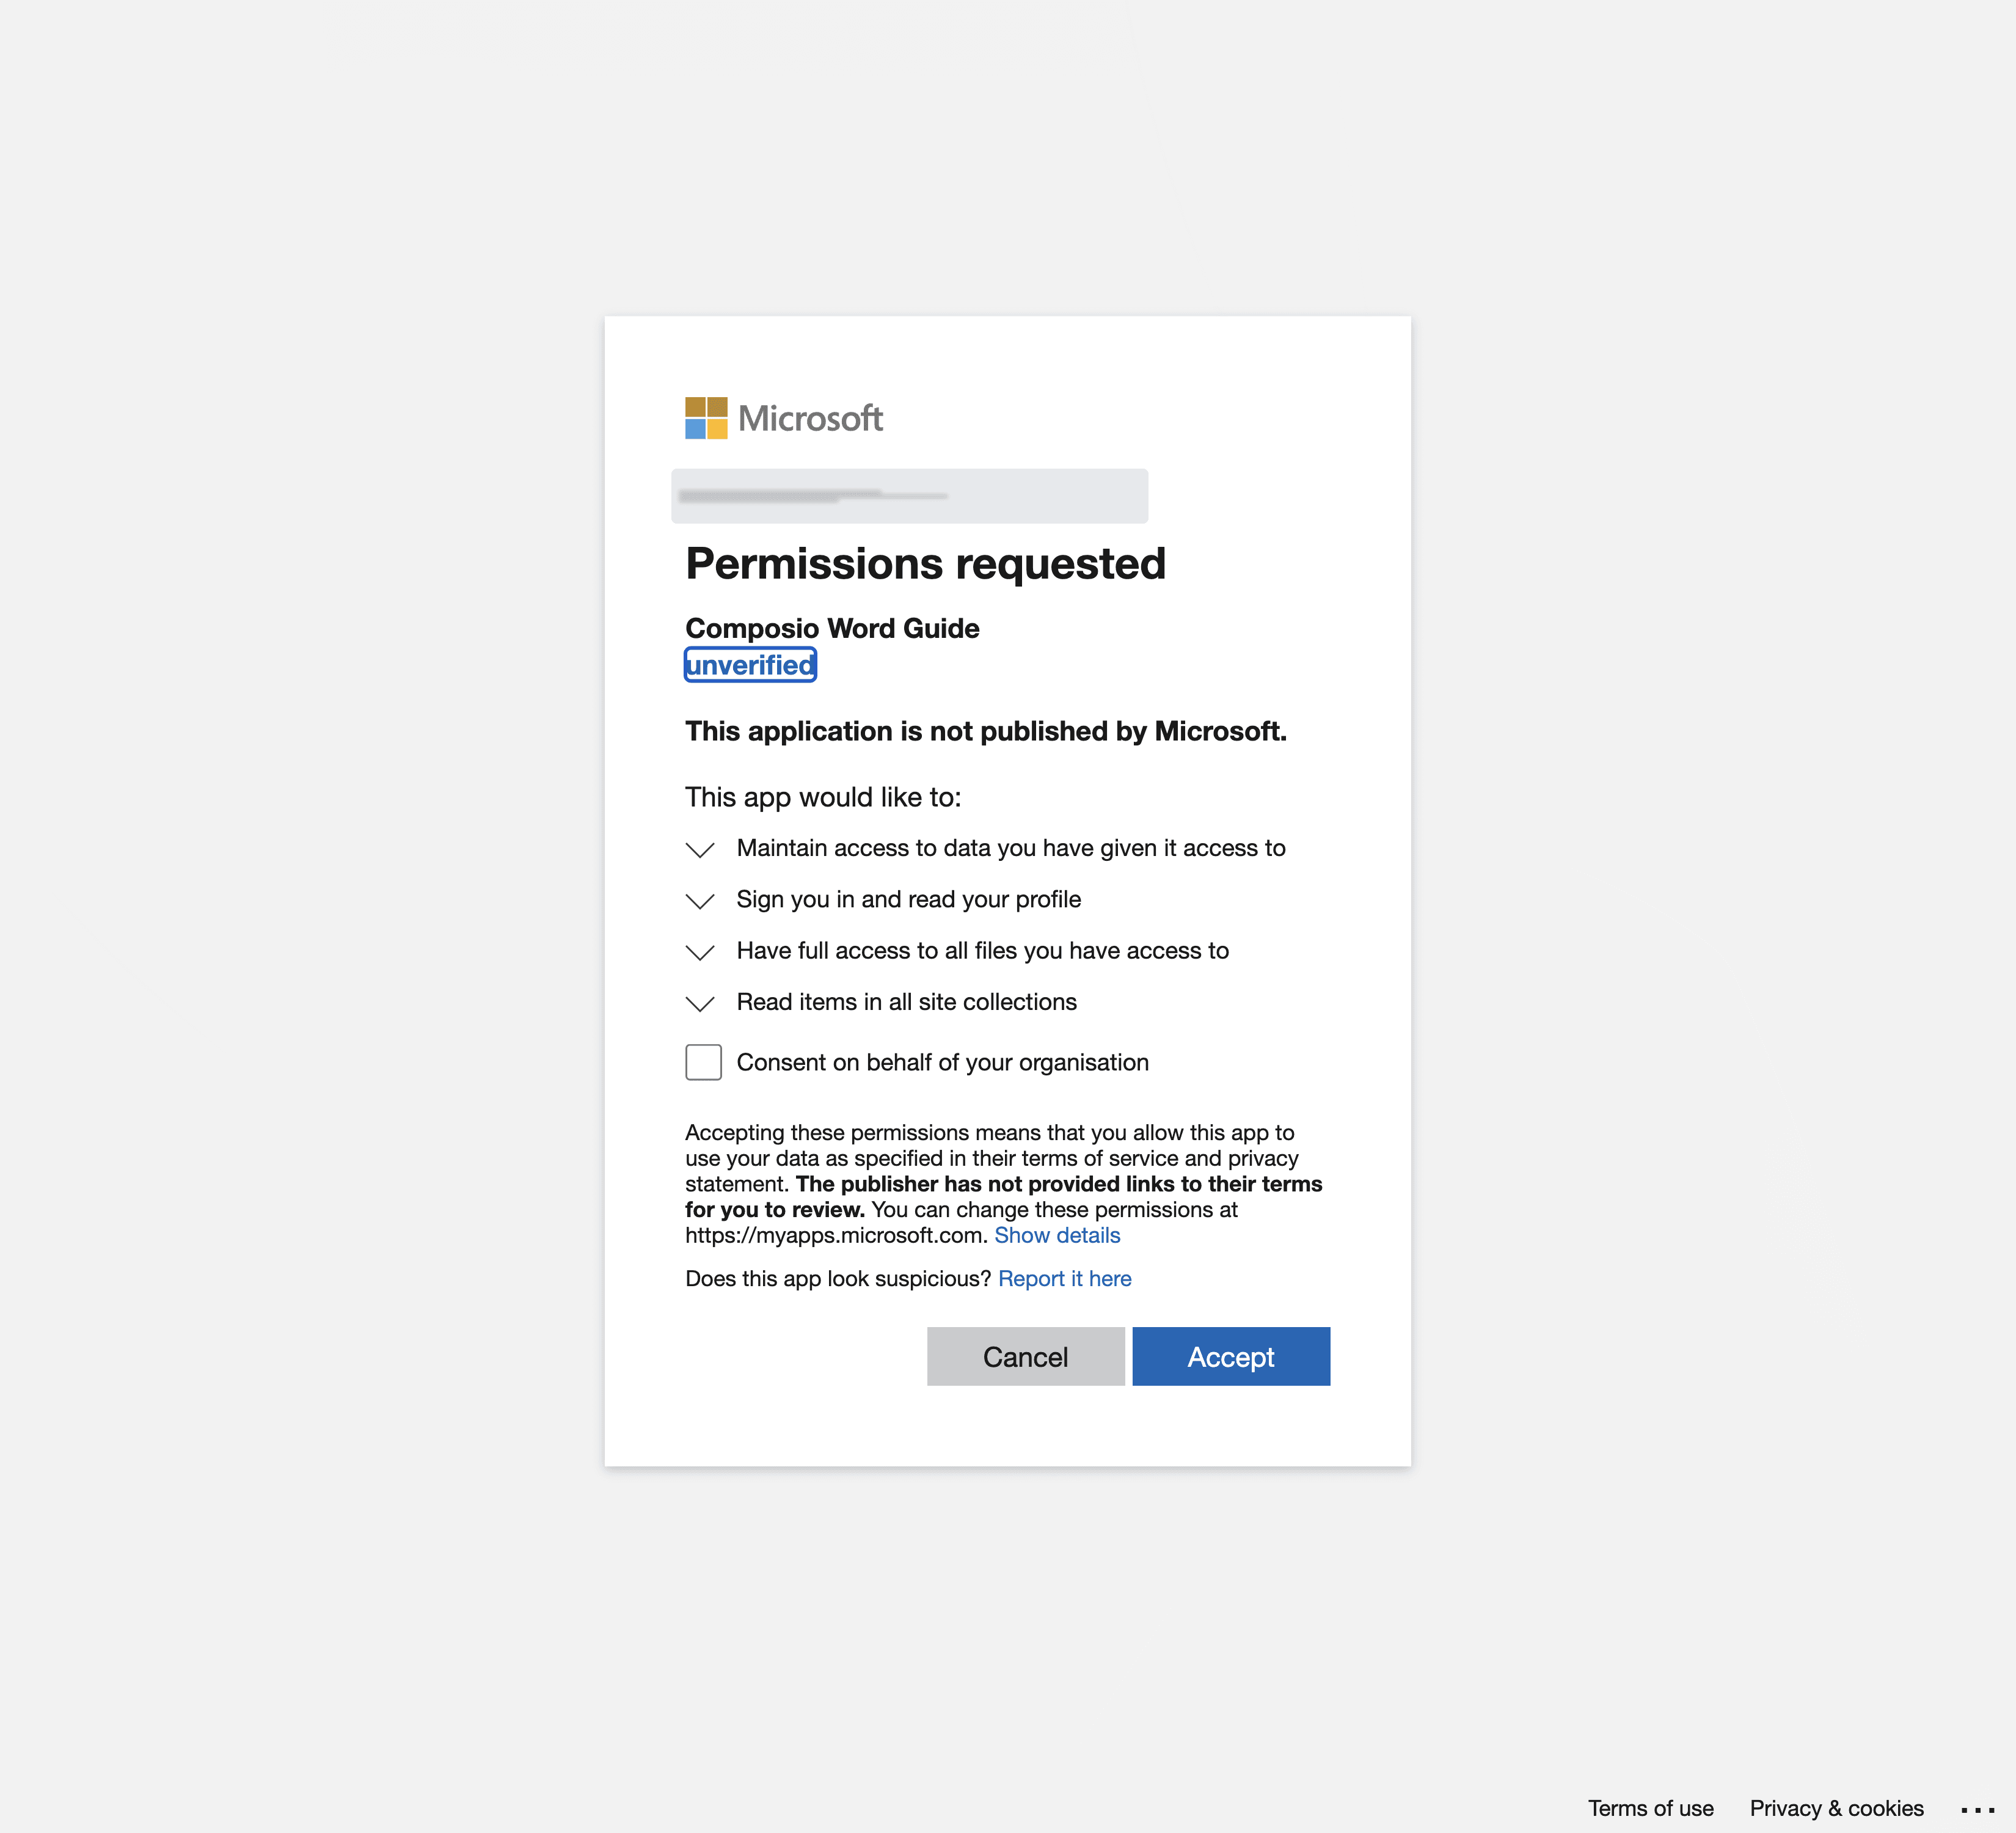
Always include only the permissions your workflow needs. Users must approve every permission when they connect their account.
Part 2: Create the auth config in Composio
With your Word credentials ready, navigate to the Composio Dashboard.
Step 5: Create a Microsoft Word Auth Config
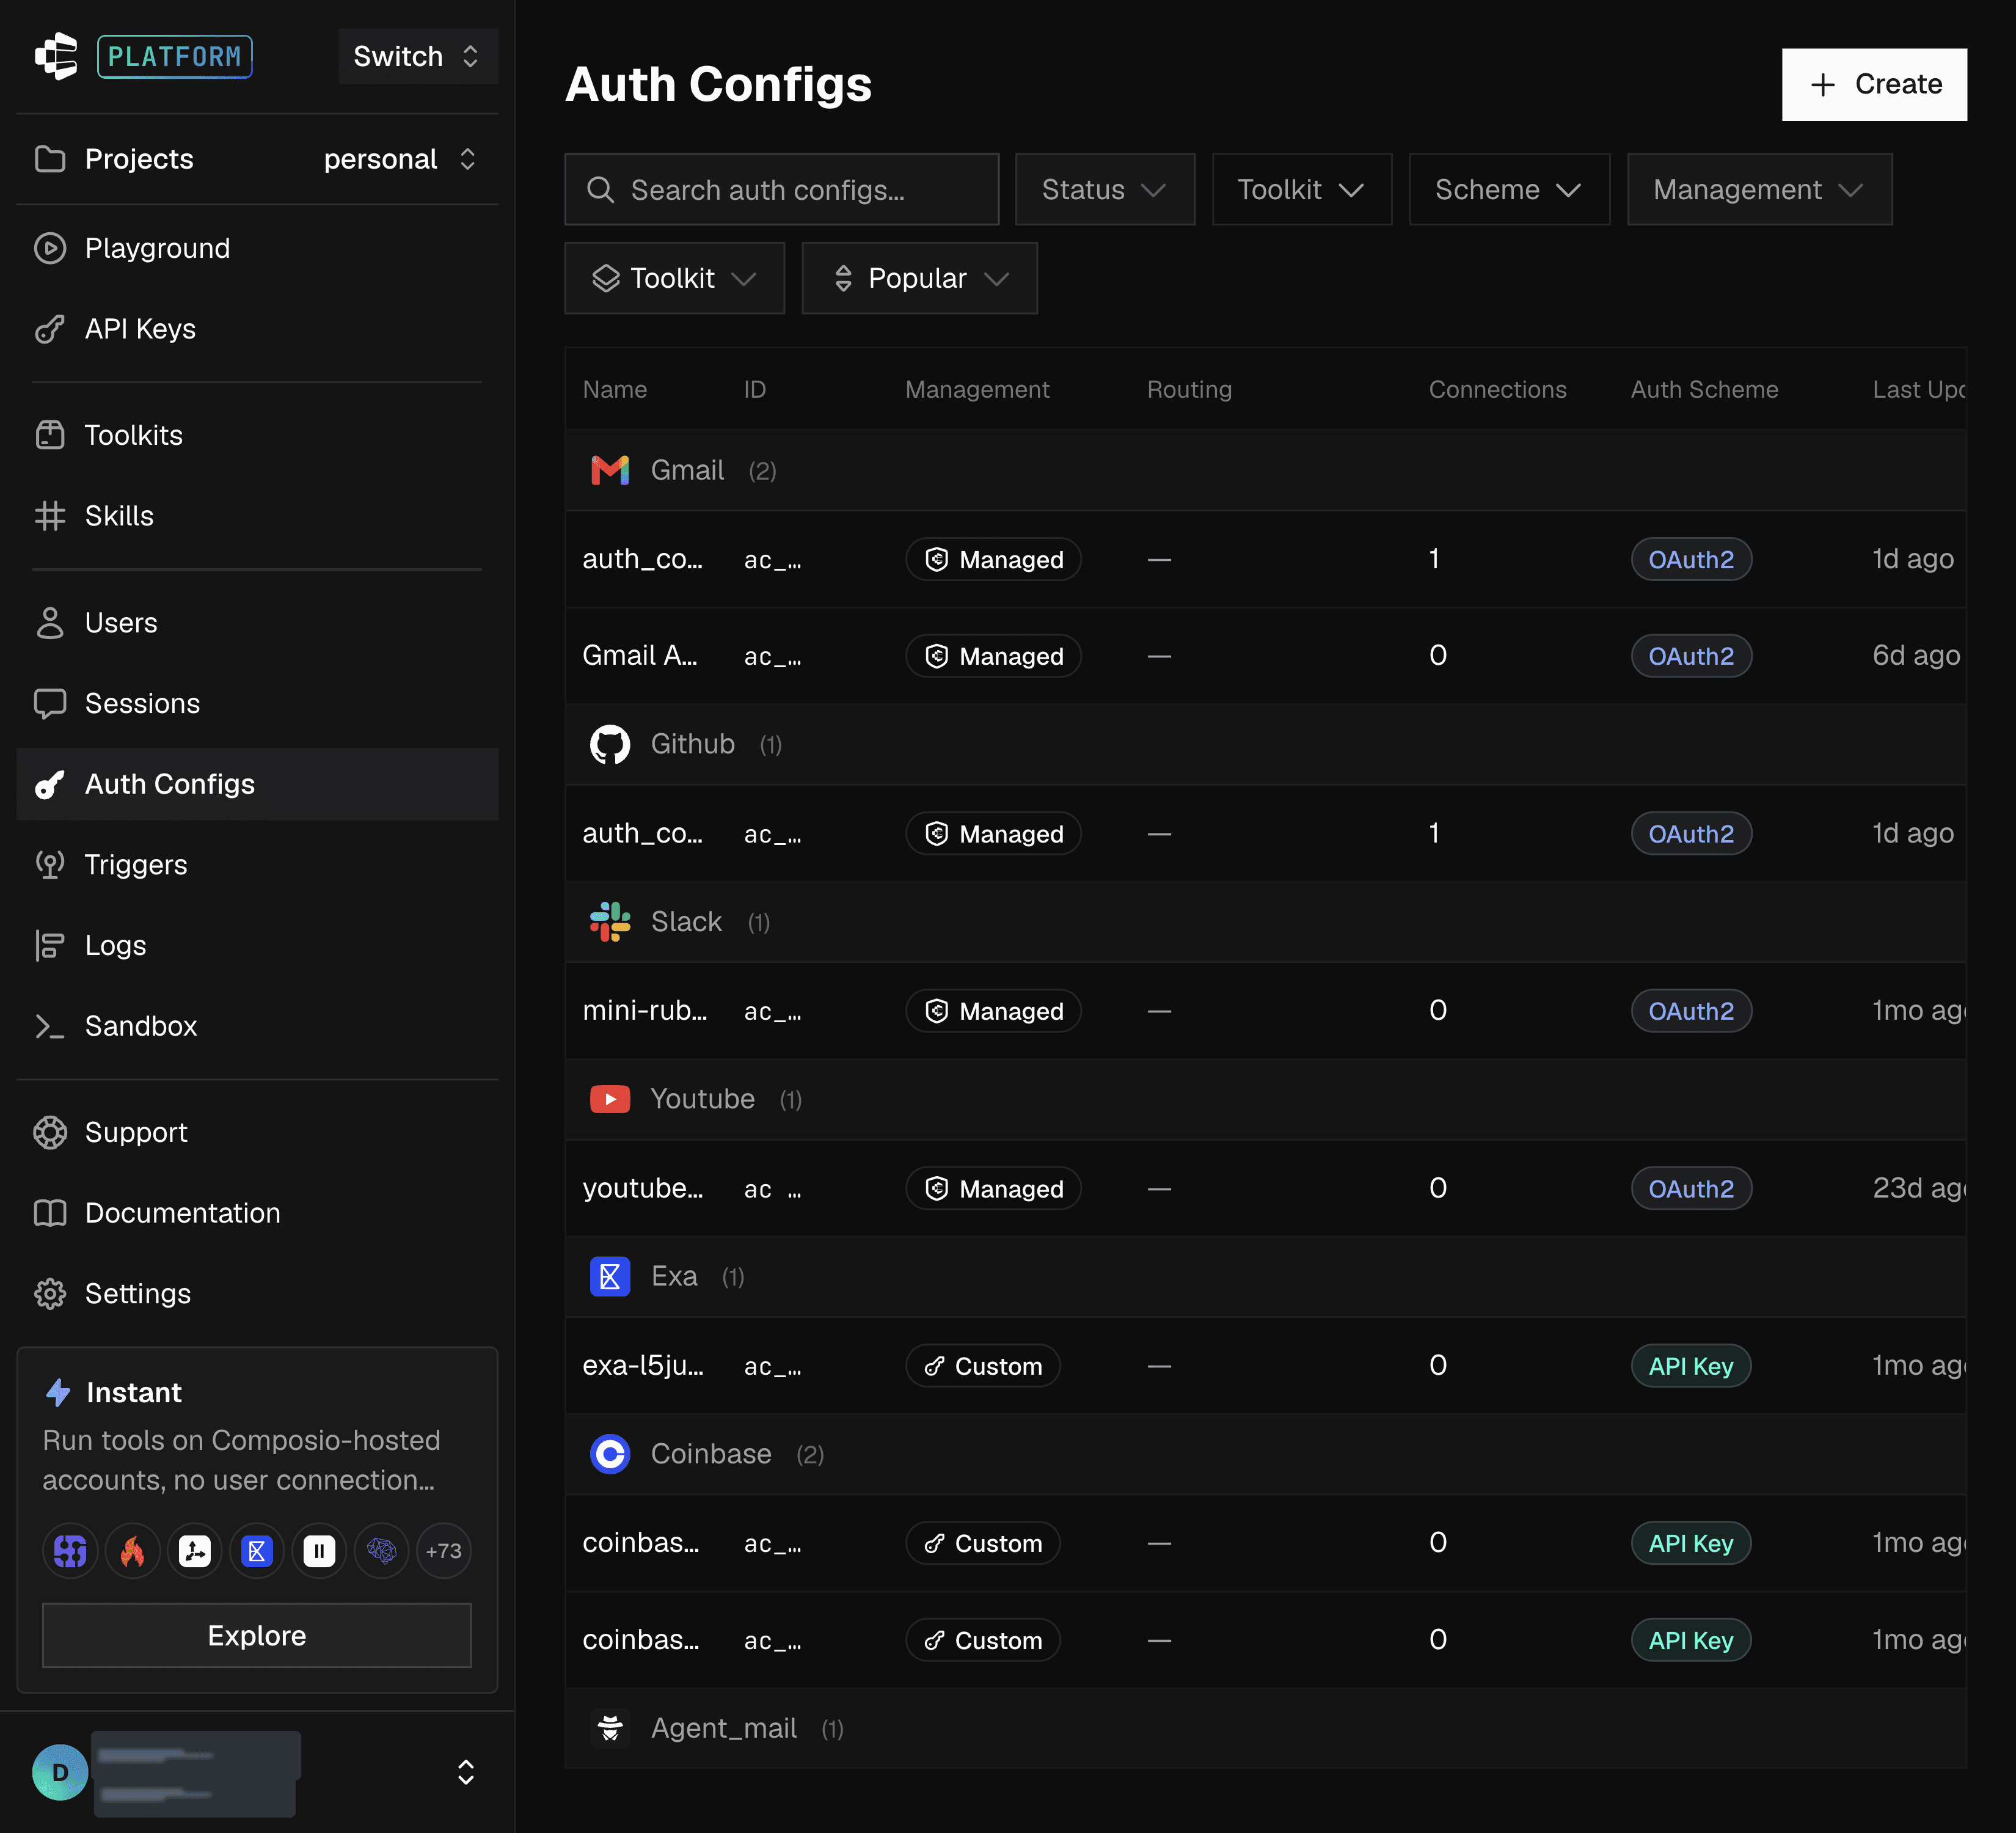
1. Go to Auth Configs in the Composio Dashboard and click Create.
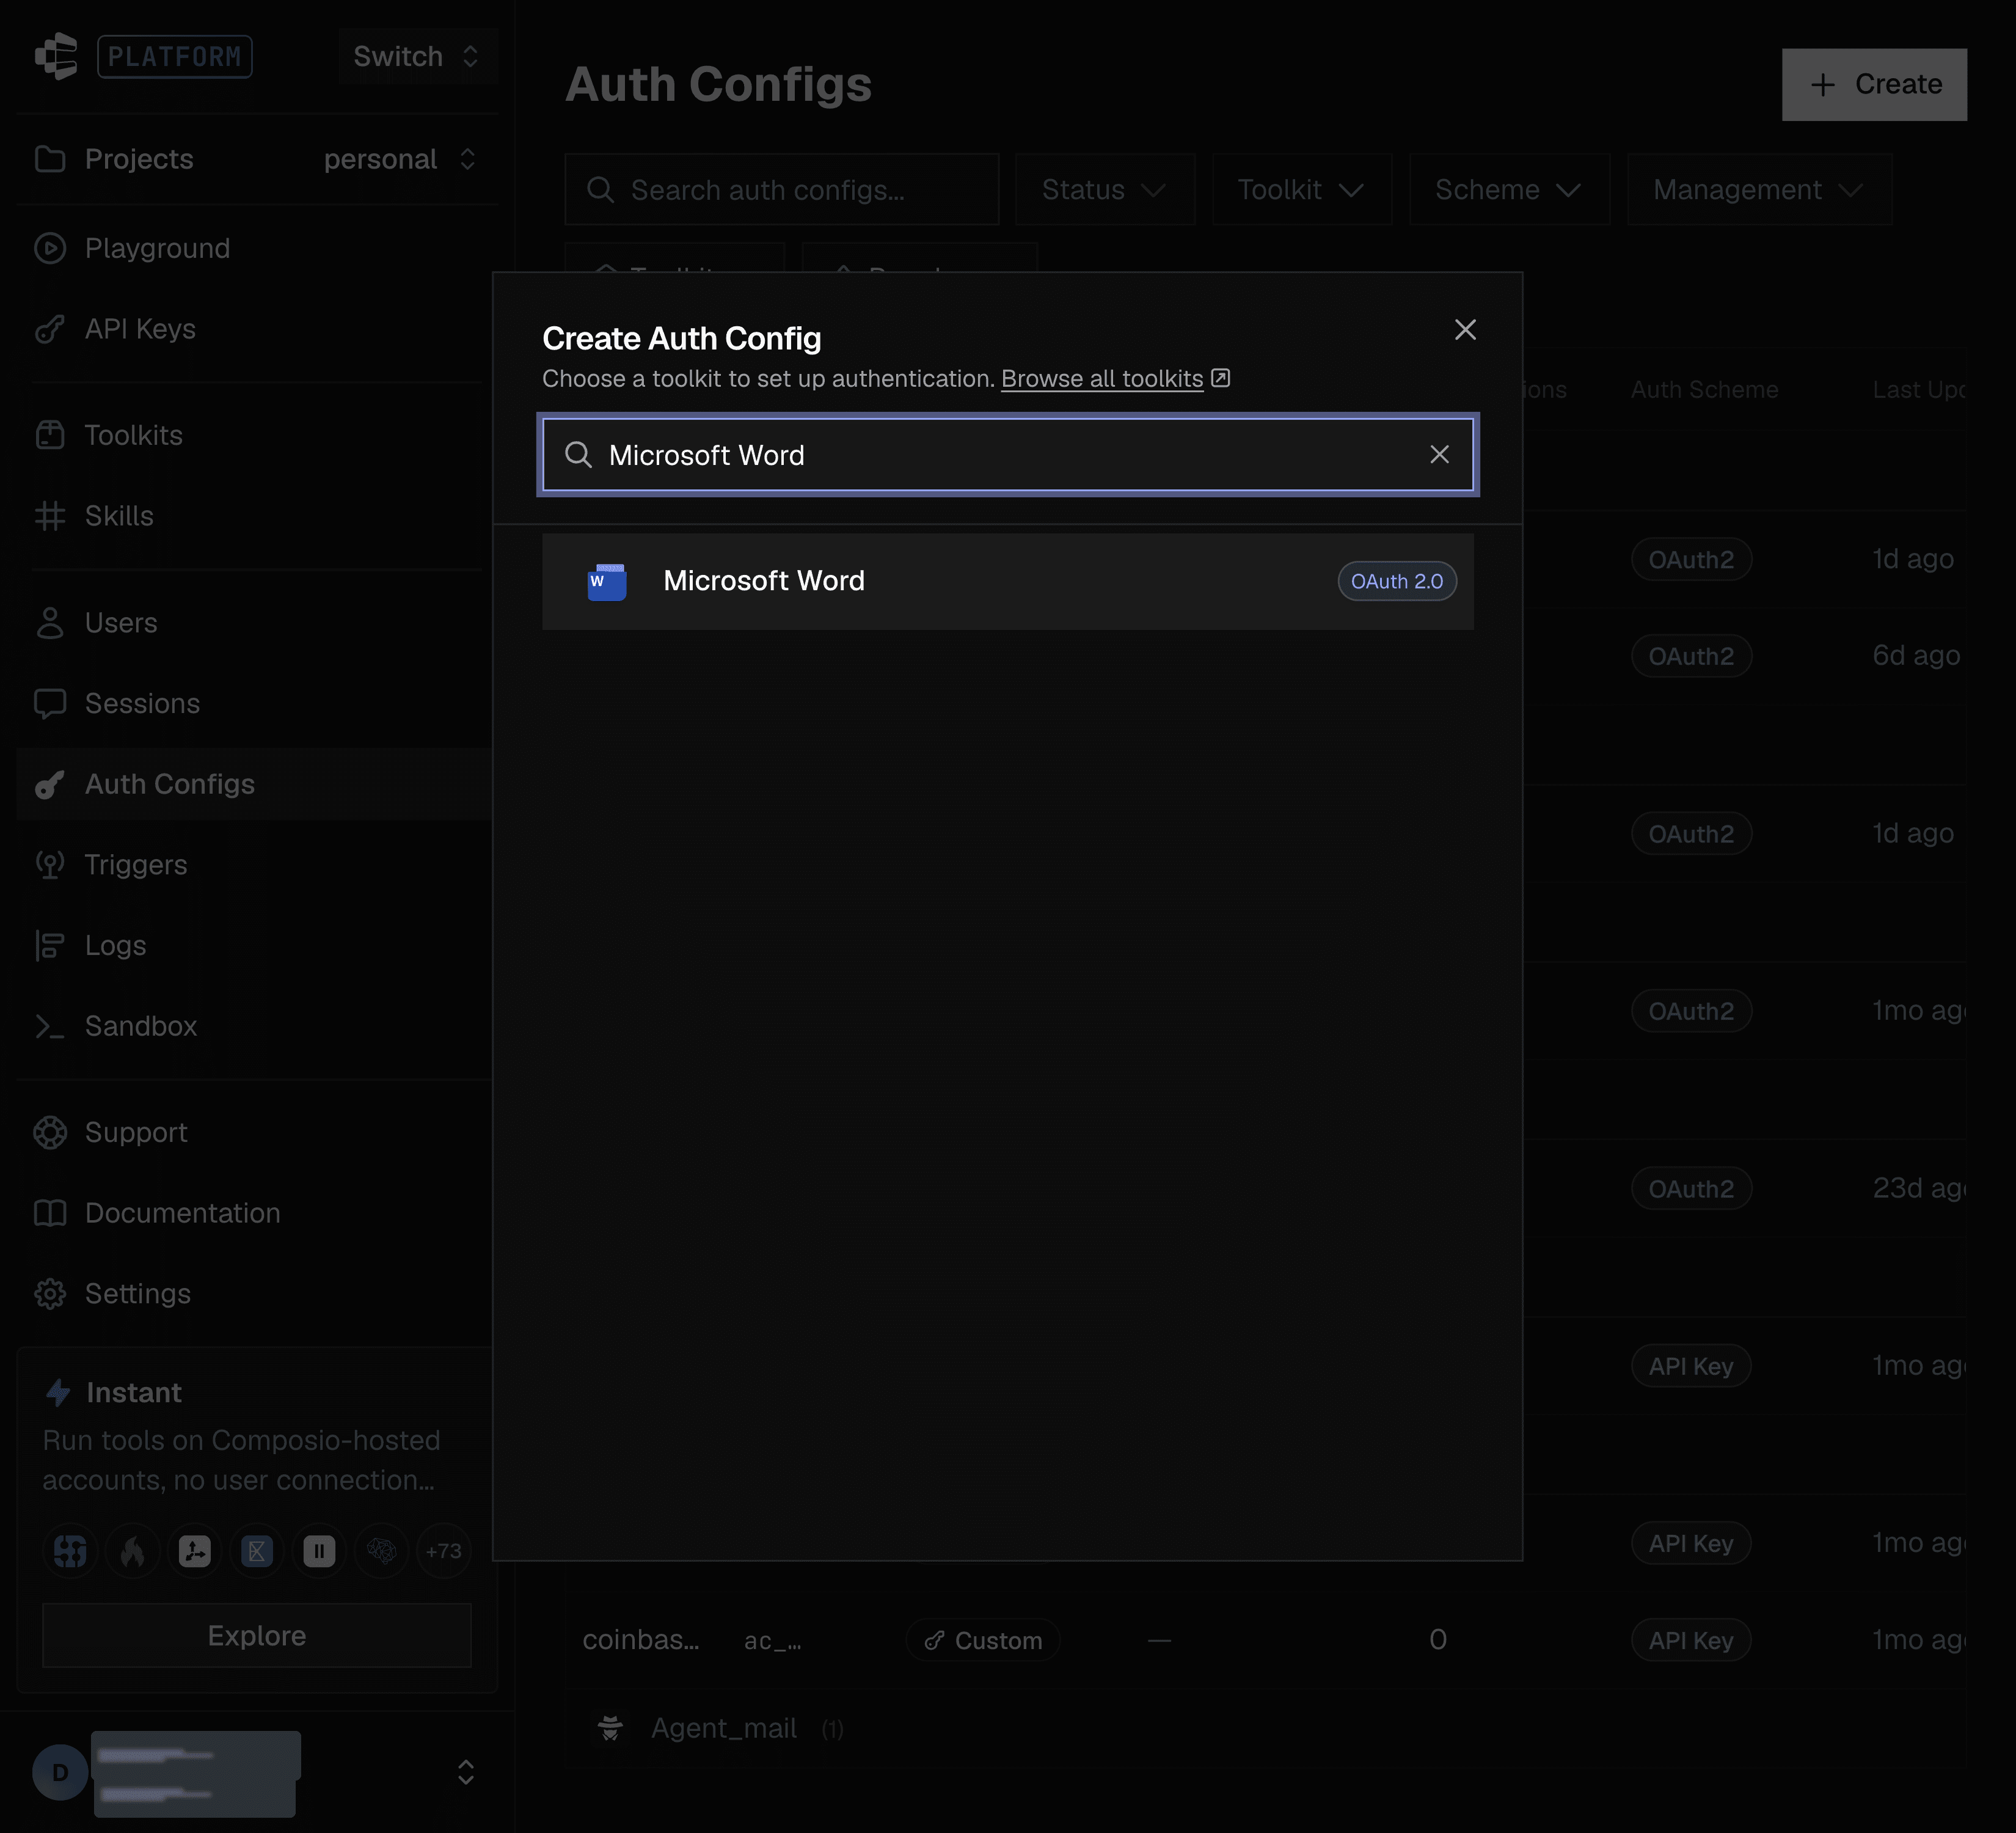
2. Search for Microsoft Word and select it from the results.
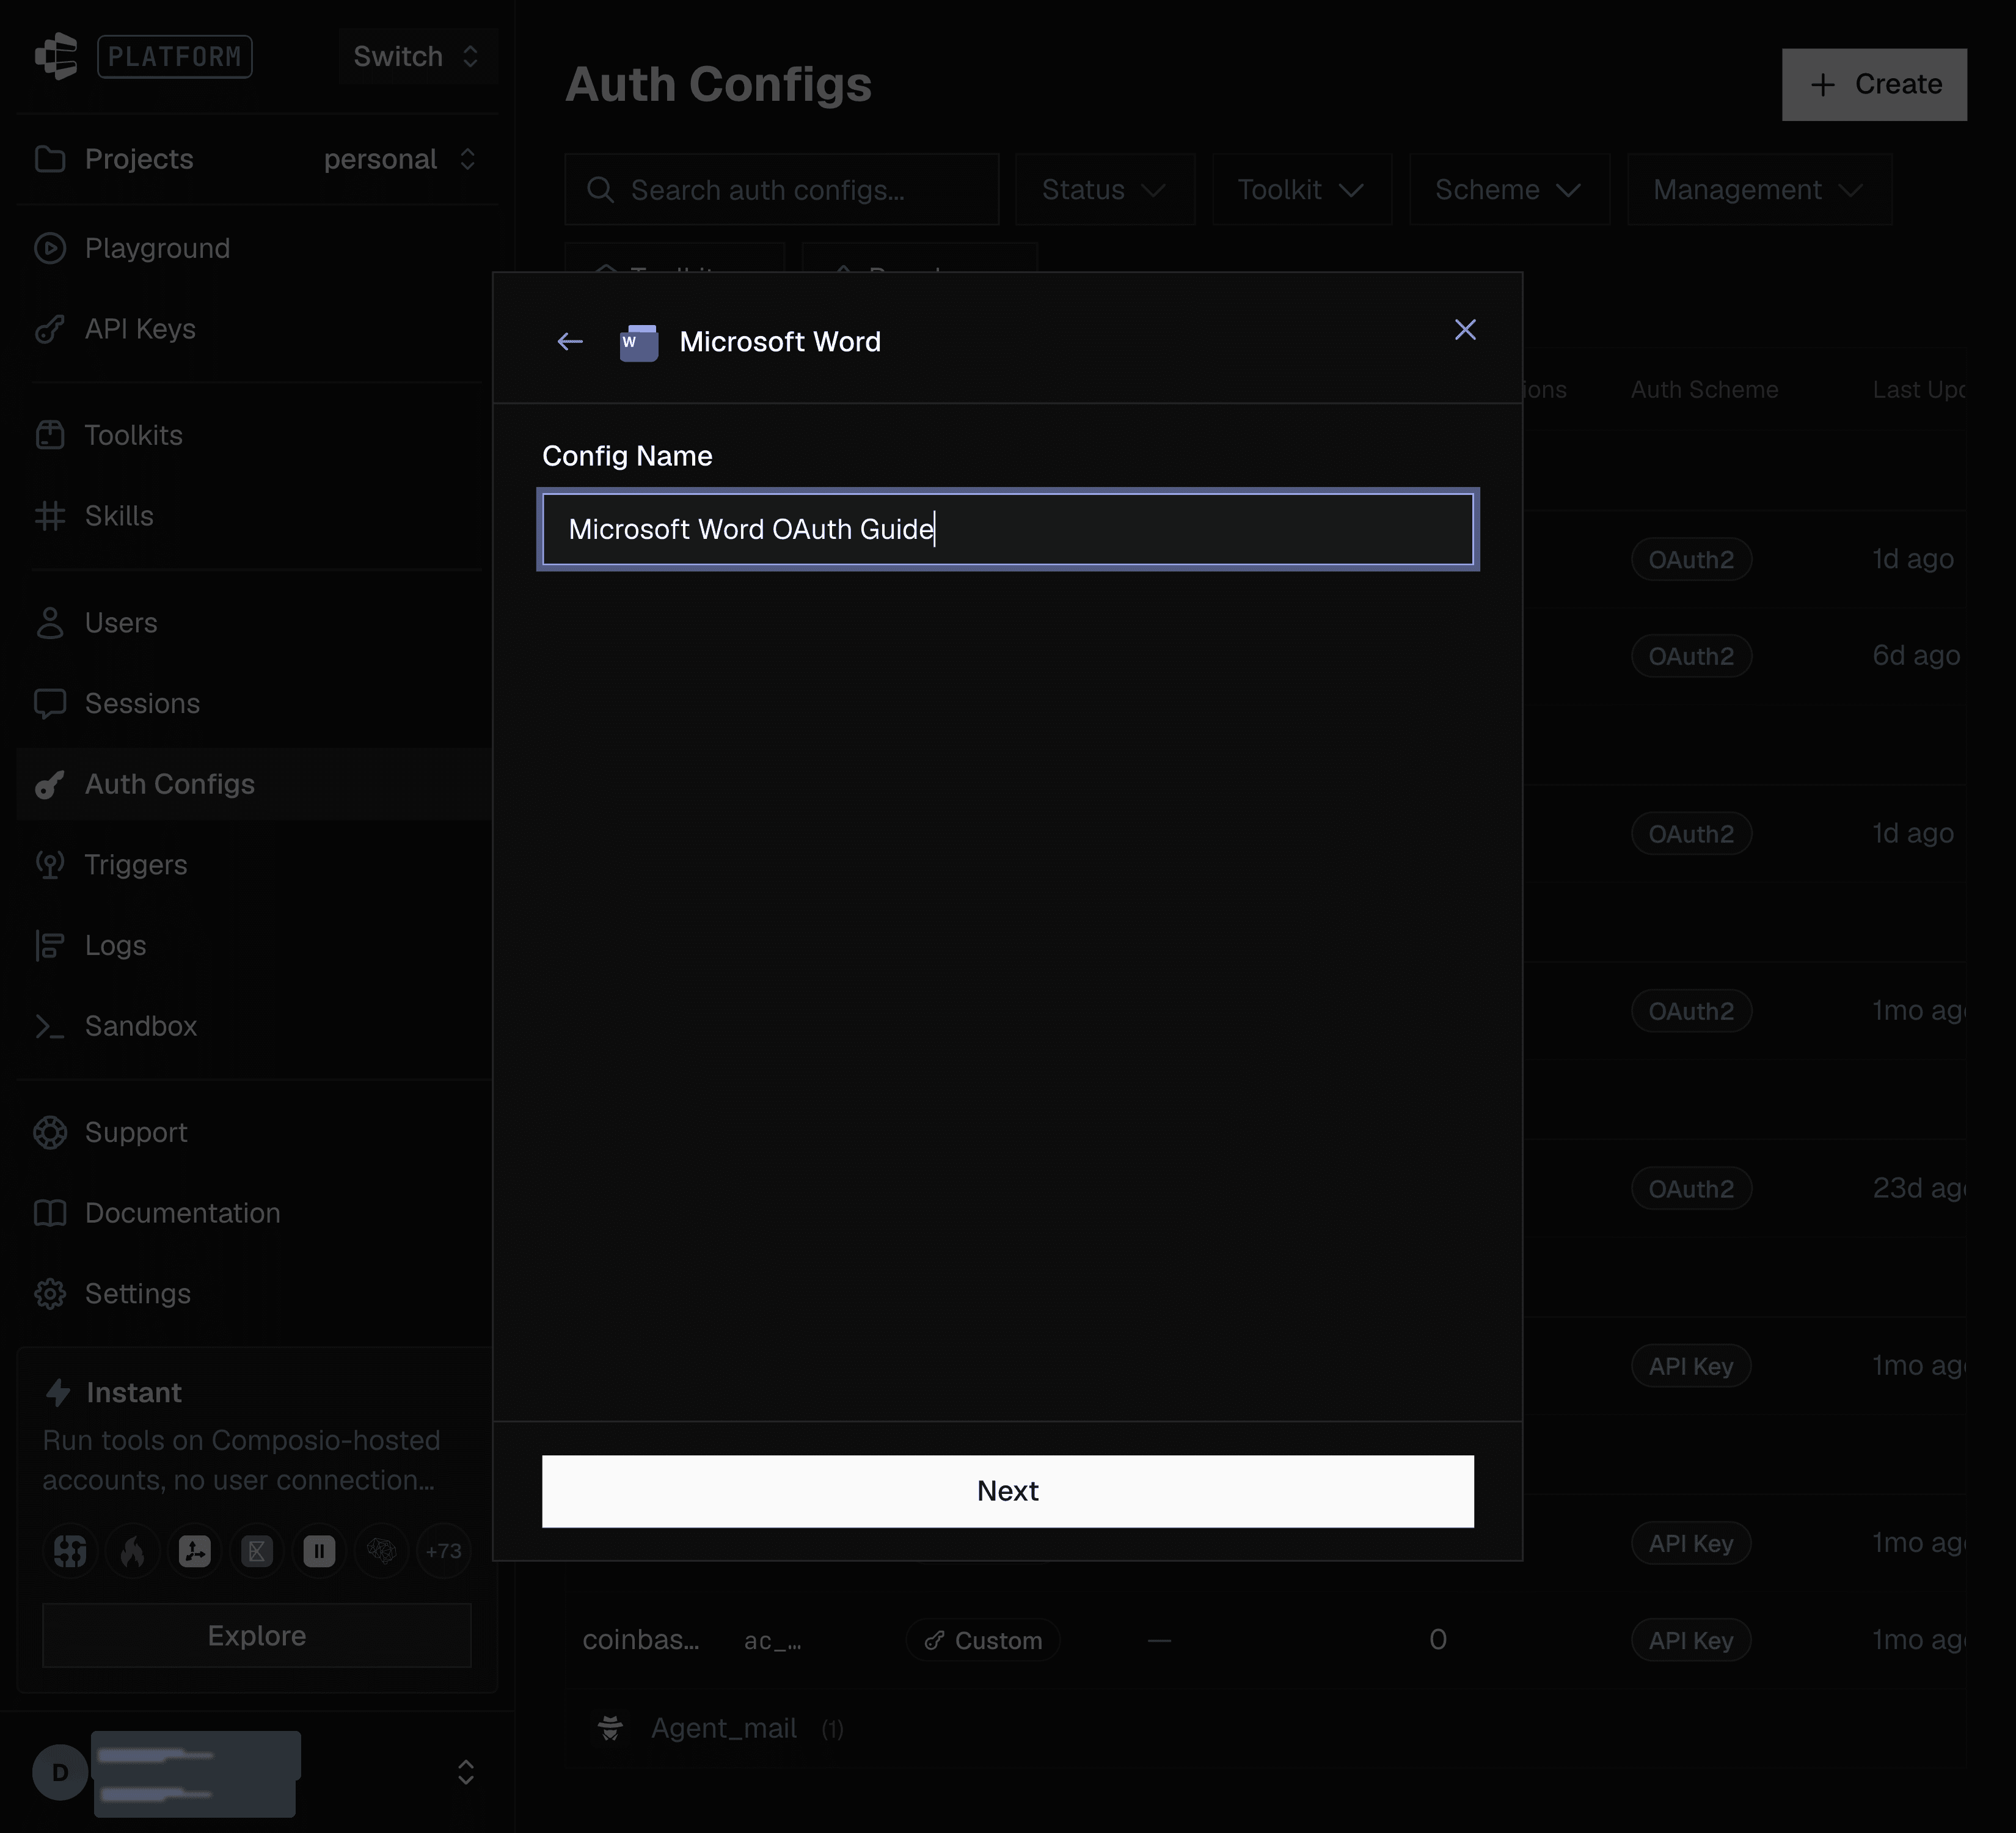
3. Enter a Config Name for your auth config and click Next.
Step 6: Enter Your Own Credentials
1. Under Authentication Method, select OAuth 2.0.

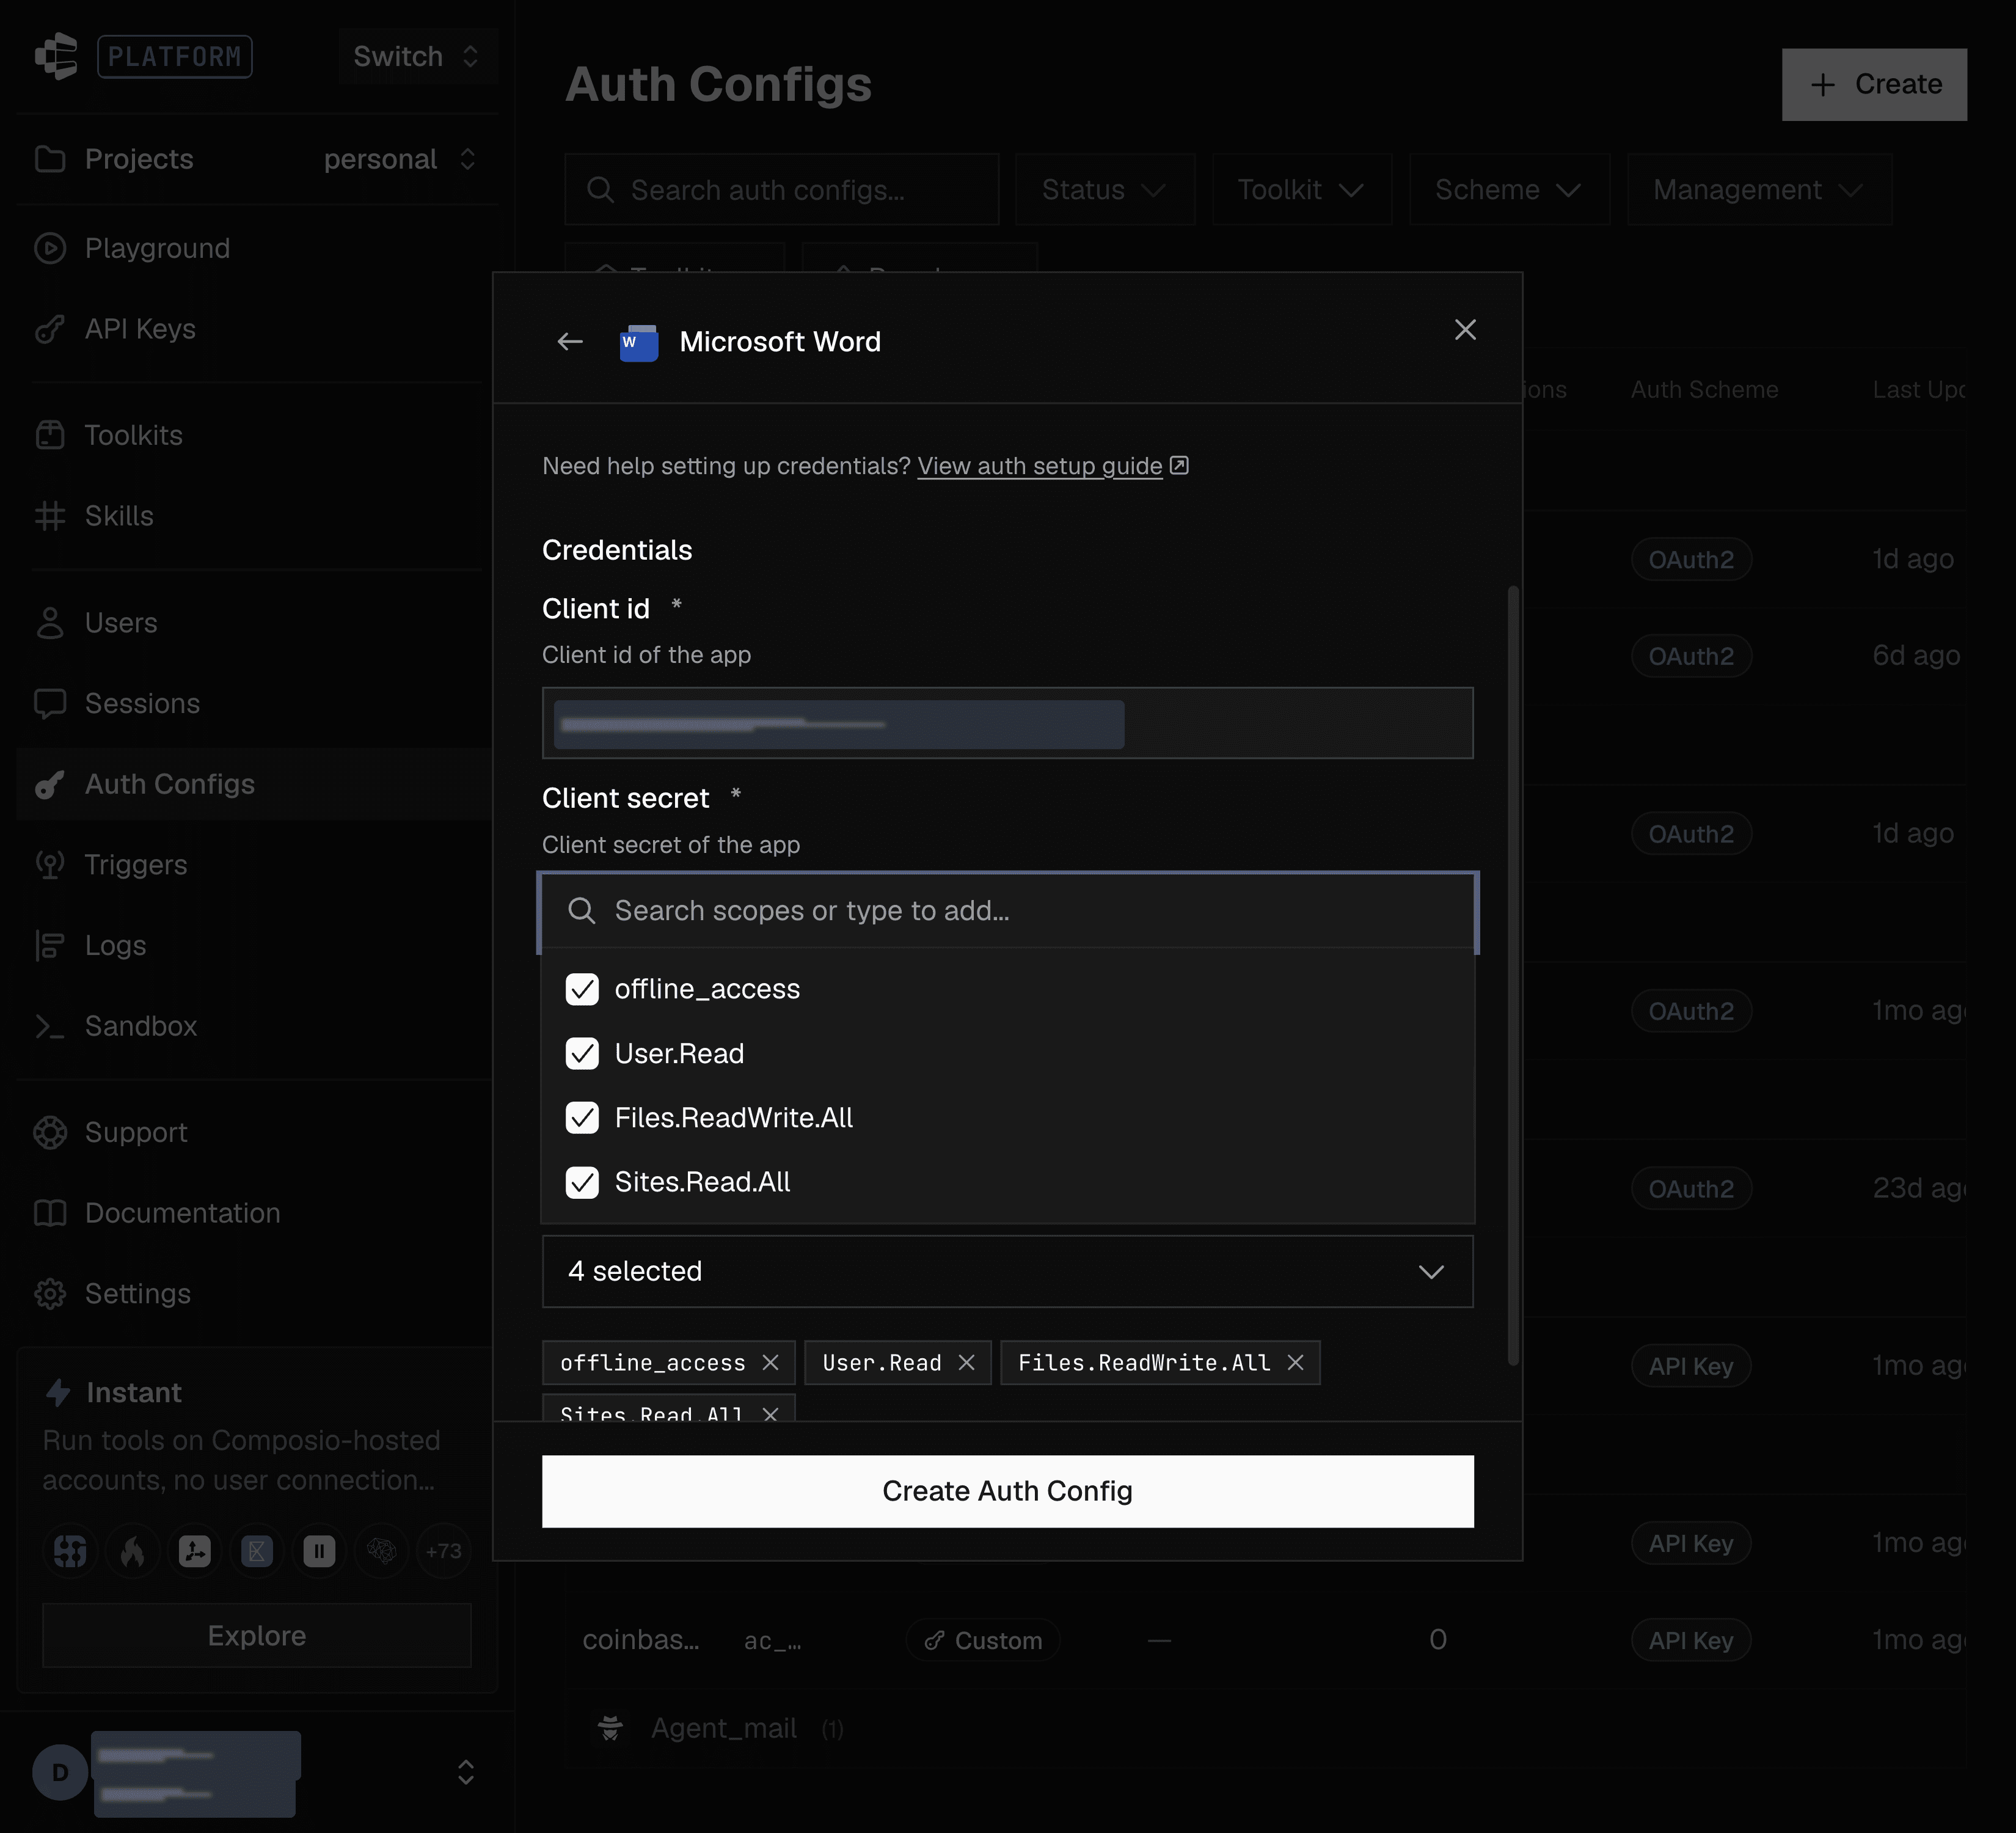
2. Paste the Client ID and Client Secret from your Azure app. Make sure the Redirect URI matches the one added in Azure:
https://backend.composio.dev/api/v1/auth-apps/add3. Under Scopes, select offline_access, User.Read, Files.ReadWrite.All, and Sites.Read.All. These must match the permissions you added in Azure.
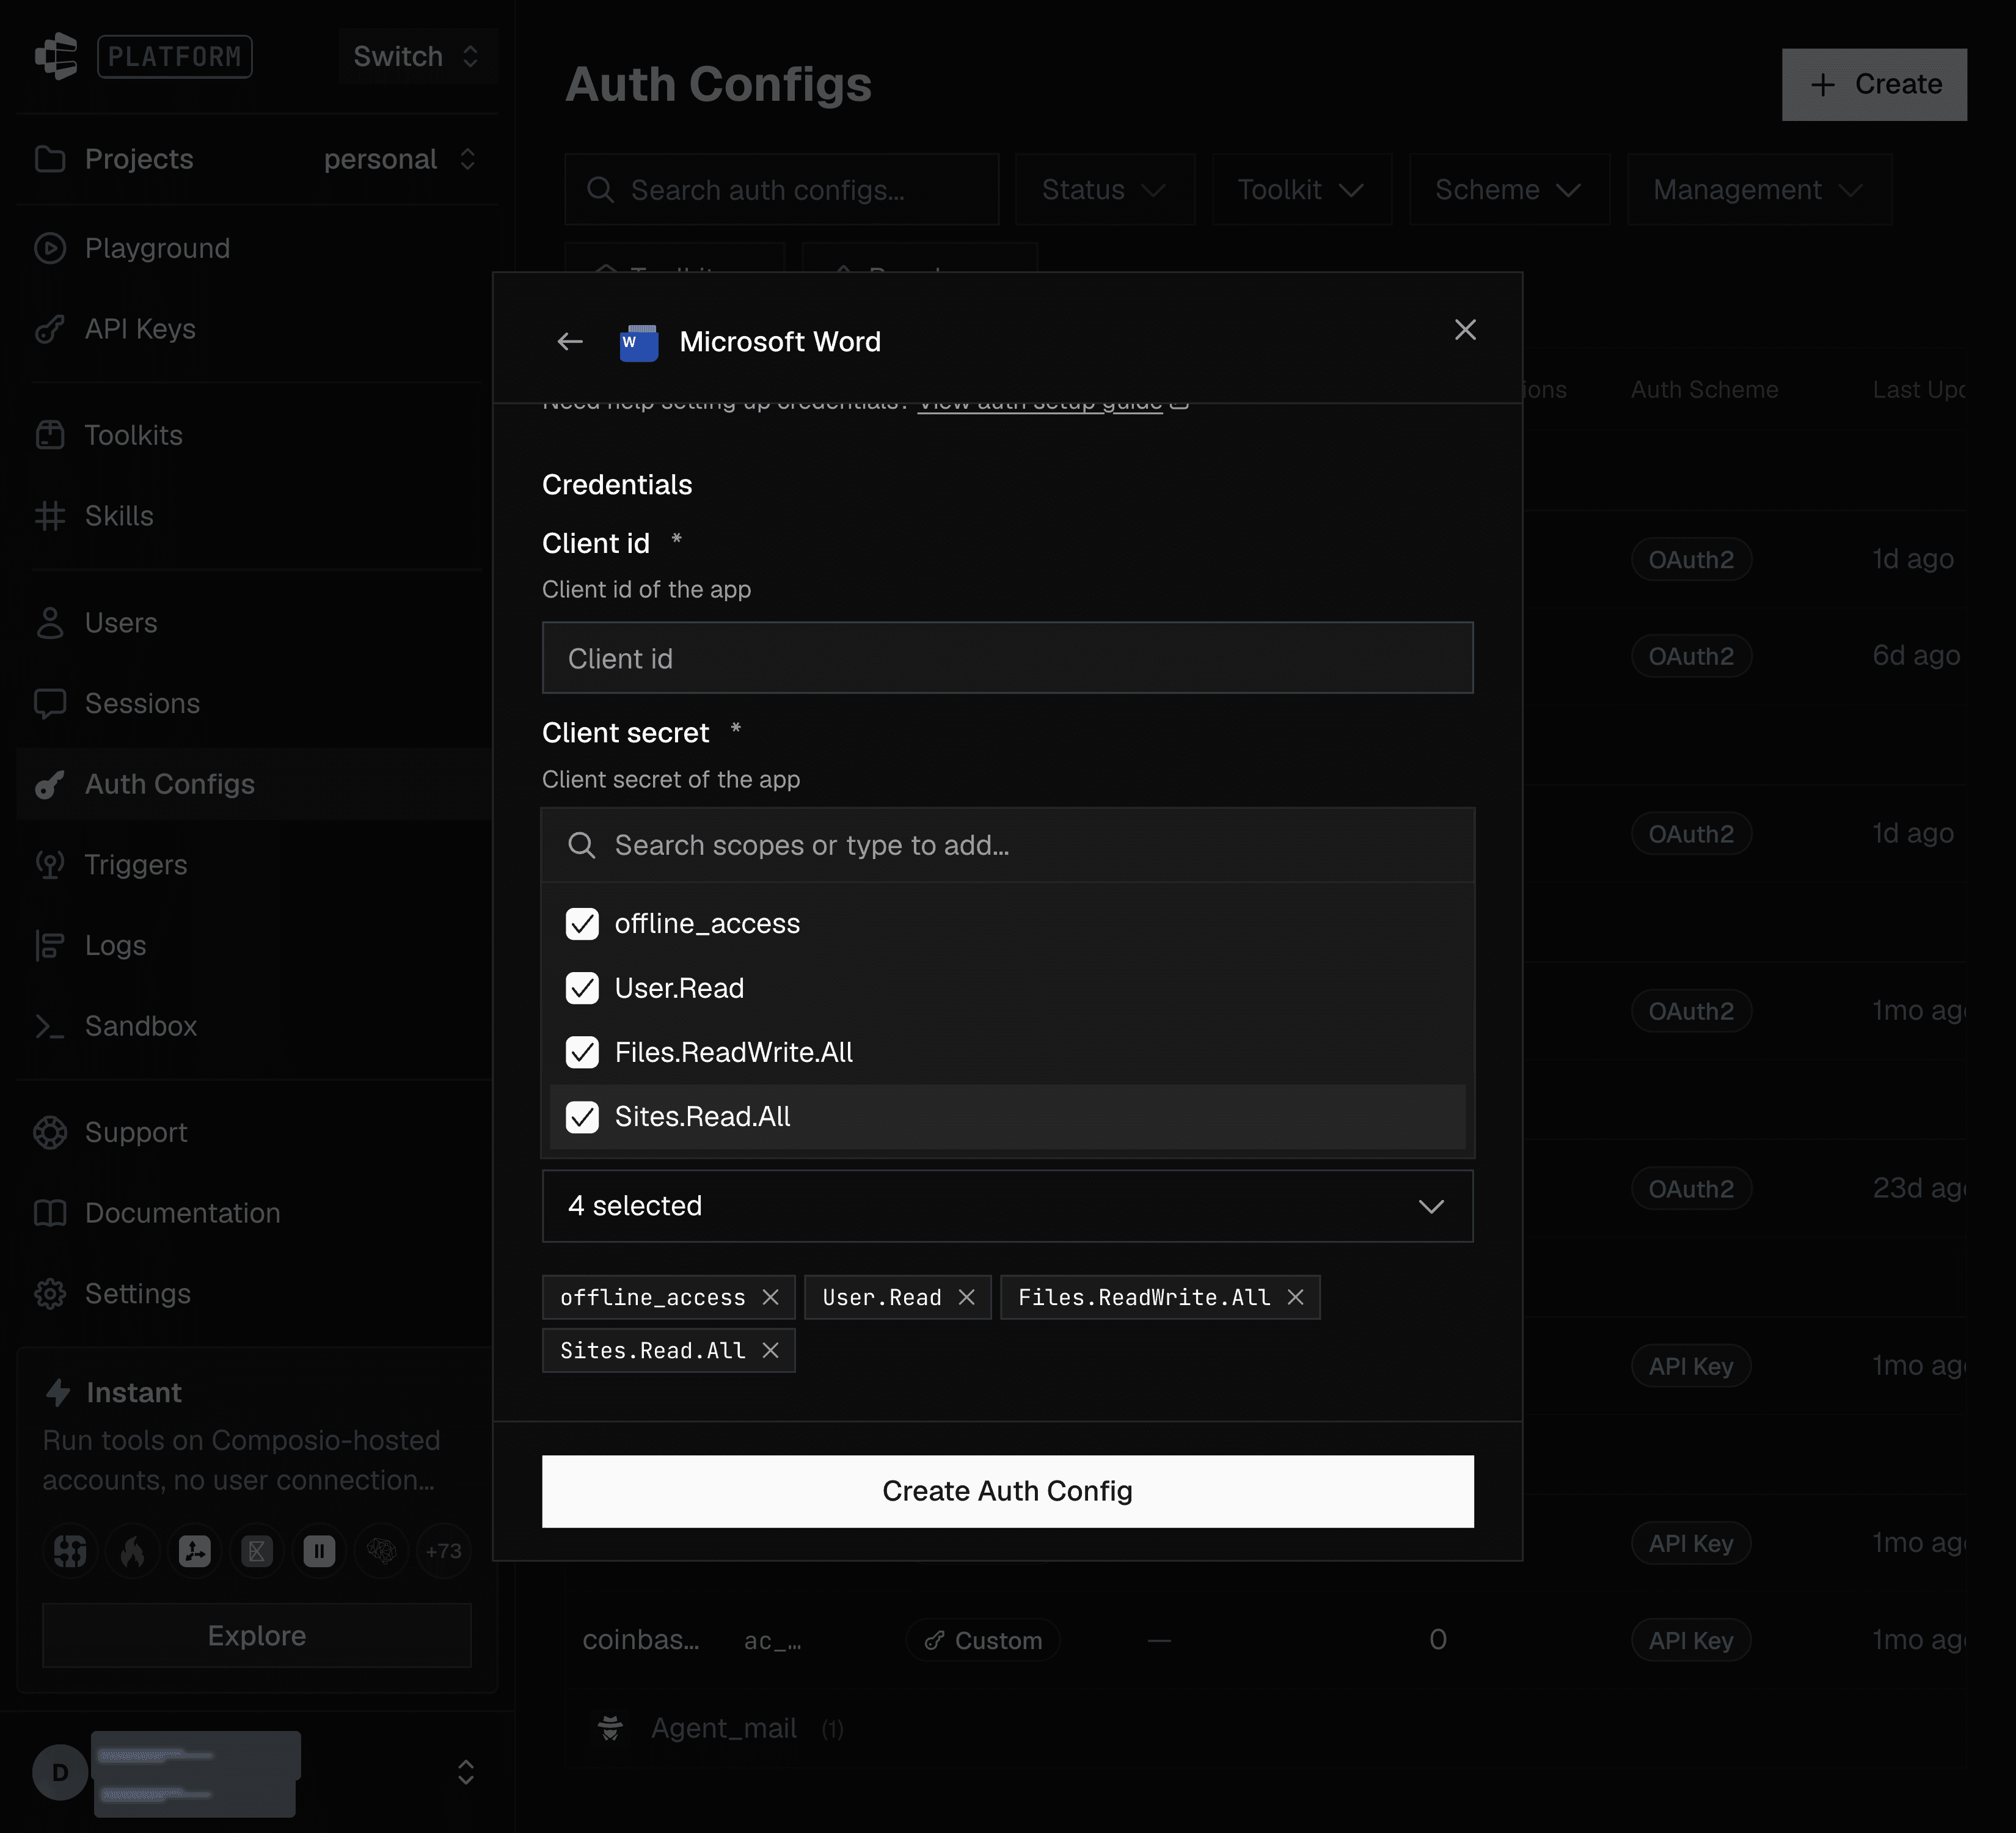
4. Click Create Auth Config.
Step 7: Connect Your Word Account
1. Open the auth config and click Connect Account. Then open the generated link.

2. Choose the Microsoft account you want to connect and sign in.
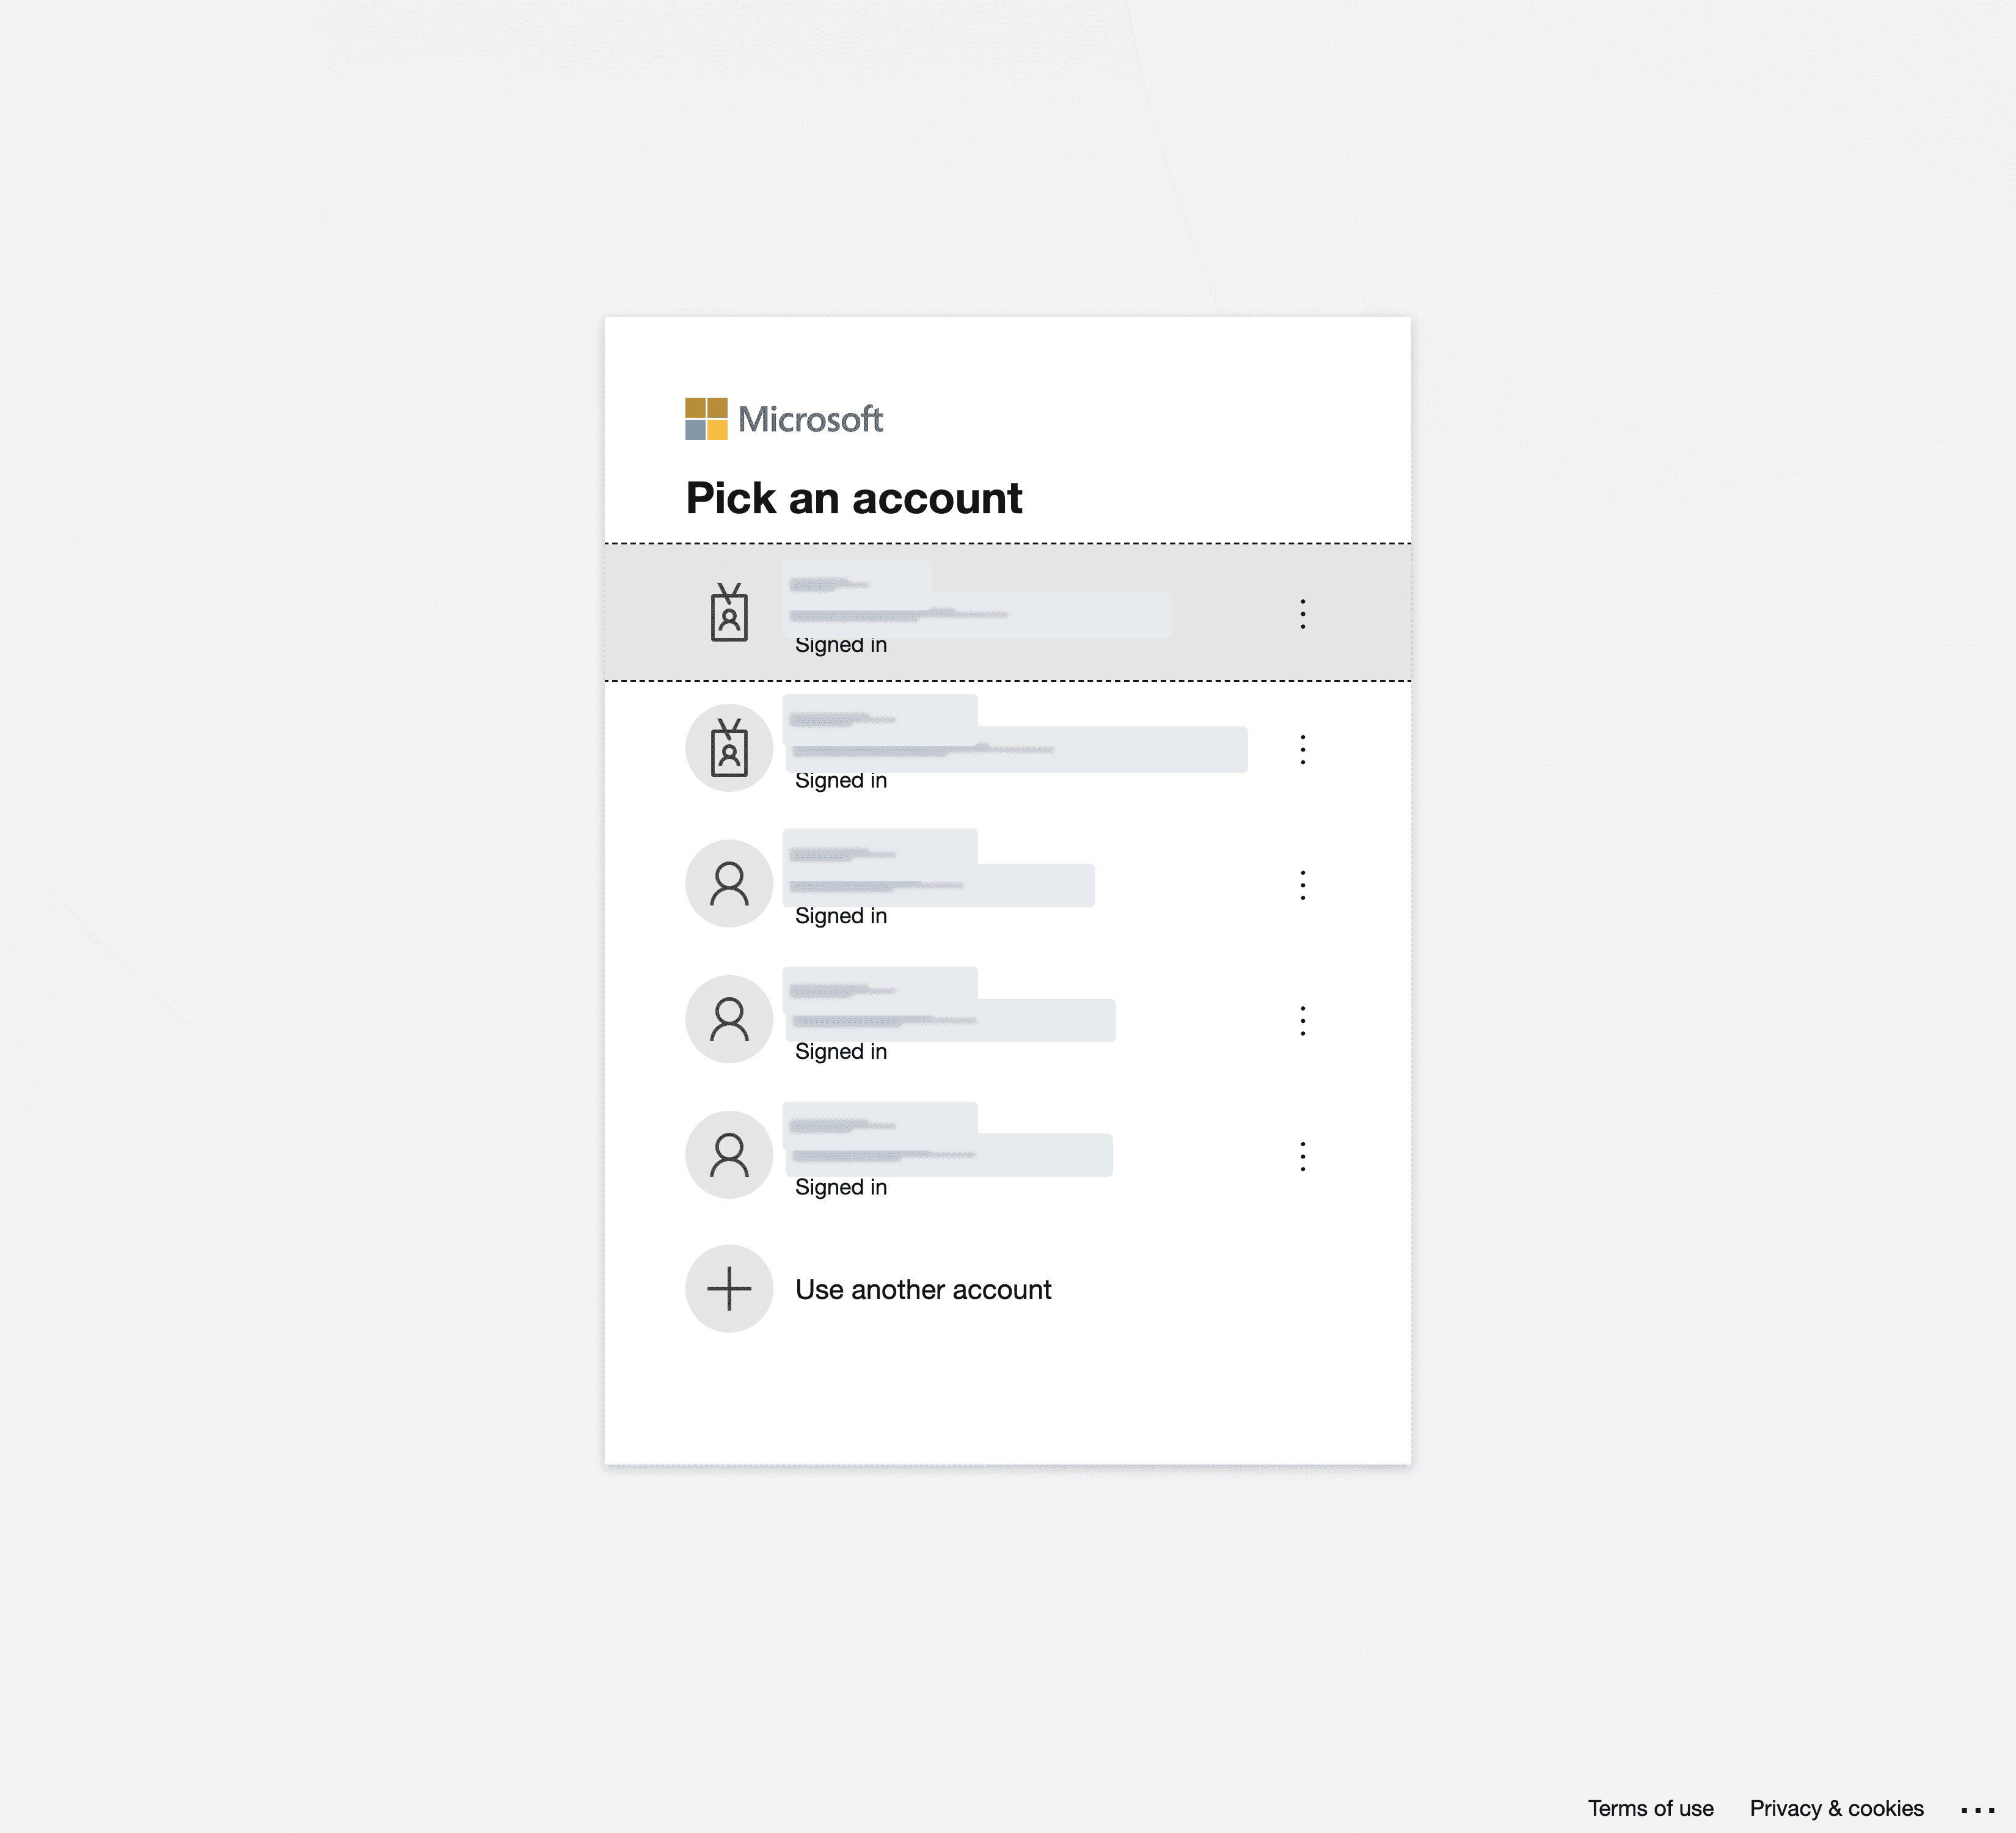
3. Review the requested permissions and click Accept. You may see an “unverified” label on a new app; that’s normal.
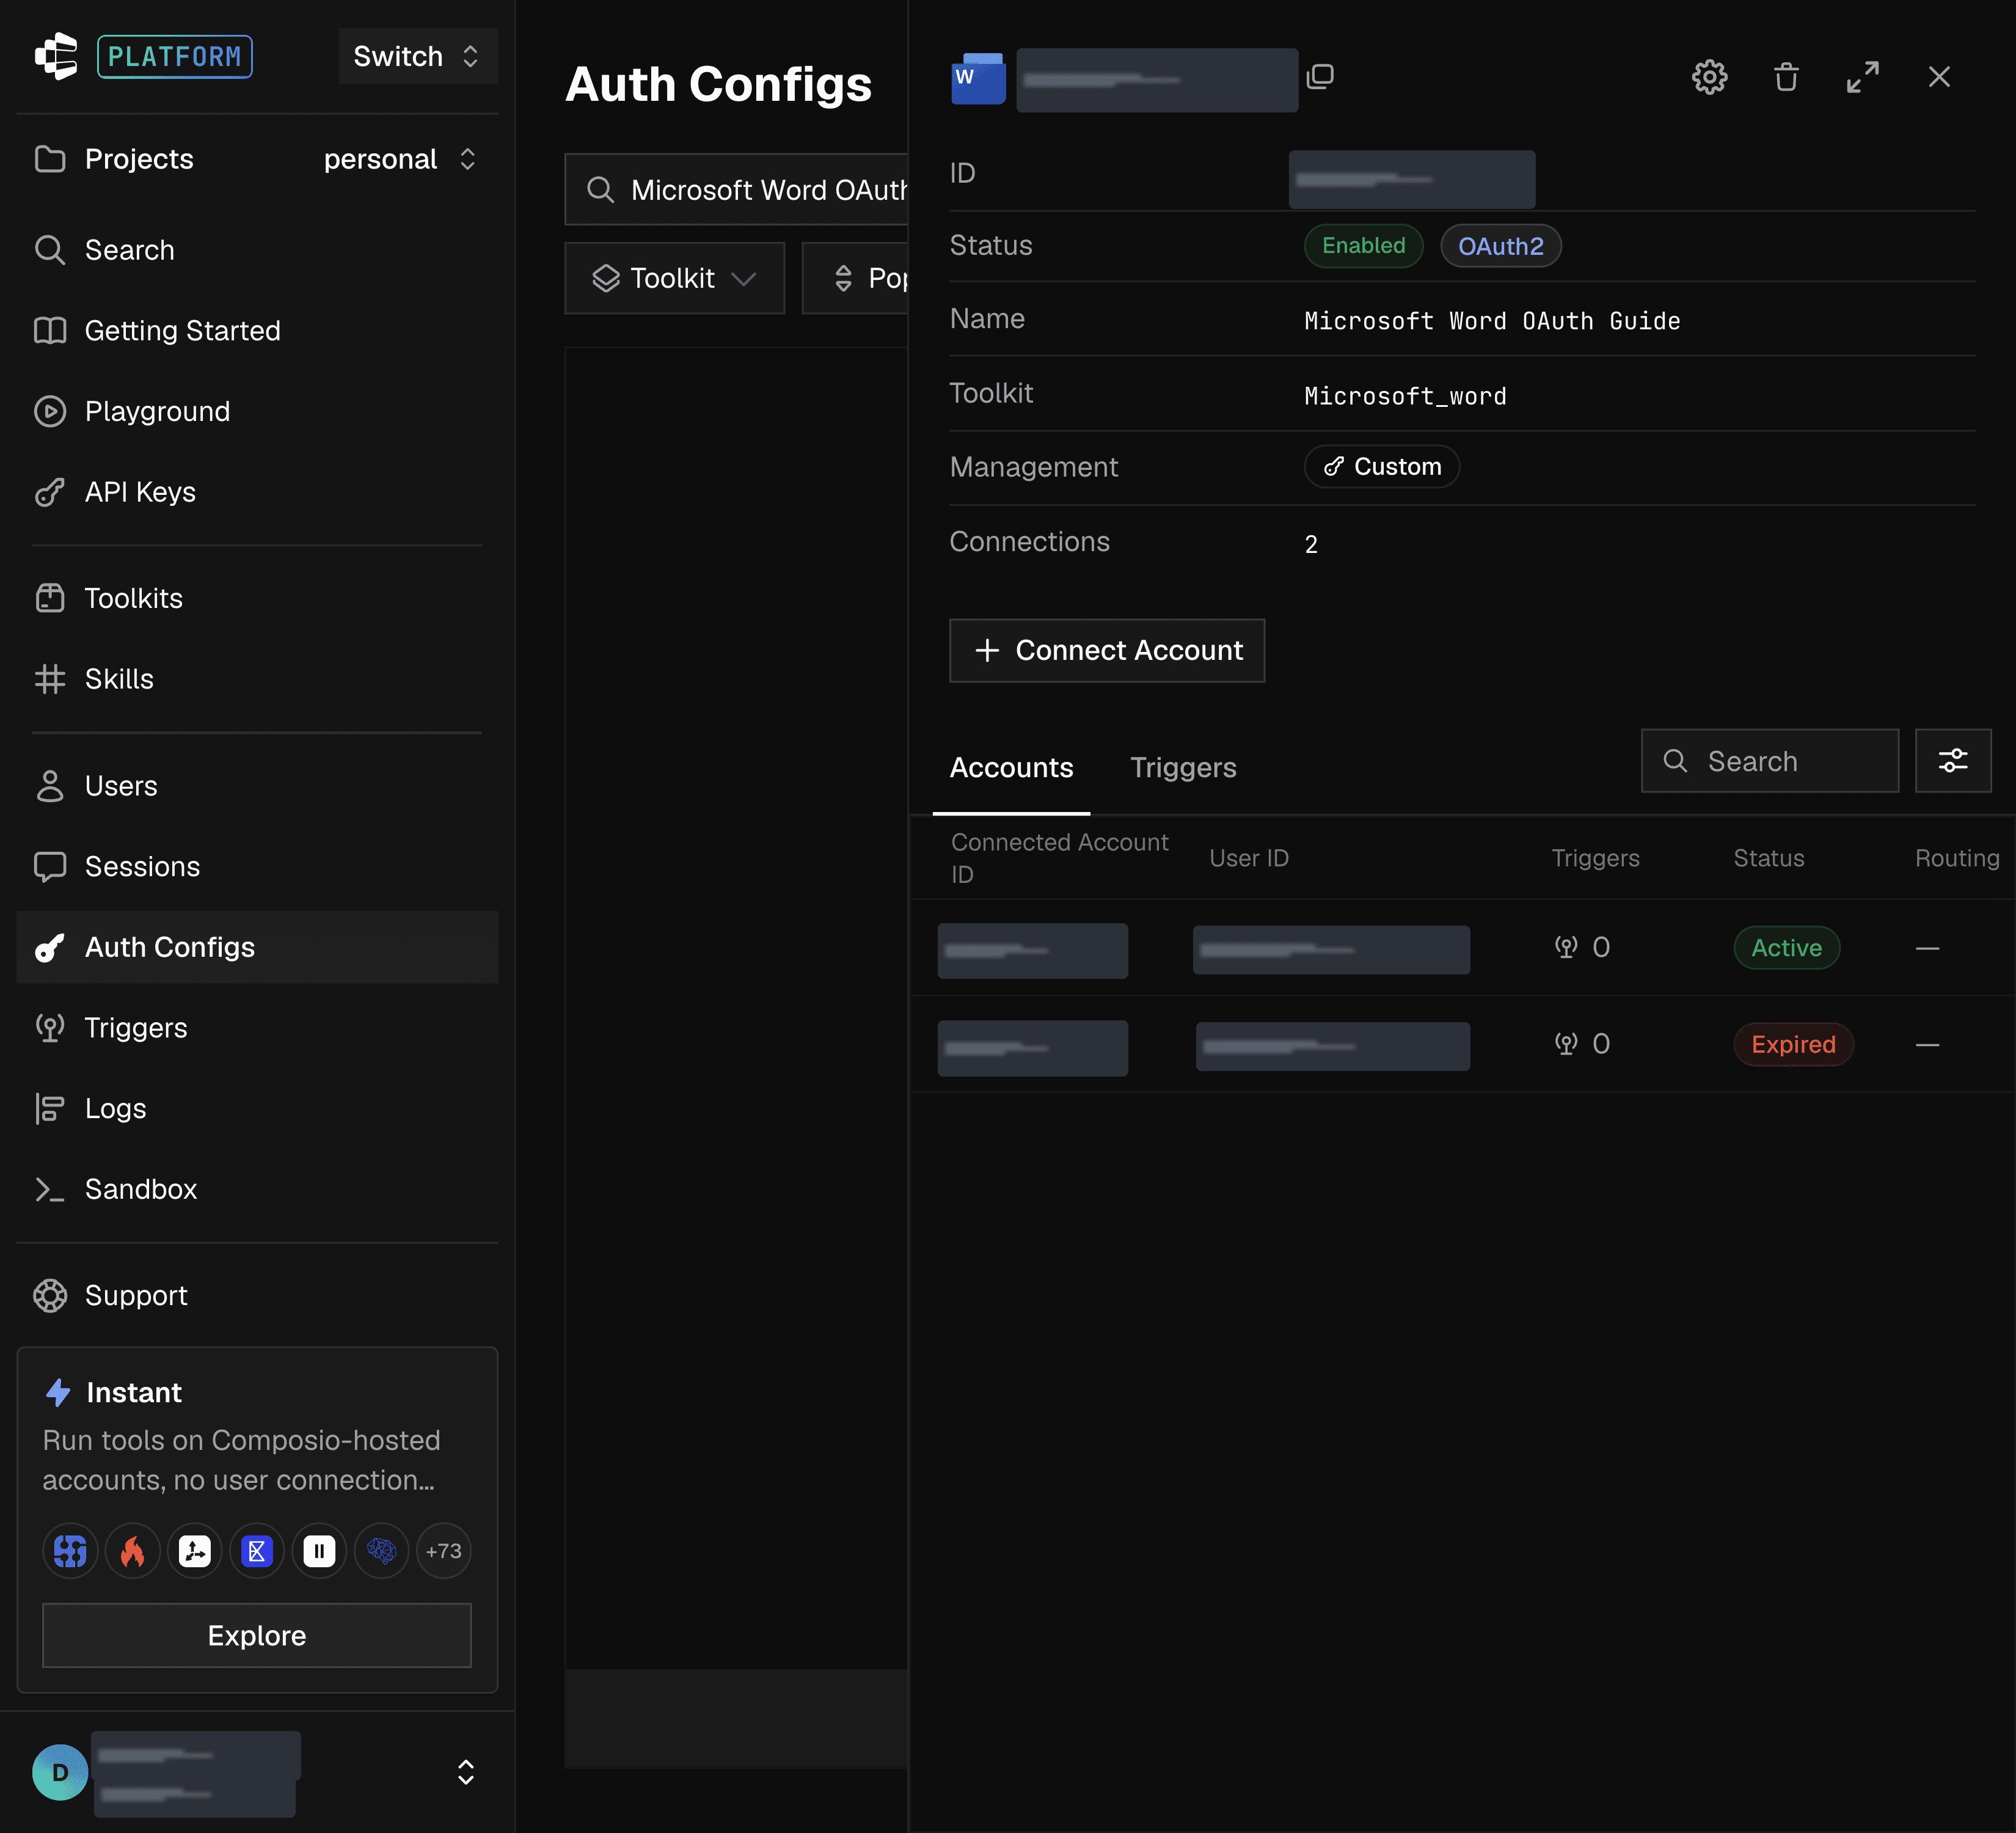
4. Your connected account now appears under Accounts with an Active status.
Base URL for the Word API
All Word API calls are made via Microsoft Graph:
https://graph.microsoft.com/v1.0/That’s it! Your Microsoft Word + Composio OAuth integration is ready.
You can now copy the Auth Config ID (ac_...) and use it inside your code or secret manager.
Revoking Access
You can disconnect Word at any time:
In Composio: open the auth config under Auth Configs and delete the connected account, or disable the auth config.
In Microsoft: go to myapps.microsoft.com (work or school accounts) or account.microsoft.com/privacy (personal accounts) and remove the app, which immediately revokes its access.
Disclaimer: Composio uses AI and may make mistakes, so please review important outputs and confirm sensitive actions.