



Composio connects AI agents to SharePoint so they can work with sites, lists, and documents. Access is limited by the permissions you approve and your account’s existing access.
This guide shows you how to set up OAuth credentials and connect SharePoint to Composio.
Part 1: Connect SharePoint with Composio Managed OAuth
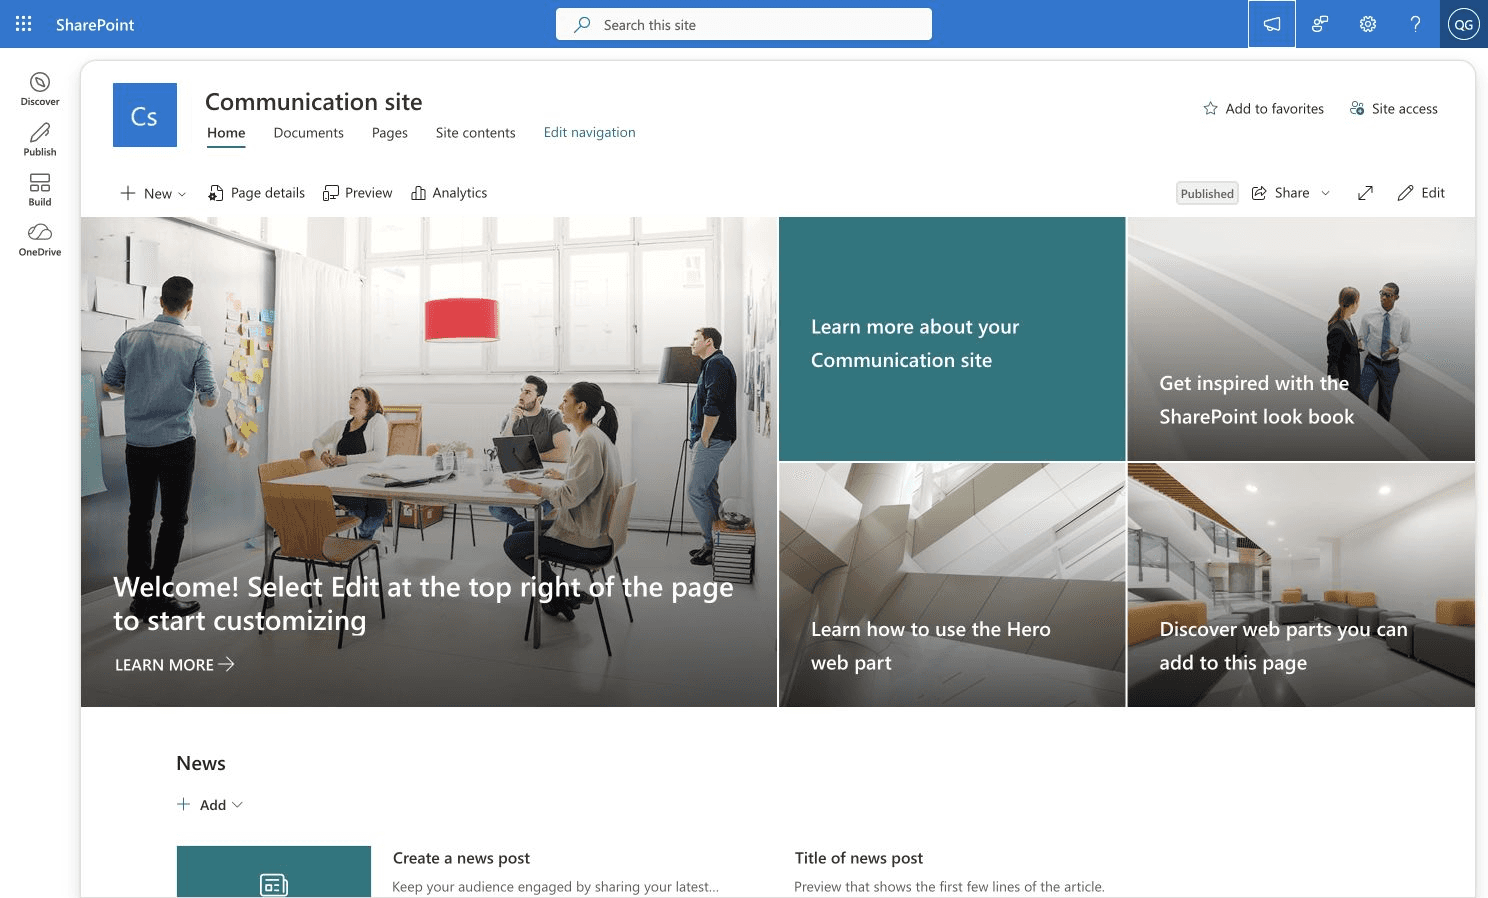
Step 1: Find Your SharePoint Tenant
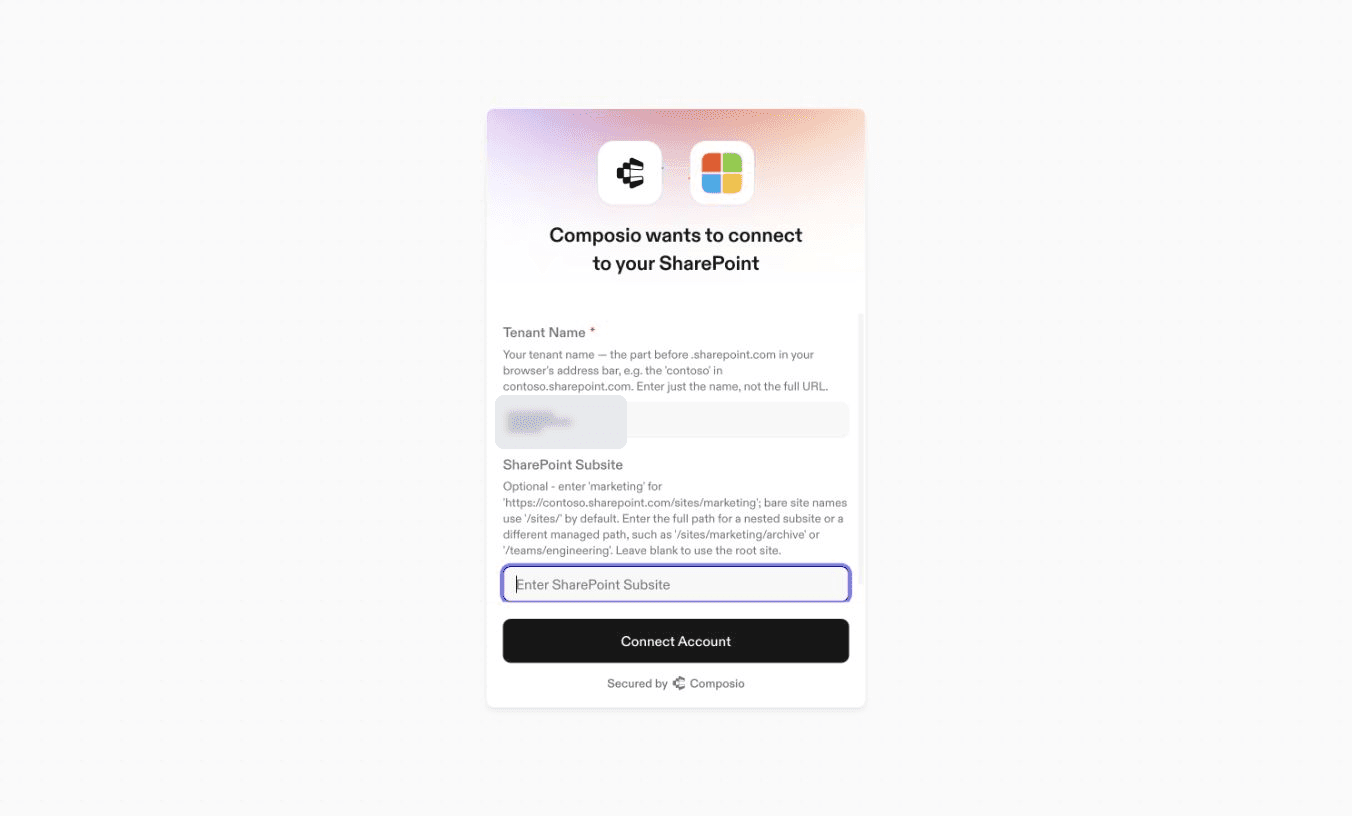
Open your SharePoint site. The part before .sharepoint.com is the Tenant Name, for example contoso.
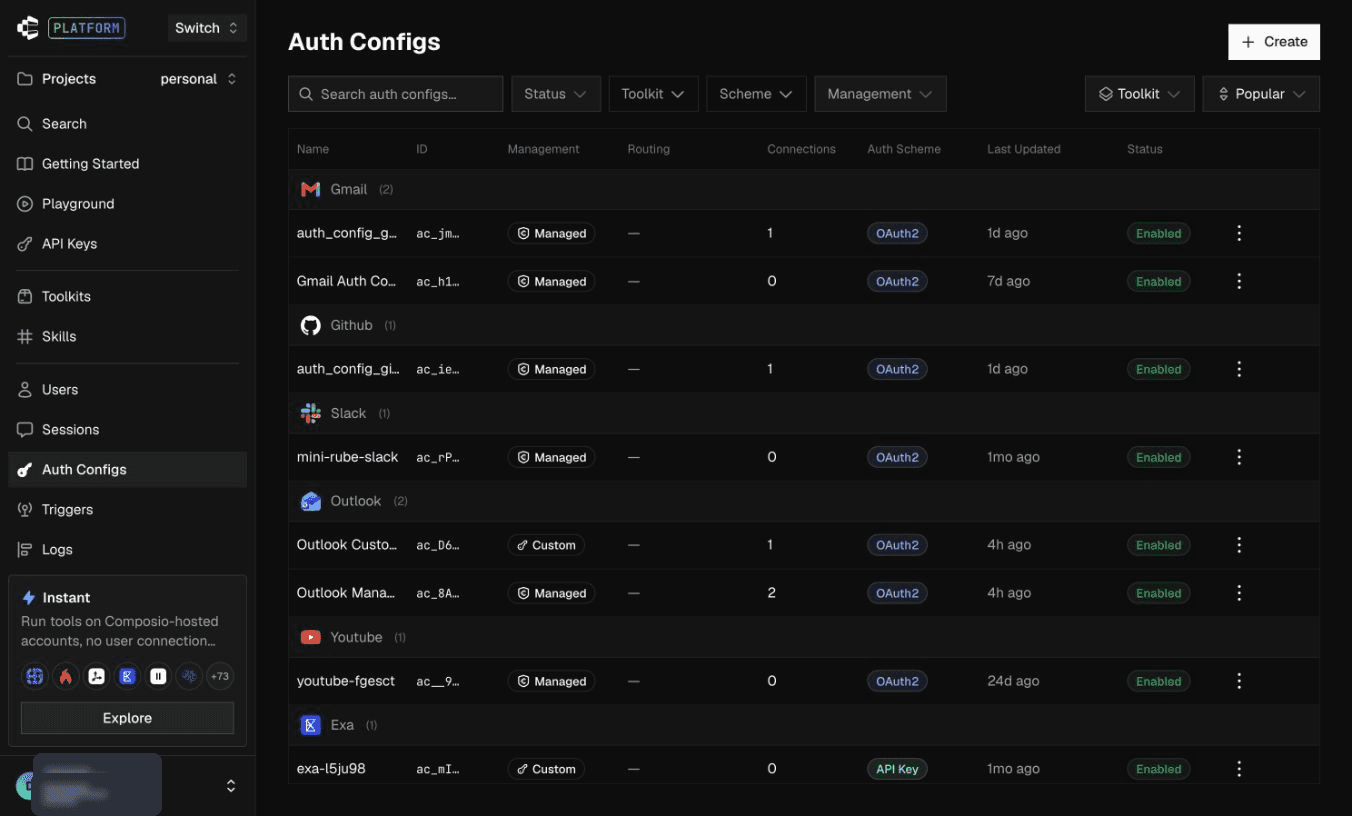
Step 2: Create an Auth Config and Select SharePoint
1. Open the Composio platform, go to Auth Configs and click Create.
2. Search for and select SharePoint. Choose the SharePoint entry shown in this guide, rather than the separate SharePoint Graph entry.

Step 3: Choose Composio Managed OAuth
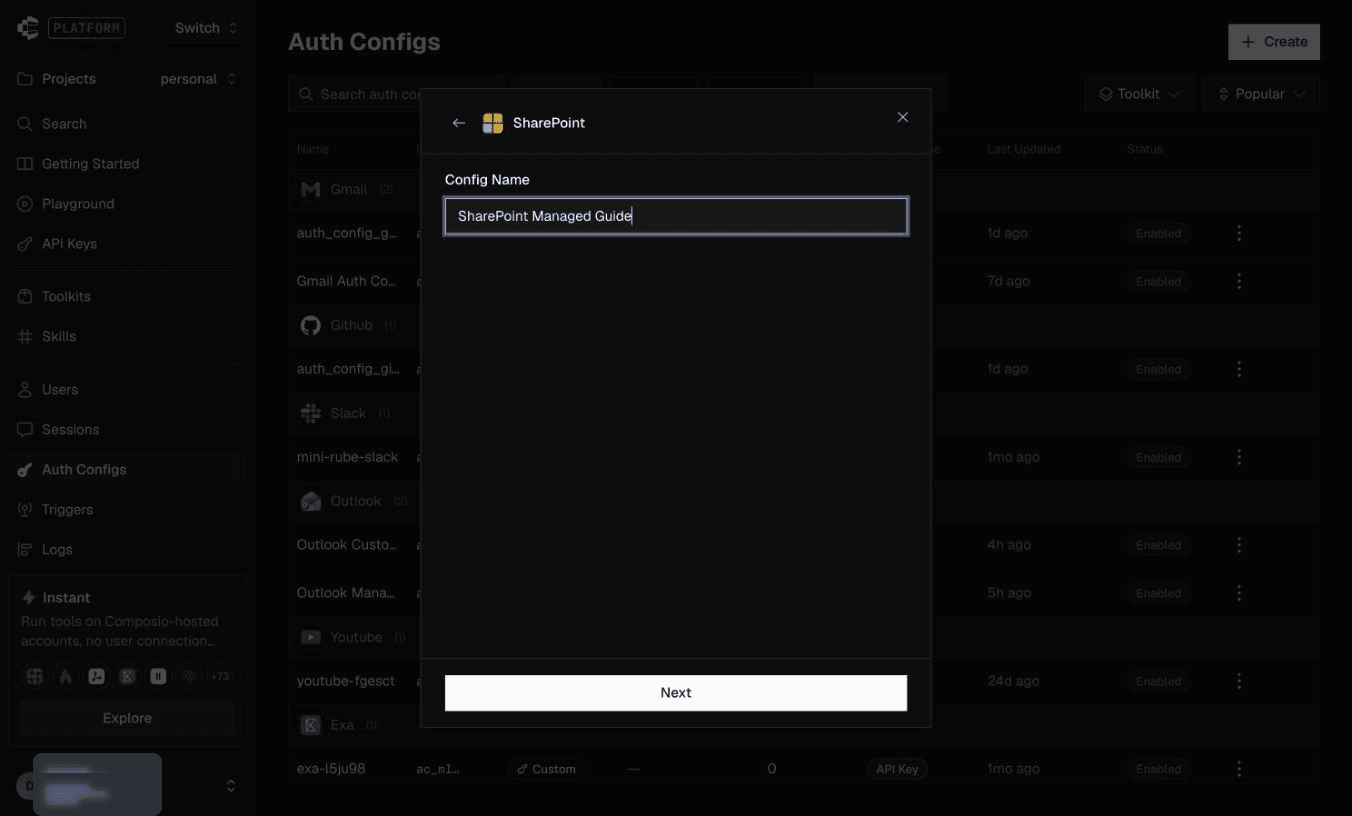
1. Enter a Config Name, such as SharePoint Managed Guide, and click Next.
2. Select OAuth 2.0 and Composio Managed. Under Scopes, choose permissions for the SharePoint operations your integration needs, then click Create Auth Config.
Permission reference. The read-only example uses SharePoint delegated AllSites.Read. Its resource-specific .default request uses the permissions configured on the app; offline_access supports continued access. Additional operations can require other permissions. Choose for your own workflow; the screenshots are examples. Microsoft permission reference.
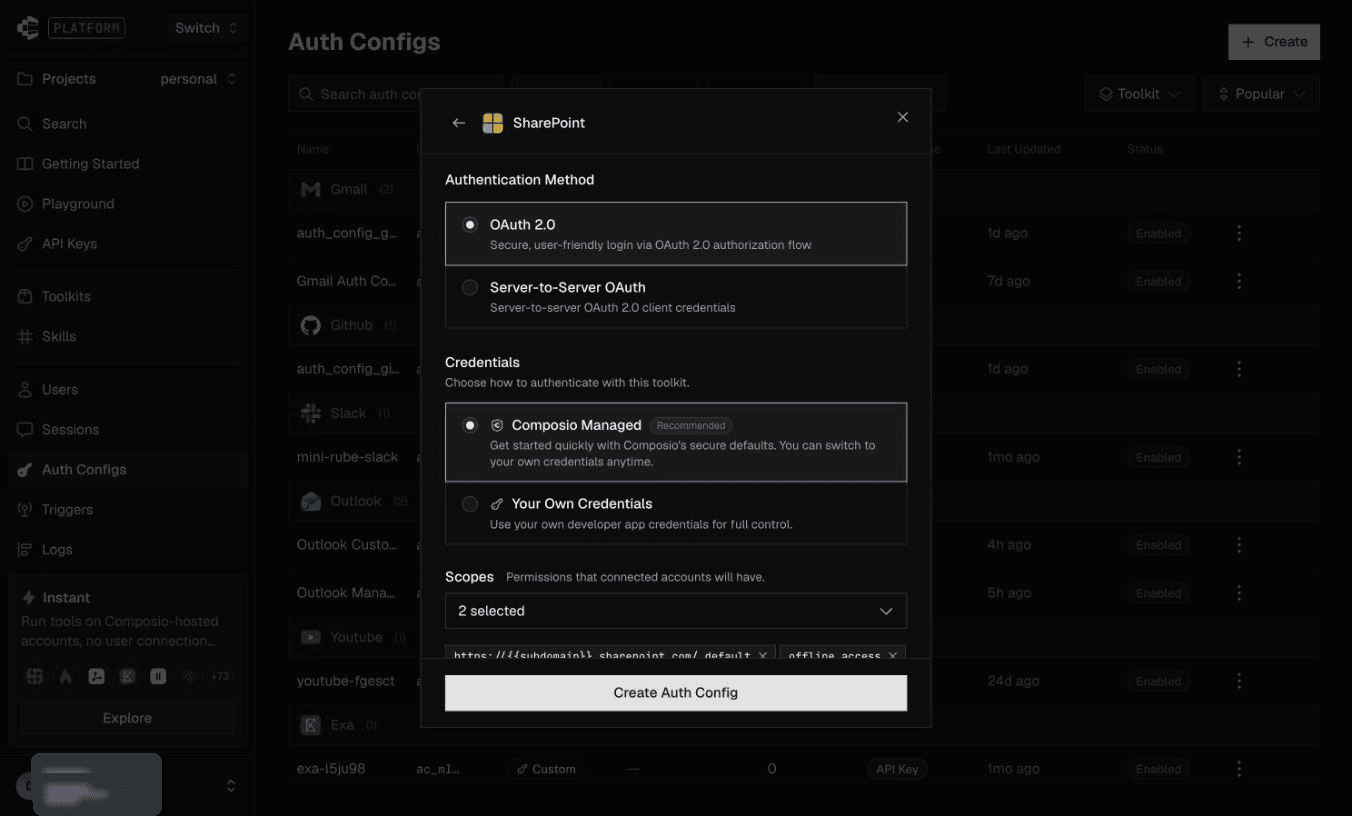
offline_access supports continued access after the initial sign-in. The .default scope uses permissions configured on the OAuth app; it does not itself mean every SharePoint operation is allowed. Microsoft’s scope documentation explains this behavior.
Step 4: Enter Your Tenant and Site
1. Open the auth config and click Connect Account.
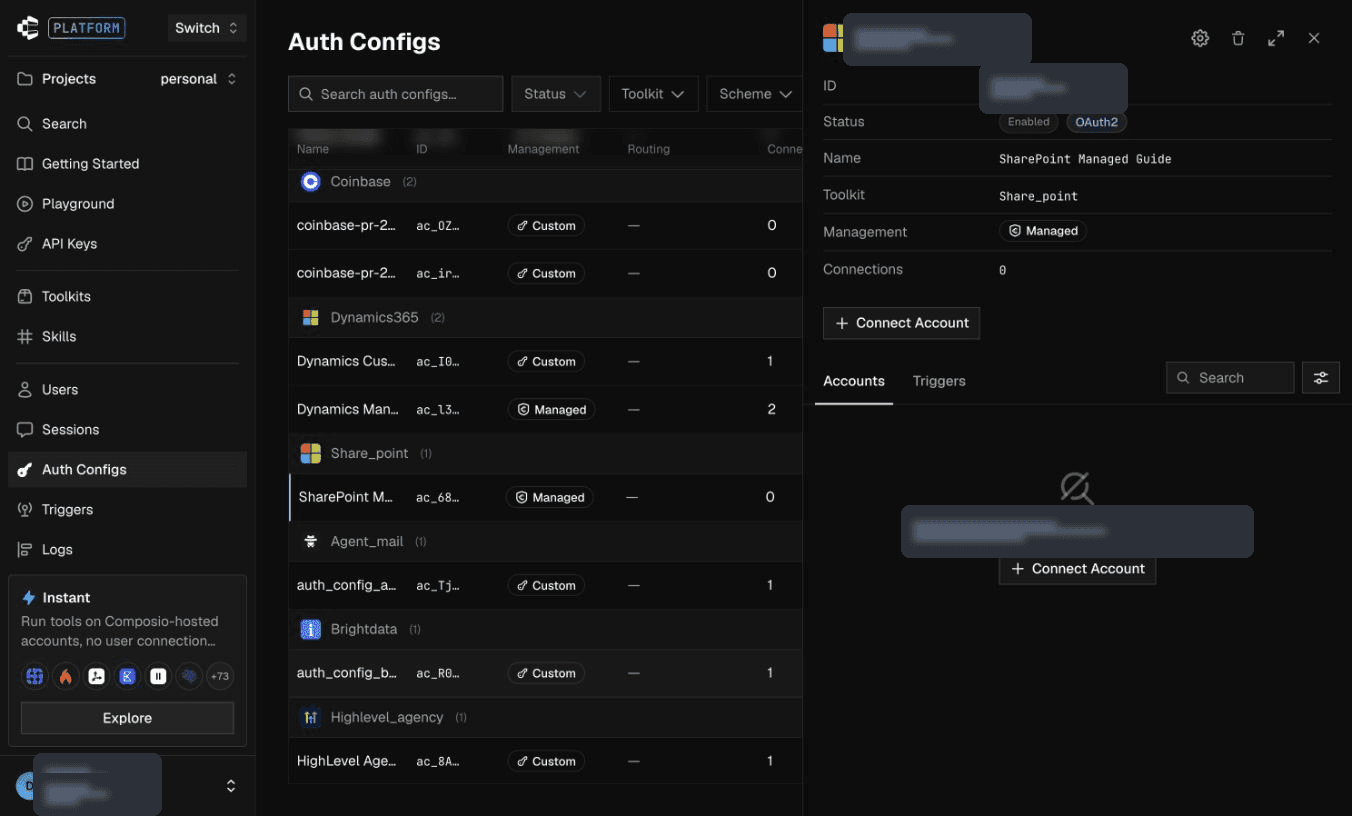
2. Enter the Tenant Name from your SharePoint URL. Set SharePoint Subsite if you want a particular site or nested path, or leave it empty for the root site. Click Connect Account. Do not put a tenant GUID or a full URL in Tenant Name.
Step 5: Sign in to Microsoft
1. Select the work or school Microsoft account that can access the target site and sign in.

2. If Microsoft asks for permissions, review the app and requested access before accepting. Your organization may require administrator approval. Existing authorization can skip that prompt. After authorization completes, Composio shows the successful connection page.

Step 6: Confirm the Connected Account Is Active
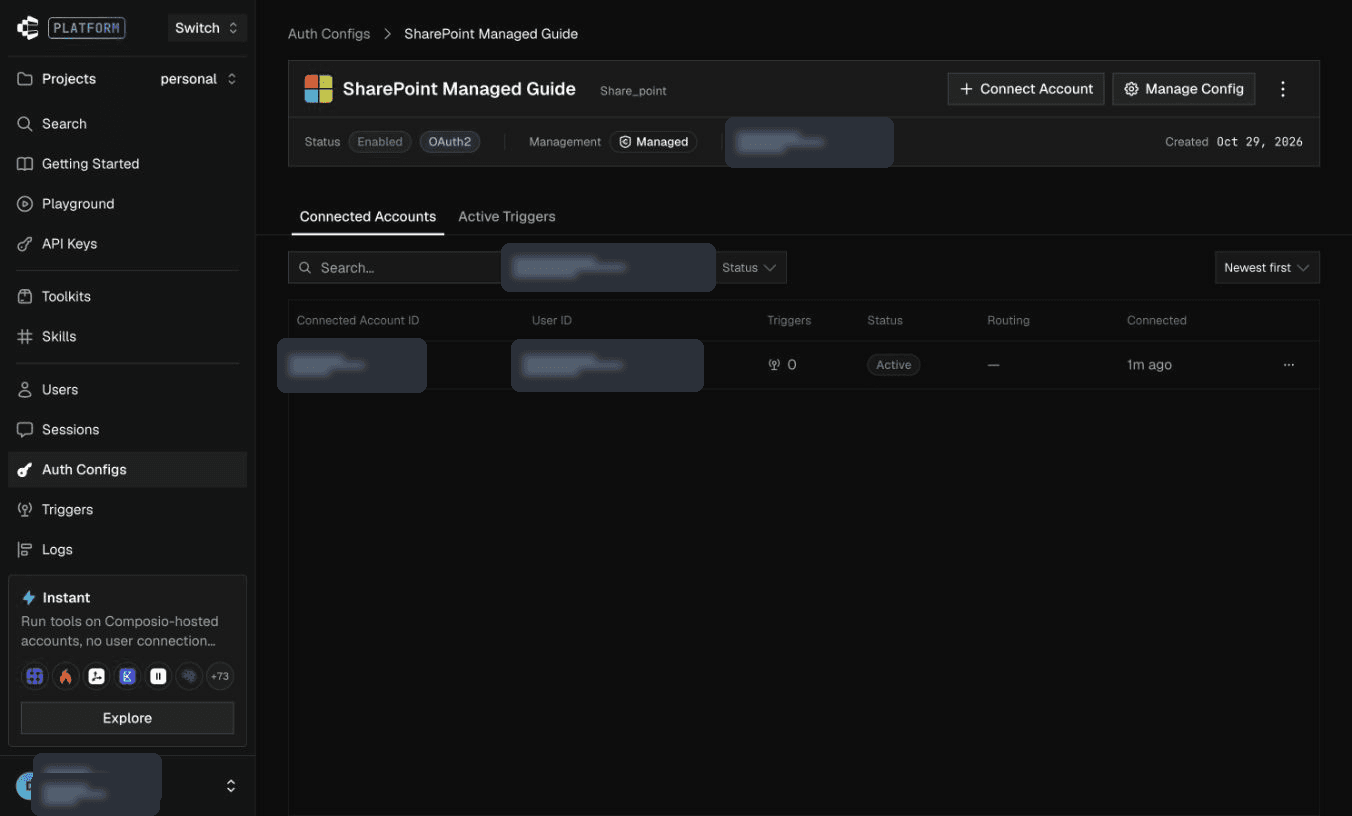
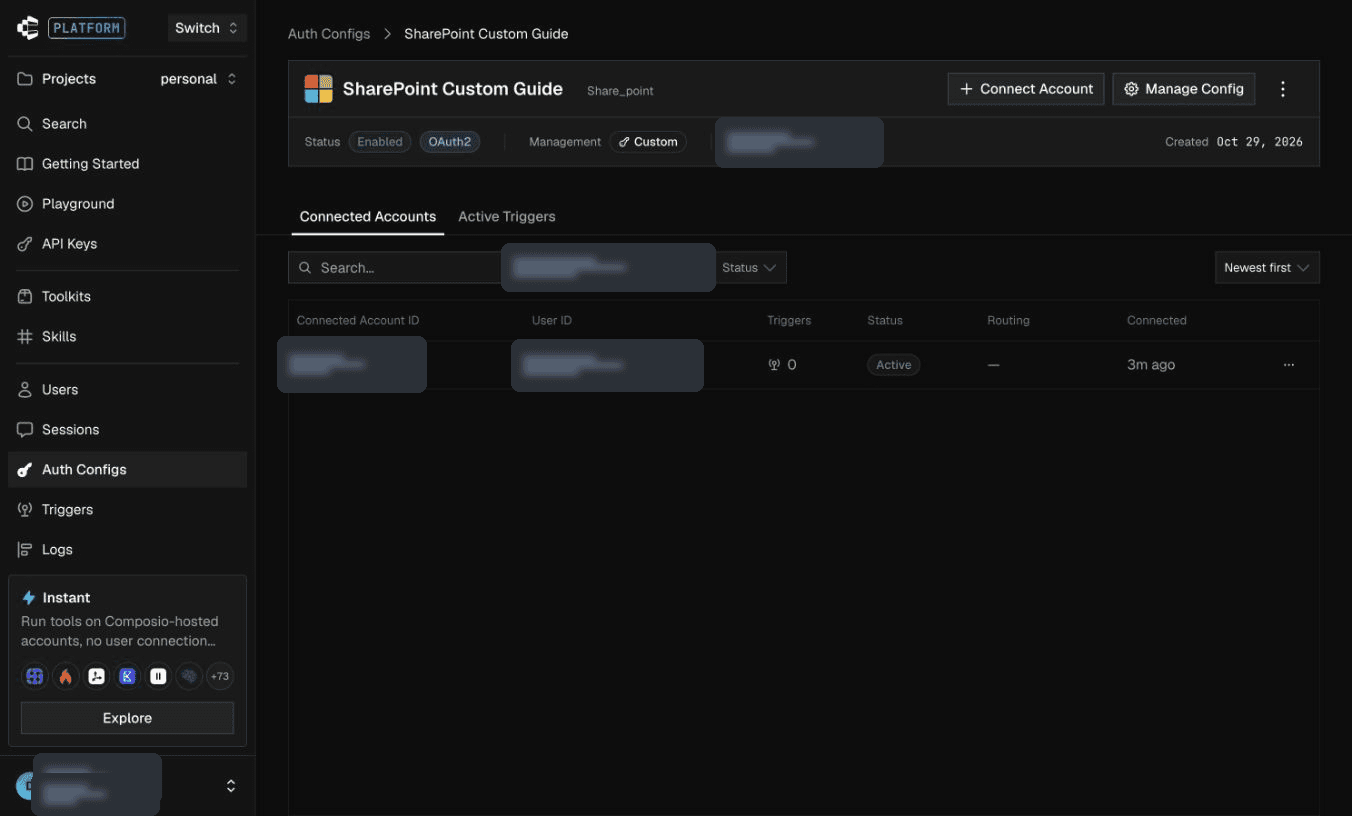
1. Return to the auth config’s Connected Accounts tab and check Active on the account row. The auth config’s Enabled status is separate from the connected-account status.
Part 2: Use your own OAuth credentials
Step 1: Register an App in Microsoft Entra ID
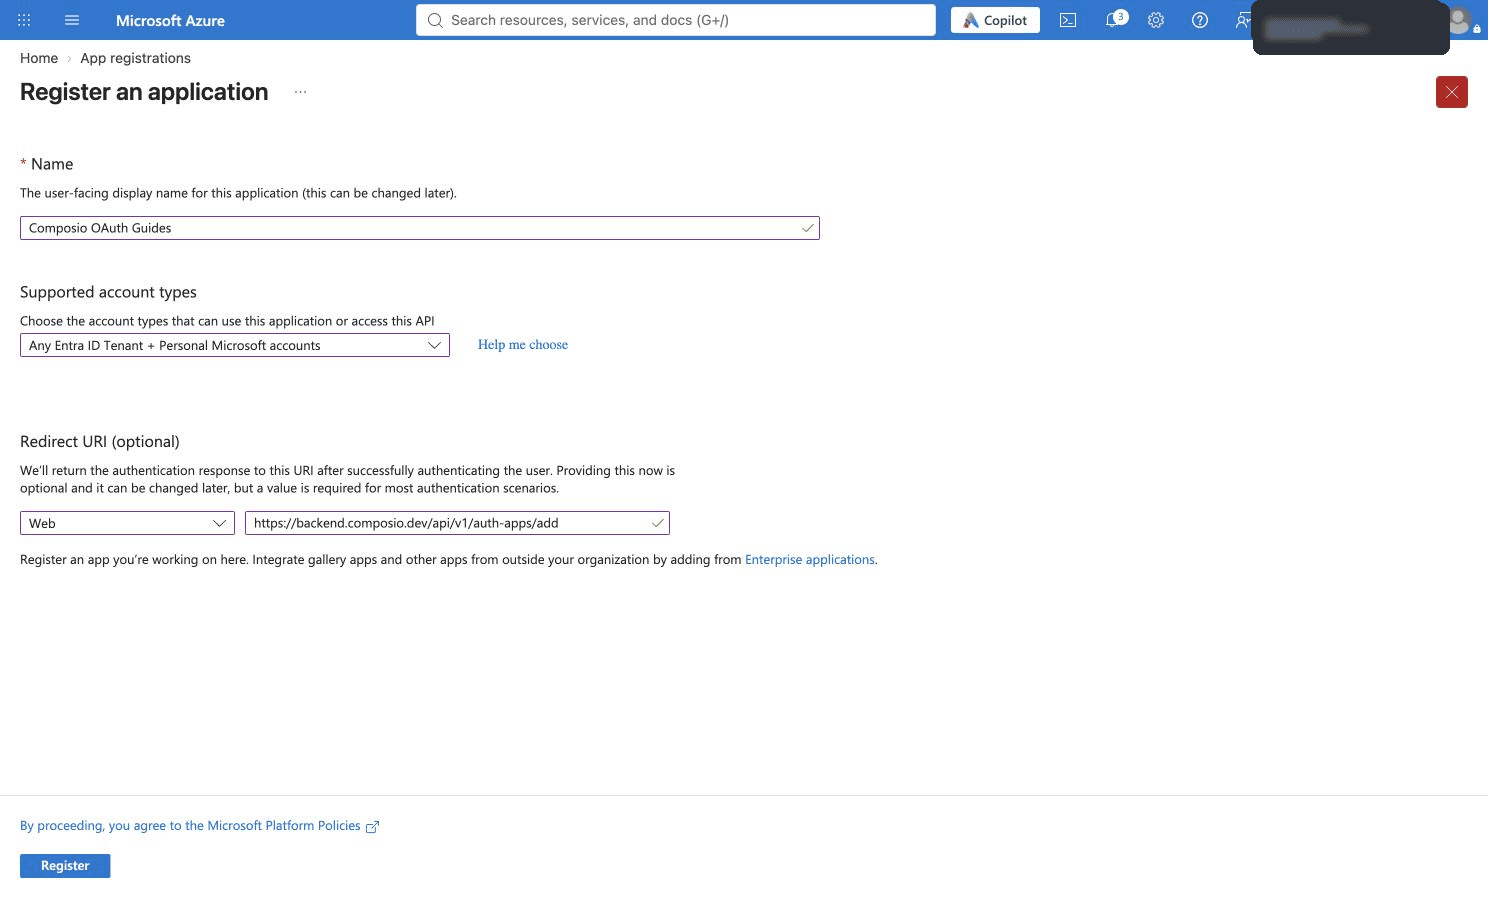
1. In the Azure portal, open App registrations and choose New registration. Enter a descriptive name. With the default common sign-in endpoint, use an account audience that allows organizational directories. The shared screenshot also allows personal accounts for other Microsoft guides; this does not give personal accounts access to an organizational SharePoint site.
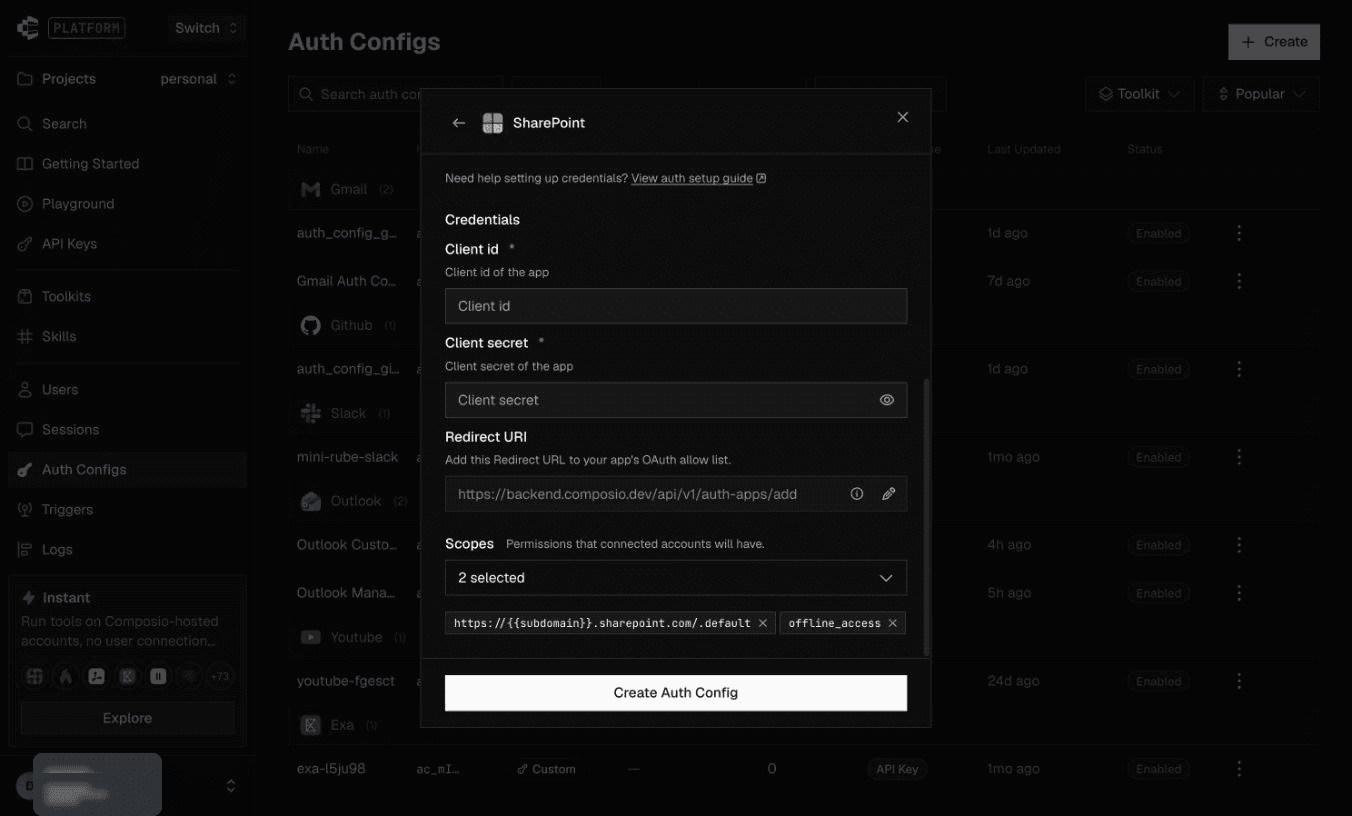
2. Select Web under Redirect URI, enter Composio’s original callback exactly as below, and click Register.
https://backend.composio.dev/api/v1/auth-apps/add
Step 2: Copy the Client ID and Create a Client Secret
1. On the app’s Overview page, copy the Application (client) ID. You will enter it as Client id in Composio.

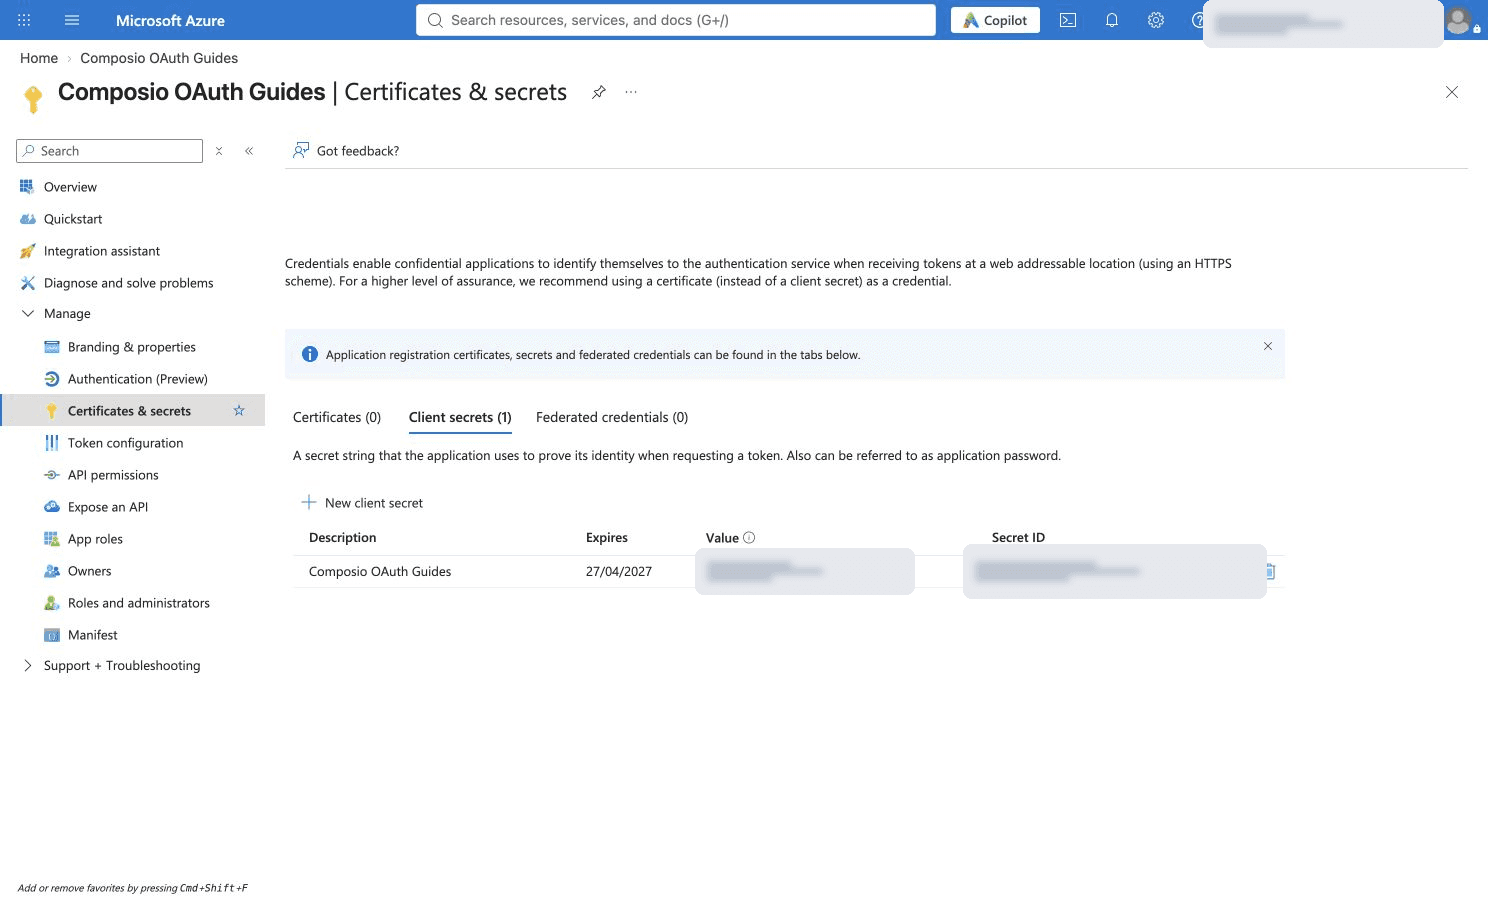
2. Open Certificates & secrets and click New client secret.
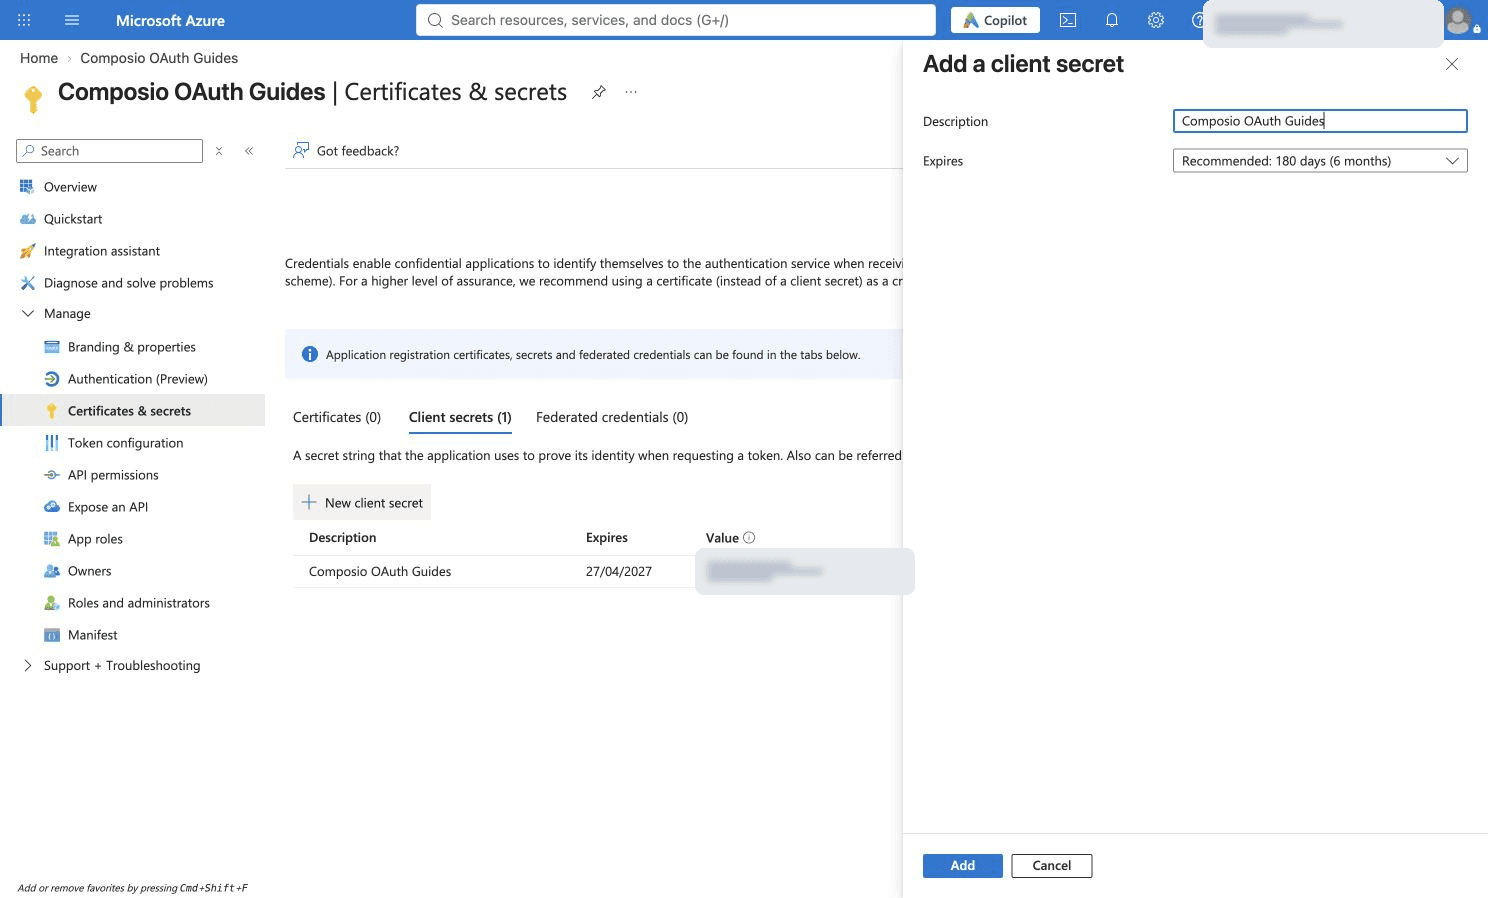
3. Add a description, choose an expiry that matches your rotation policy and click Add. The example uses 180 days. Rotate the secret before it expires.
4. Copy the secret Value immediately and store it privately. Use the Value, not the Secret ID. Azure does not show the full Value on later visits. The screenshot censors the entire Value field. Keep public client flows disabled for this confidential Web client.

Step 3: Configure SharePoint Delegated Permissions
1. Open API permissions and click Add a permission.
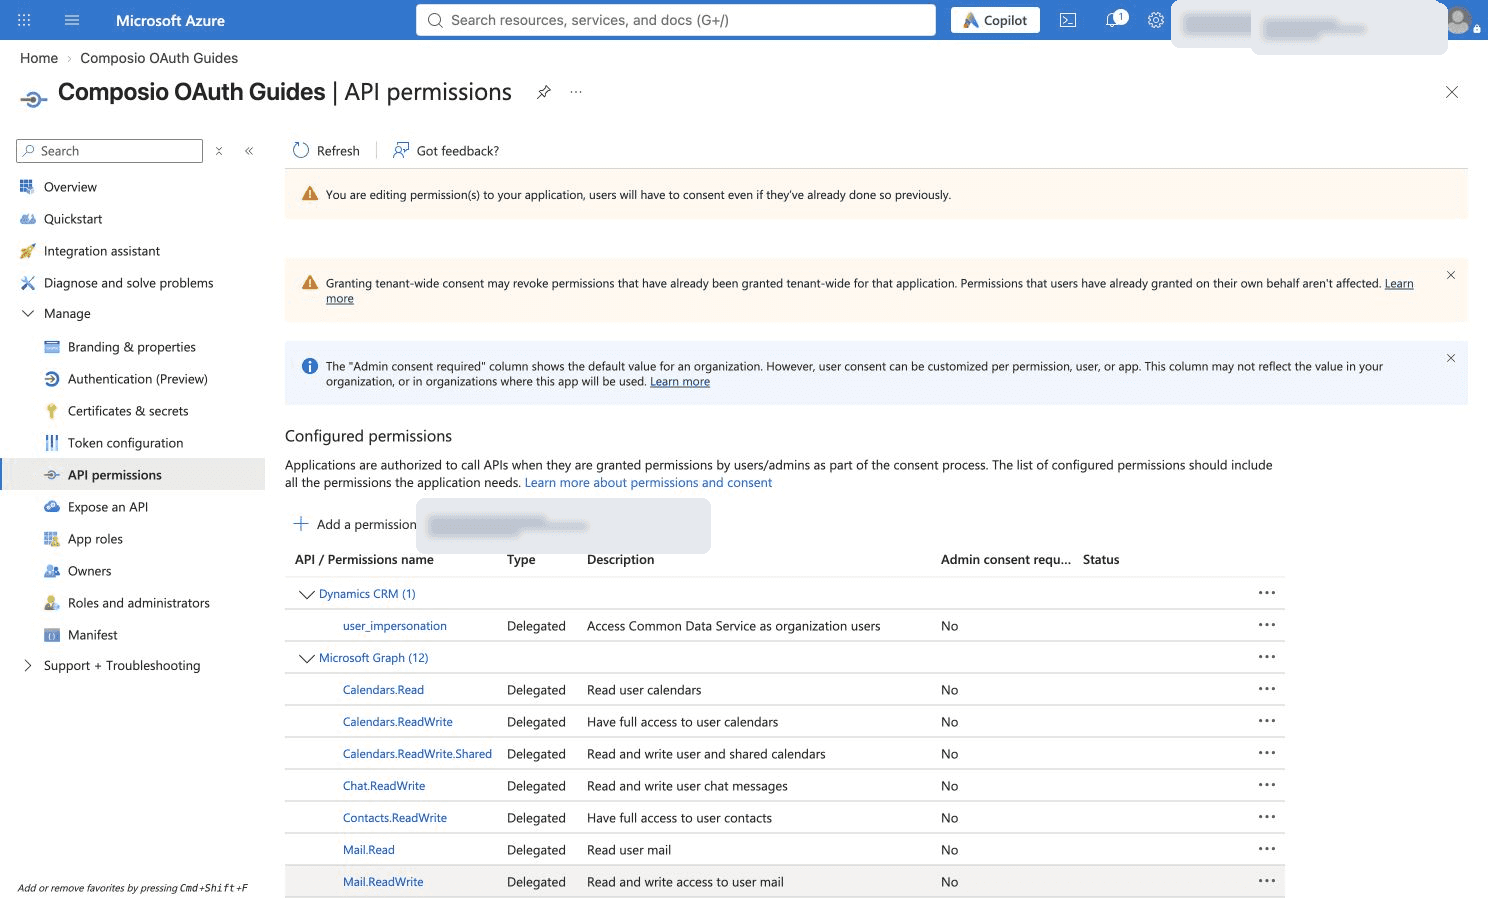
2. Select the SharePoint API resource. The permission in the next step belongs to SharePoint, not Microsoft Graph.
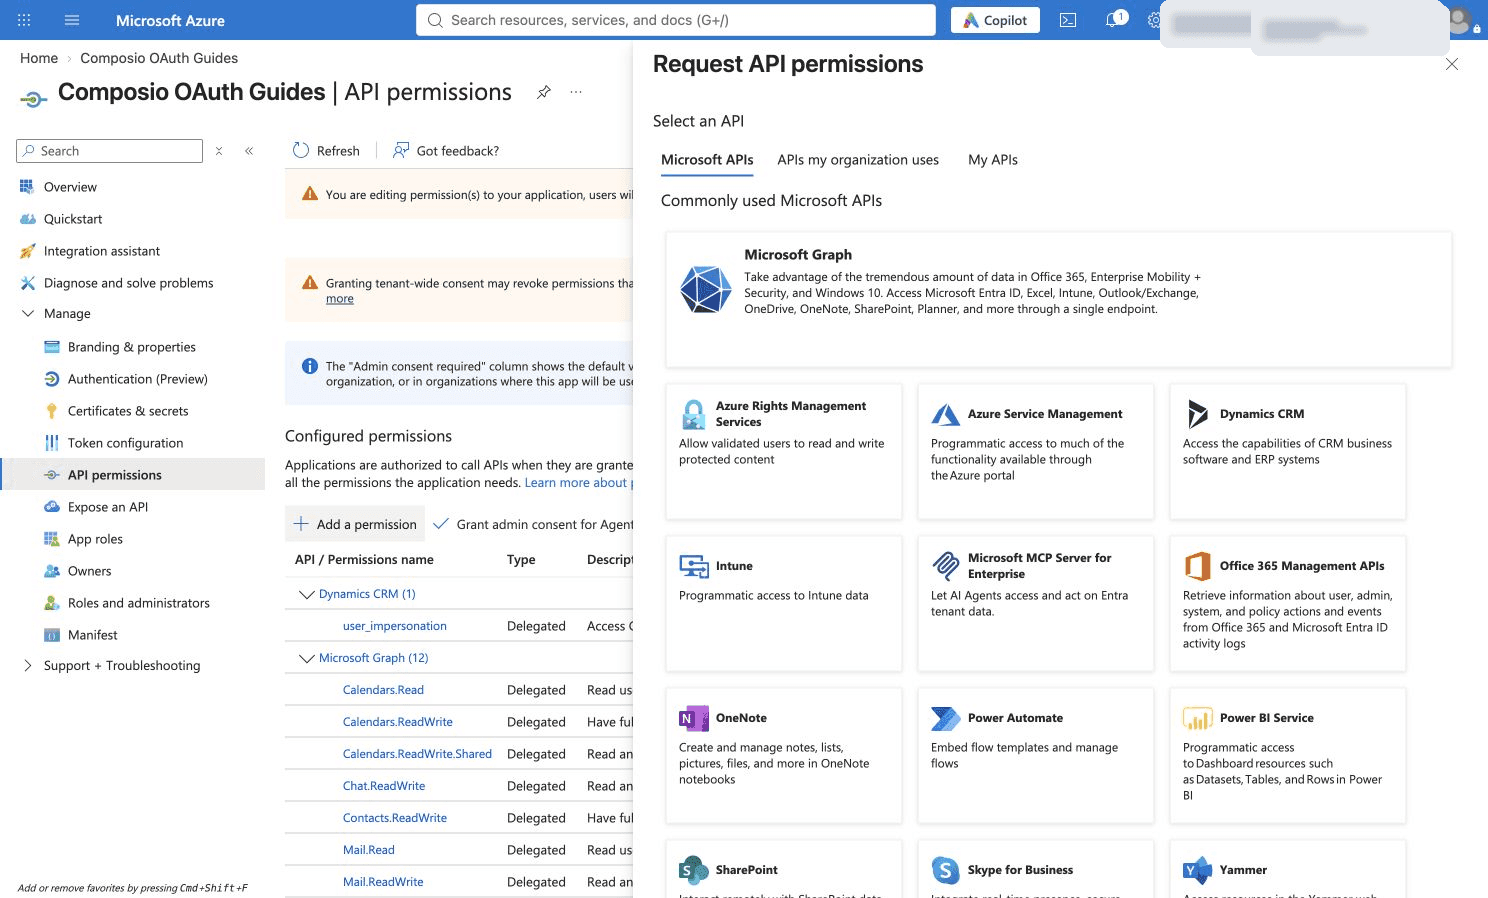
3. Choose Delegated permissions. Choose the delegated permissions needed for the operations your integration will use. Then click Add permissions.
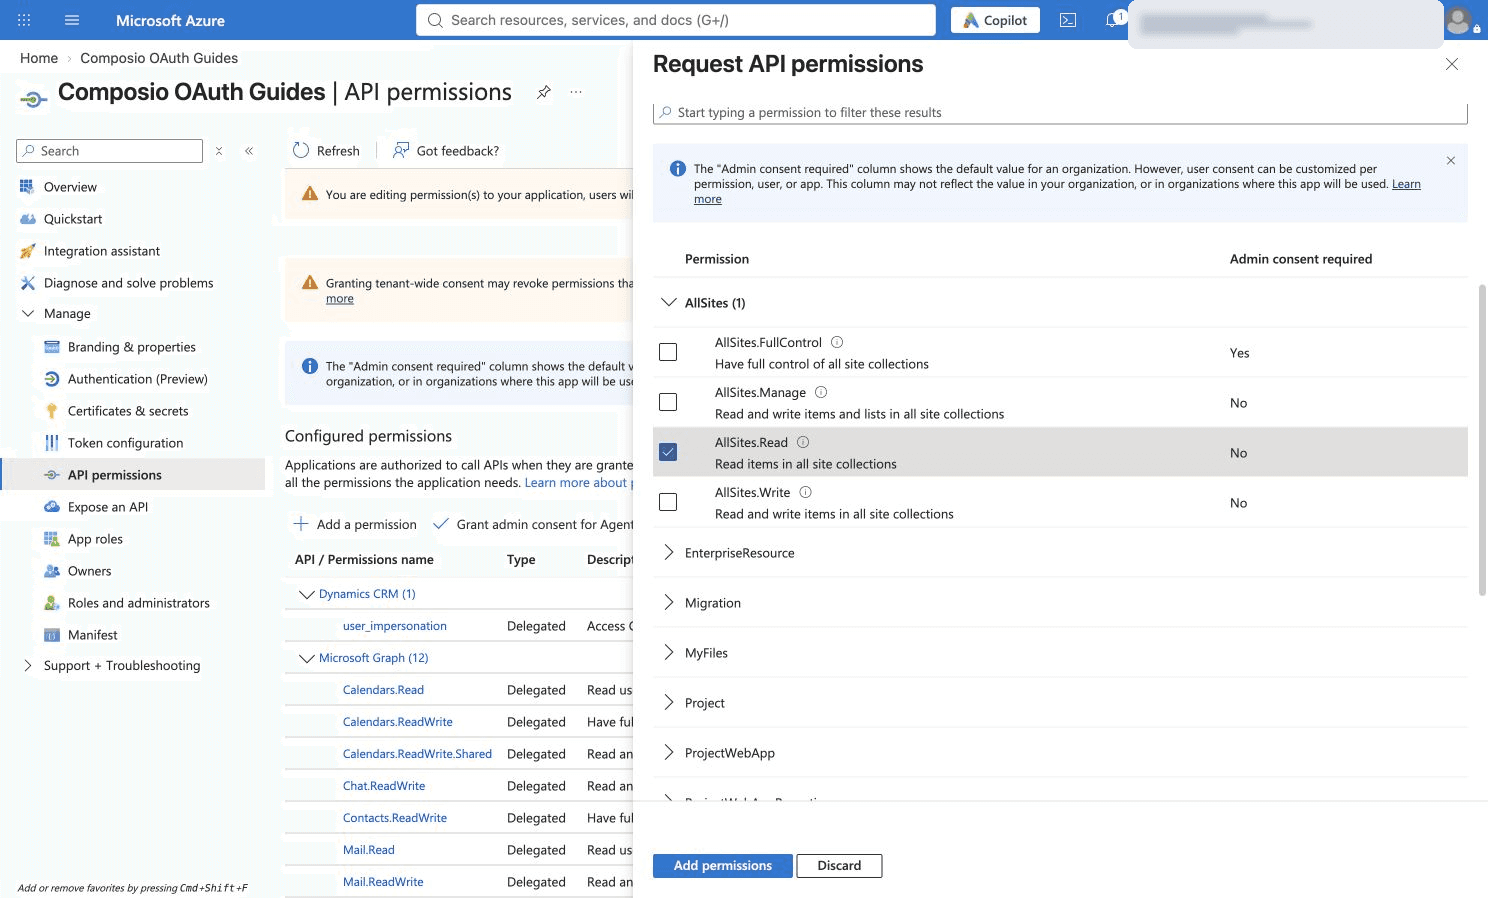
4. Review the configured permission. Choose additional SharePoint delegated permissions only when the intended tools need them. Write, list-management and administrative operations can require other permissions and site or tenant roles. Declaring a permission in the app registration is separate from granting consent.
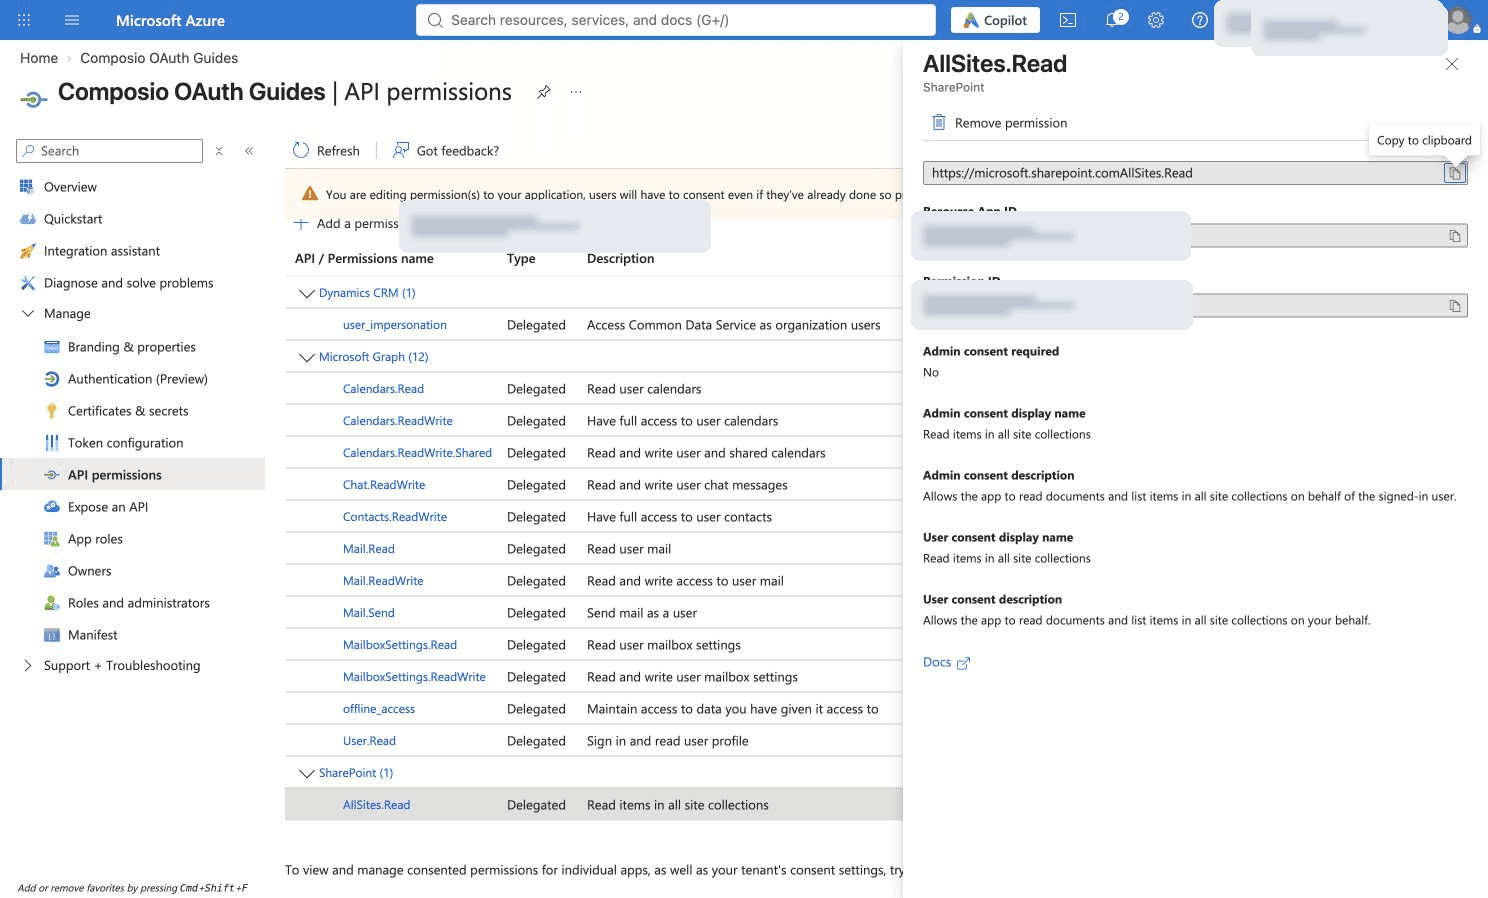
If new consent is required, .default can present other API permissions configured on a reused app as well. Review everything Microsoft requests. Do not delete permissions that other integrations rely on, or grant every API permission by default. An administrator may need to approve according to tenant policy. The SharePoint authorization documentation describes separate requirements for administrative operations.
Step 4: Create the Auth Config with Your Own Credentials
1. In Composio, create an auth config for SharePoint. Enter a name, such as SharePoint Custom Guide, and click Next.
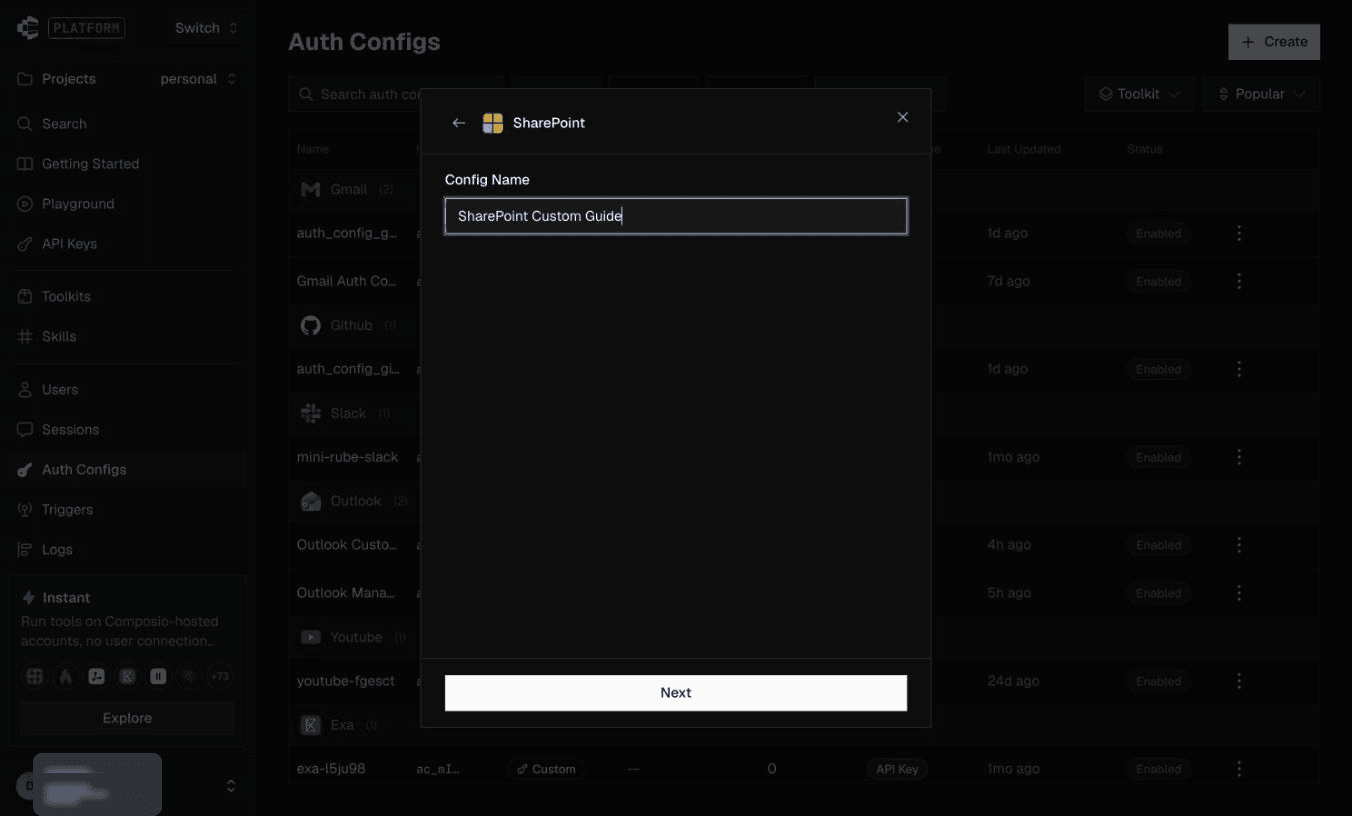
2. Select OAuth 2.0 and Your Own Credentials. Enter your app’s Client id and client-secret Value. The screenshot leaves those fields empty for privacy.
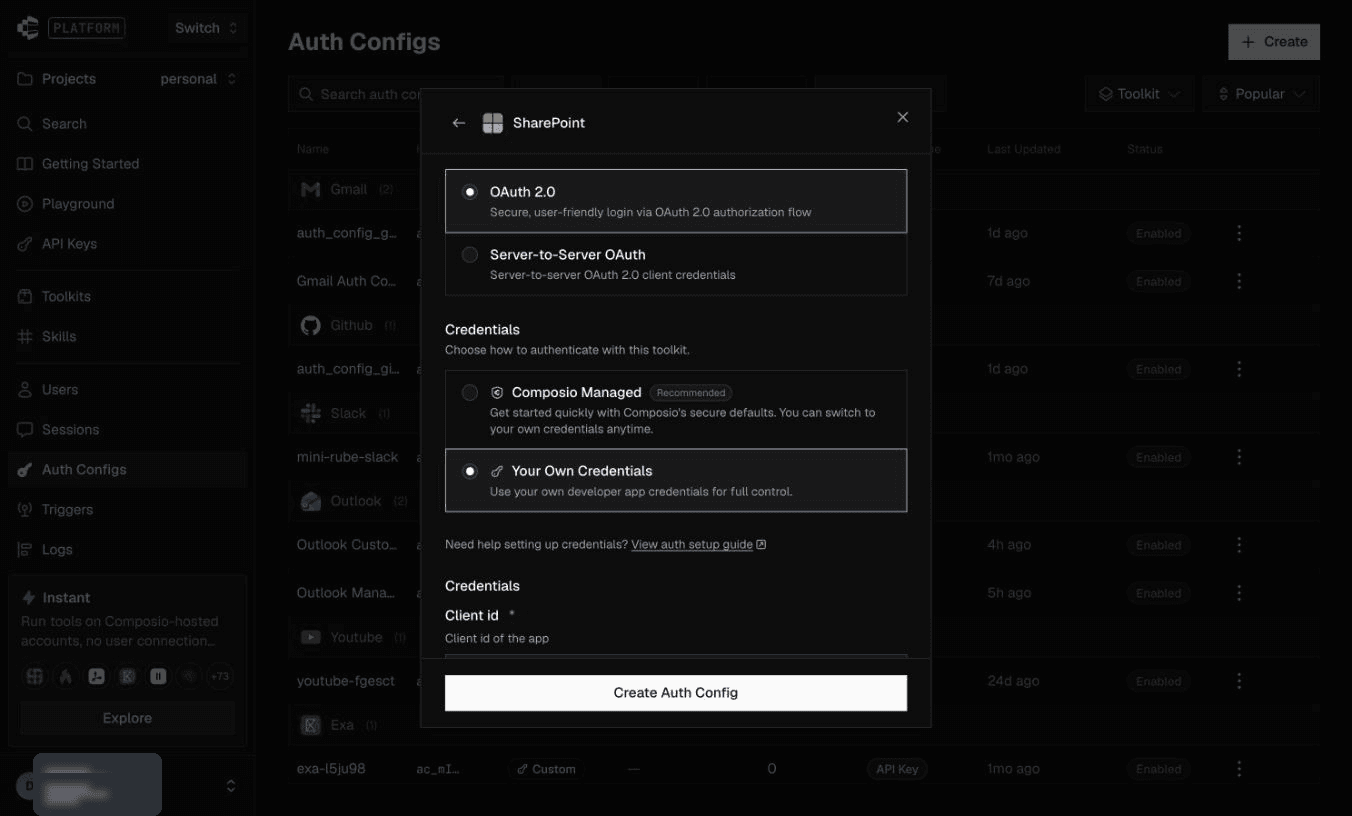
3. Keep the Redirect URI identical to the registered Web callback. Under Scopes, choose permissions required by your integration and supported by your app registration. Click Create Auth Config.
Step 5: Connect Your SharePoint Site
1. Open the custom auth config and click Connect Account.
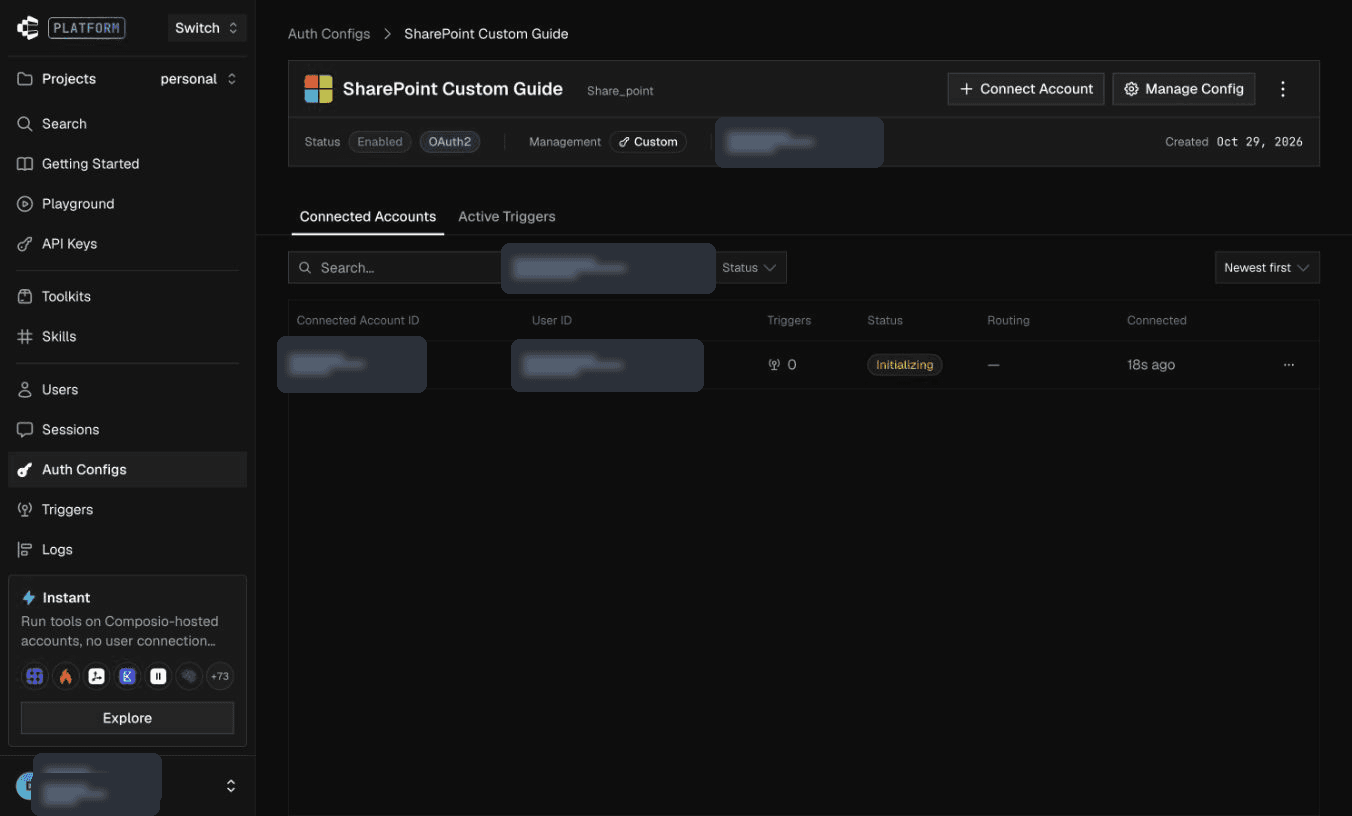
2. Enter the Tenant Name and optional SharePoint Subsite for the site you want to use. Leave the site field empty for the root site, or provide a site name or full nested path. Click Connect Account.

3. Select the work or school account with site access and sign in. If a permissions prompt appears, confirm it is your own app and review the requested access before accepting. Leave organization-wide consent unchecked unless an administrator intends tenant-wide approval. Existing consent may skip the prompt.
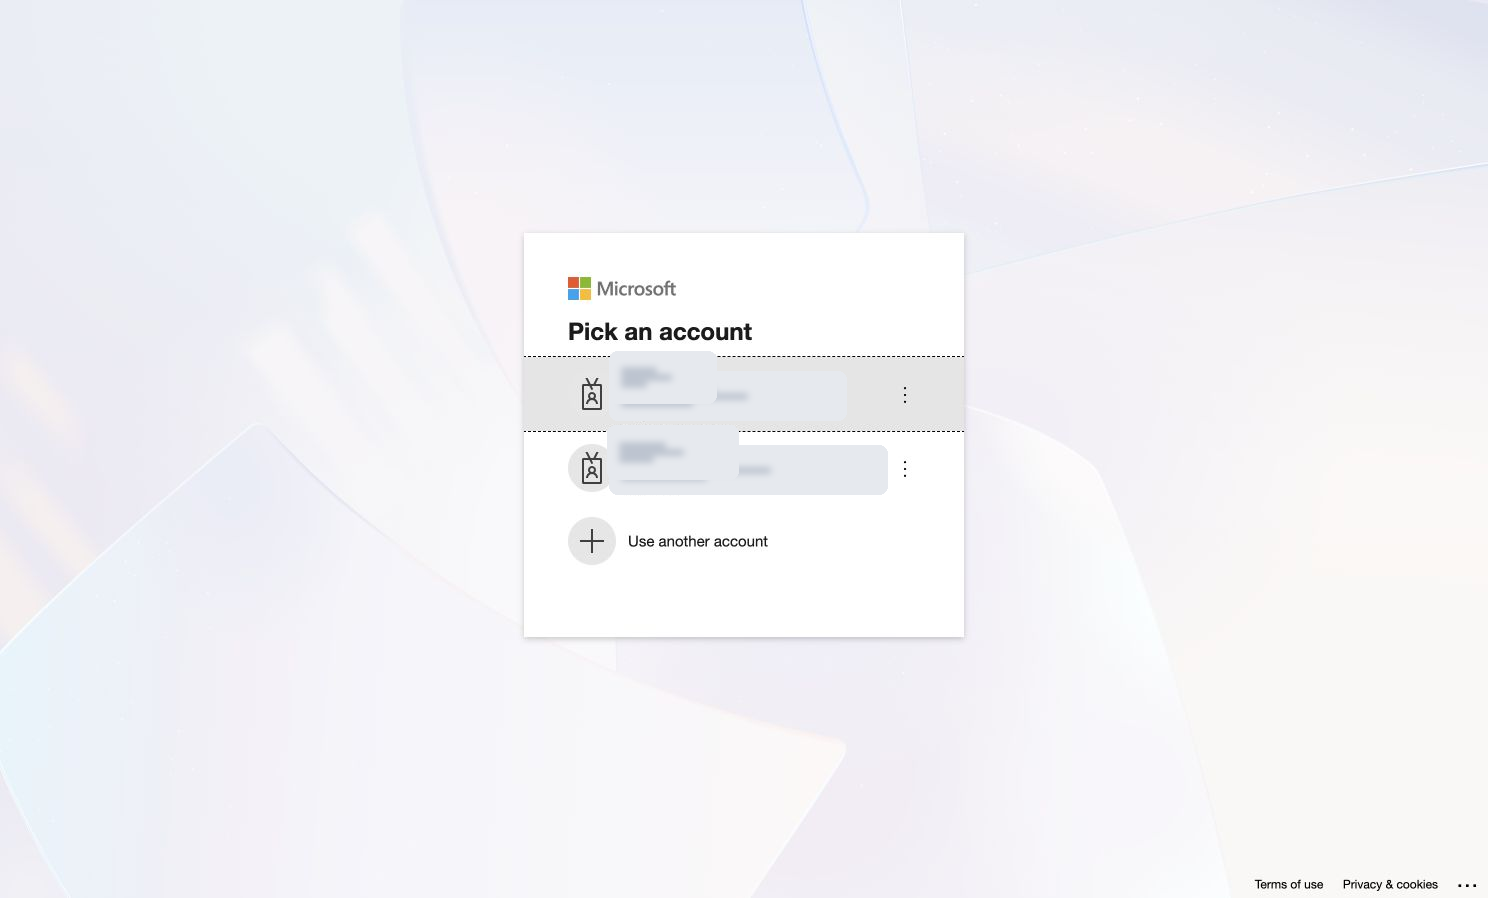
4. Wait for the successful Composio connection page.
Step 6: Confirm the Custom Connected Account Is Active
1. Return to the custom auth config and check that its Connected Accounts tab shows Active on the account row. Keep the app’s permissions and the Microsoft account’s site access aligned with the tools you intend to use.
Copy the Auth Config ID from Composio and use it in your application’s integration setup. The read-only example does not grant every SharePoint toolkit operation.