



Composio connects AI agents to OneDrive so they can find, read, and manage files. Access is limited by the permissions you approve and your account’s existing access.
This guide shows you how to set up OAuth credentials and connect OneDrive to Composio.
Part 1: Connect OneDrive with Composio Managed OAuth
Step 1: Create an Auth Config and Select OneDrive
1. Go to Auth Configs in the Composio Dashboard and click Create.
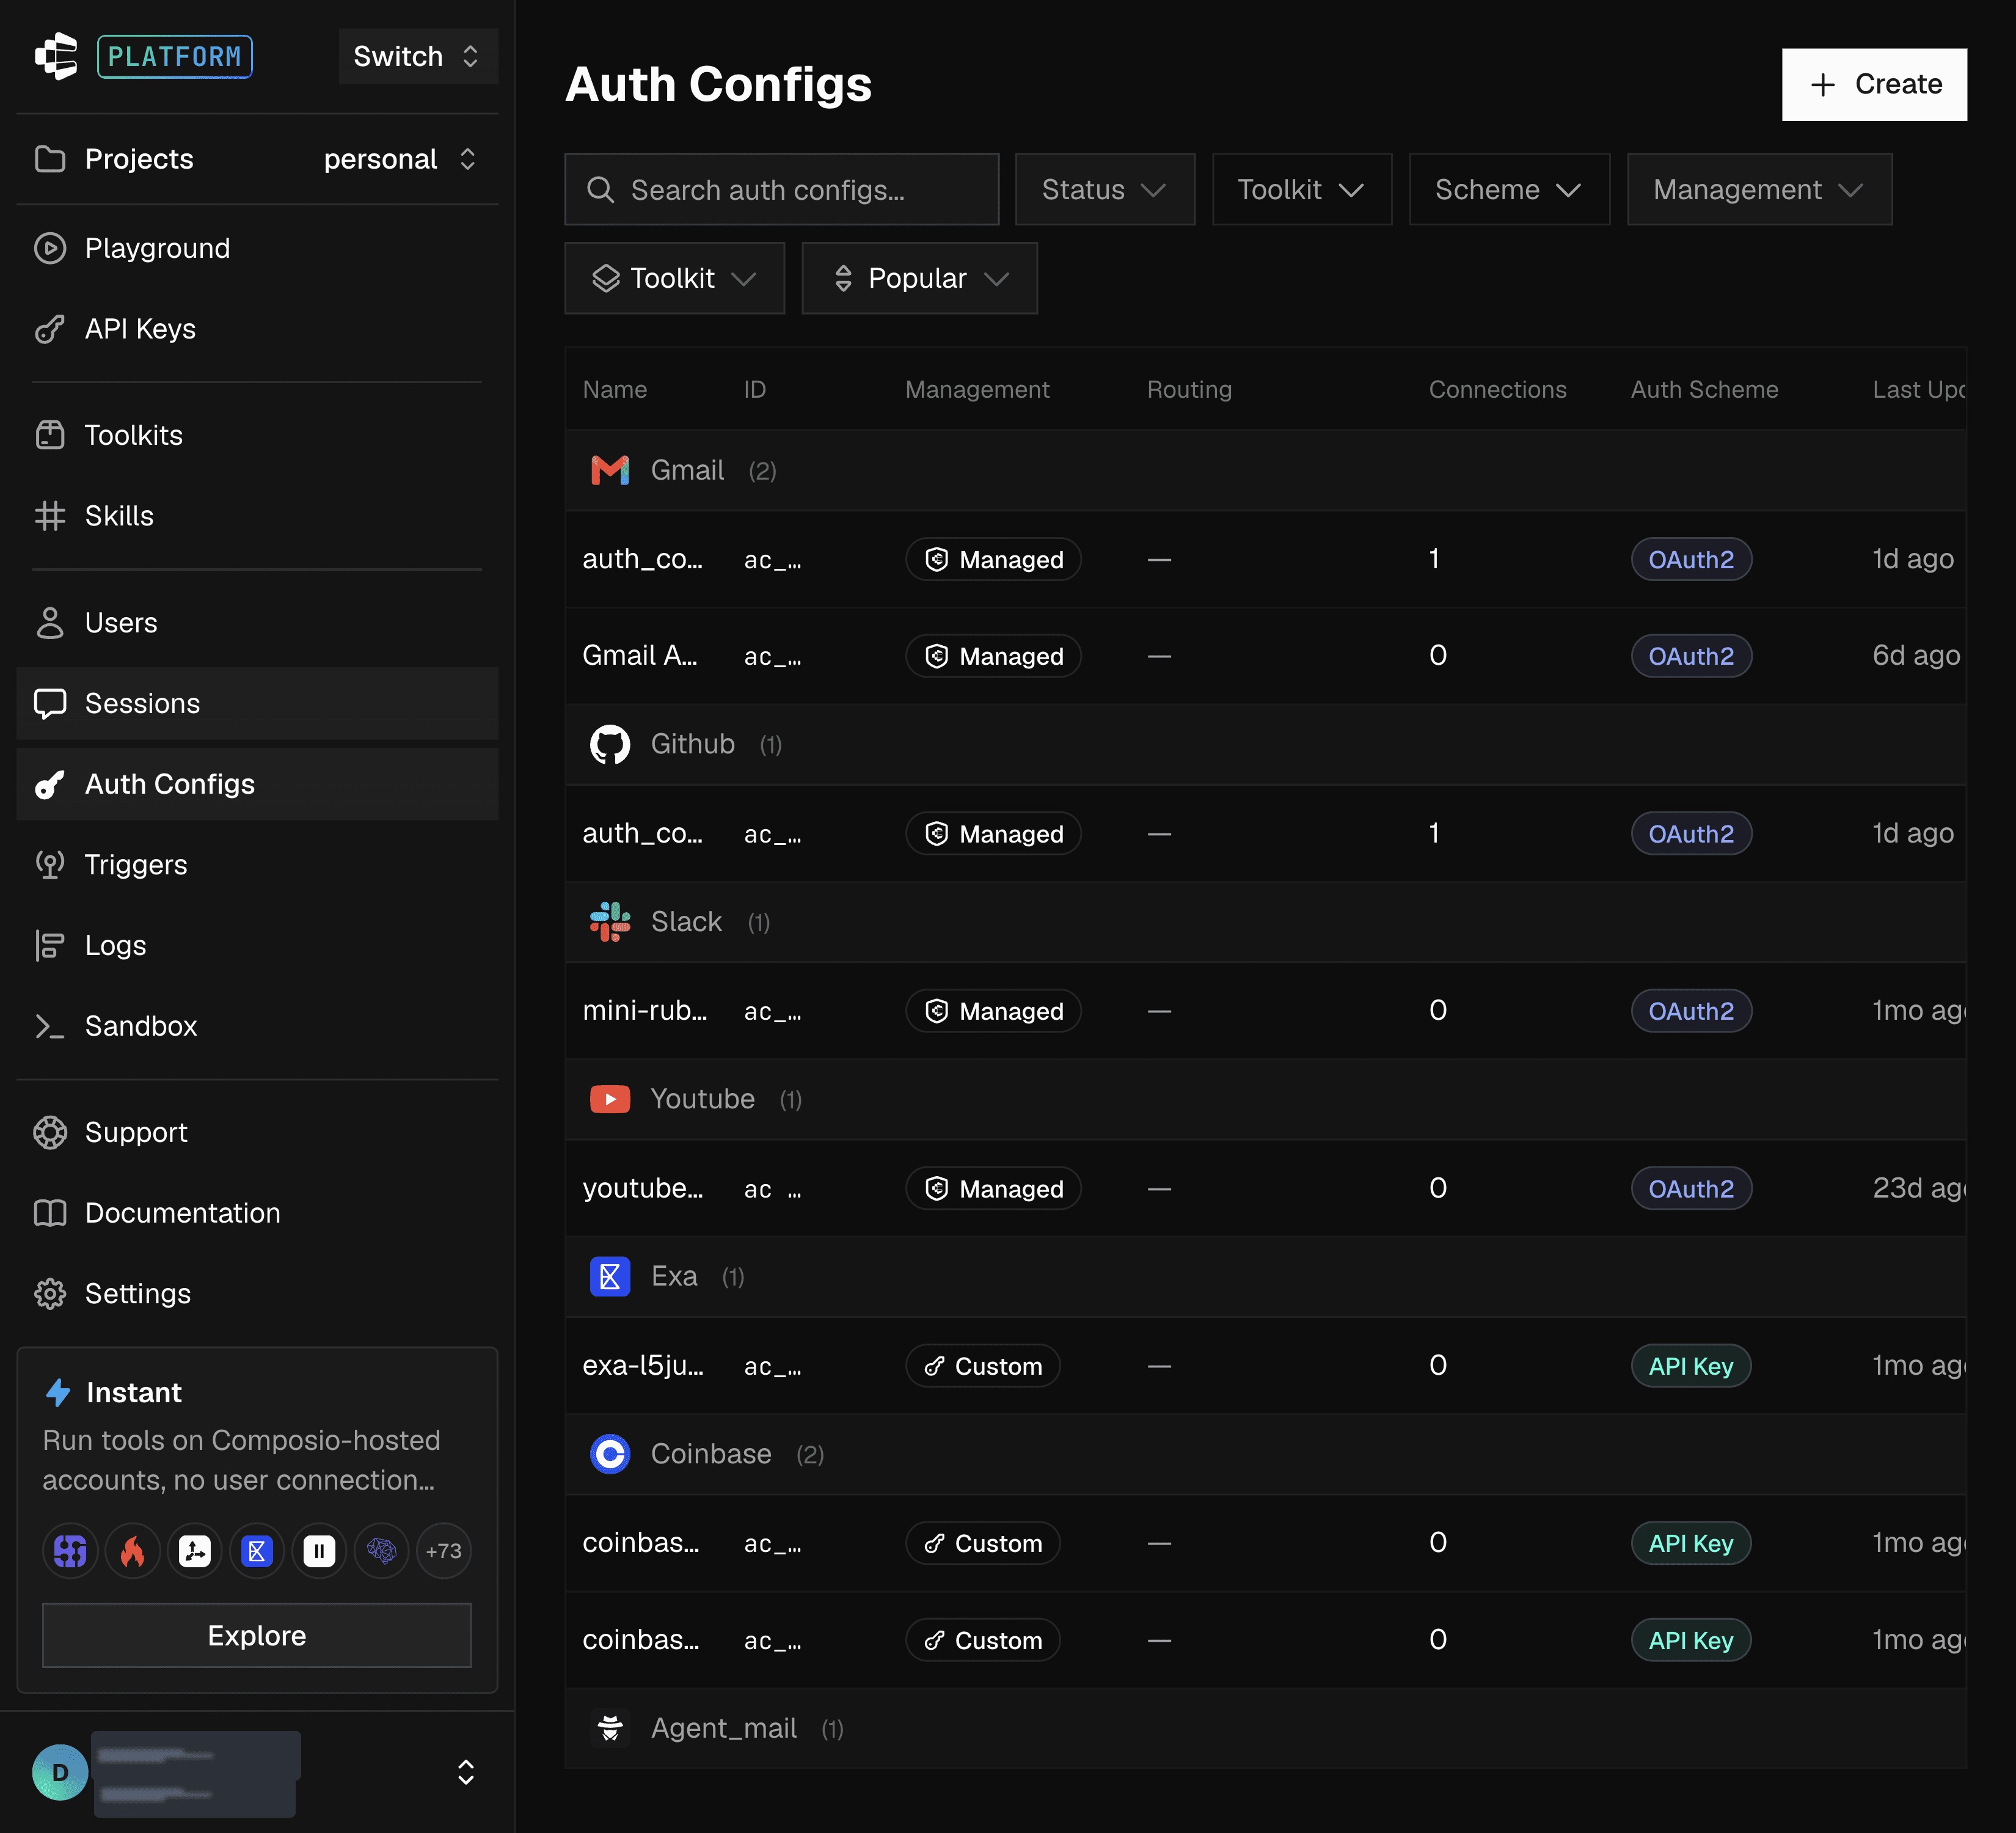
2. Search for OneDrive and select it from the results.

Step 2: Name the Config and Choose Composio Managed
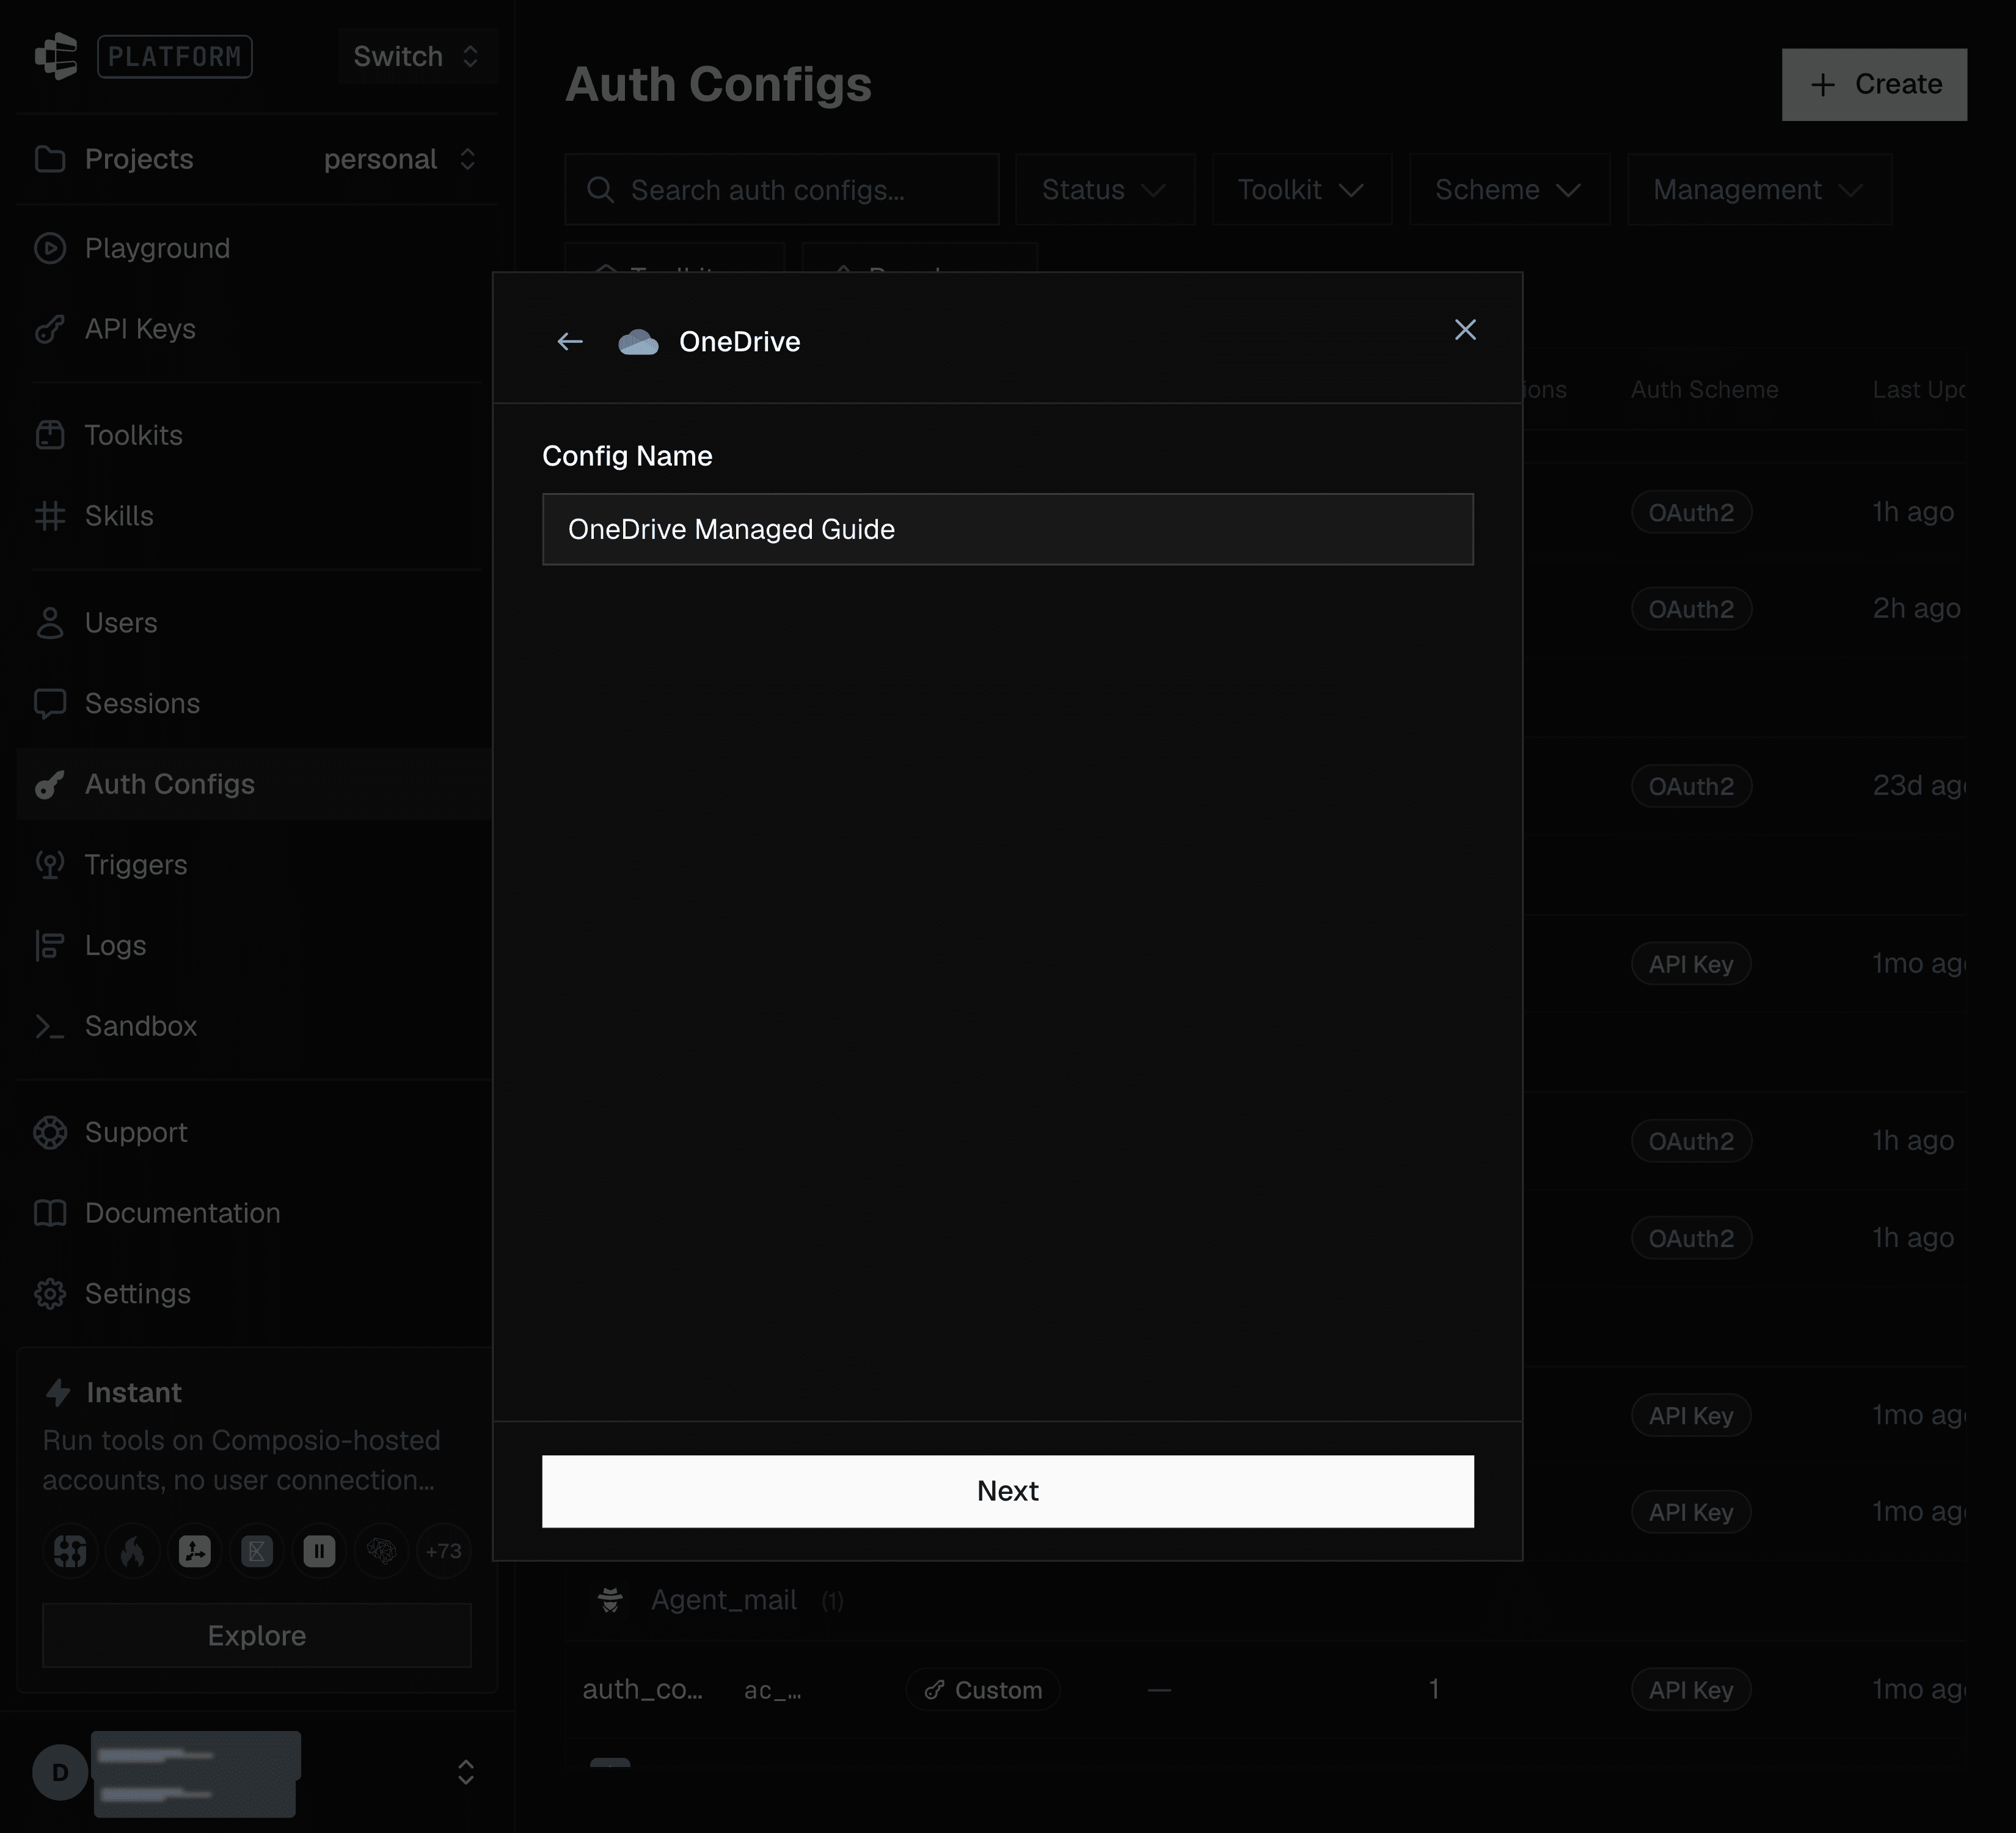
1. Enter a Config Name for your auth config (the screenshots use OneDrive Managed Guide) and click Next.
2. Under Authentication Method, select OAuth 2.0. Under Credentials, select Composio Managed.
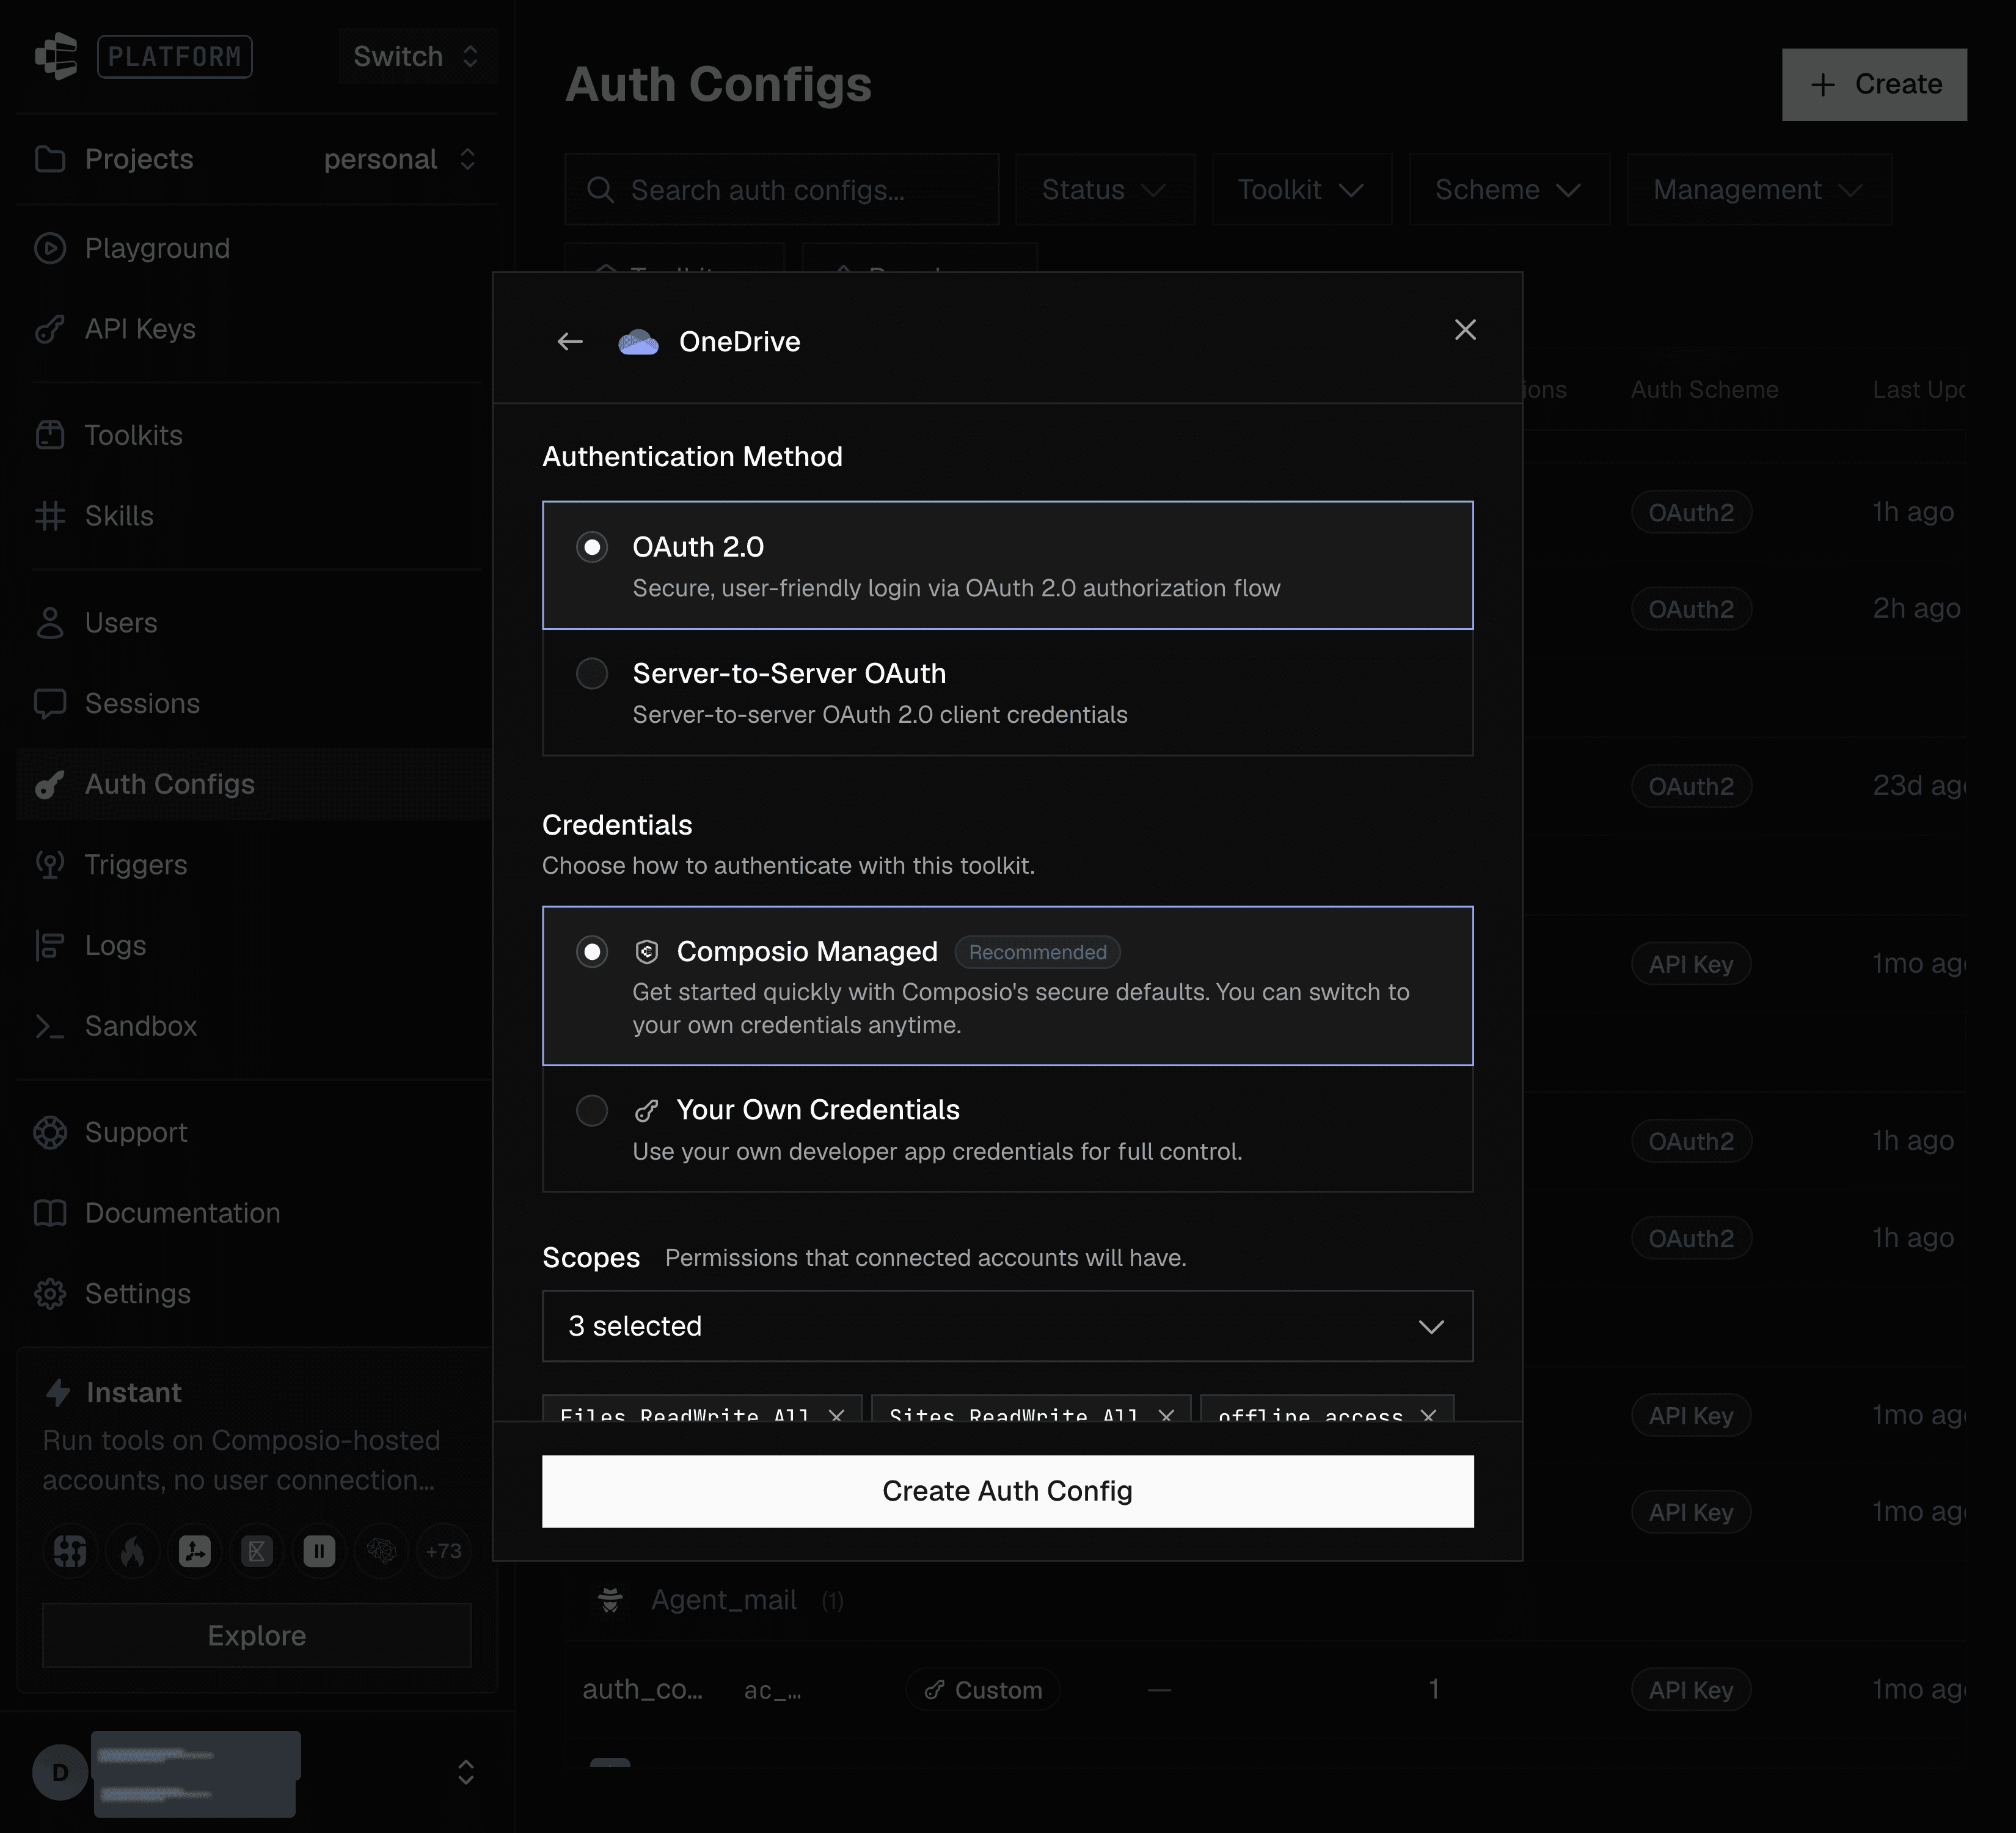
3. Under Scopes, choose permissions required by your integration and supported by your app registration. Click Create Auth Config.
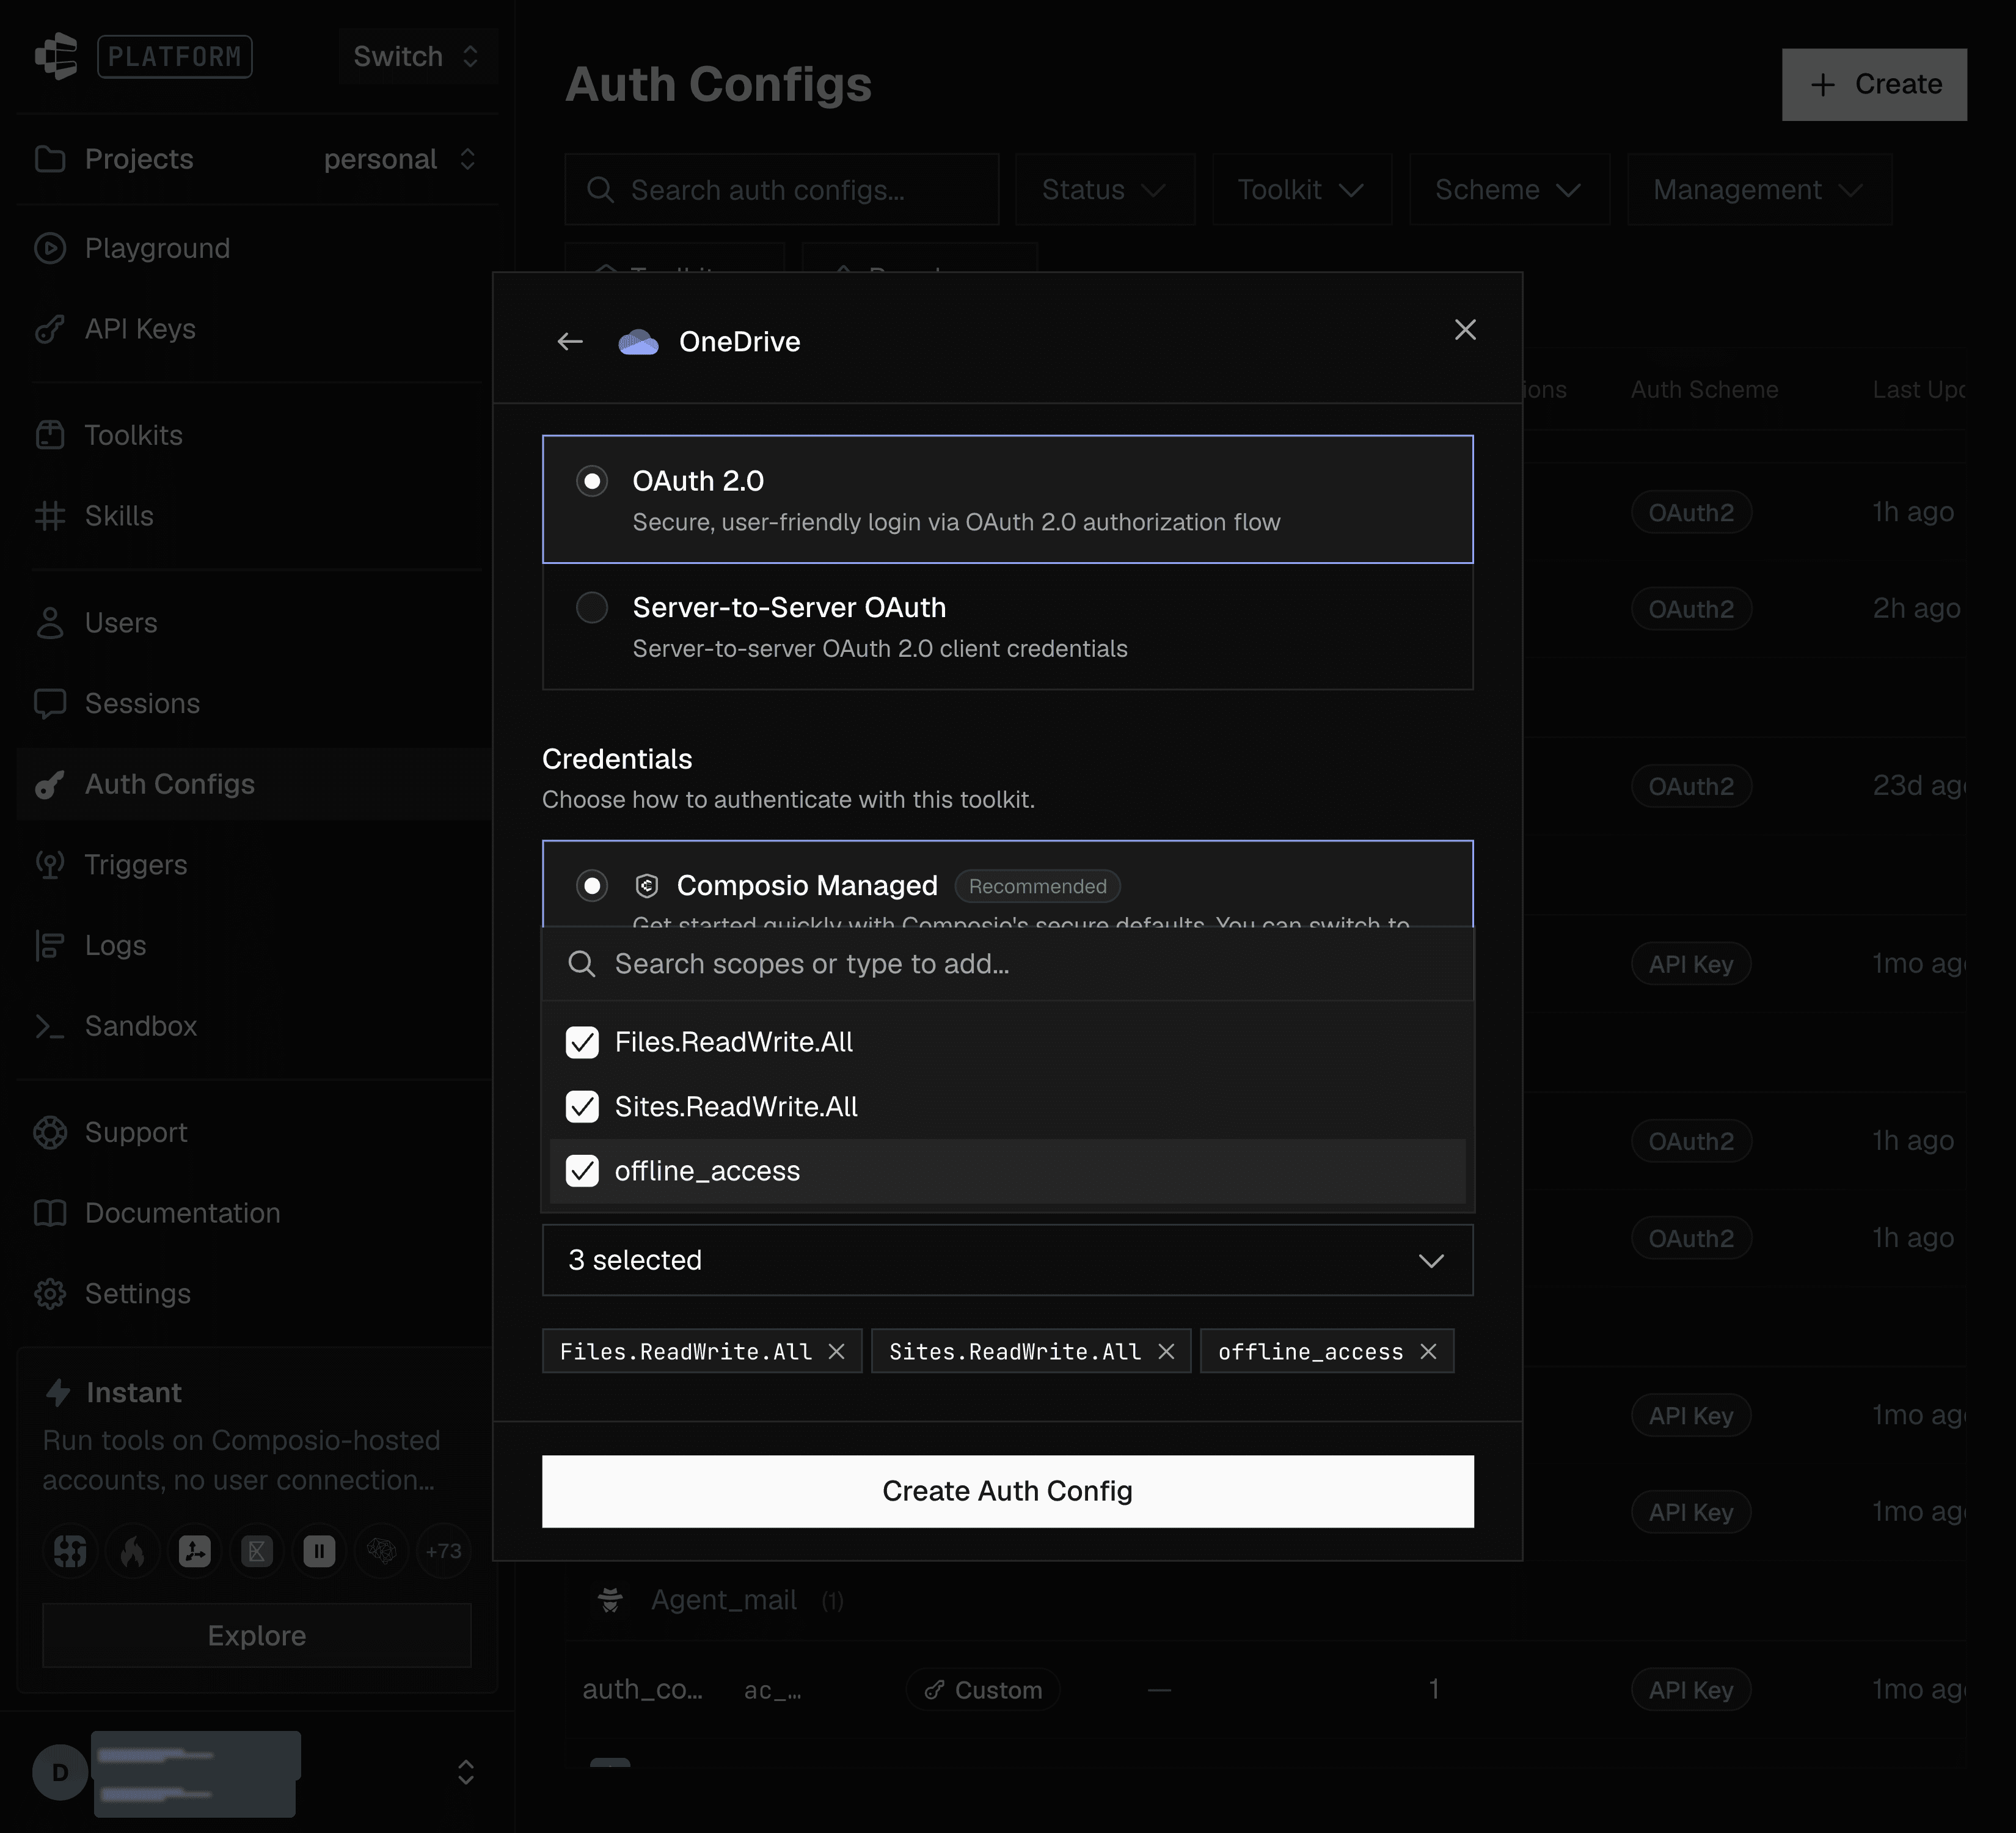
Step 3: Connect Your Microsoft Account
1. Open the auth config and click Connect Account. Then open the generated link.
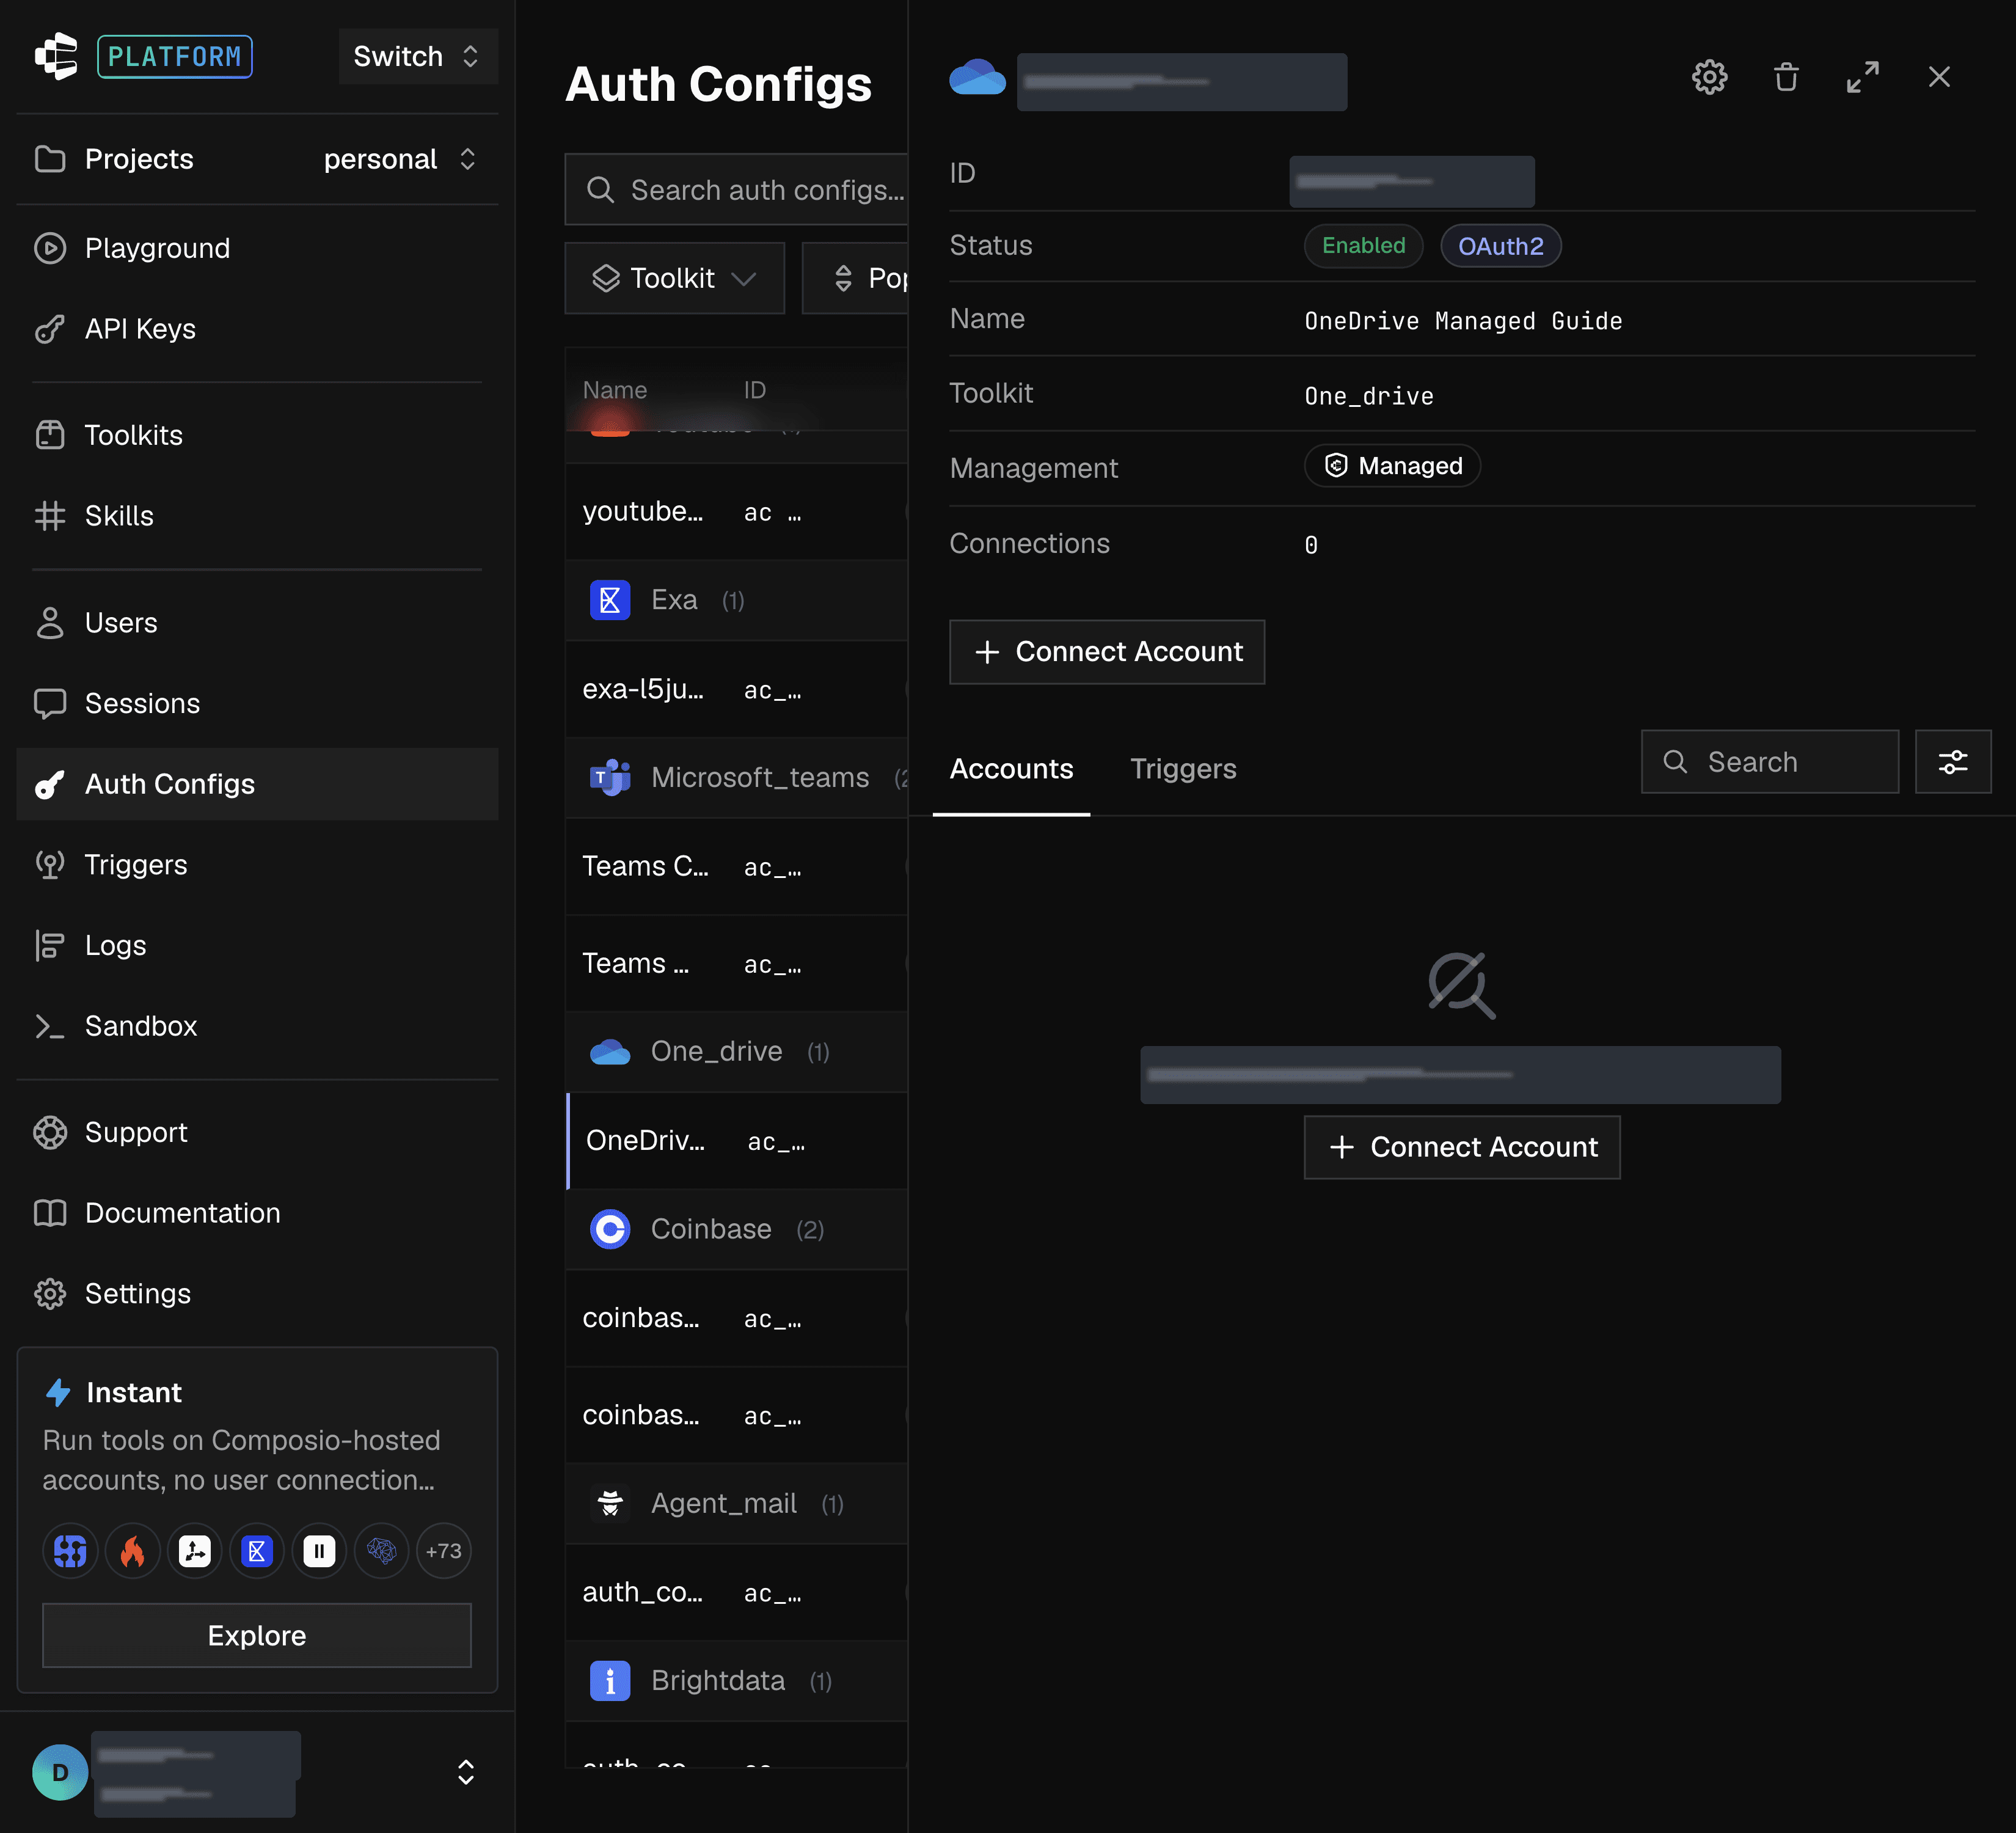
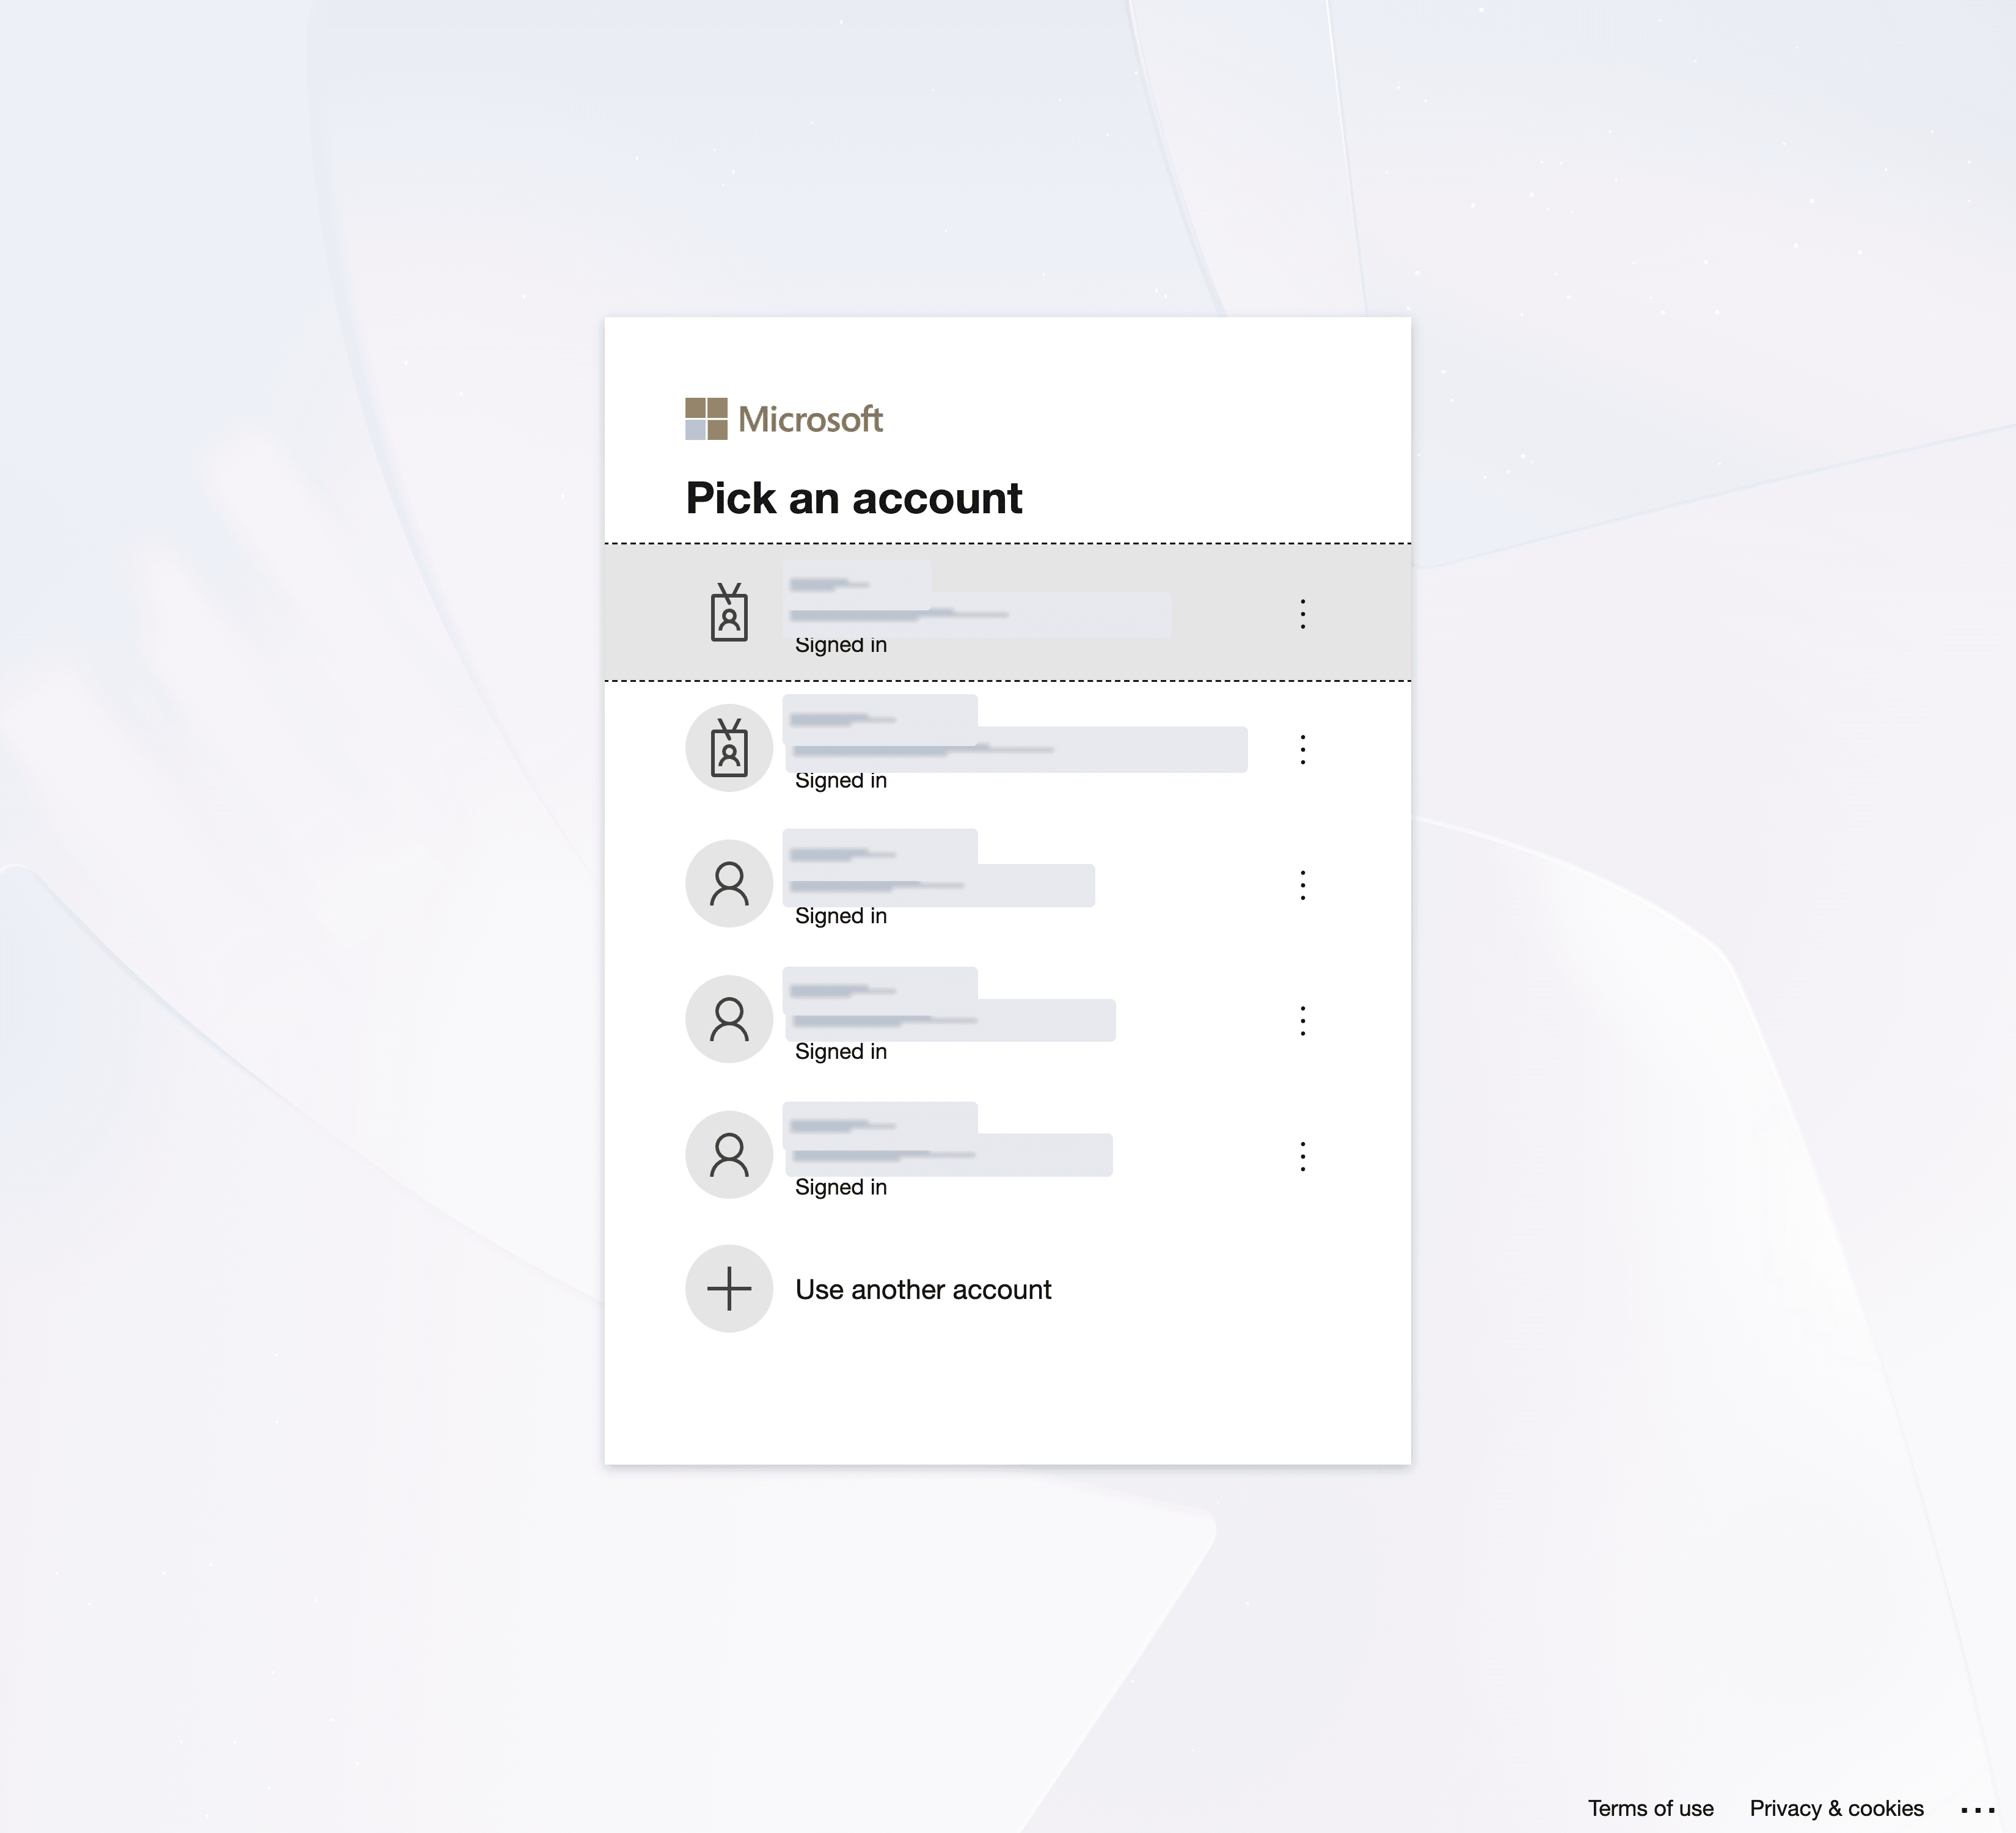
2. Select the Microsoft account you want to connect and sign in. Make sure it is the account whose OneDrive you intend to use.
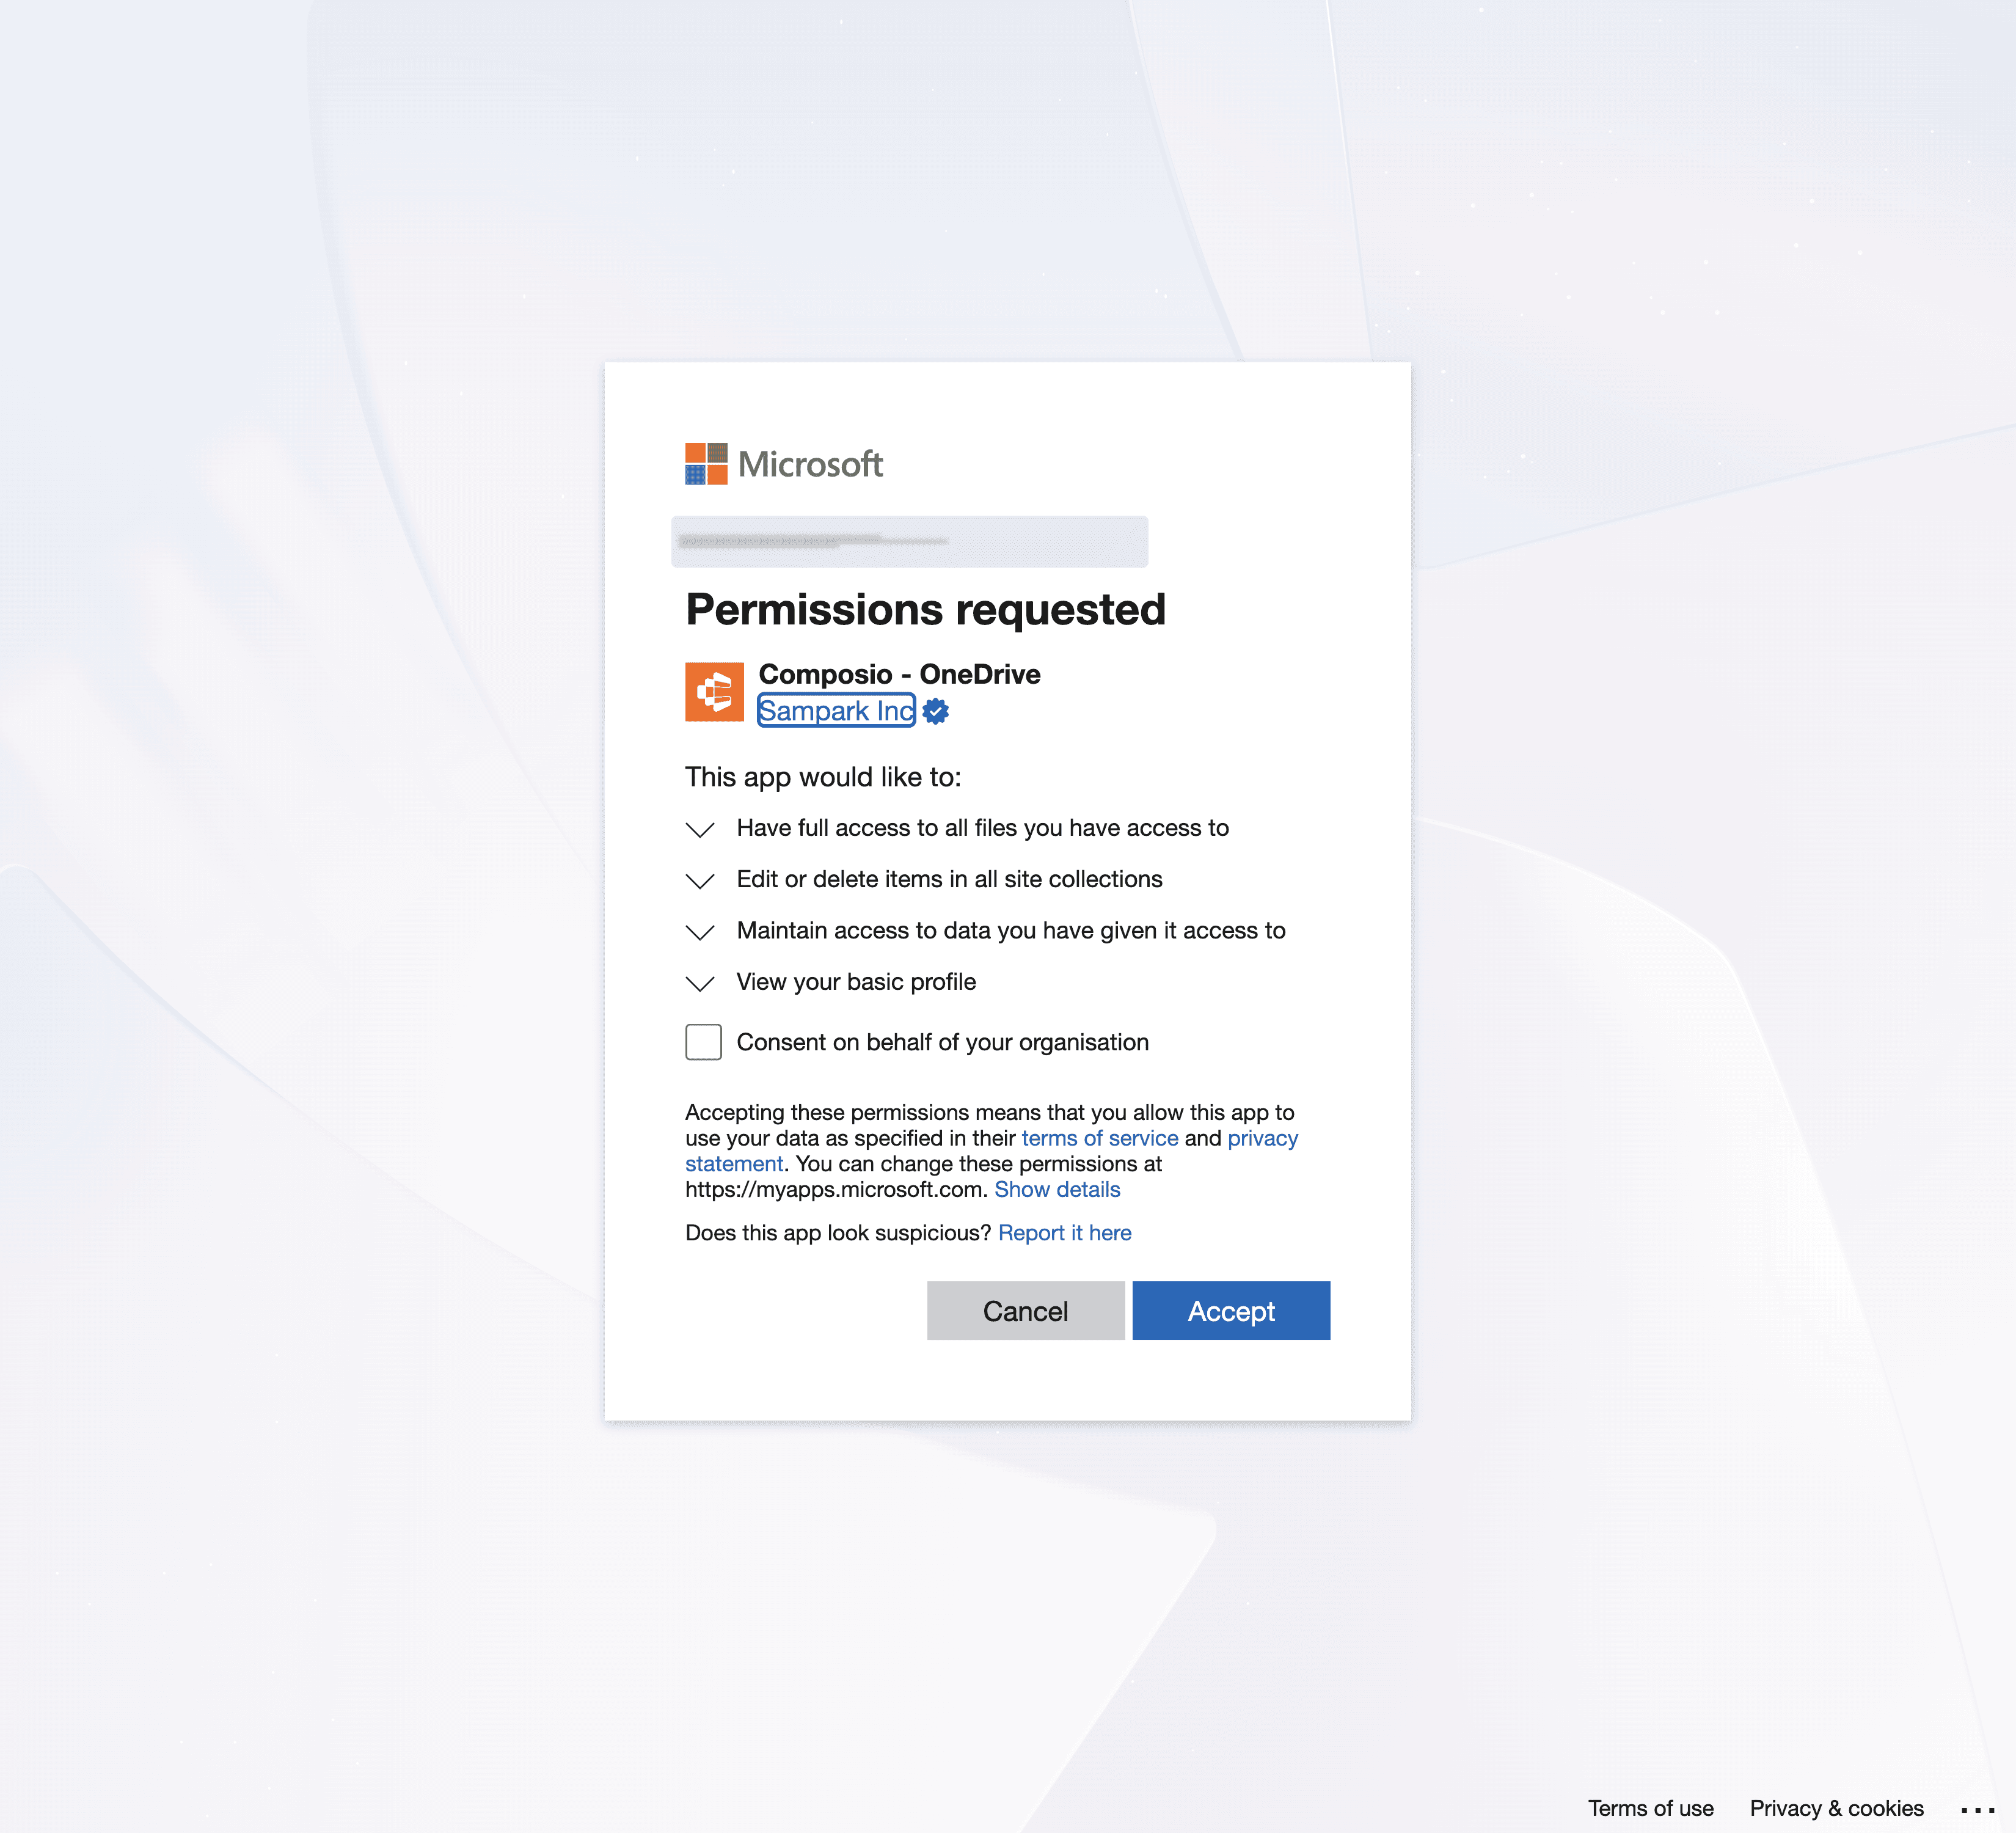
3. If Microsoft asks for permissions, review them and click Accept only if they are appropriate for this account. You may not see this prompt if the account has already consented to these permissions. If your organization restricts app consent, an administrator may need to approve the request before the connection can complete.
Step 4: Confirm the Connected Account Is Active
1. Back in Composio, open the Accounts tab on the auth config. The connected account should show an Active status. The Enabled status at the top of the page refers to the auth config itself, not to a connected account.

Part 2: Use your own OAuth credentials
Step 1: Register an App in Microsoft Entra ID
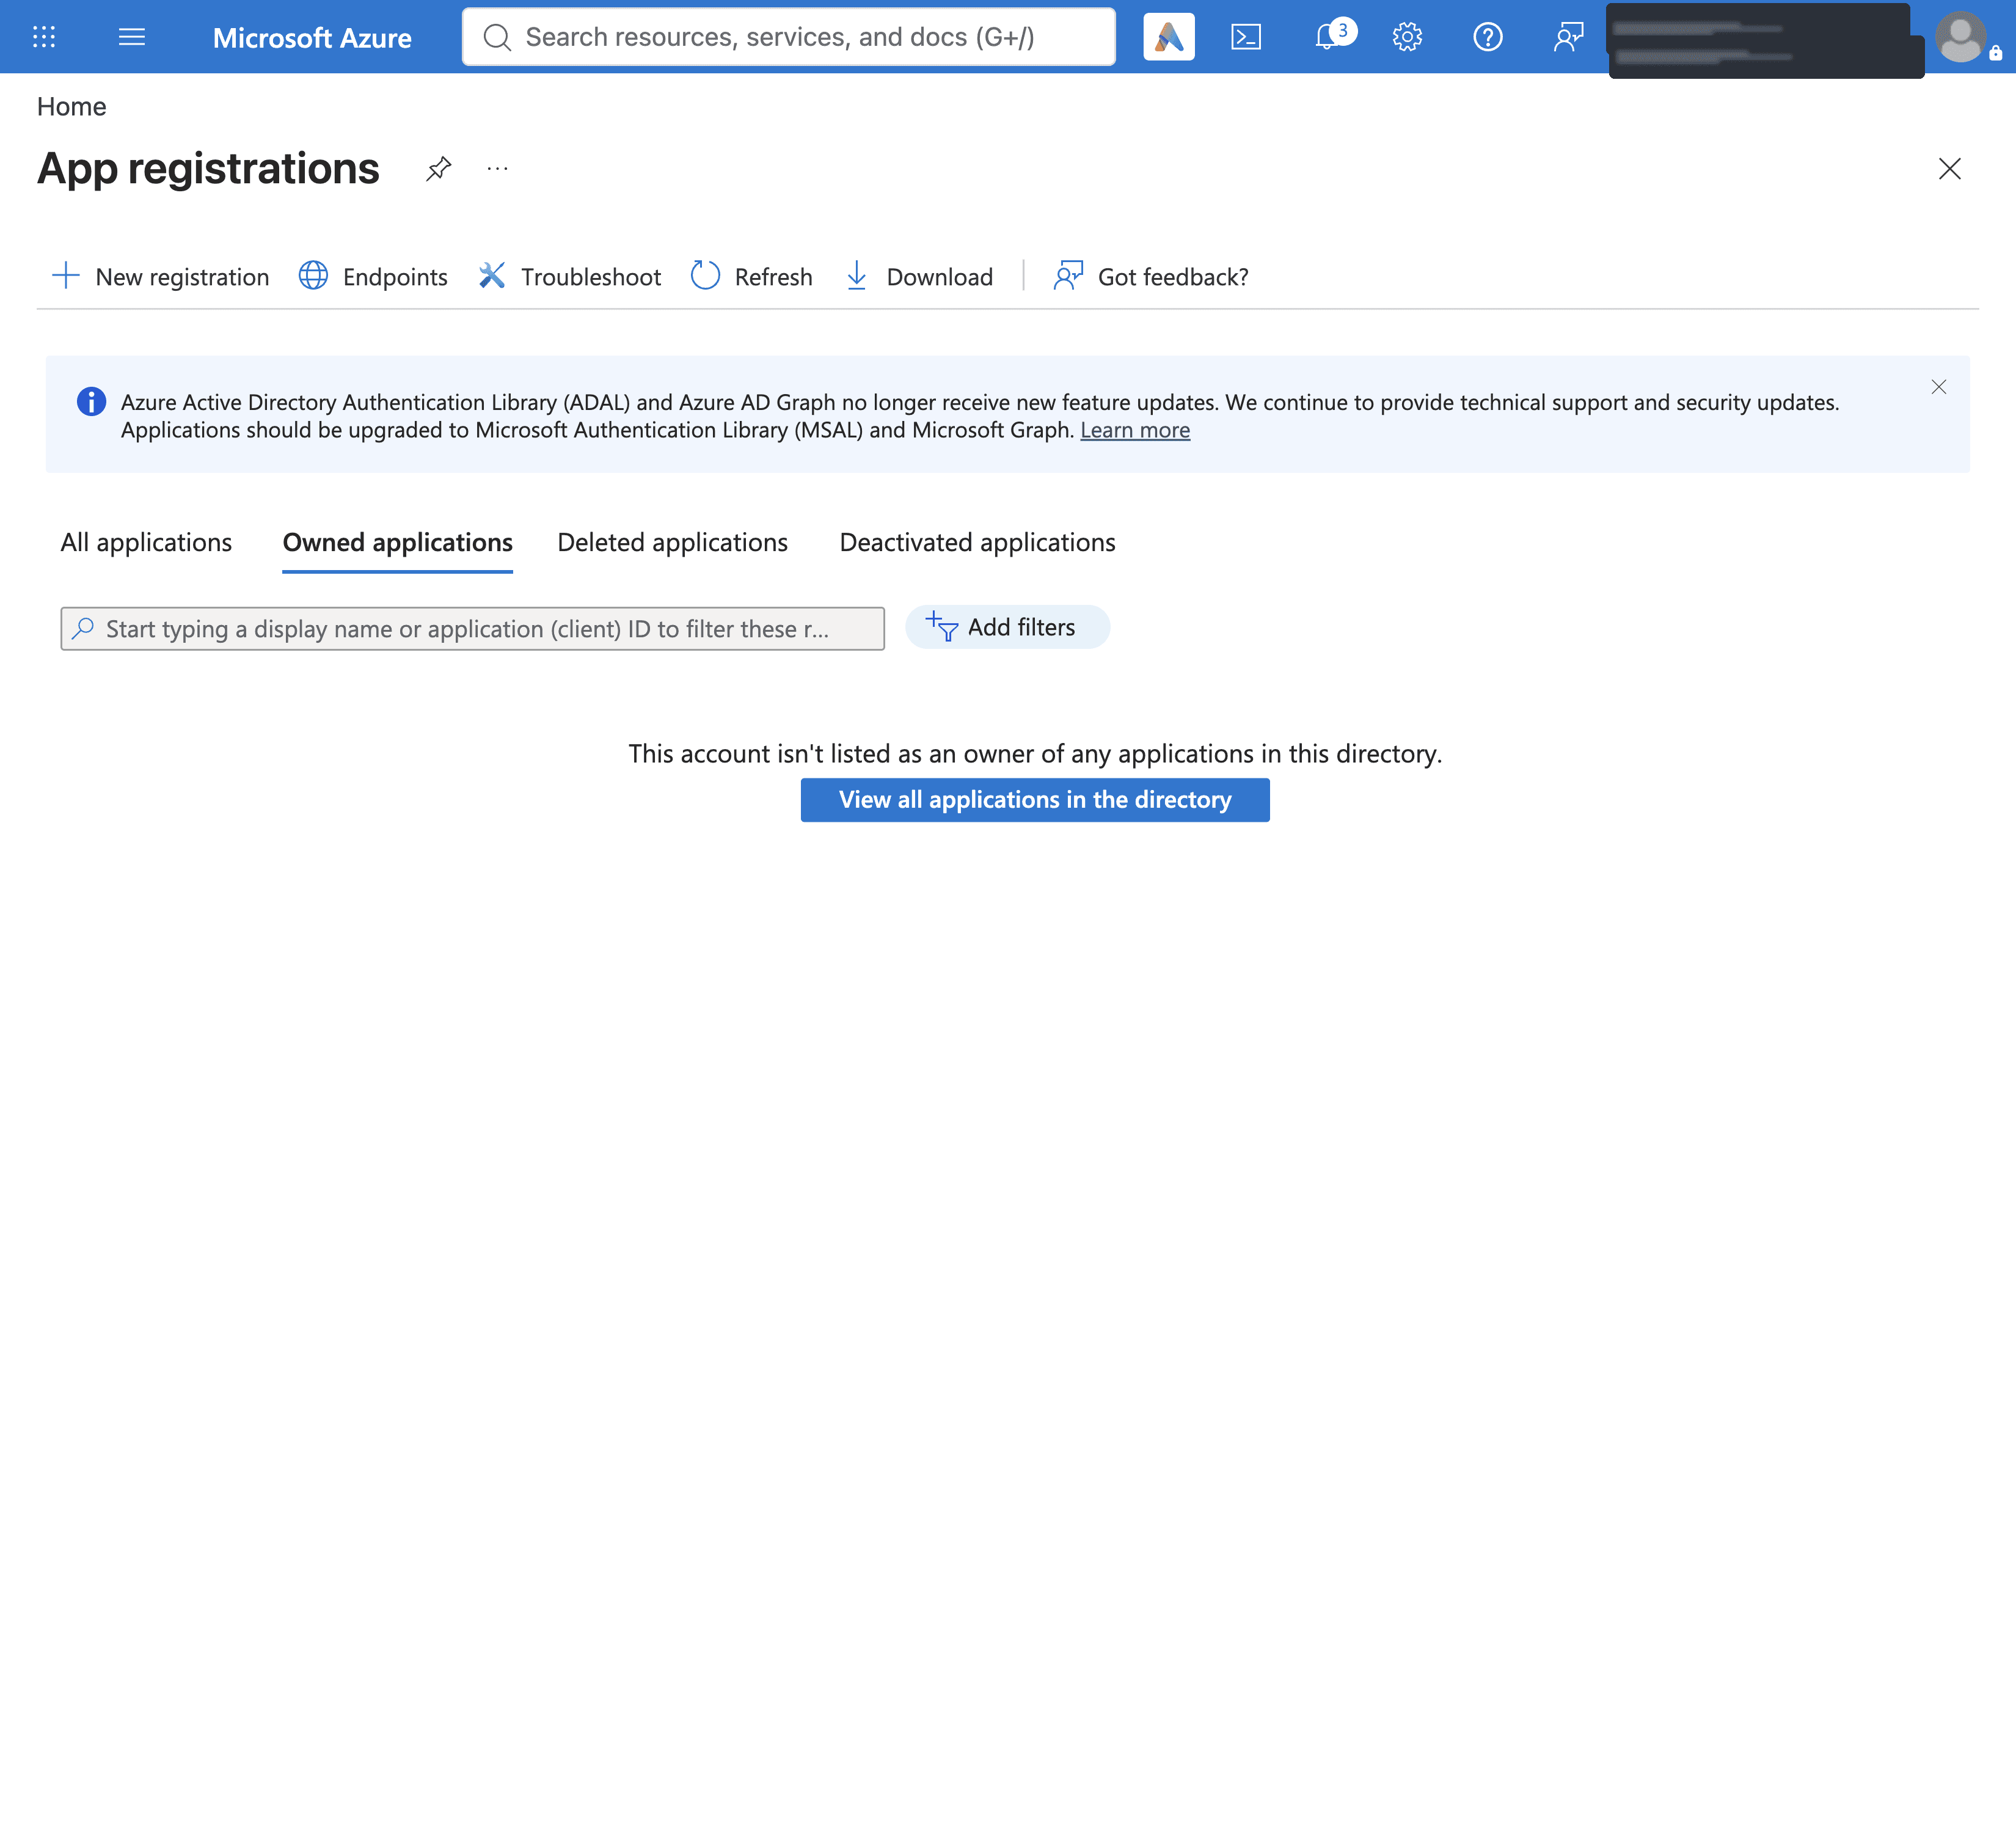
1. Sign in to the Azure portal, open App registrations, and click New registration. Microsoft’s app registration quickstart covers the same steps.
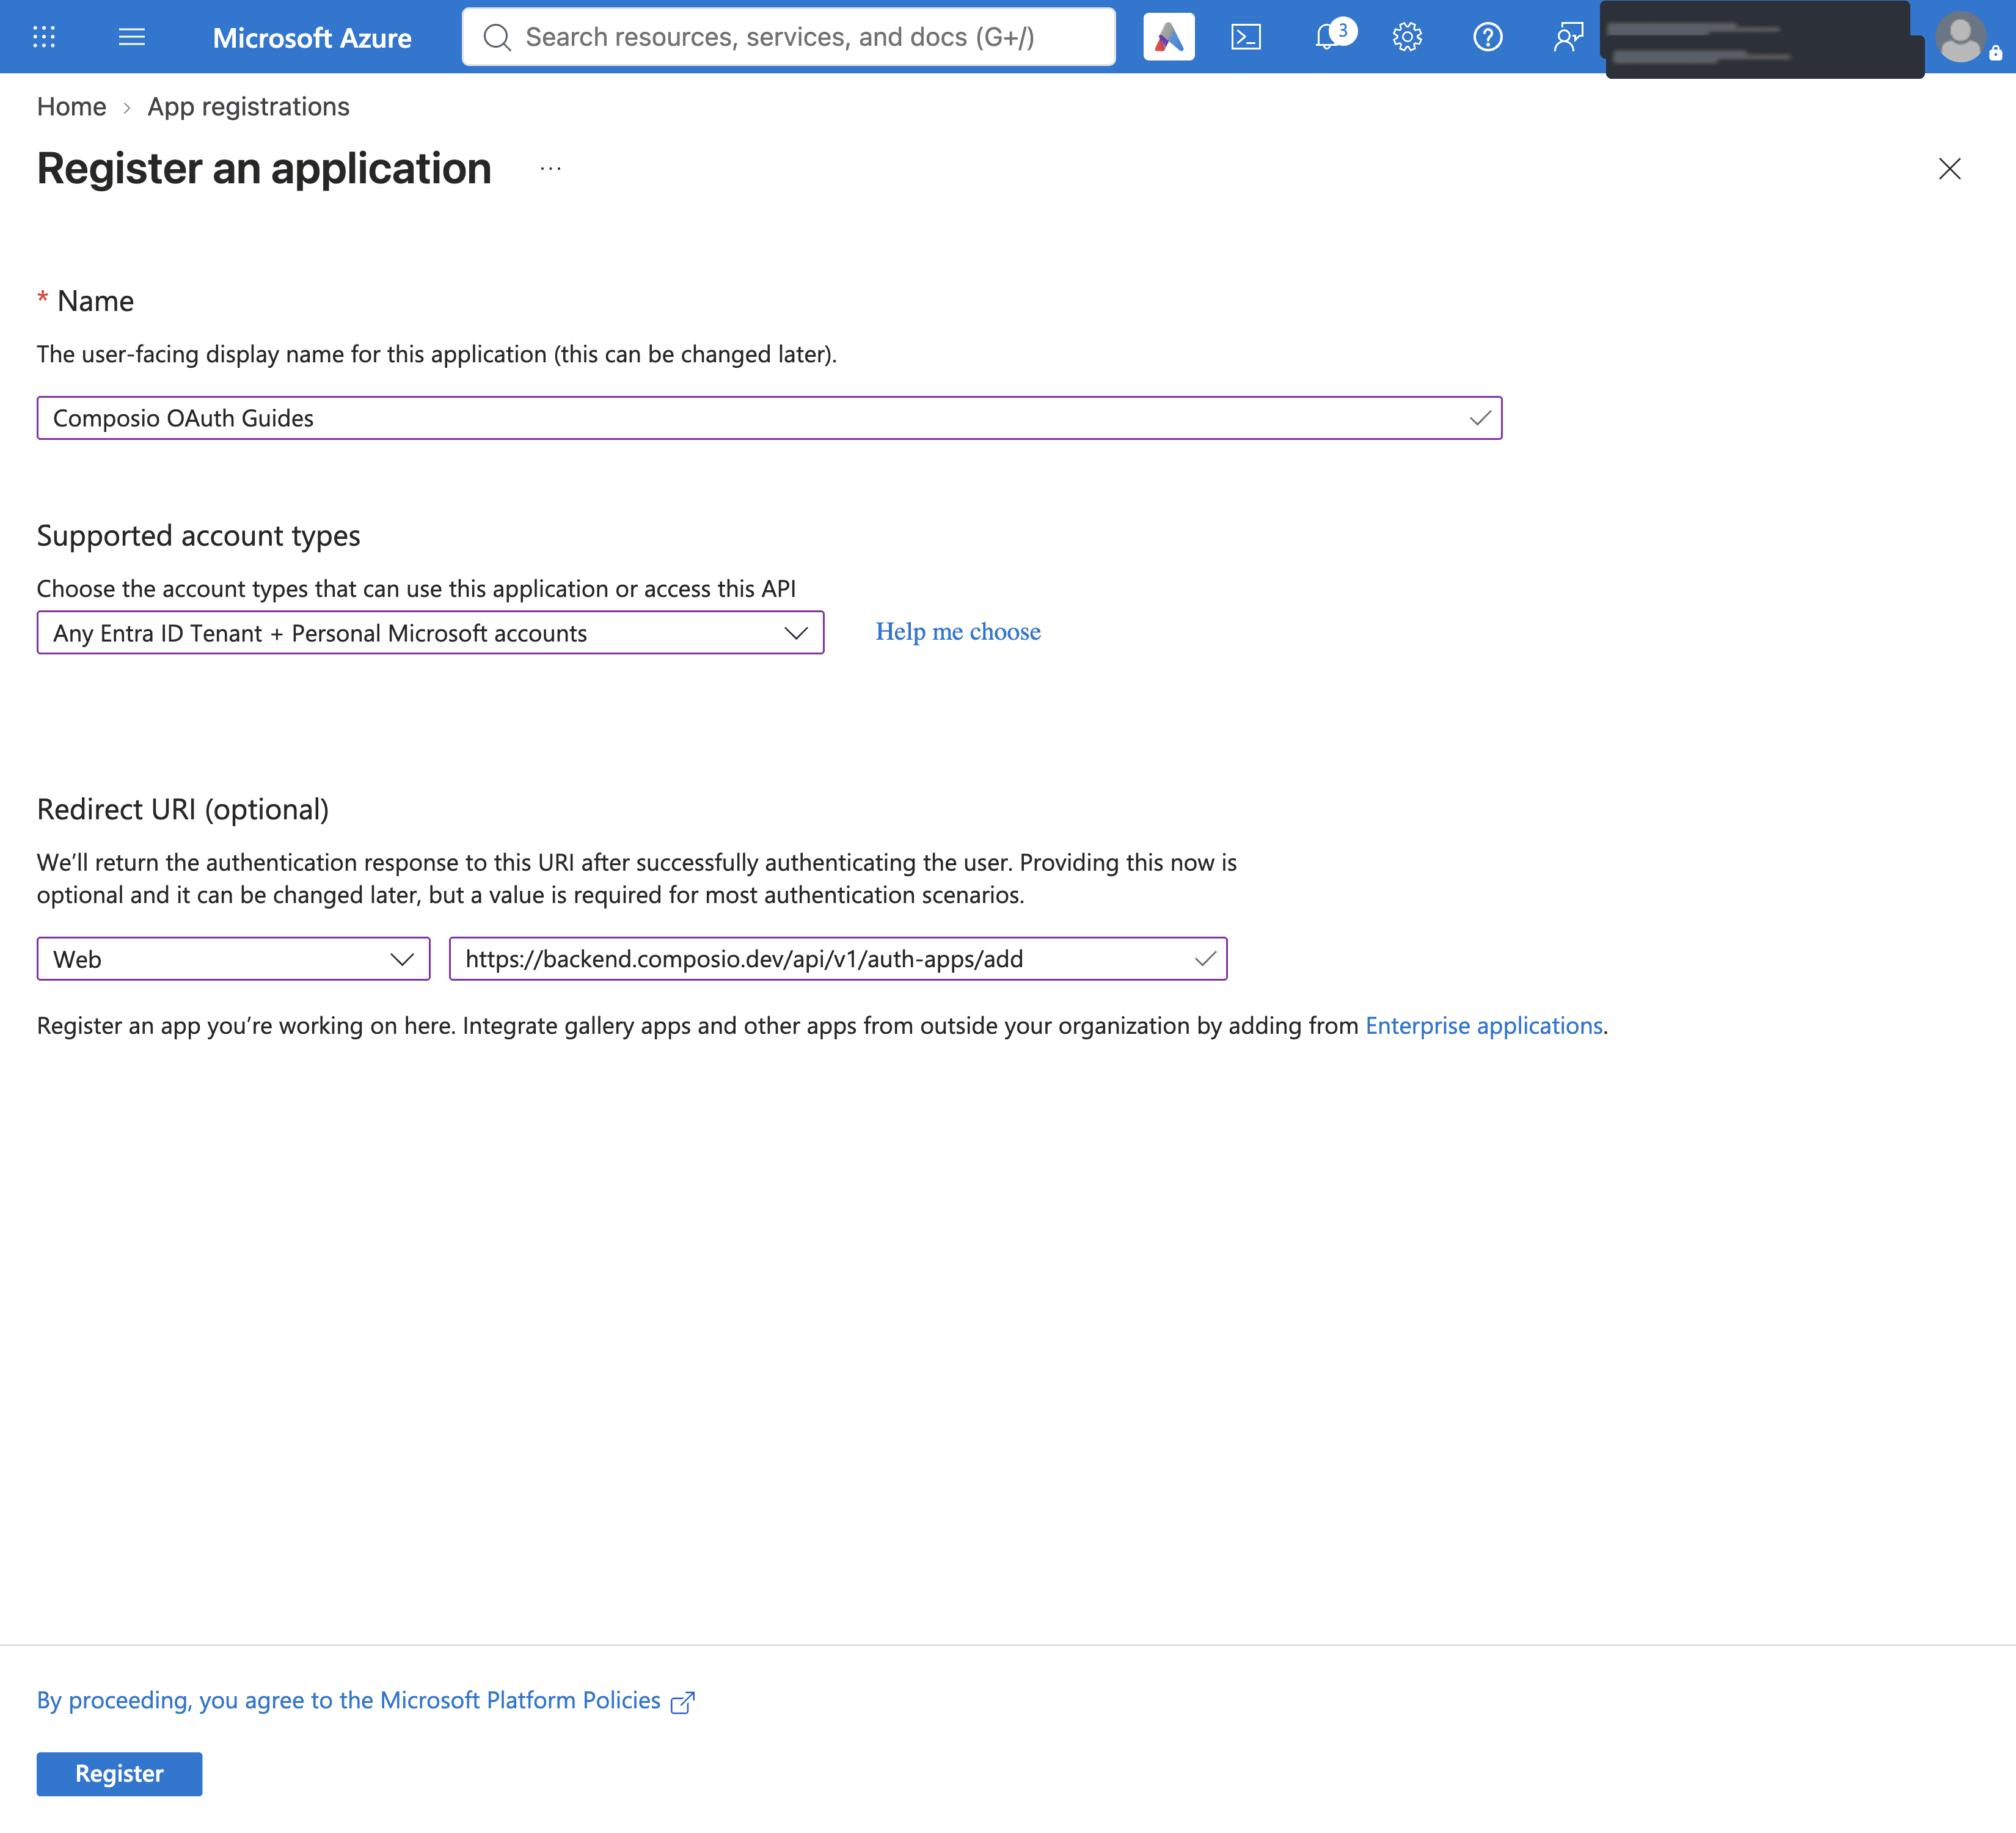
2. Name the app and choose the supported organizational/personal account audience. Select Web, enter the callback below and click Register.
https://backend.composio.dev/api/v1/auth-apps/add
Step 2: Copy the Client ID and Create a Client Secret
1. On the app’s Overview page, copy the Application (client) ID. This is the Client ID you will enter in Composio.

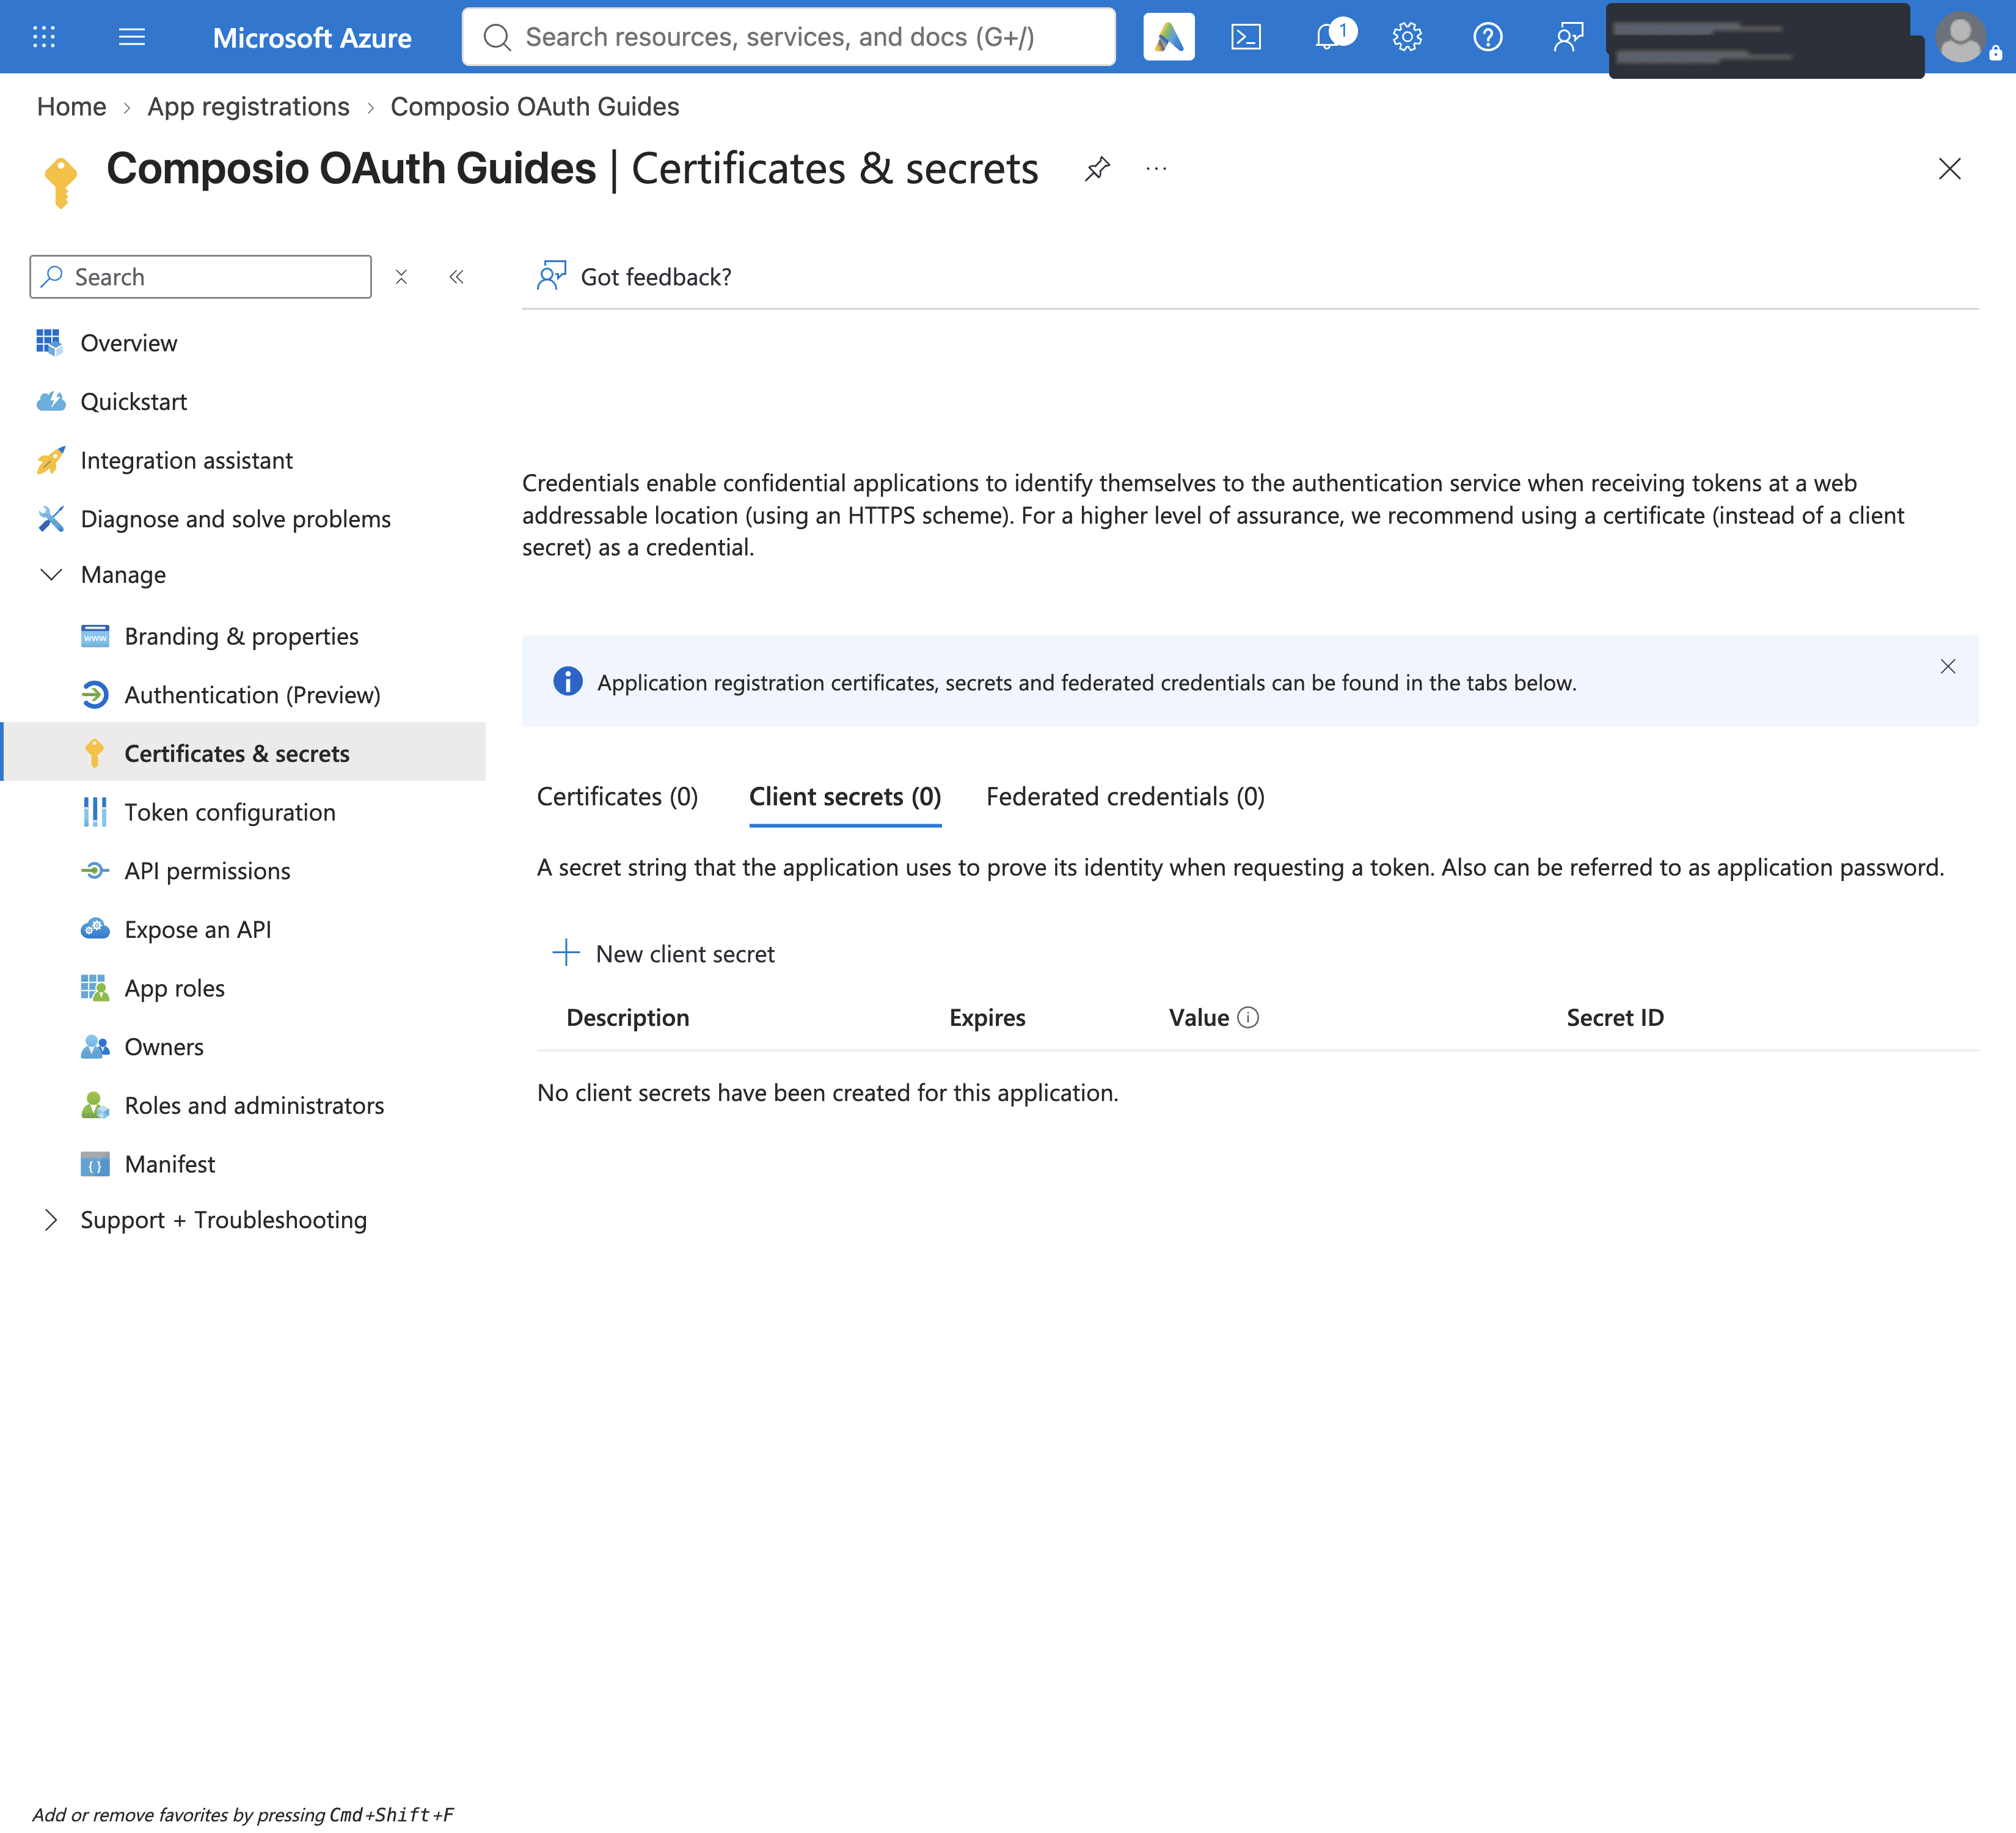
2. Open Certificates & secrets and click New client secret.
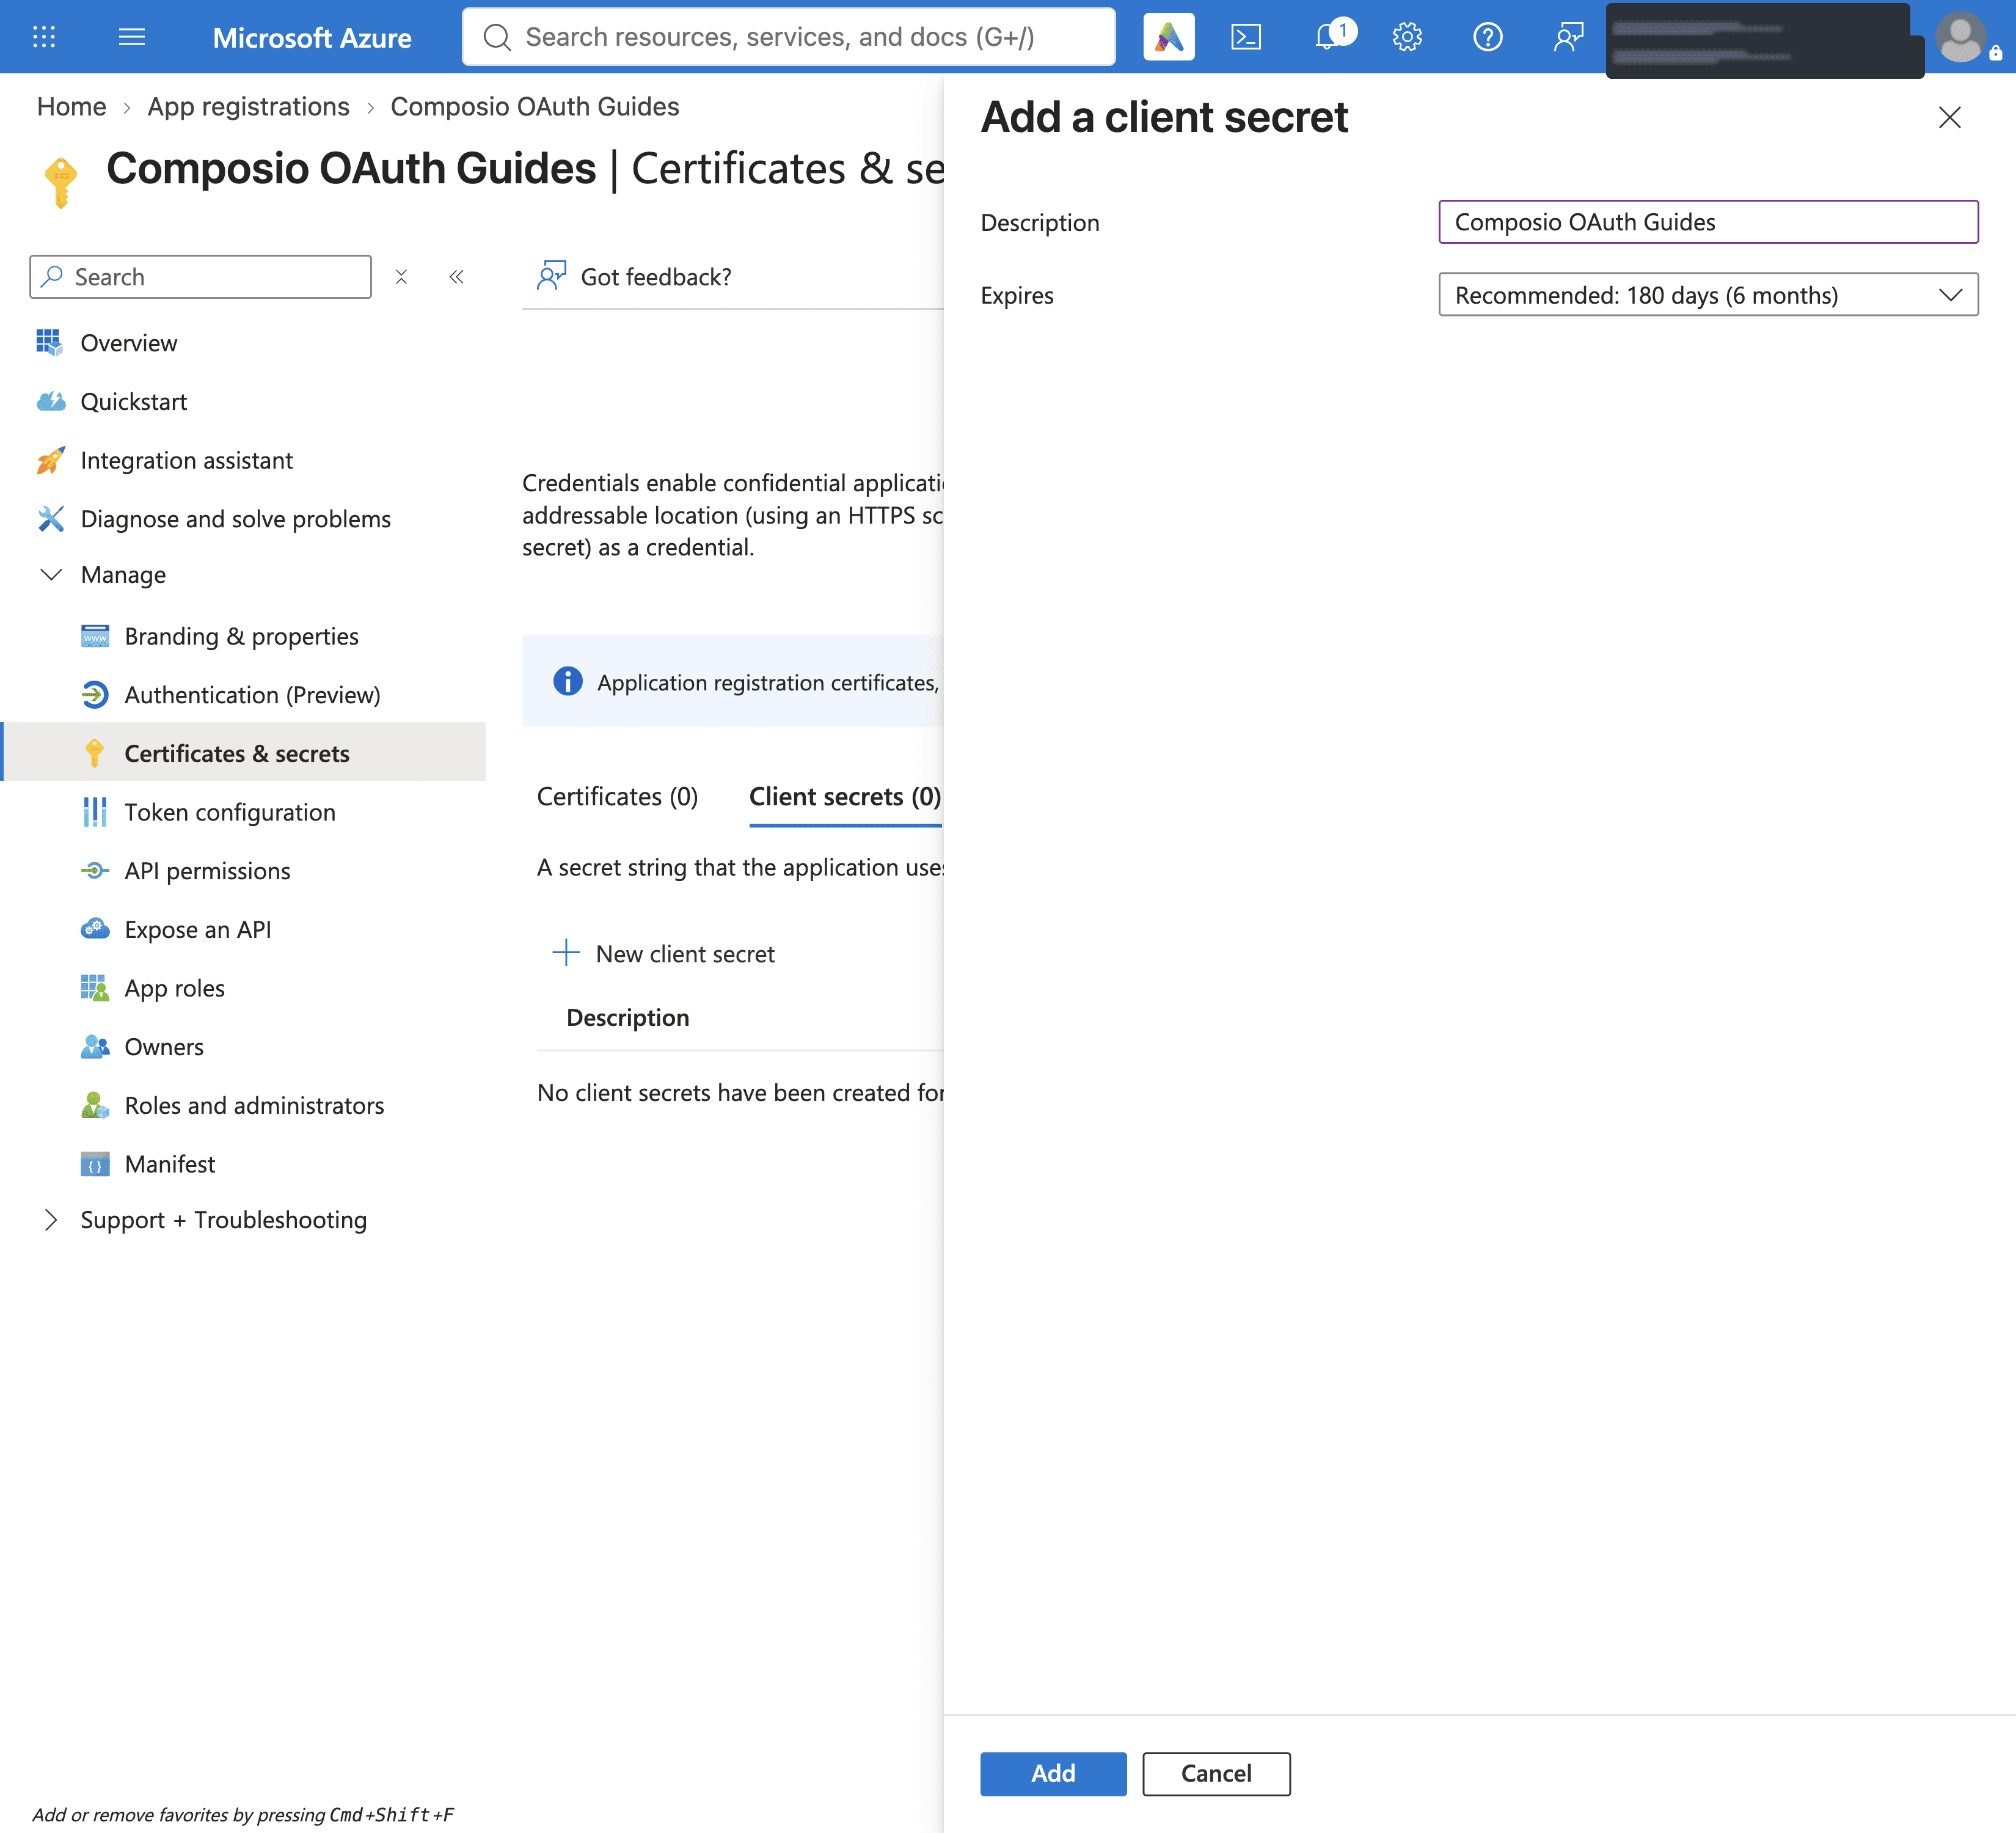
3. Add a description and choose an expiry that fits your rotation policy, then click Add. The screenshots use a 180-day expiry. Plan to rotate the secret before it expires.
4. Copy the secret Value immediately and store it privately. Use the Value, not the Secret ID. Azure shows the Value only once, so if you leave the page without copying it you will need to create a new secret. Do not enable public client flows for this confidential Web client.

Step 3: Add Microsoft Graph Permissions
1. Open API permissions and click Add a permission.
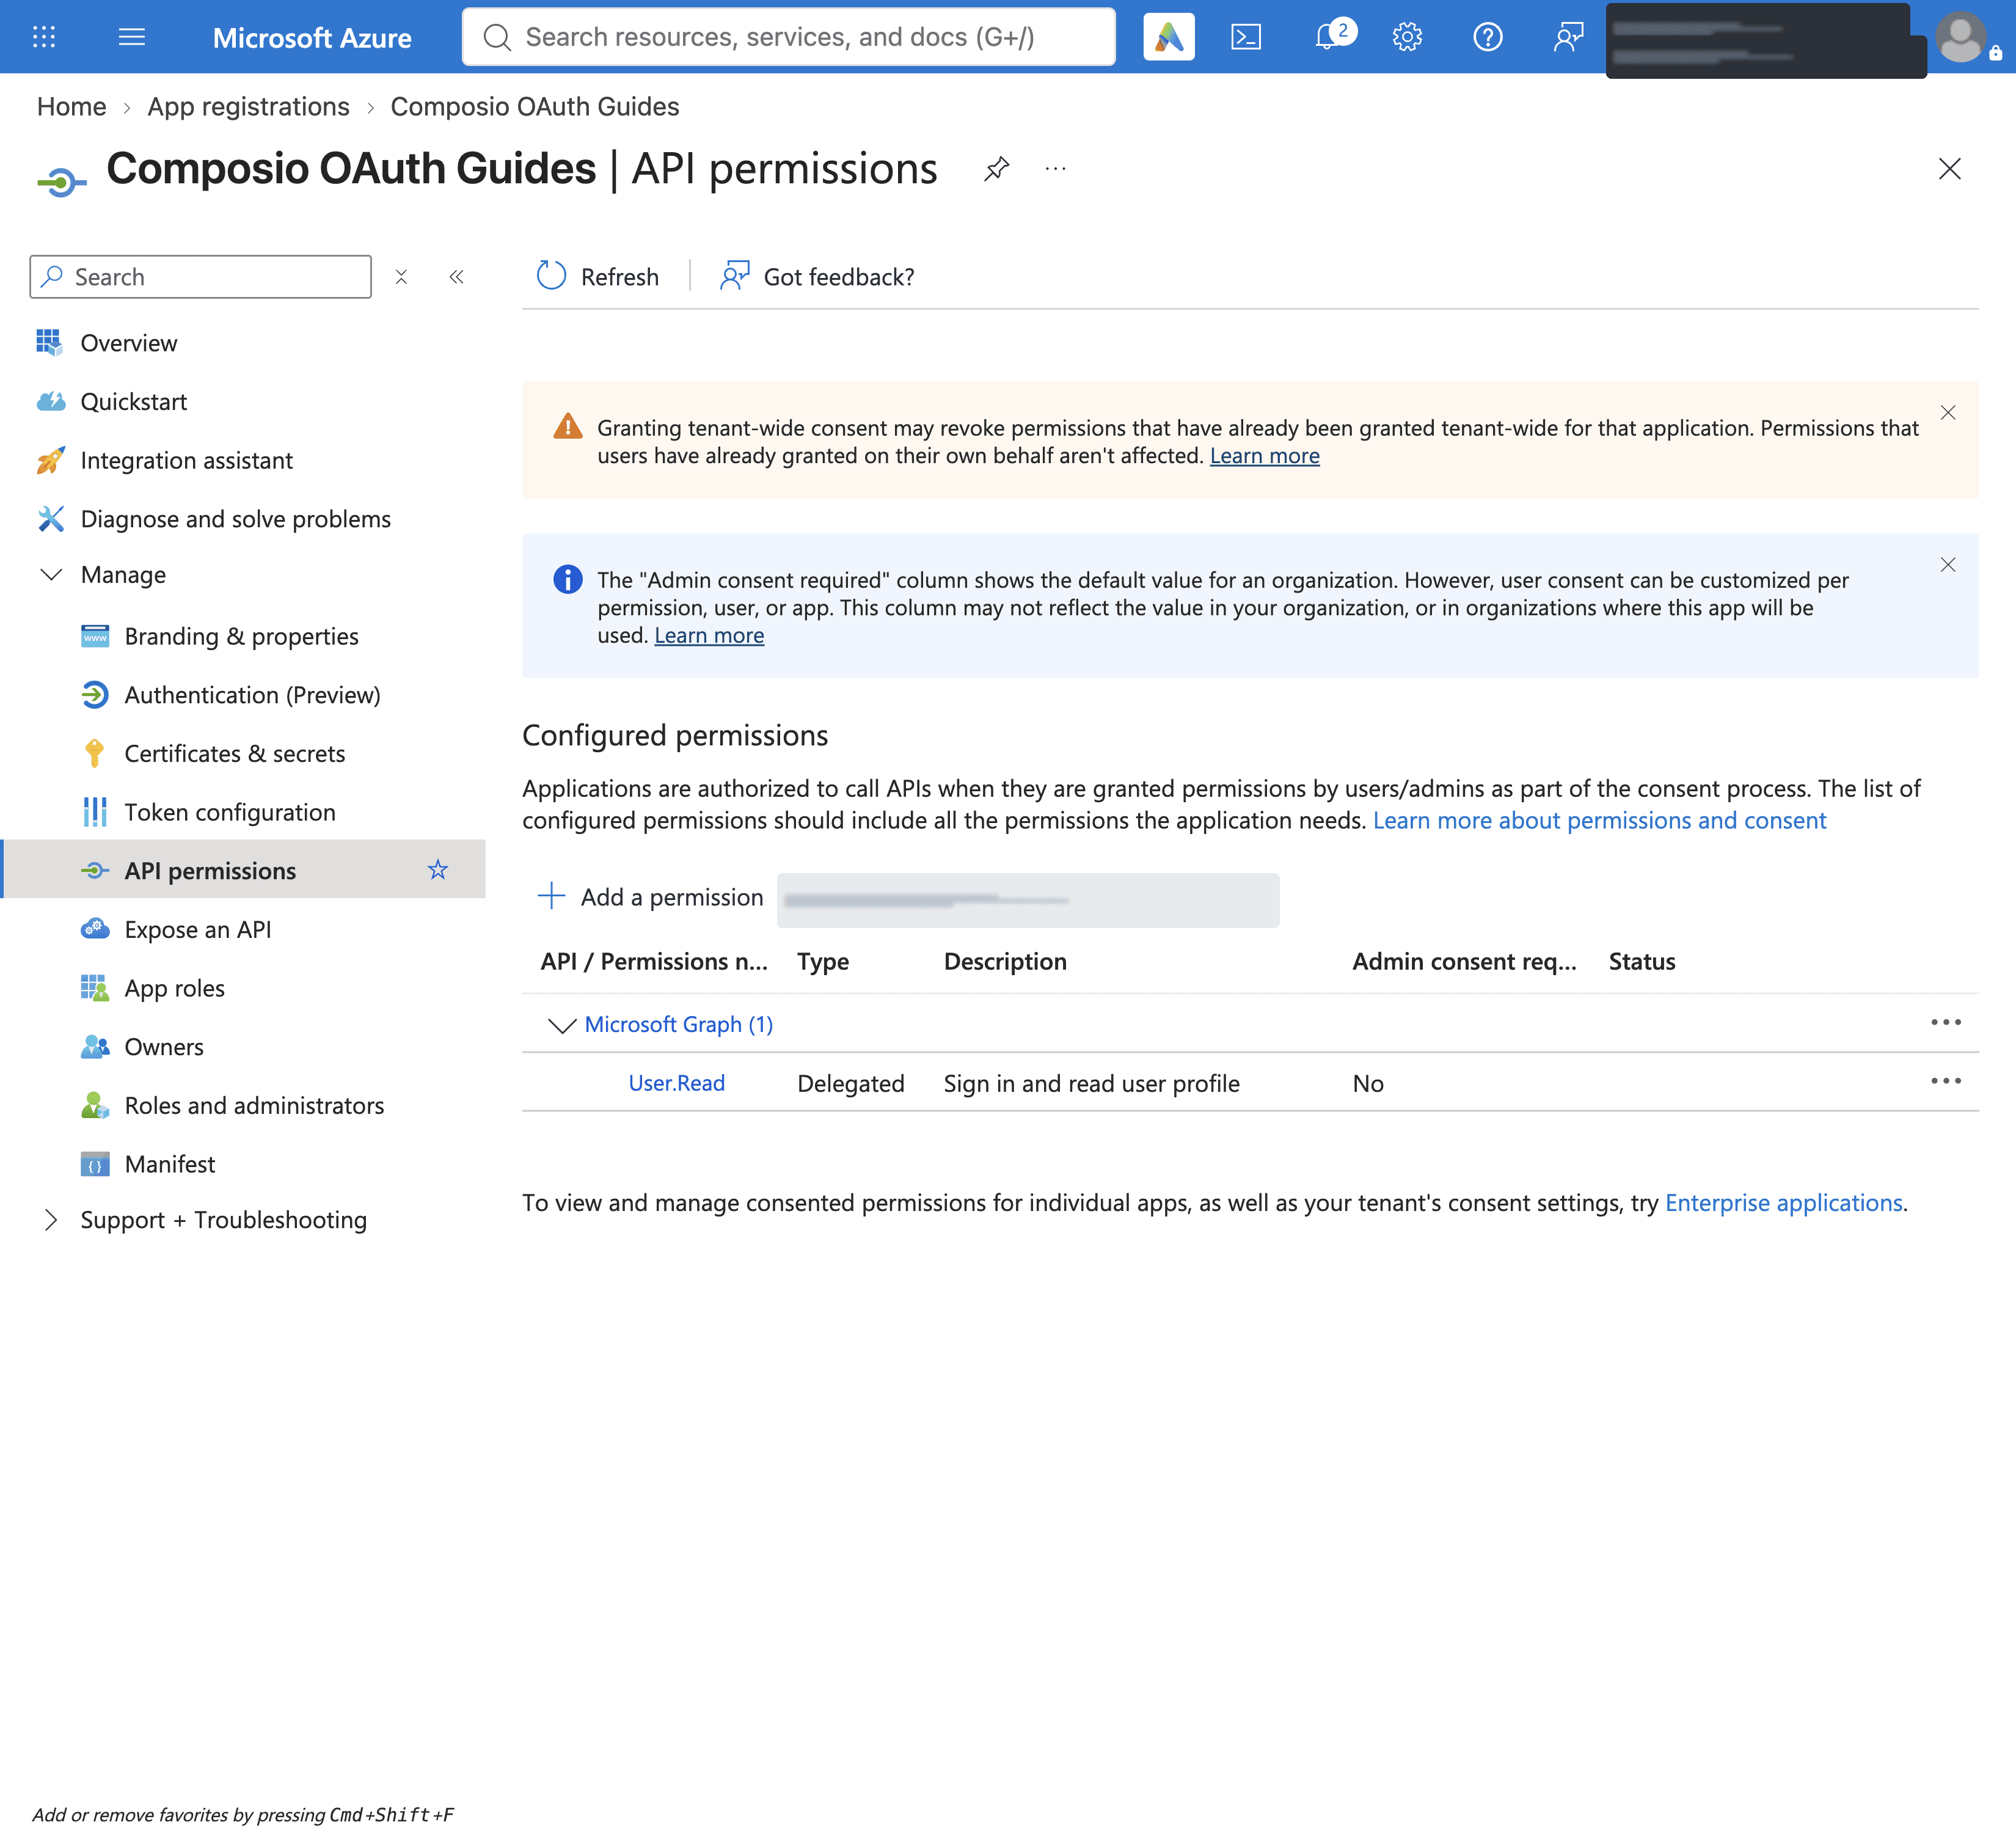
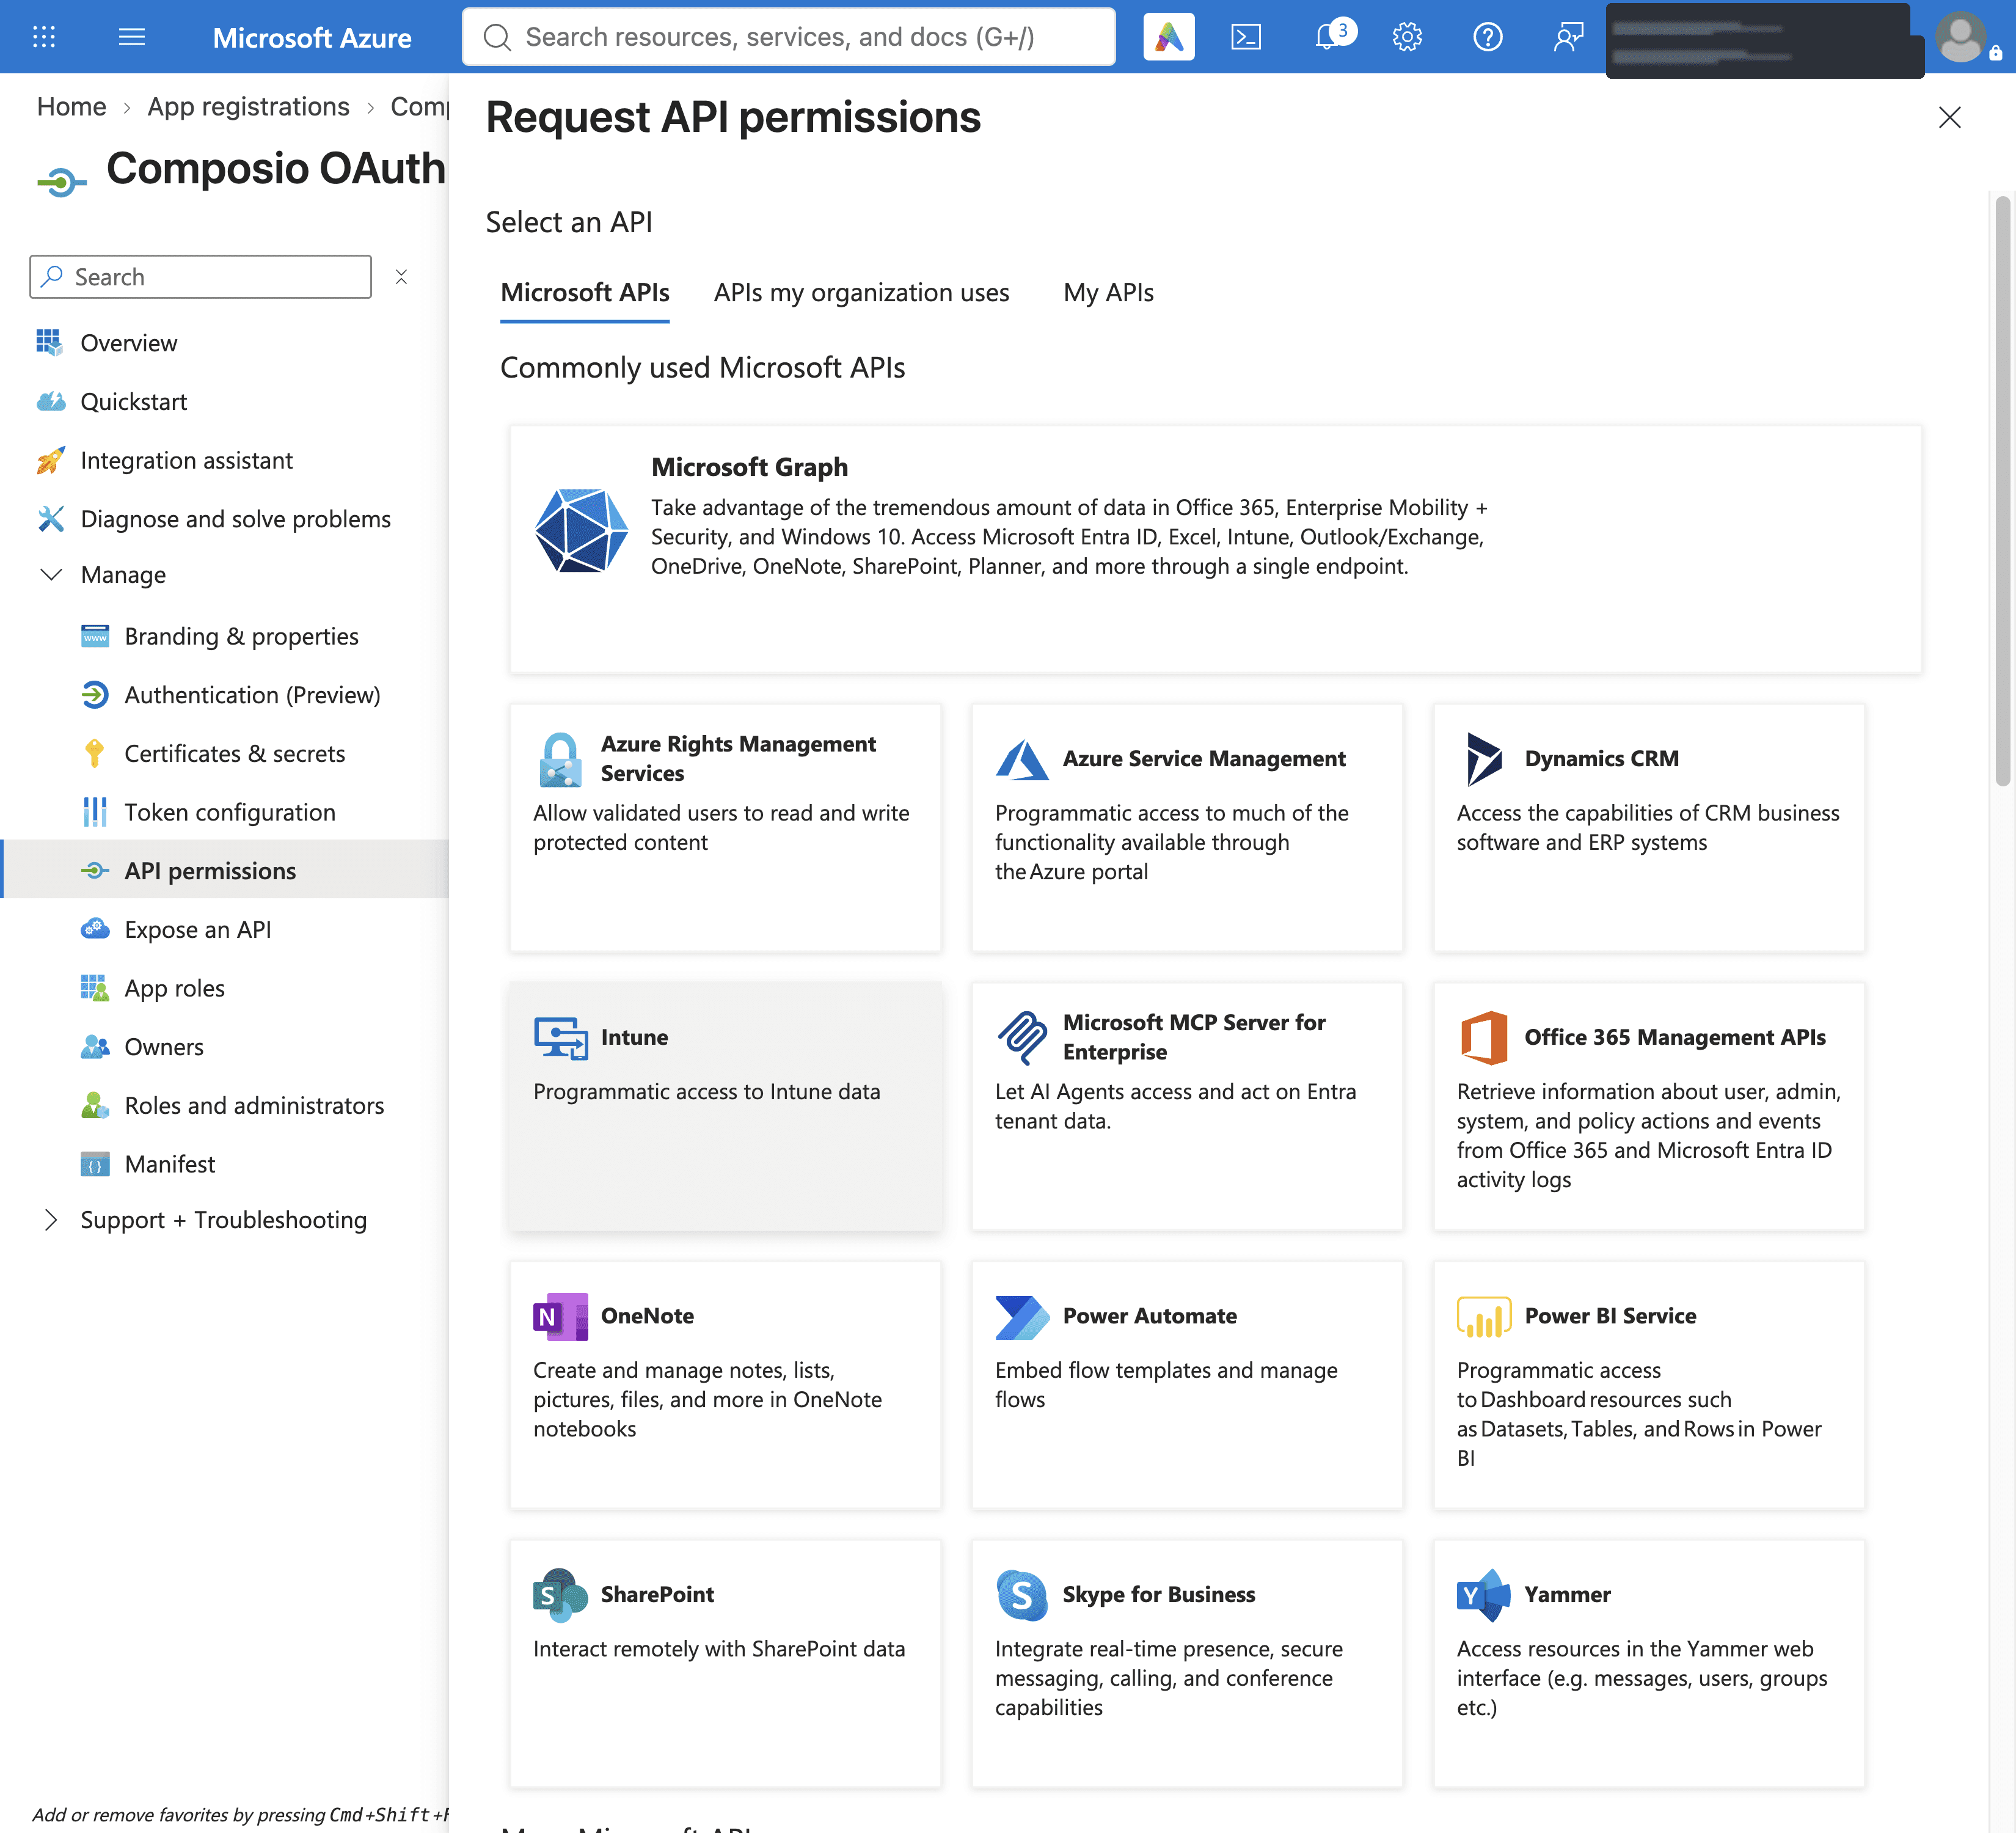
2. Select Microsoft Graph.
3. Choose Delegated permissions, so the app acts on behalf of the signed-in user.
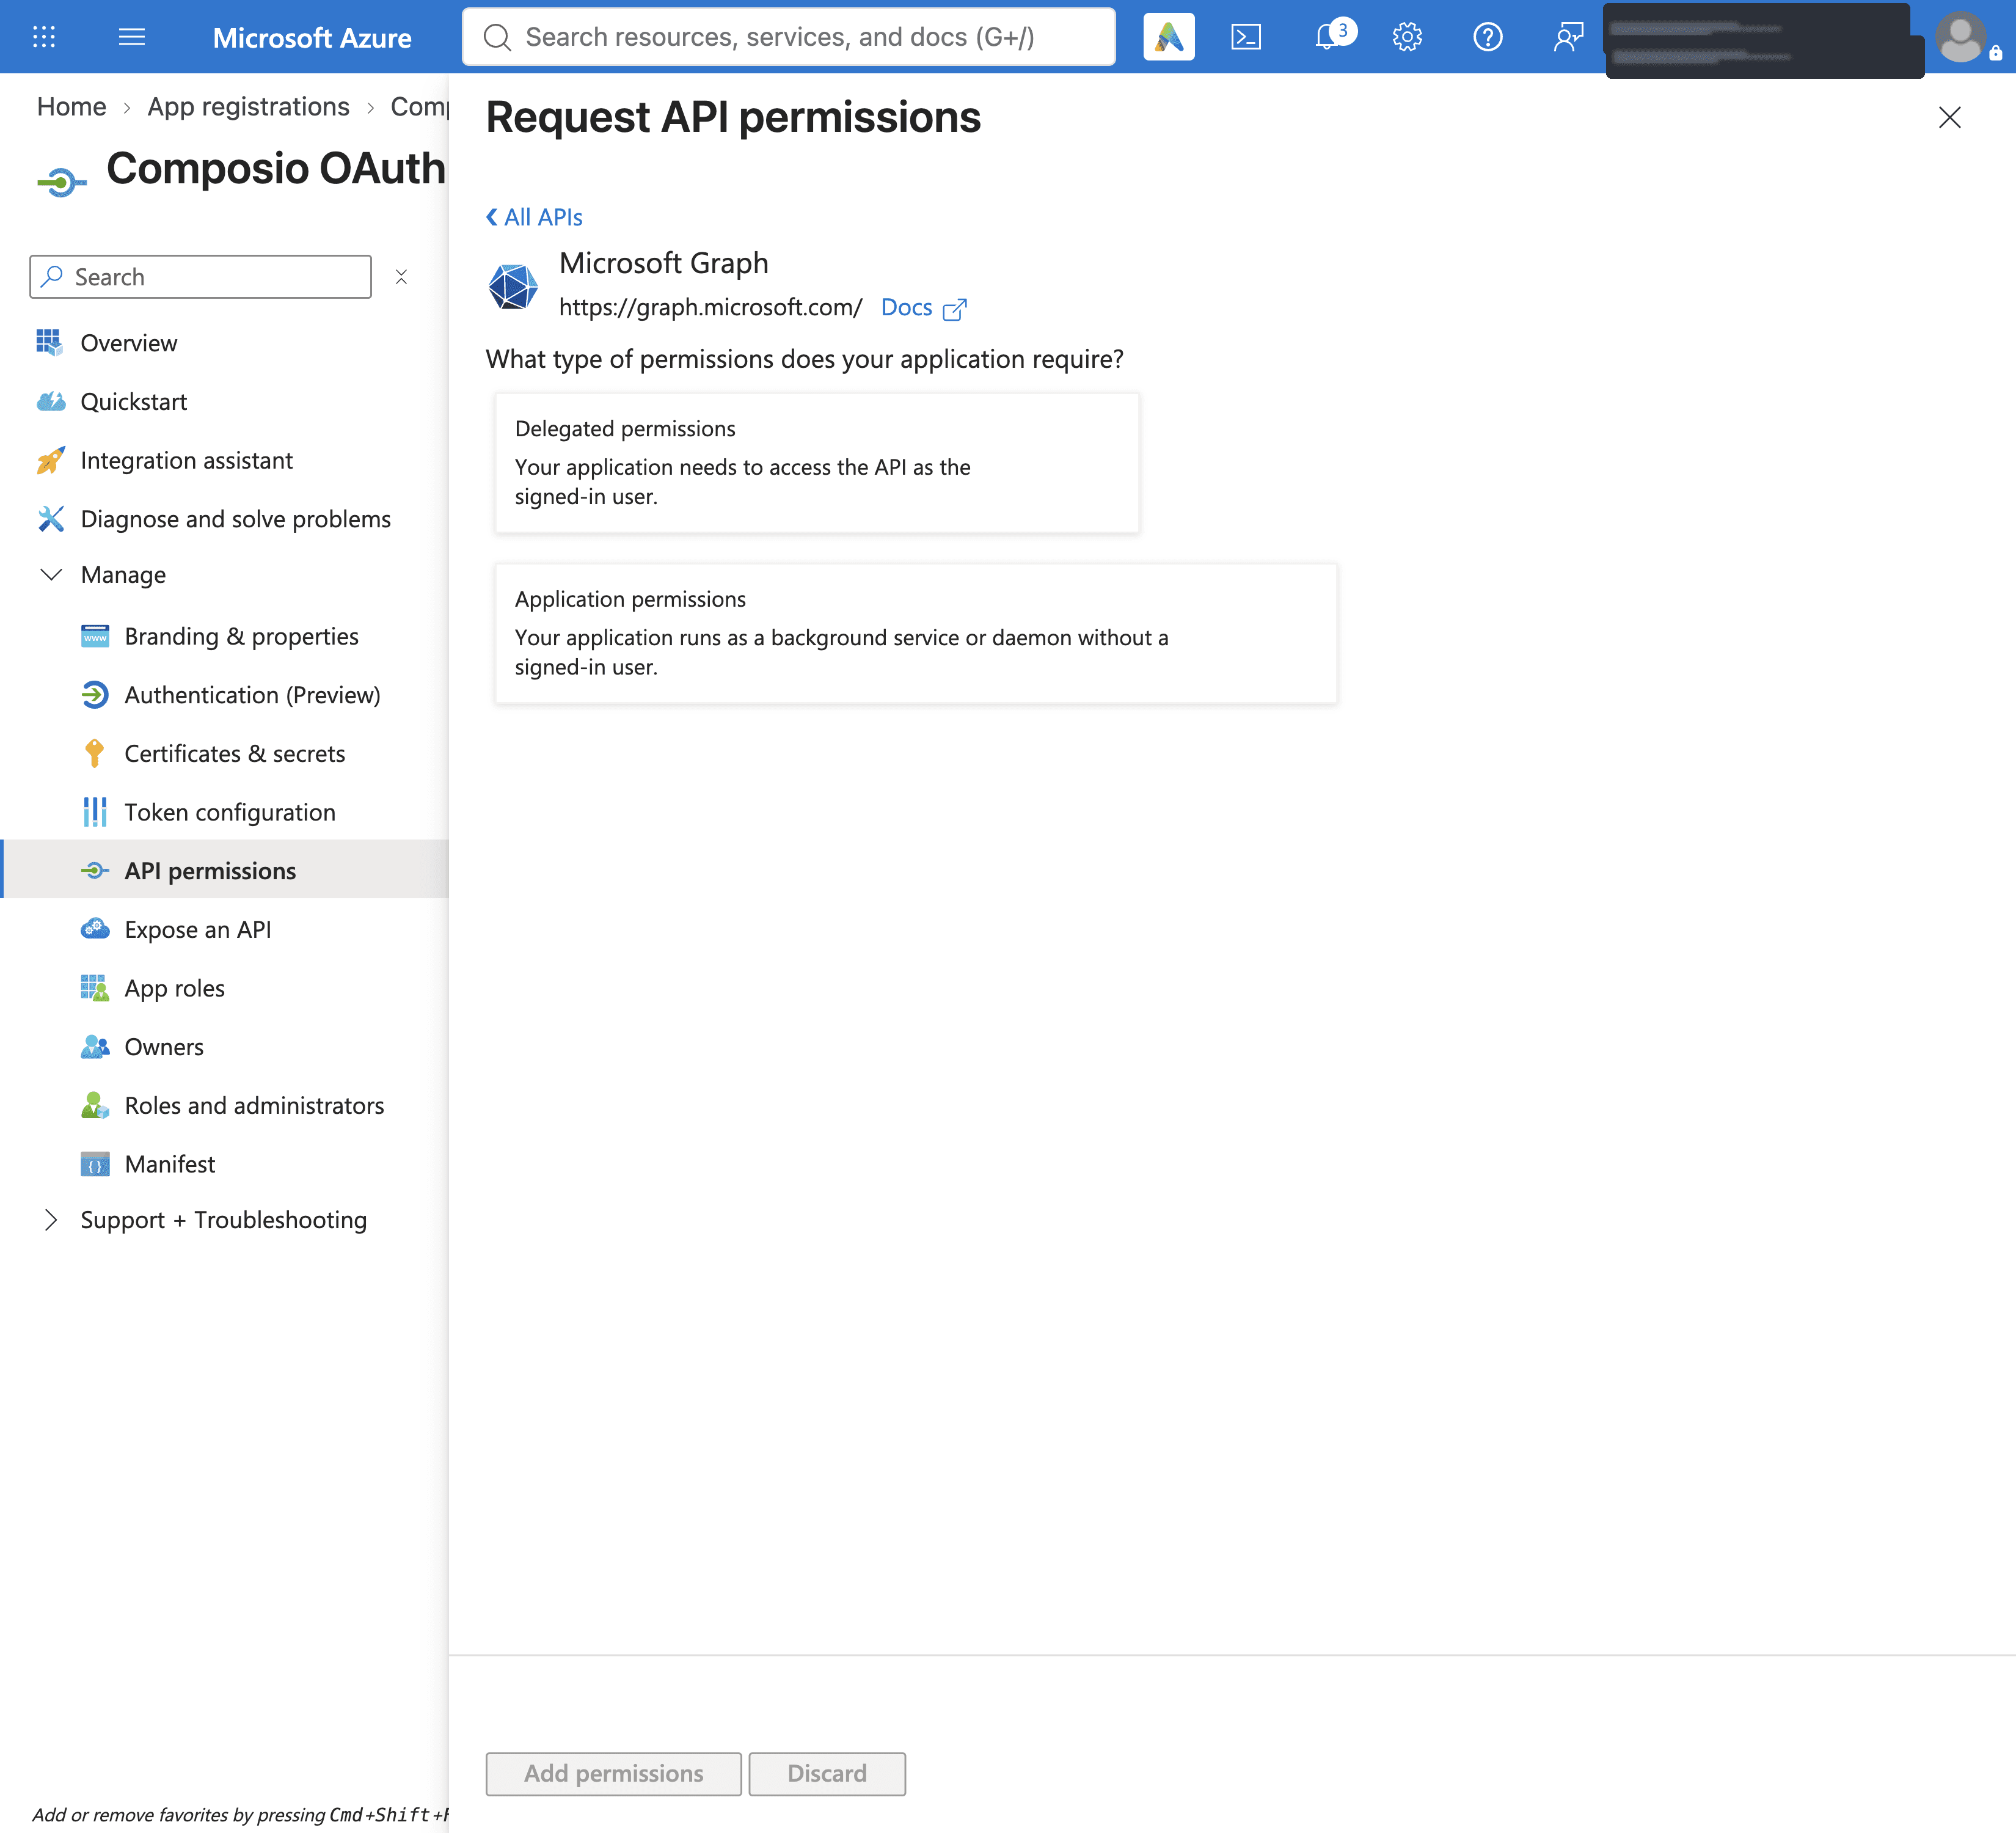
4. Choose the delegated permissions needed for the operations your integration will use. Then click Add permissions.
Step 4: Create the Auth Config with Your Own Credentials
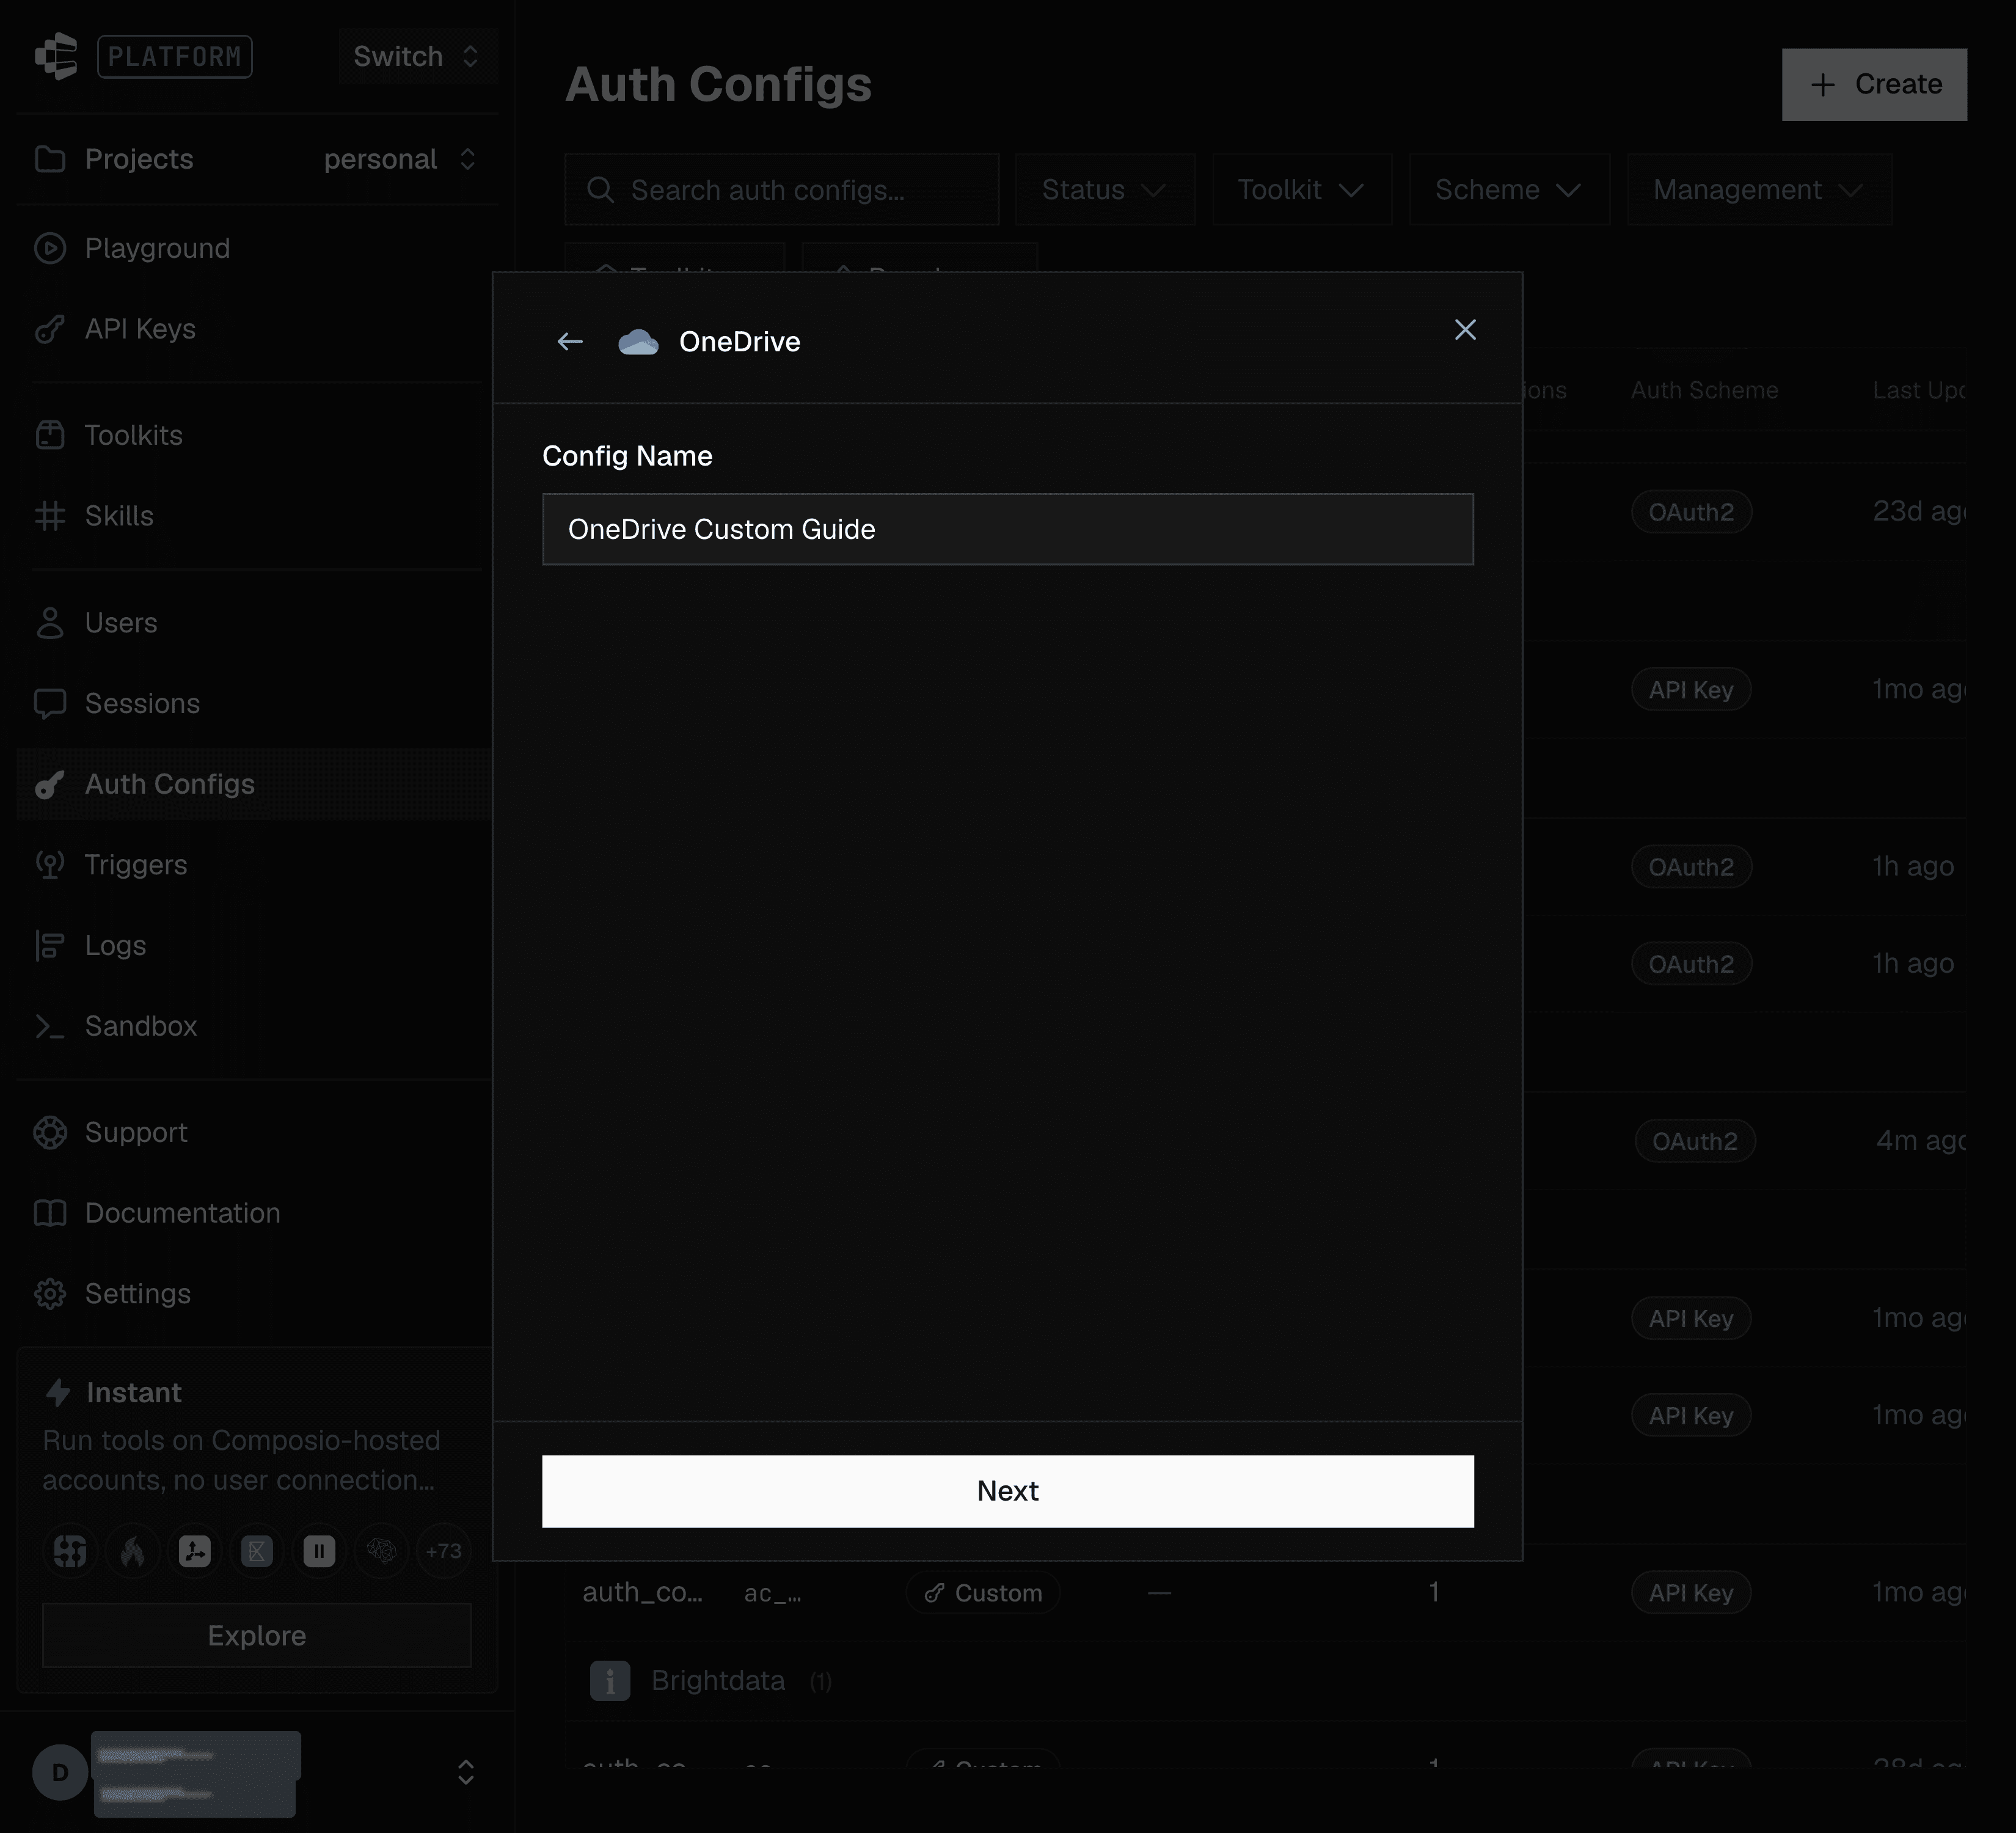
1. In the Composio Dashboard, go to Auth Configs, click Create, and select OneDrive. Enter a Config Name (the screenshots use OneDrive Custom Guide) and click Next.
2. Under Authentication Method, select OAuth 2.0. Under Credentials, select Your Own Credentials.

3. Paste the Client id and the secret Value from your Entra app into Client secret. The inputs are left empty in the screenshot to keep the credentials private. Leave the Redirect URI exactly as shown; it must match the redirect URI you registered in Step 1. For Microsoft cloud environment, keep global for the commercial Microsoft 365 cloud.
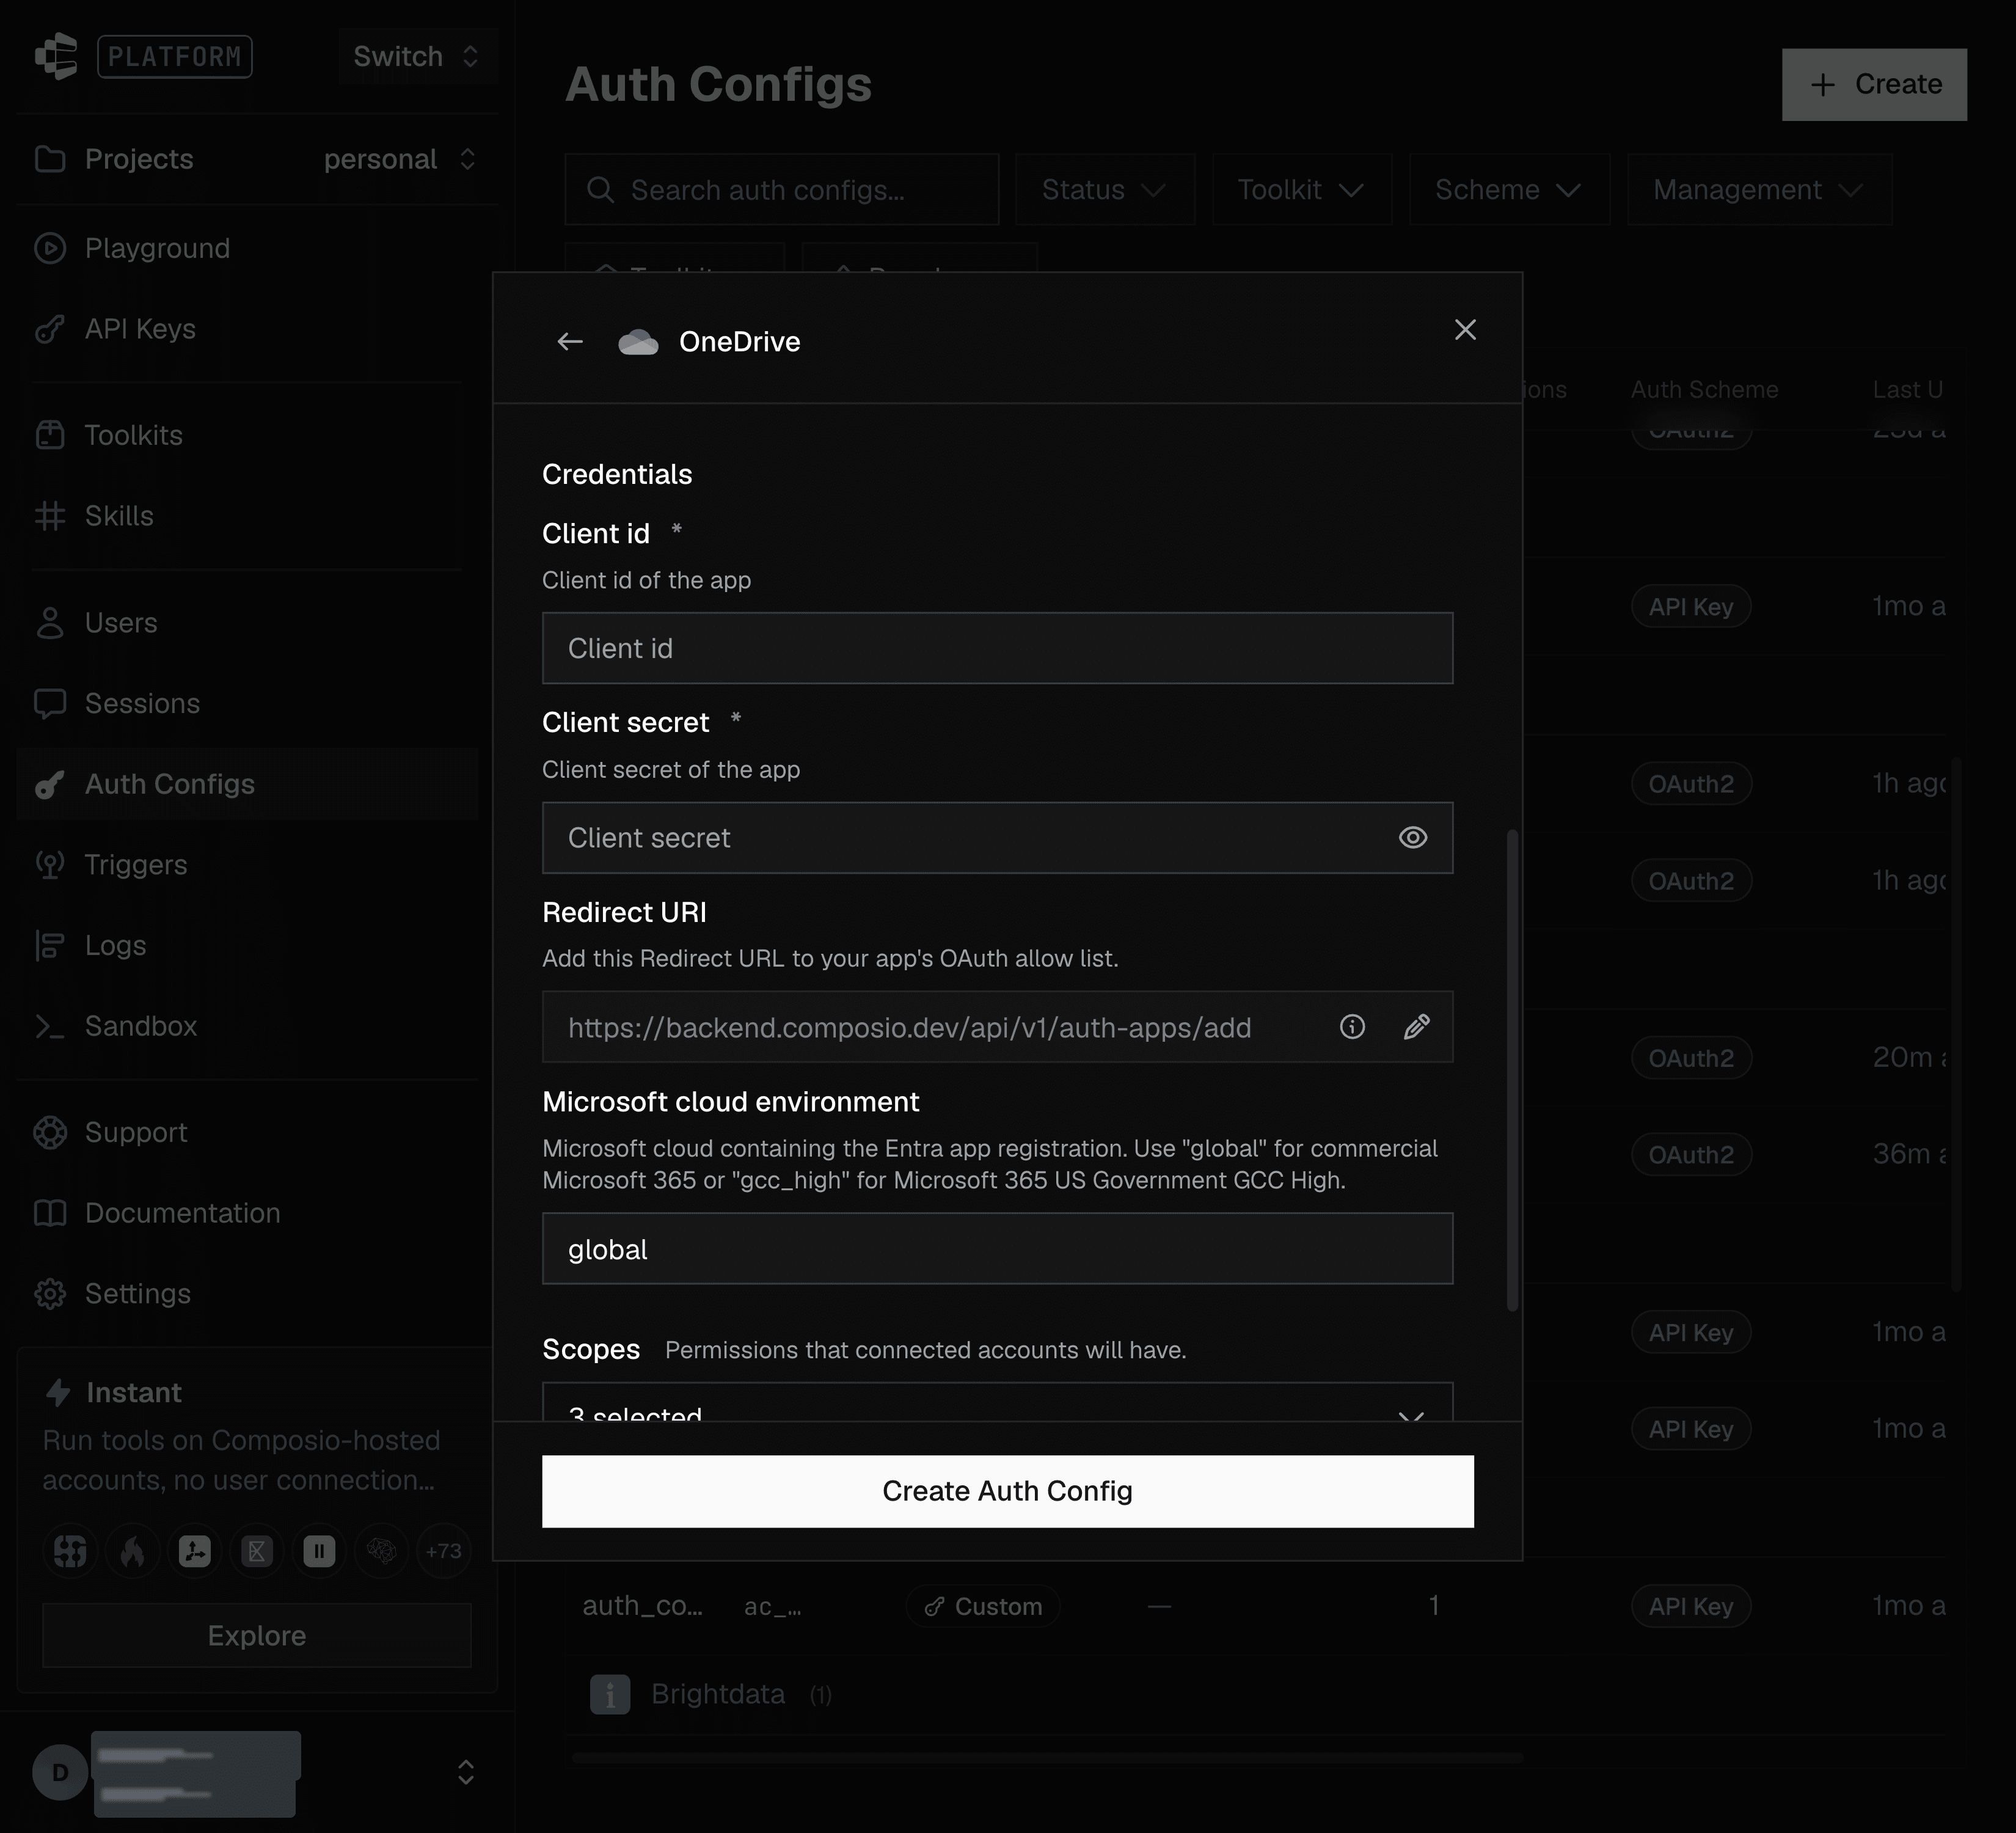
4. Under Scopes, choose permissions required by your integration and supported by your app registration. Click Create Auth Config.
Permission reference. Basic file reads require Files.Read; file edits require Files.ReadWrite. Broader shared-file or SharePoint operations can require additional permissions. offline_access supports continued access. Choose for your own workflow; the screenshots are examples, not a required scope set. Microsoft permission reference.


Step 5: Connect Your Microsoft Account
1. Open the auth config and click Connect Account. Then open the generated link.
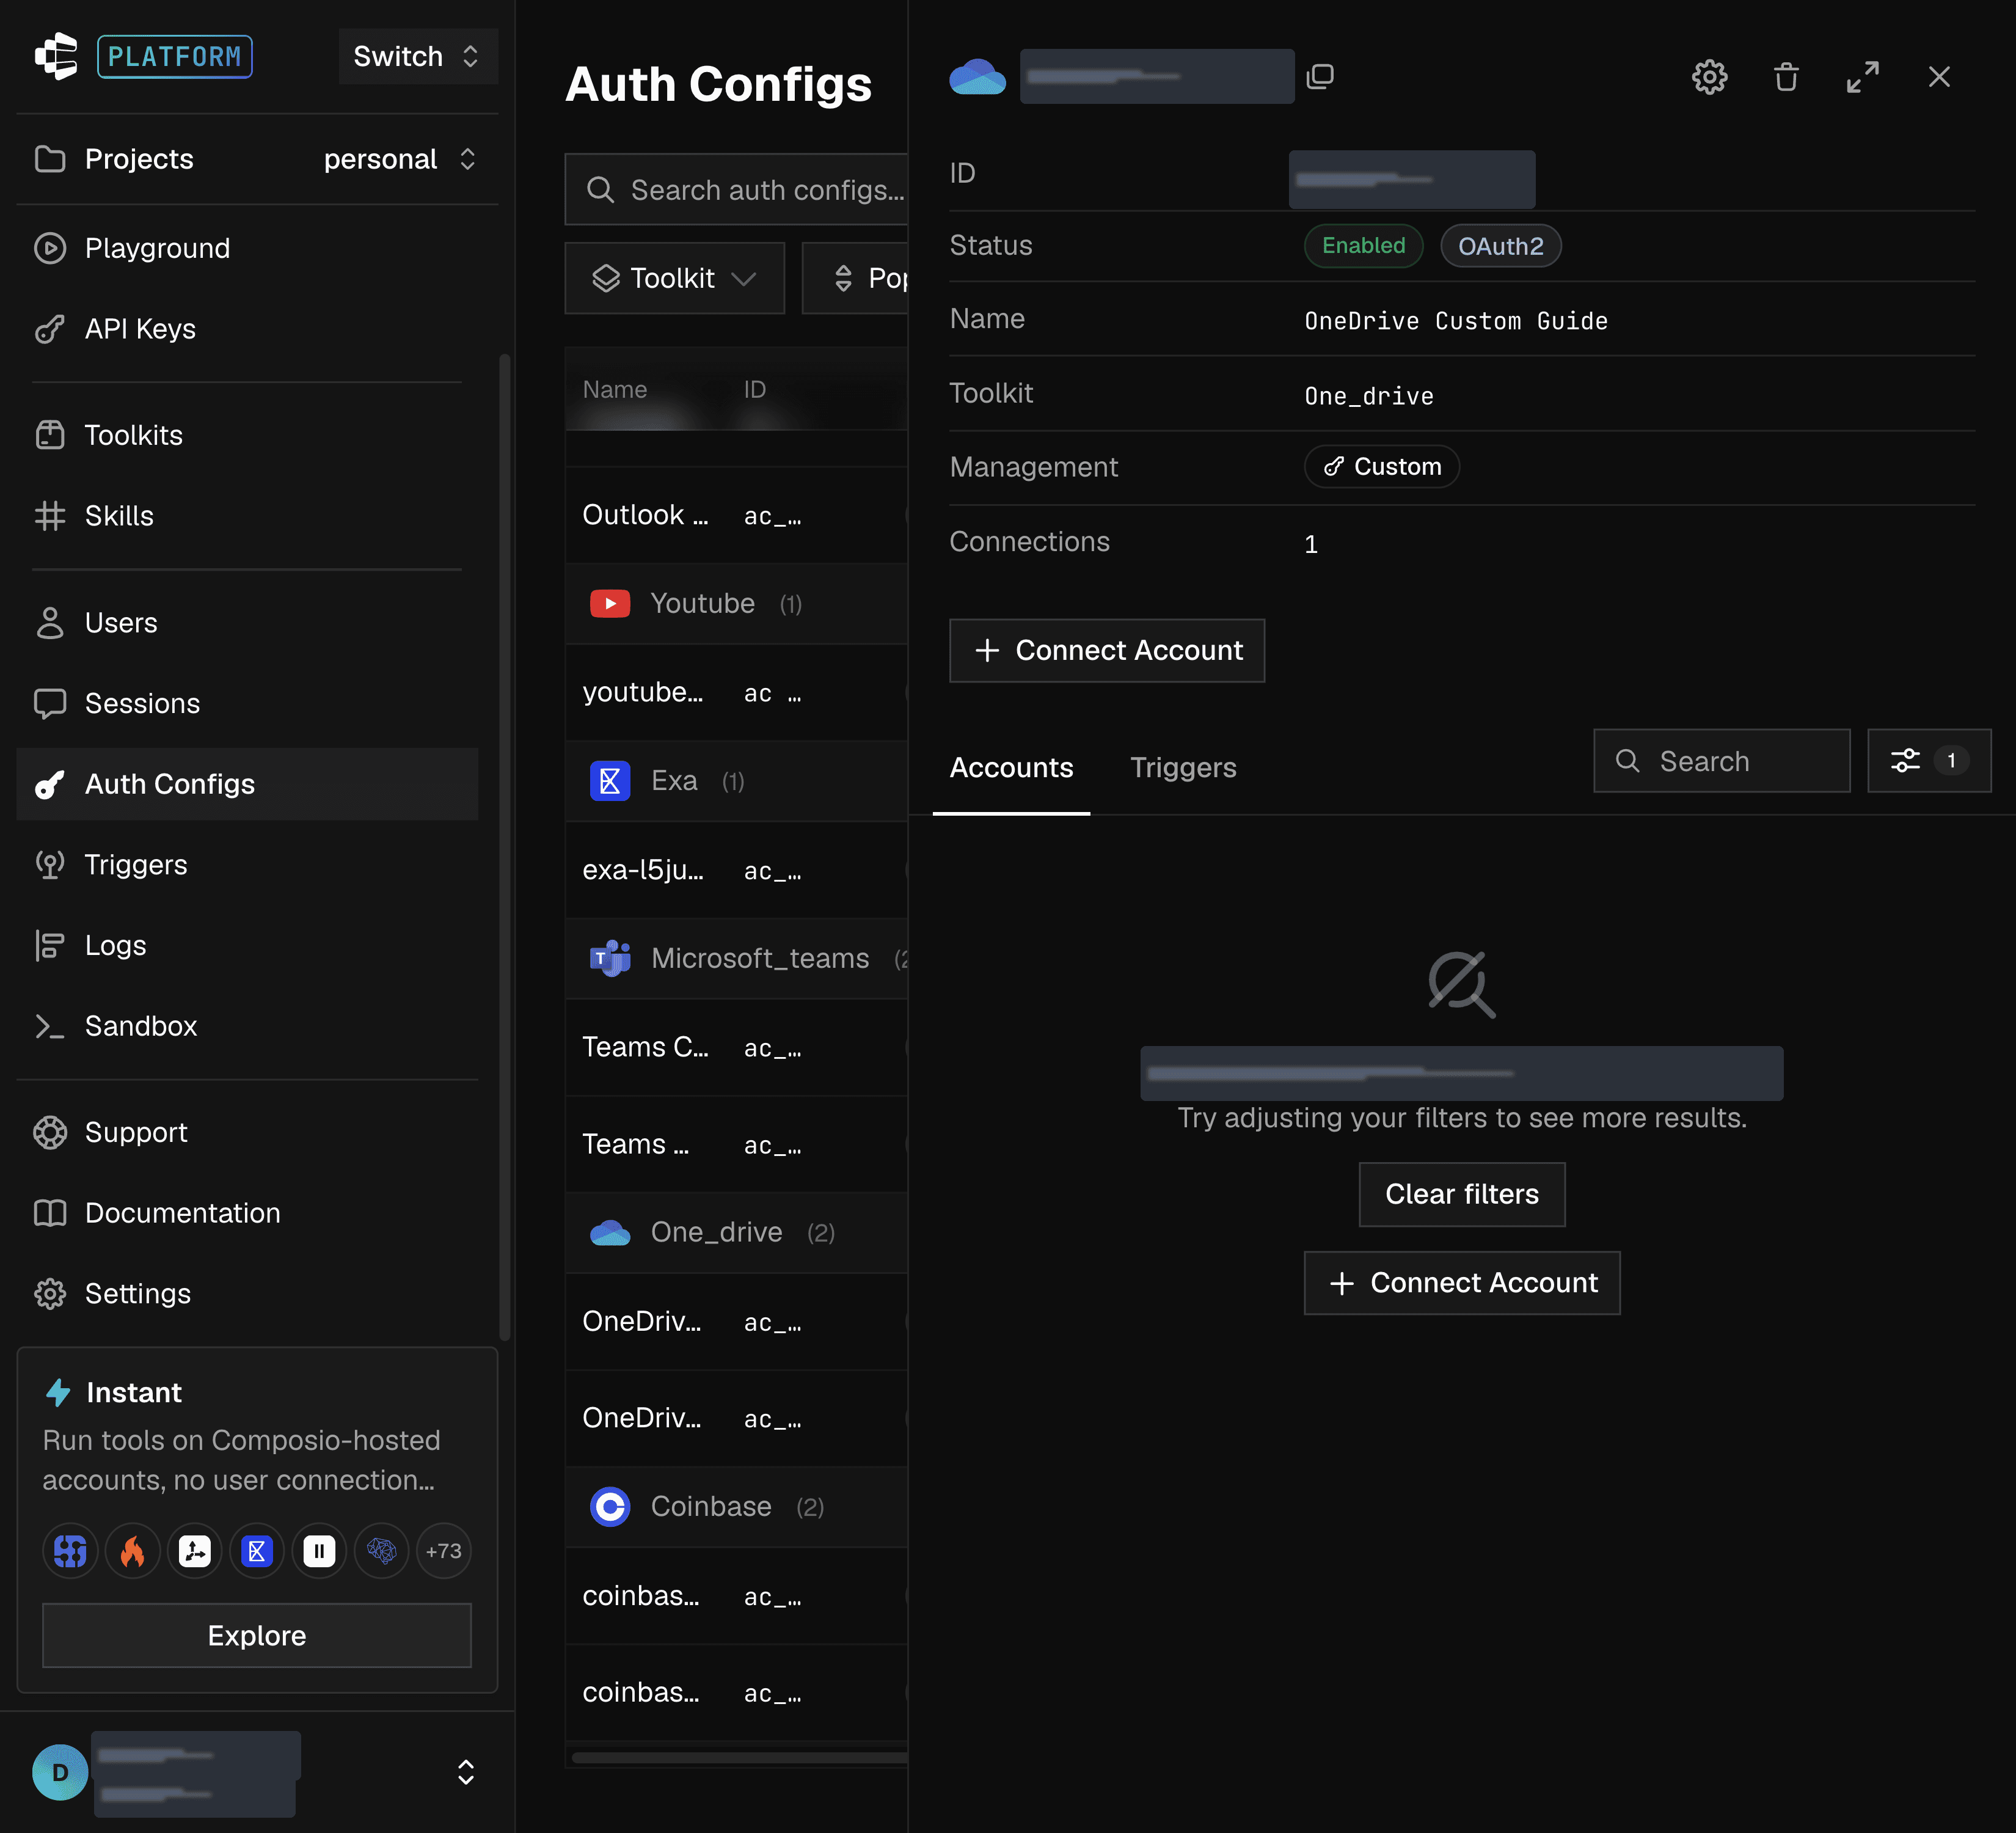
2. Select the Microsoft account you want to connect and sign in.
3. Verify your app name, review the permissions and click Accept if appropriate. Leave organization-wide consent unchecked unless an administrator intends tenant-wide approval.
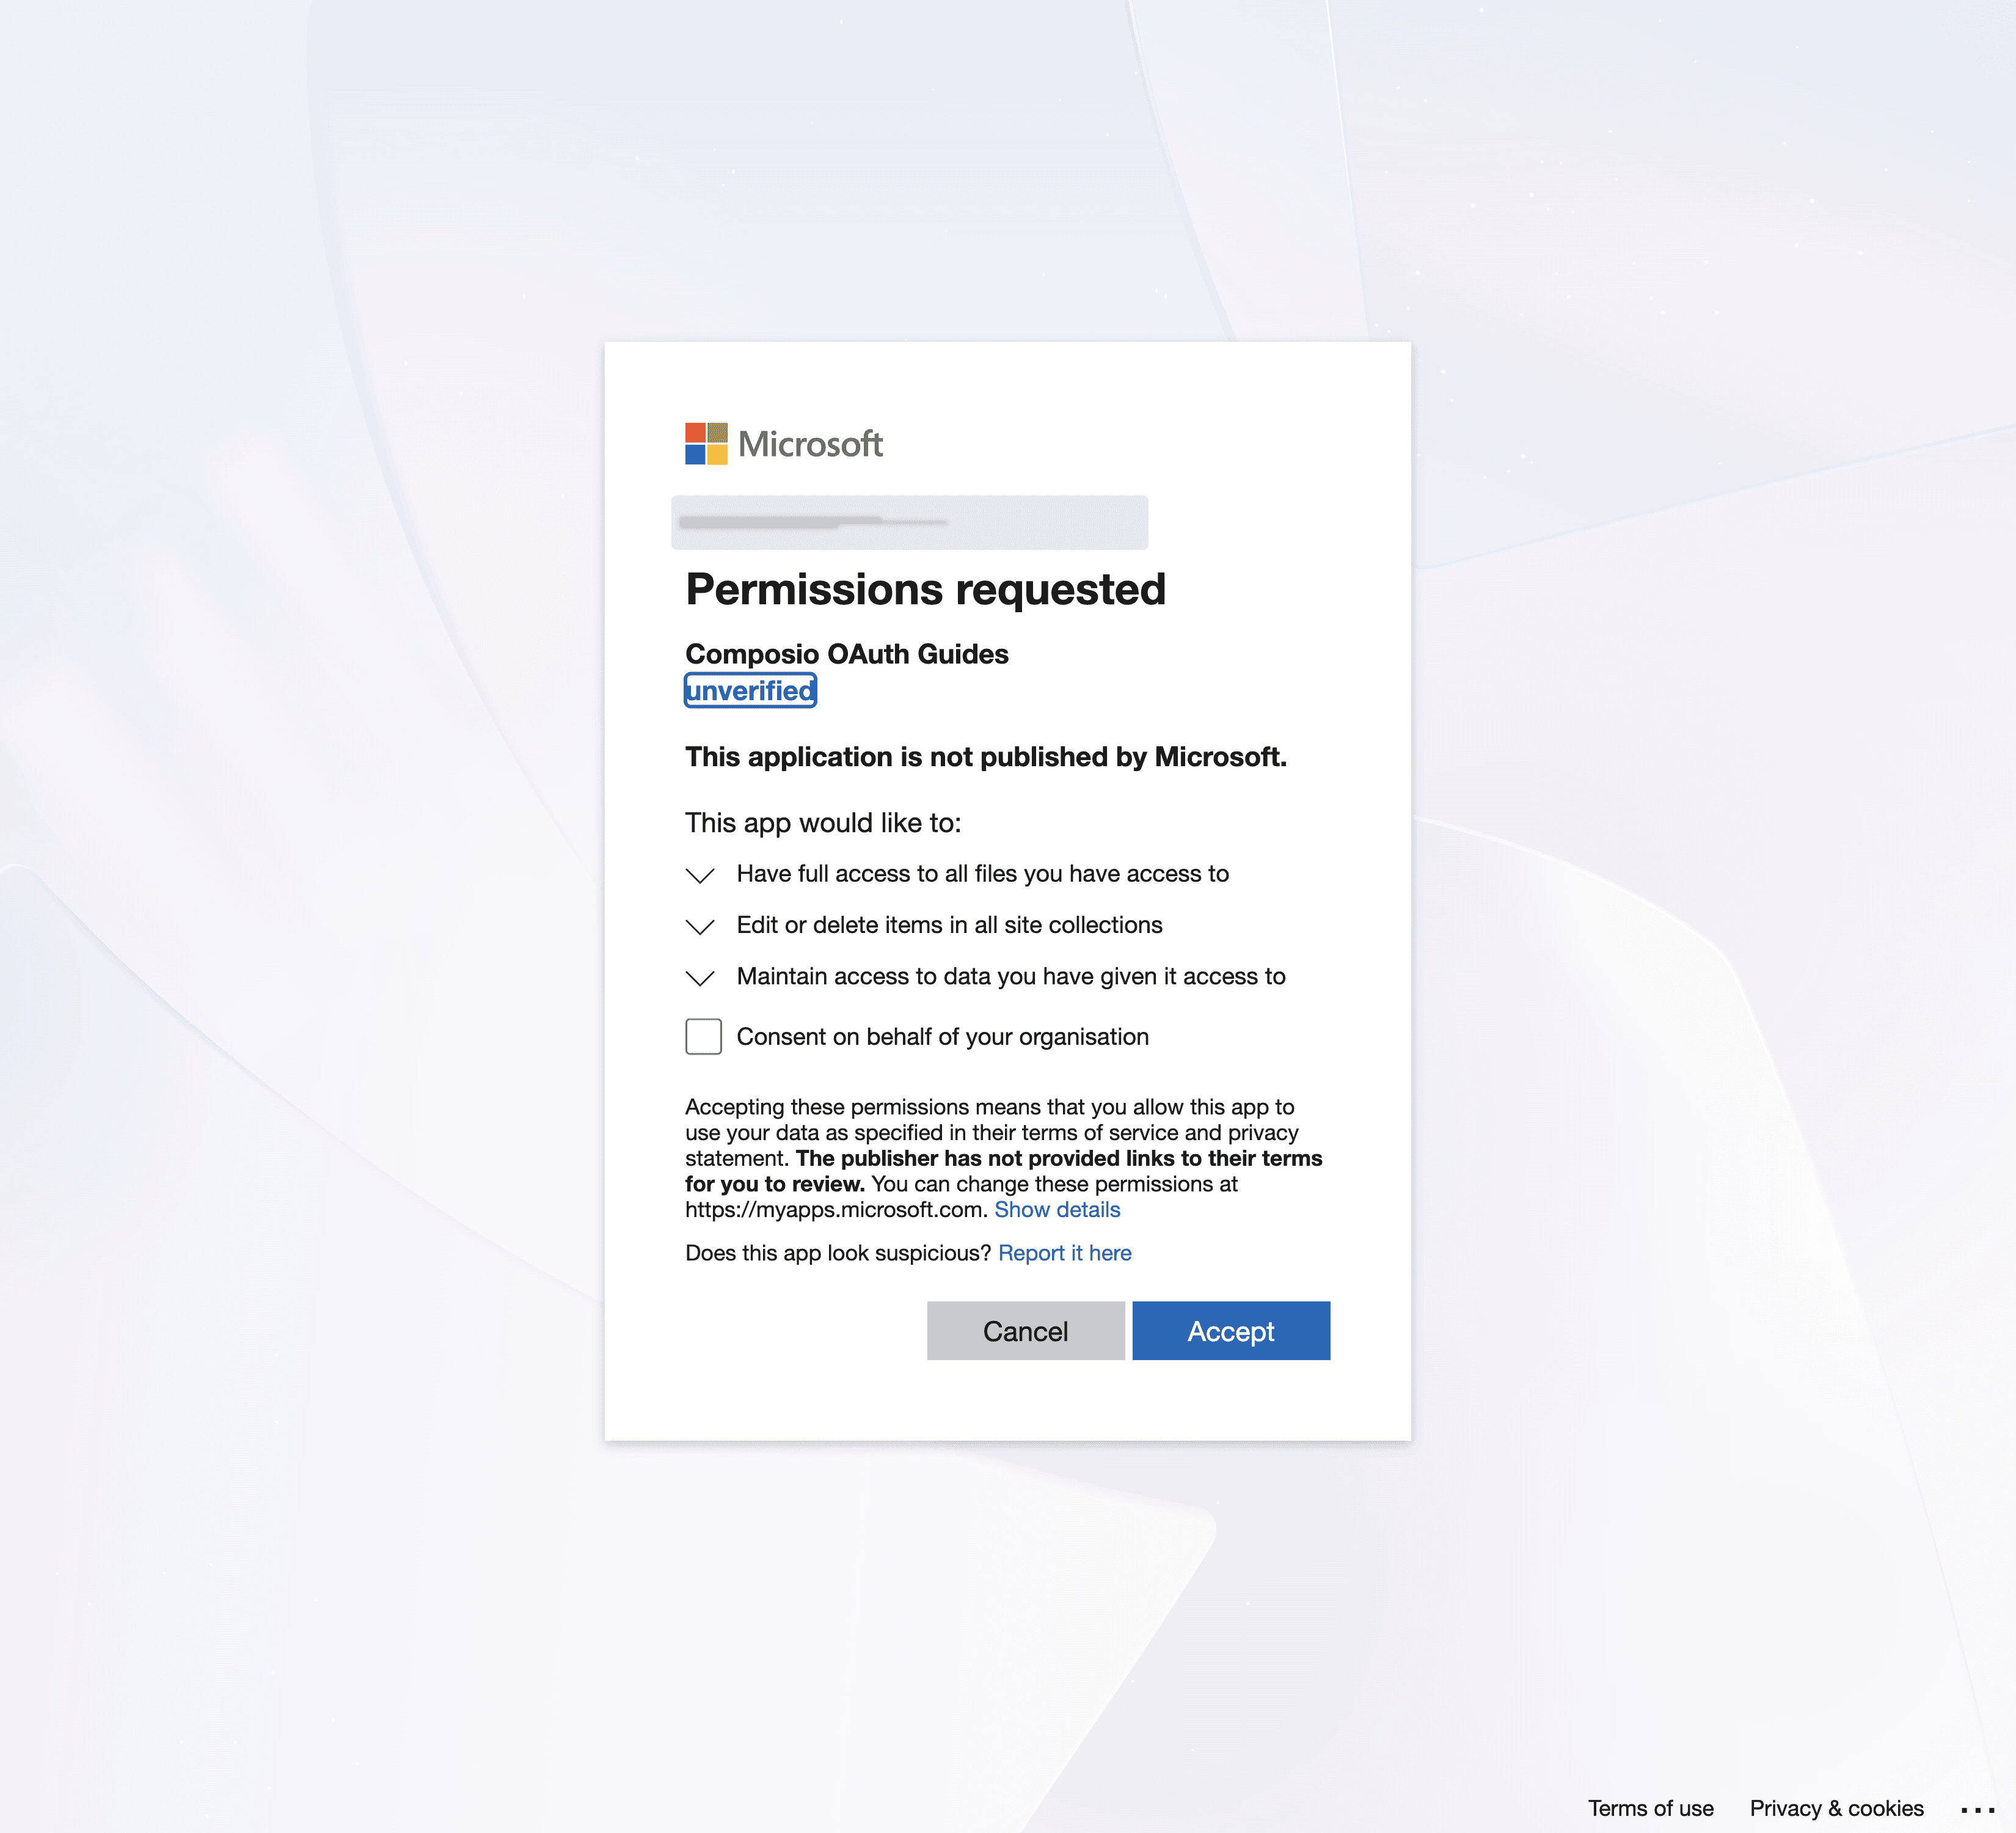
Step 6: Confirm the Connected Account Is Active
1. After approval, open Accounts and check Active on the connected account. Enabled describes the auth config.
Your OneDrive auth config is ready. Copy the Auth Config ID (ac_...) and use it in your application code or secret manager.
