

Composio connects AI agents to Microsoft To Do so they can read and manage task lists and tasks. Access is limited by the permissions you approve and your account’s existing access.
This guide shows you how to set up OAuth credentials and connect Microsoft To Do to Composio.
Part 1: Create your Microsoft Entra OAuth app
Step 1: Register the app
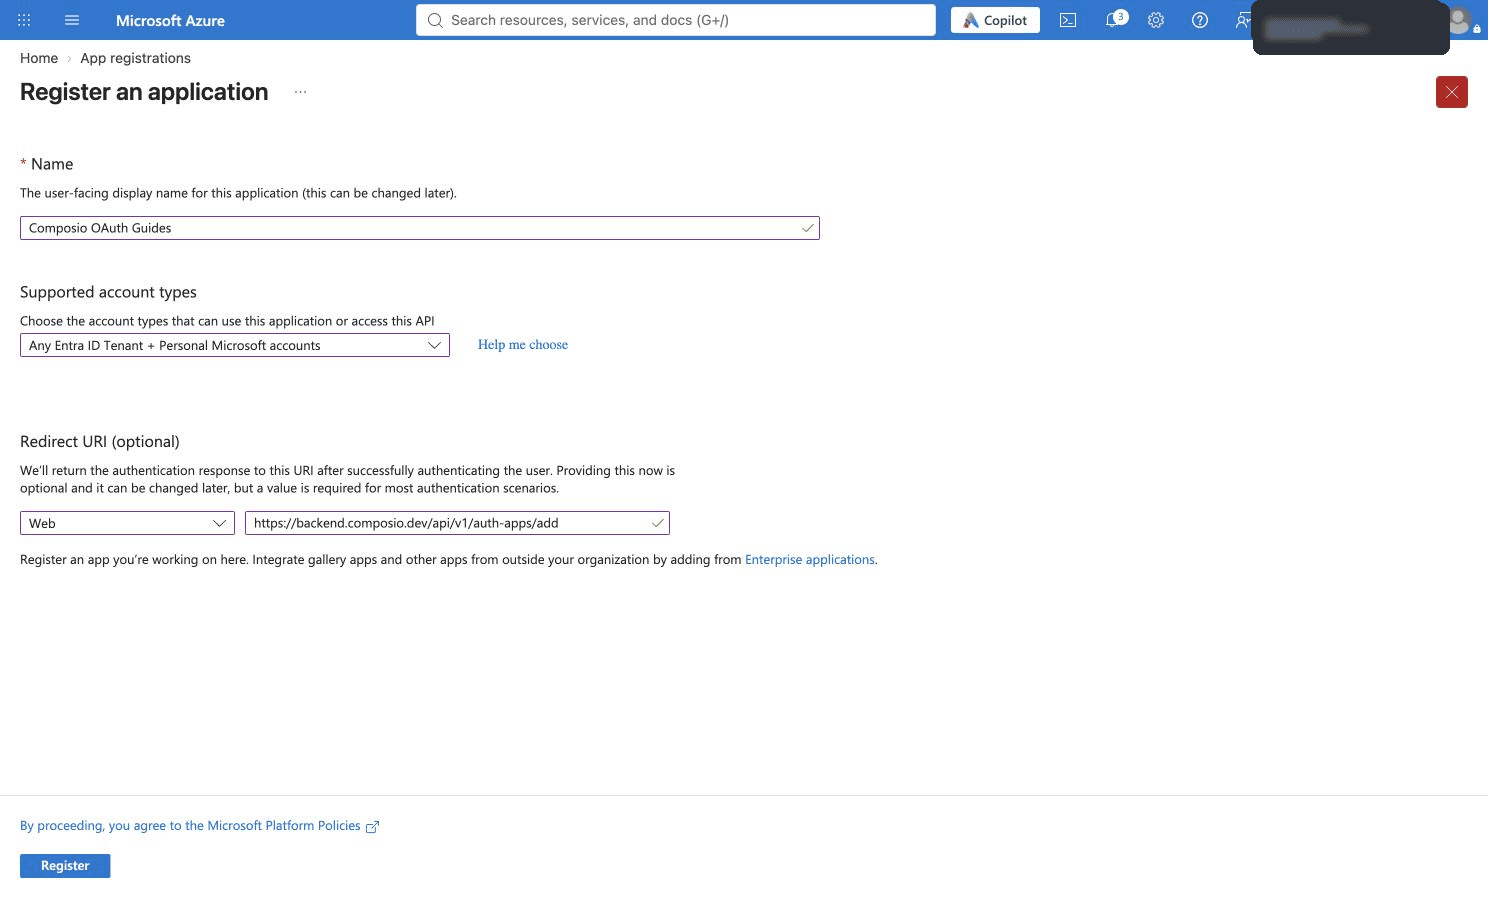
1. Open Azure portal → App registrations → New registration. Name your app and choose the organizational accounts you want to support.
2. Select Web, enter this redirect URI and click Register.
https://backend.composio.dev/api/v1/auth-apps/add
Step 2: Copy your client ID and create a secret
1. Copy the Application (client) ID from Overview.

2. Open Certificates & secrets → New client secret.
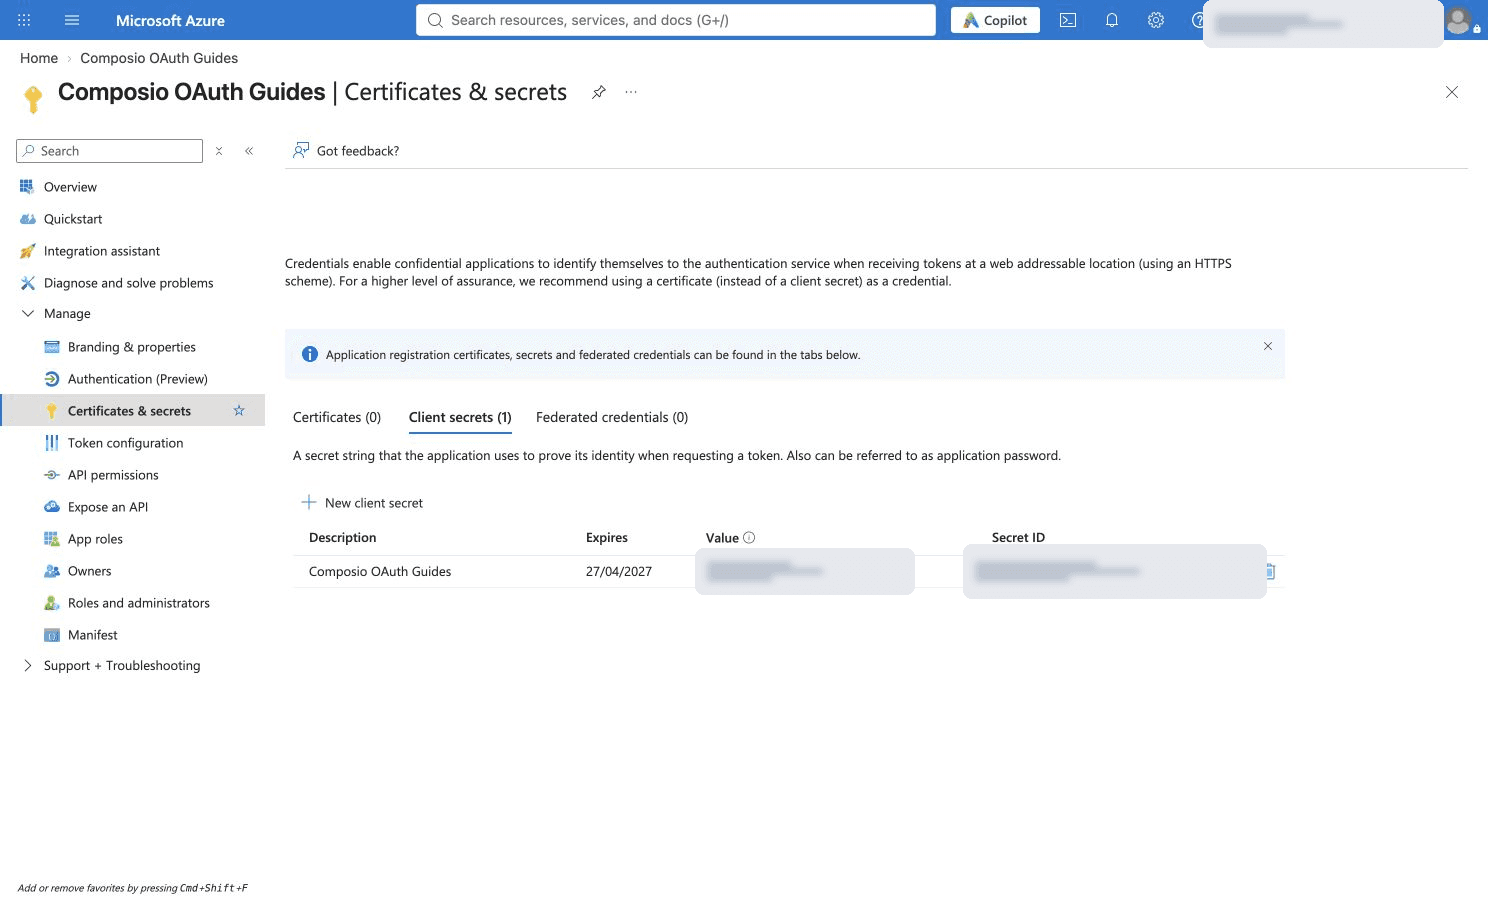
3. Enter a description, choose an expiry and click Add.
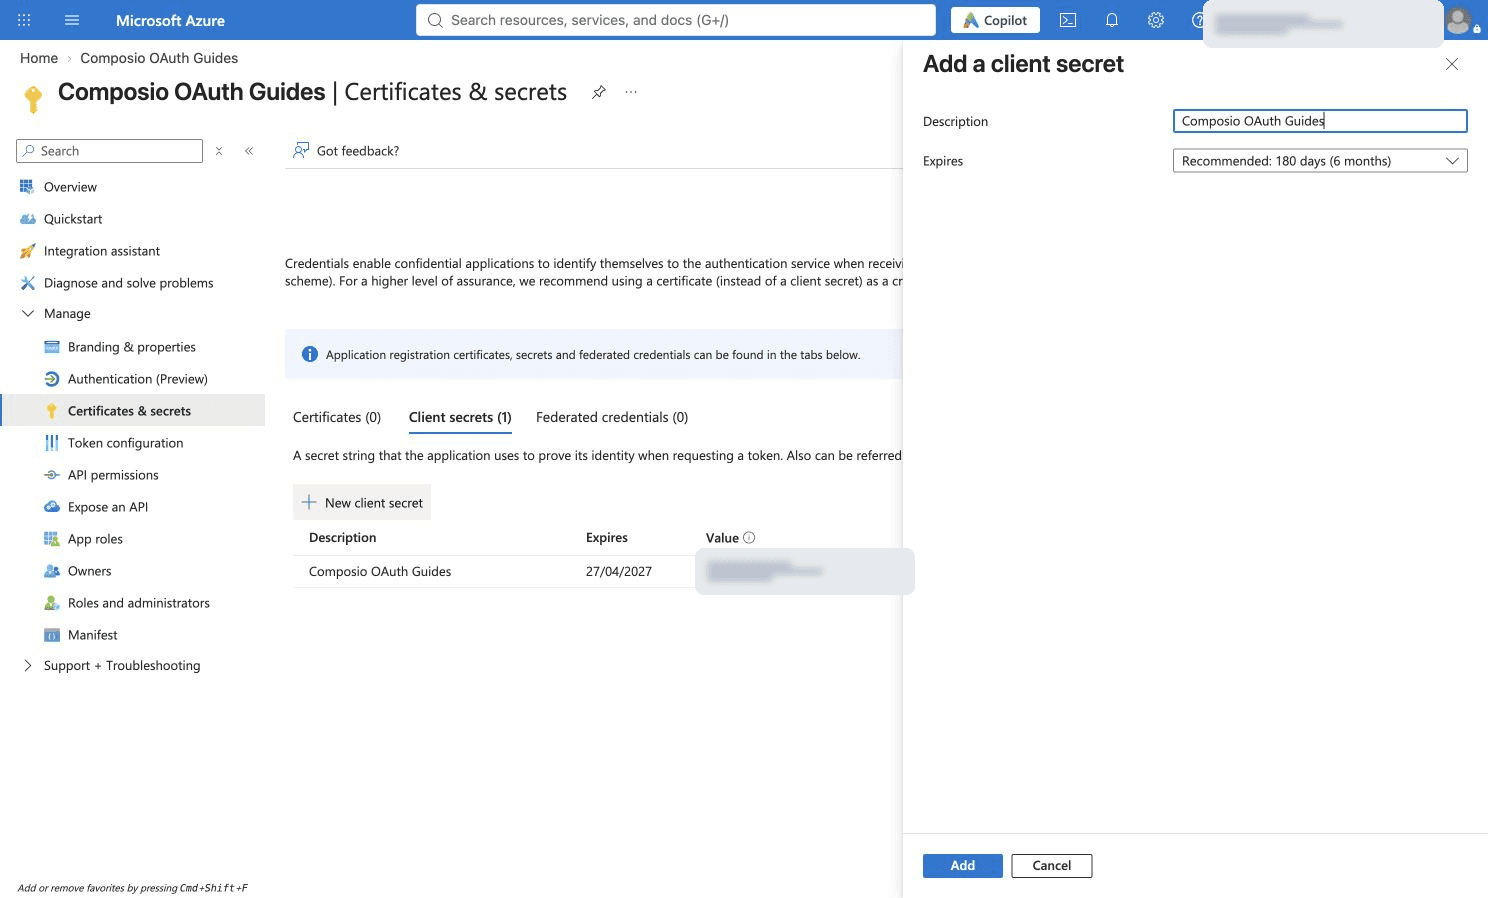
4. Copy and securely store the secret Value. Use the Value, not the Secret ID. Rotate it before expiry.

Step 3: Add Microsoft Graph delegated permissions
1. Open API permissions → Add a permission.

2. Select Microsoft Graph.
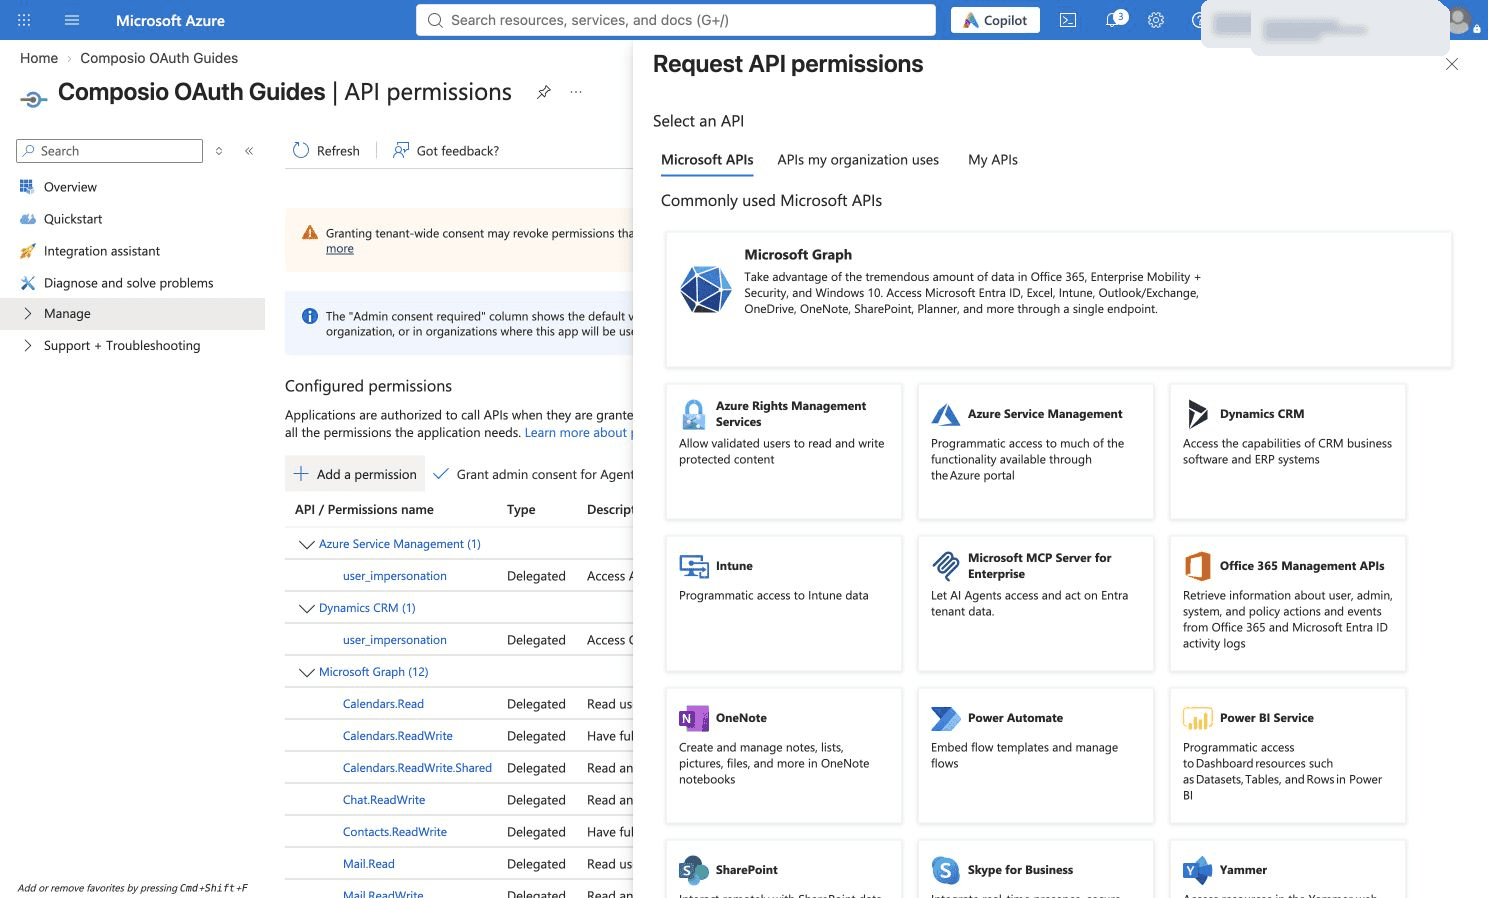
3. Select Delegated permissions.
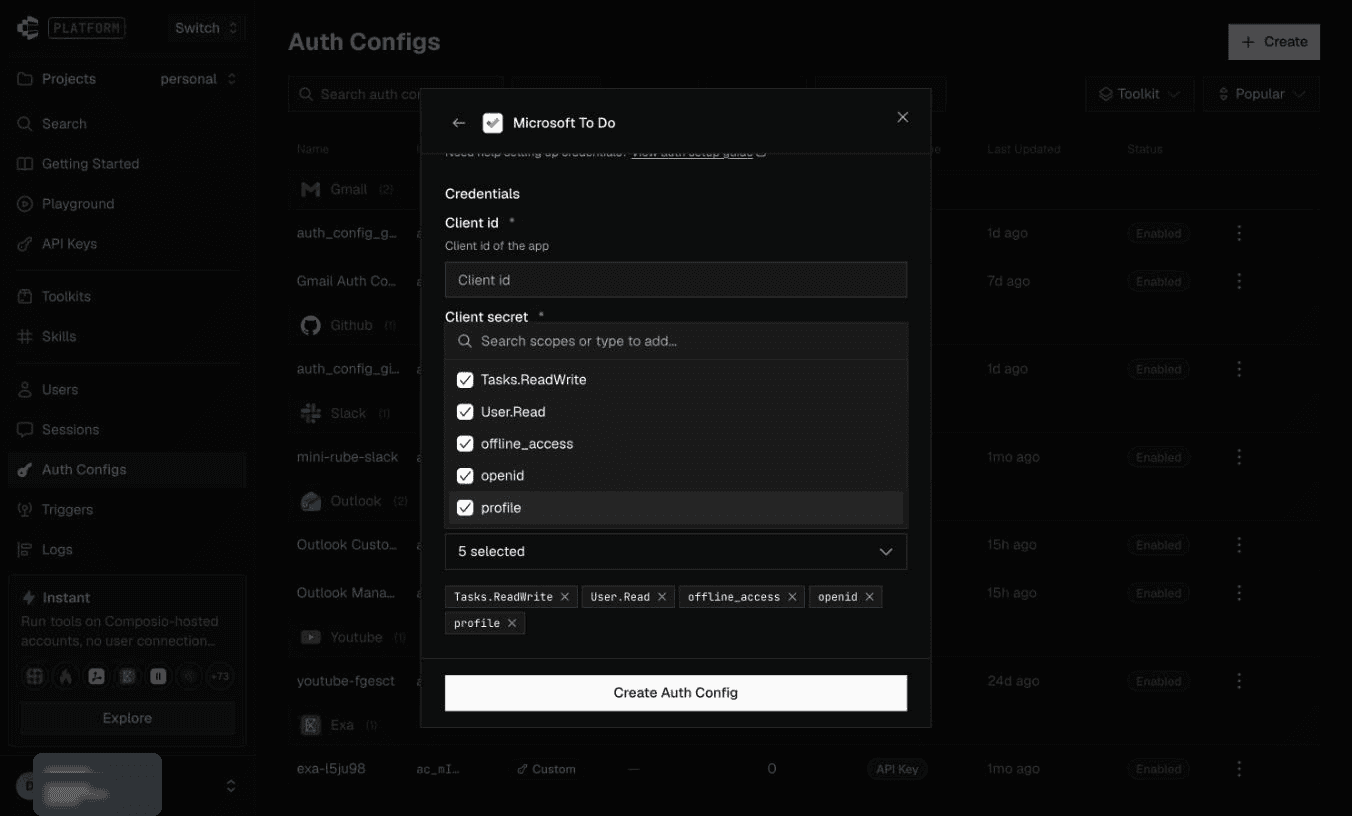
Permission reference. For updating tasks, the minimum delegated permission is Tasks.ReadWrite; read-only task access can use Tasks.Read. User.Read supports profile access and offline_access continued access. Choose for your own workflow; additional identity scopes shown are examples, not a required checklist. Microsoft permission reference.

4. Choose the delegated permissions needed for the operations your integration will use.
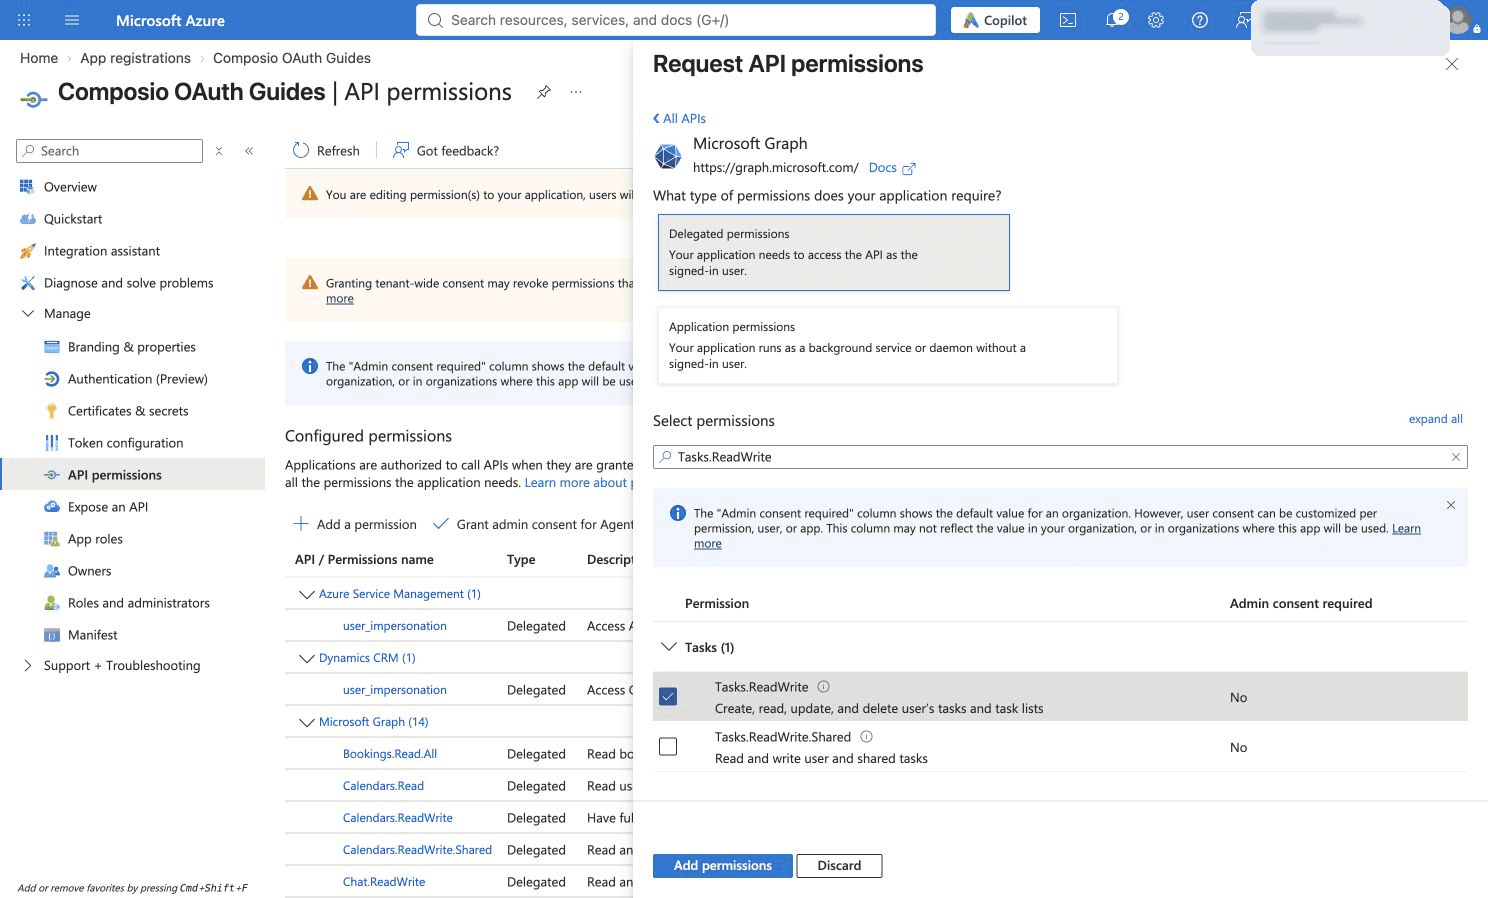
5. Choose the delegated permissions needed for the operations your integration will use. Then click Add permissions.

Part 2: Connect Microsoft To Do in Composio
Step 1: Create an auth config
1. In Composio, open Auth Configs and click Create.
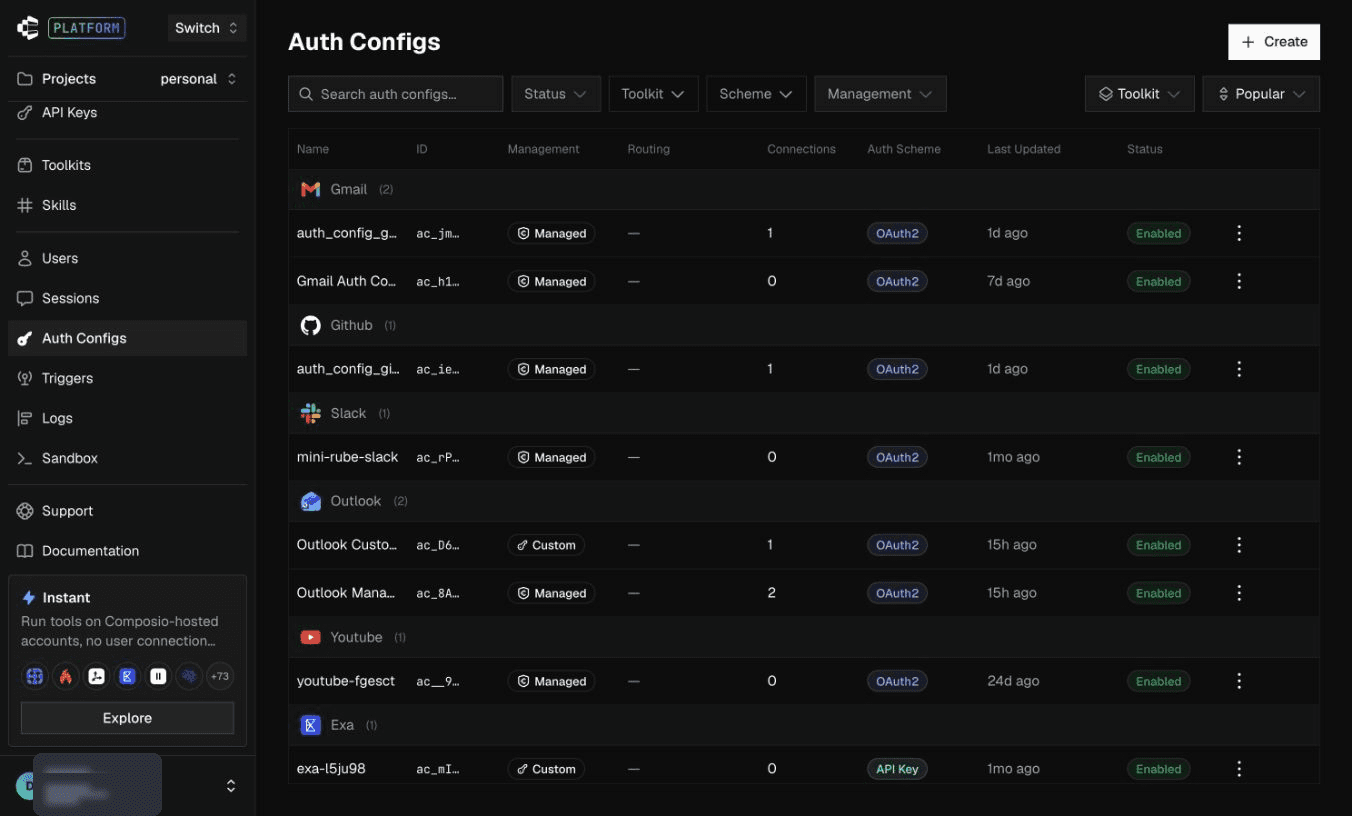
2. Search for and select Microsoft To Do.
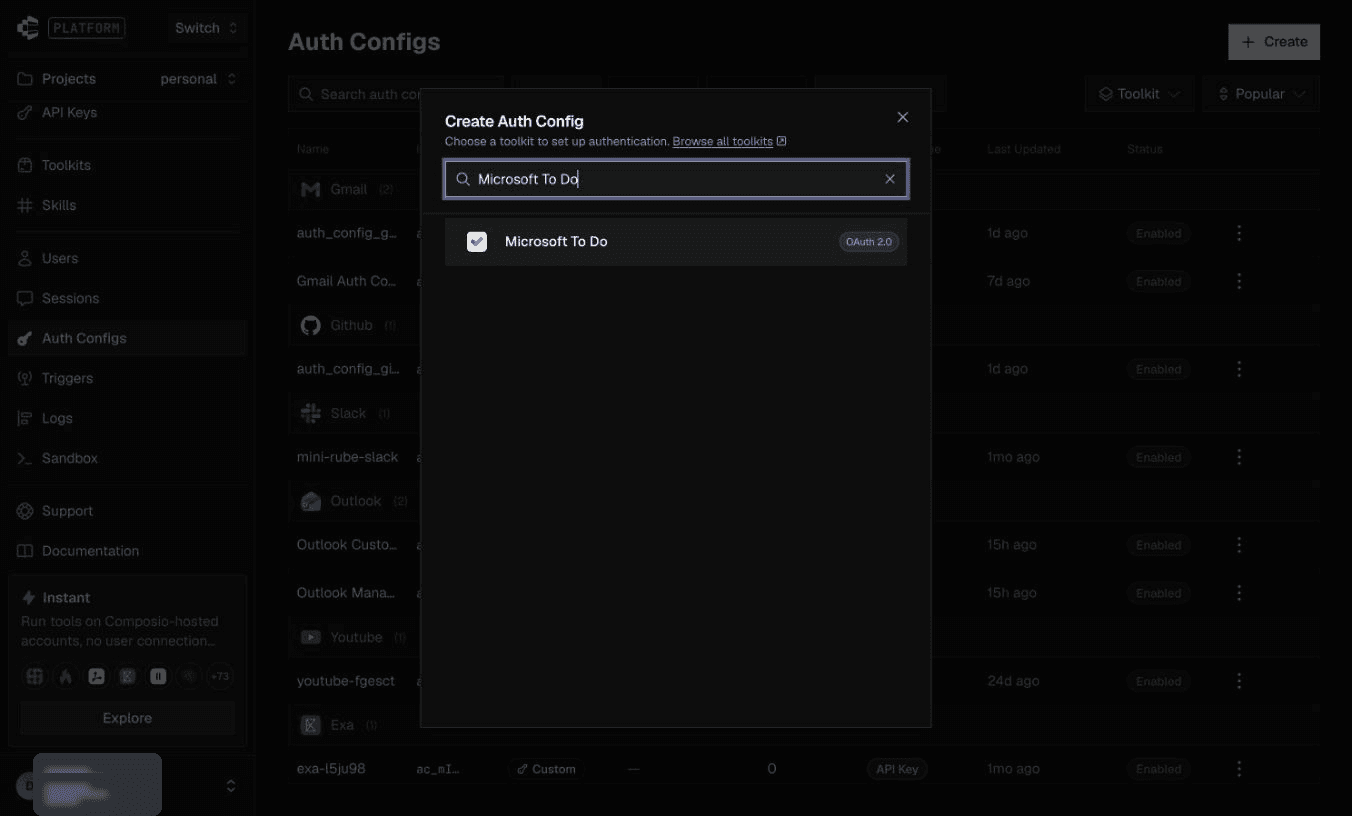
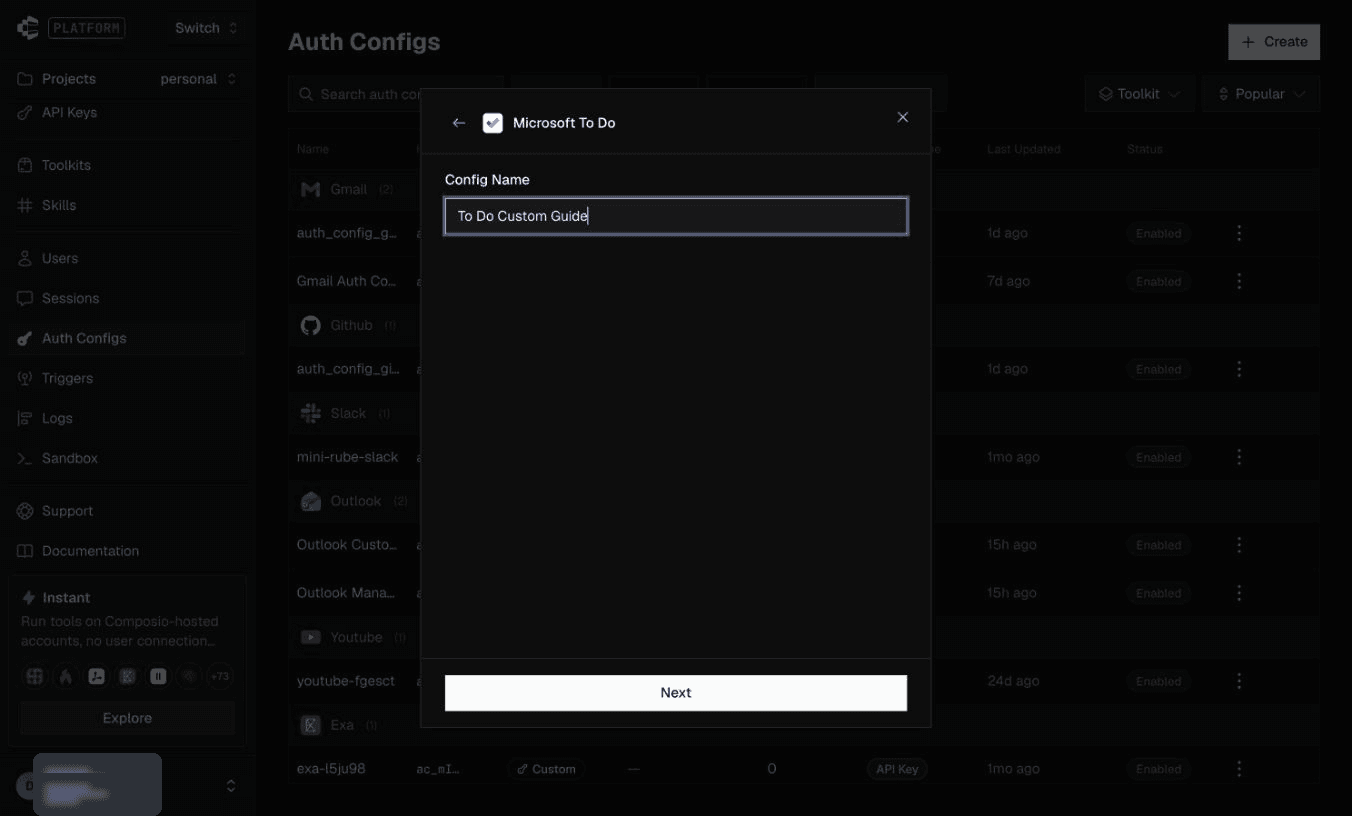
3. Enter a config name and click Next.
Step 2: Enter your OAuth credentials
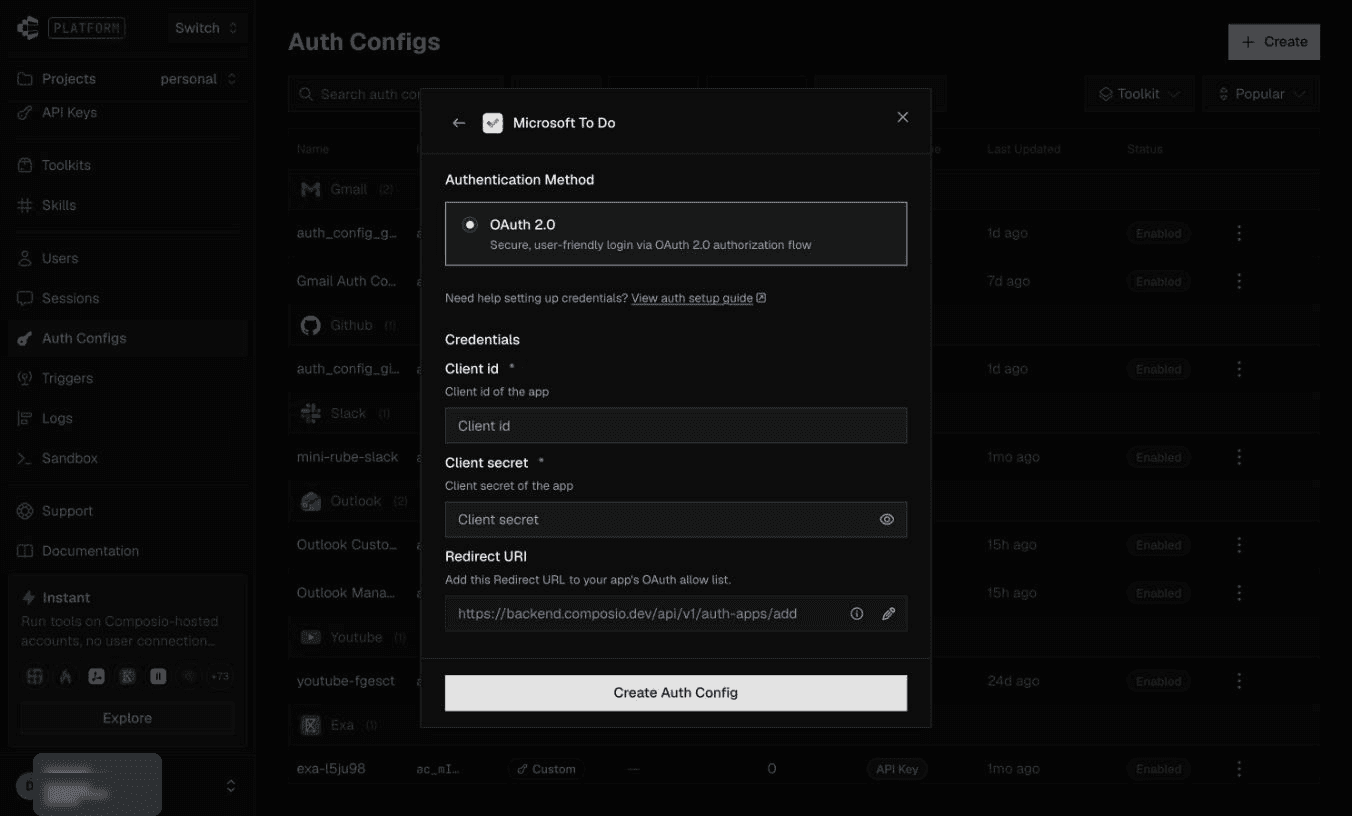
1. Choose OAuth 2.0. Enter your app’s Client id and client-secret Value. Keep the original redirect URI.
2. Under Scopes, choose permissions required by your integration and supported by your app registration. Click Create Auth Config.
Step 3: Connect your Microsoft account
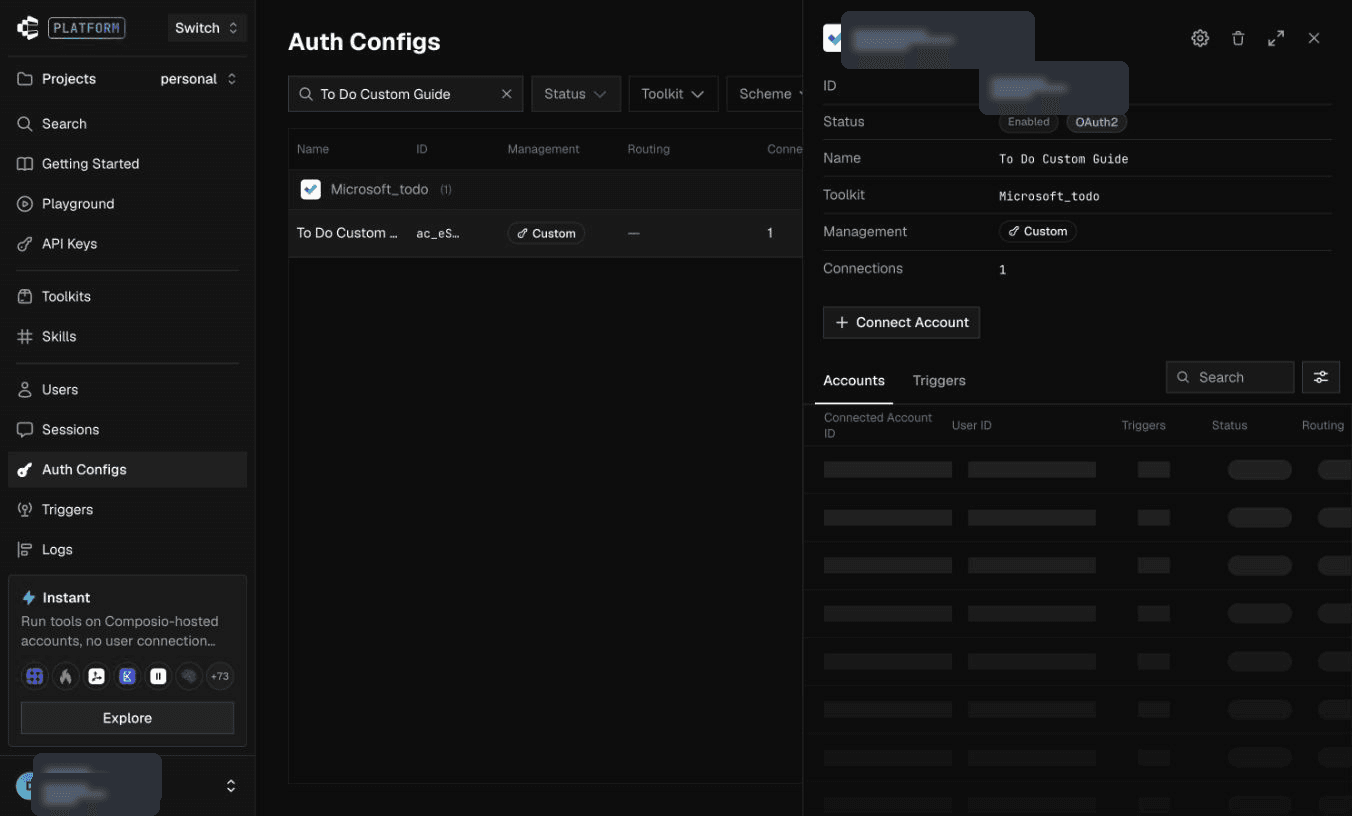
1. Open the auth config and click Connect Account.
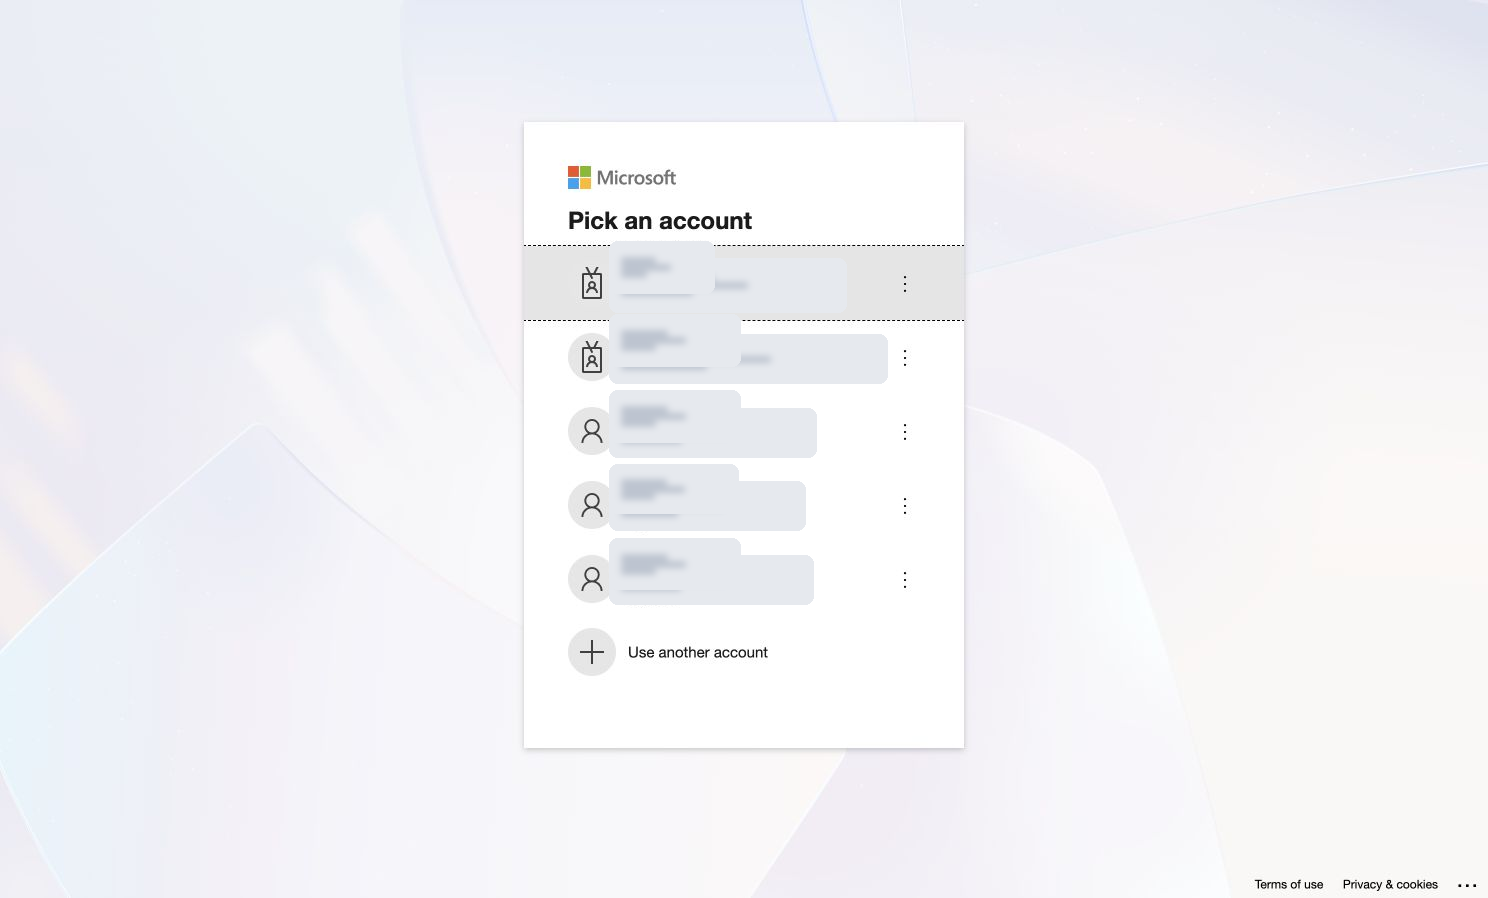
2. Sign in with the Microsoft account you use for To Do. Work, school and personal accounts are supported for this delegated flow.
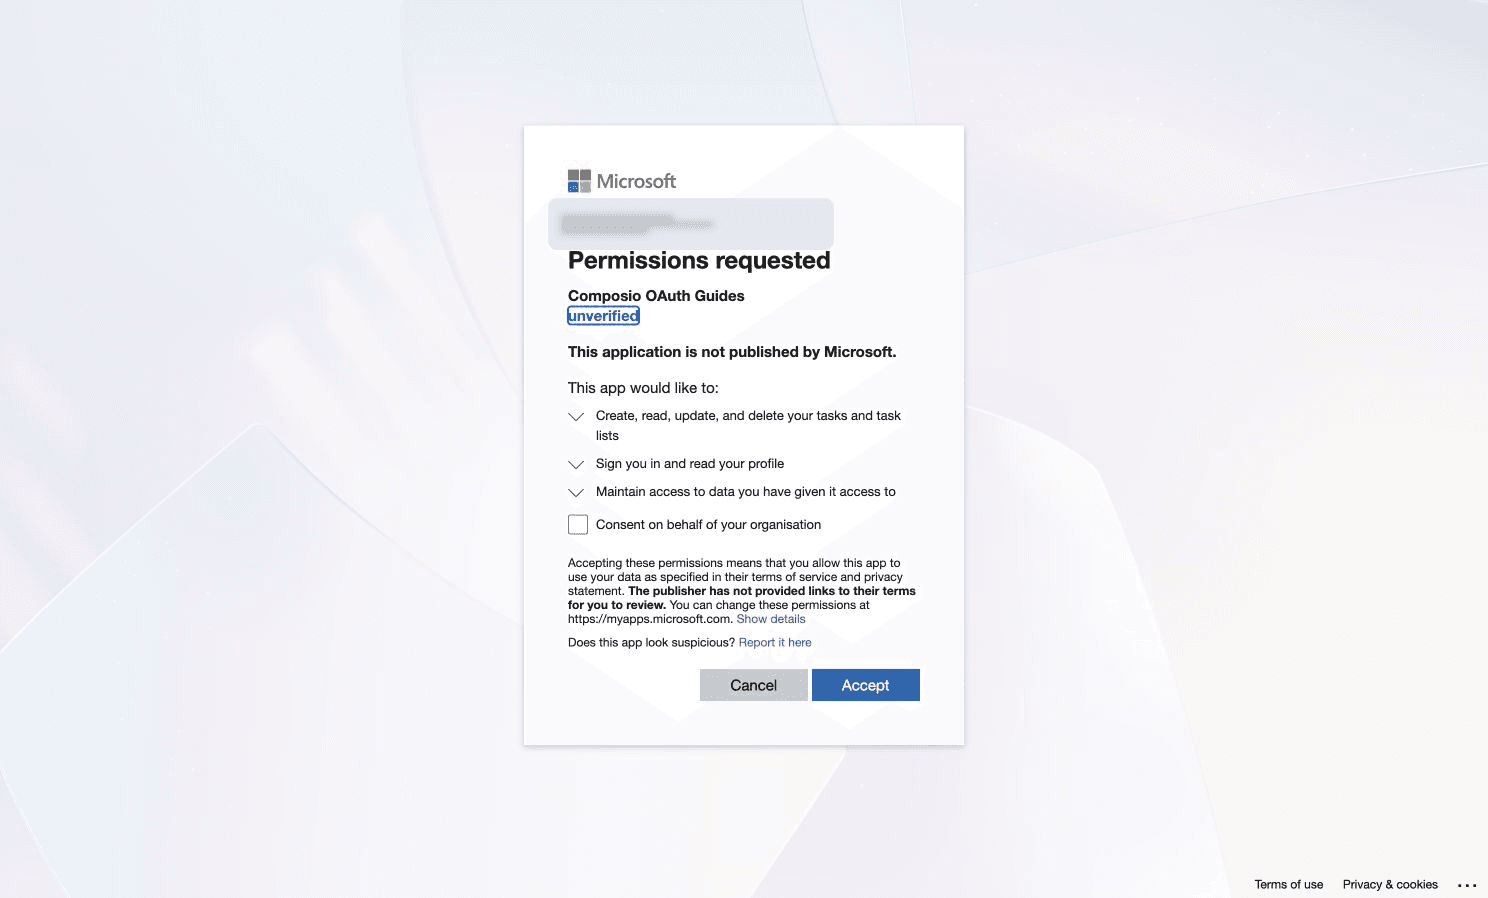
3. Review the app and requested task access, then click Accept. Leave organization-wide consent unchecked unless your administrator intends tenant-wide approval.
Step 4: Check the connection
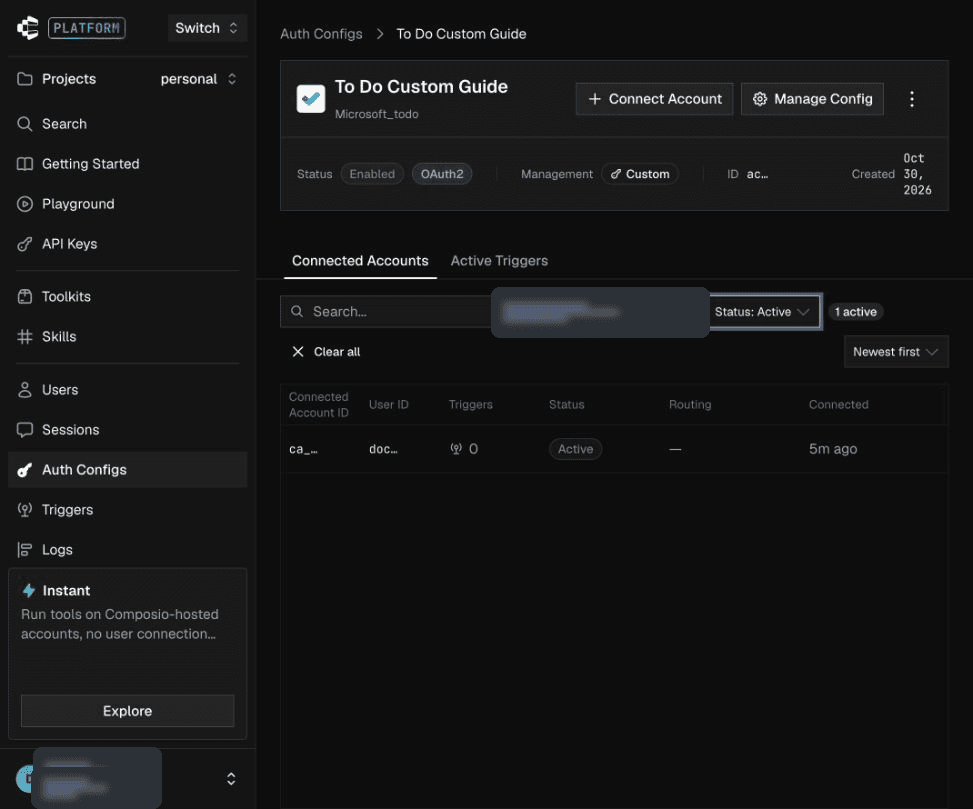
1. Return to the auth config’s Accounts tab and confirm the connected account shows Active. Copy the Auth Config ID for your application.