



Composio connects AI agents to Azure Monitor Activity Log so they can retrieve Azure subscription activity logs. Access is limited by the permissions you approve and your account’s existing access.
This guide shows you how to set up OAuth credentials and connect Azure Monitor Activity Log to Composio.
Part 1: Create Your Microsoft Entra OAuth App
Step 1: Register the App
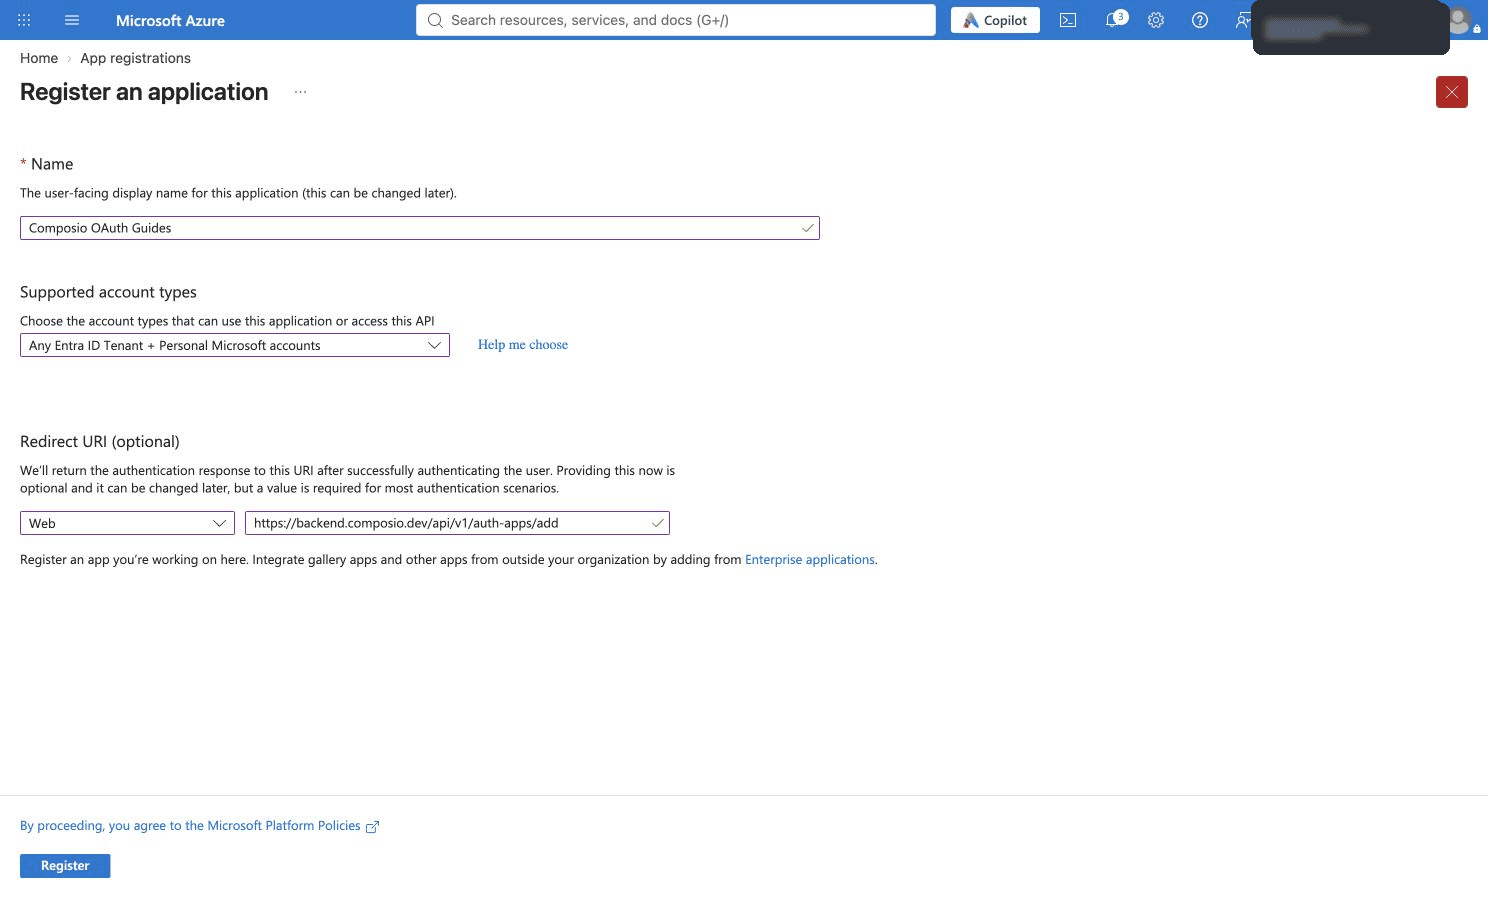
1. Sign in to the Azure portal, open App registrations and click New registration. Enter a descriptive name, such as Composio OAuth Guides. For the illustrated common sign-in flow, choose an organizational account audience that allows the intended Azure tenant. The shared QA screenshot also allows personal accounts for other Microsoft guides.
2. Select the Web platform and enter Composio’s original callback exactly, then click Register.
https://backend.composio.dev/api/v1/auth-apps/add
Step 2: Copy the Client ID and Create a Client Secret
1. On Overview, copy the Application (client) ID. You will enter it as Client id in Composio.

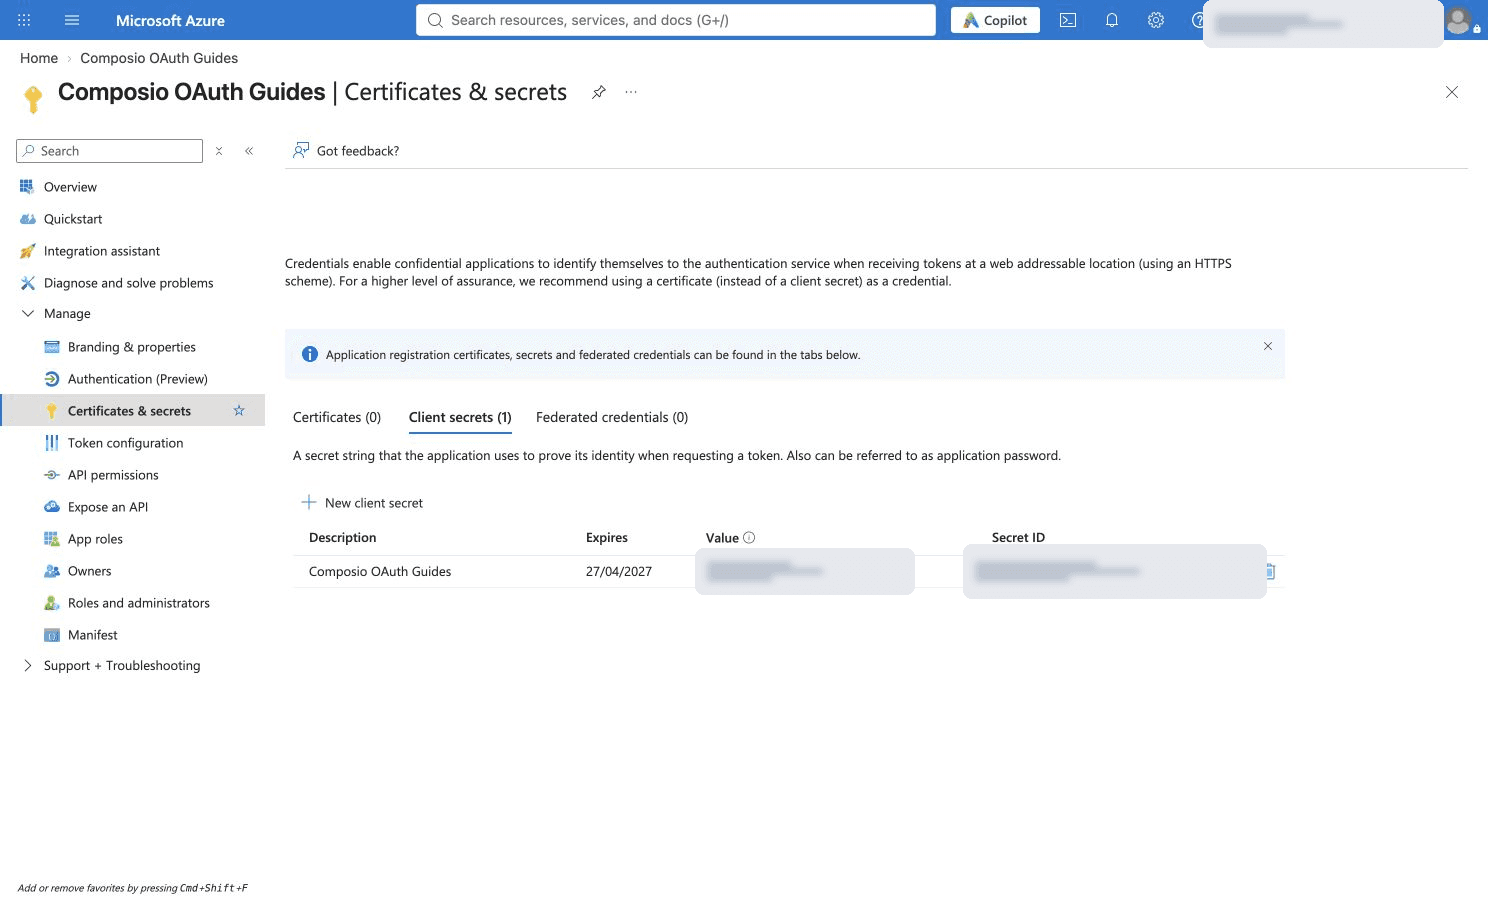
2. Open Certificates & secrets and click New client secret.
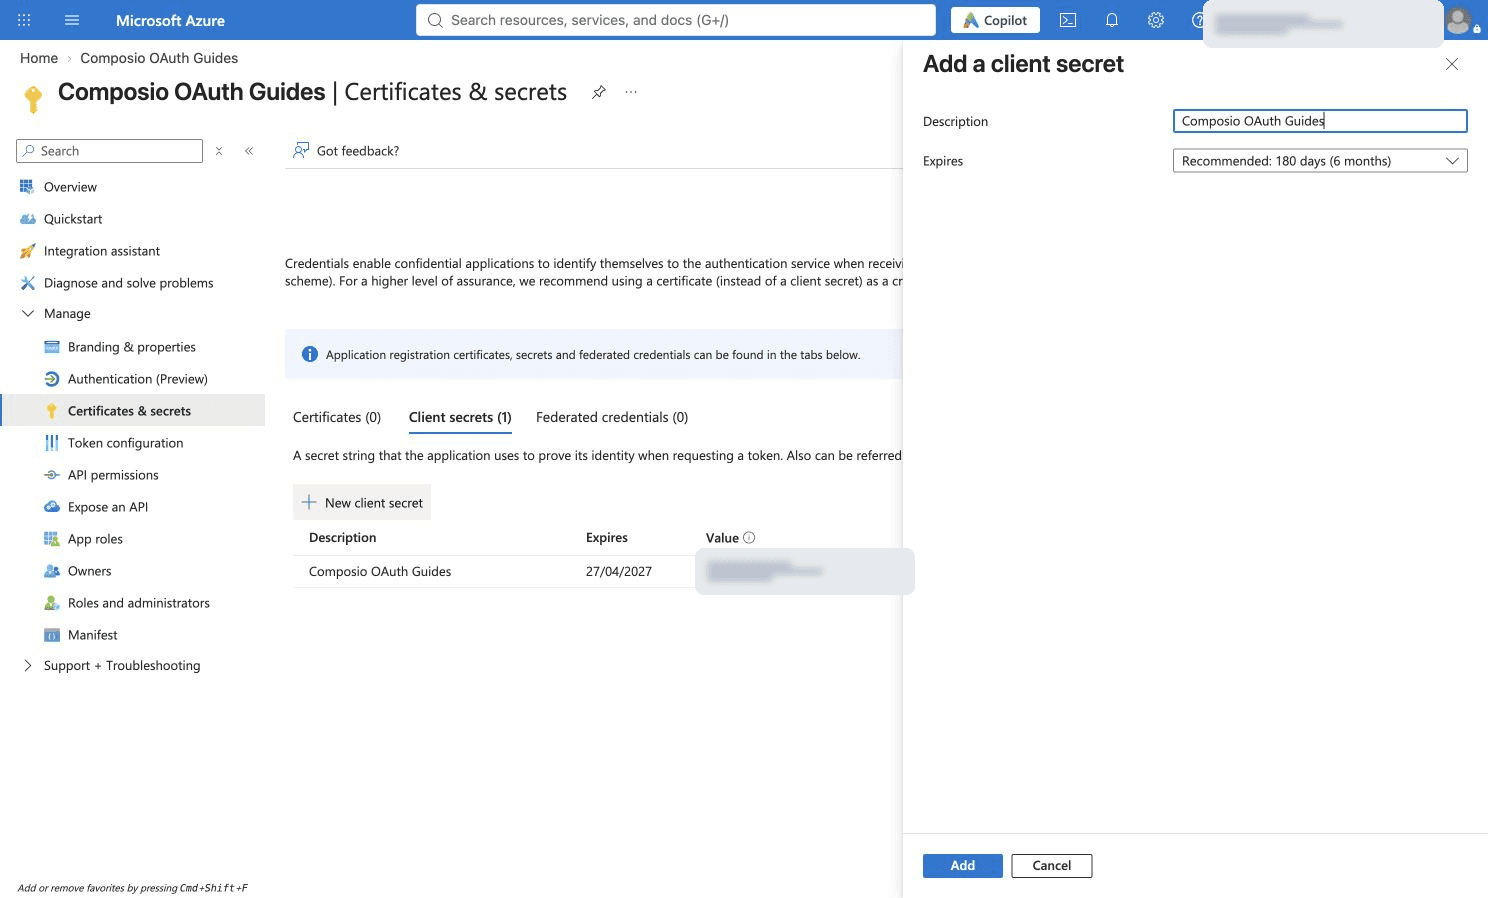
3. Add a description, choose an expiry that fits your rotation policy and click Add. The example uses 180 days. Rotate the secret before expiry.
4. Copy the secret Value immediately and store it privately. Use the Value, not the Secret ID. Azure does not reveal the full Value on later visits. The screenshot censors the entire Value field. Keep public client flows disabled for this confidential Web client.

Step 3: Add Azure Service Management Permissions
1. Open API permissions and click Add a permission.
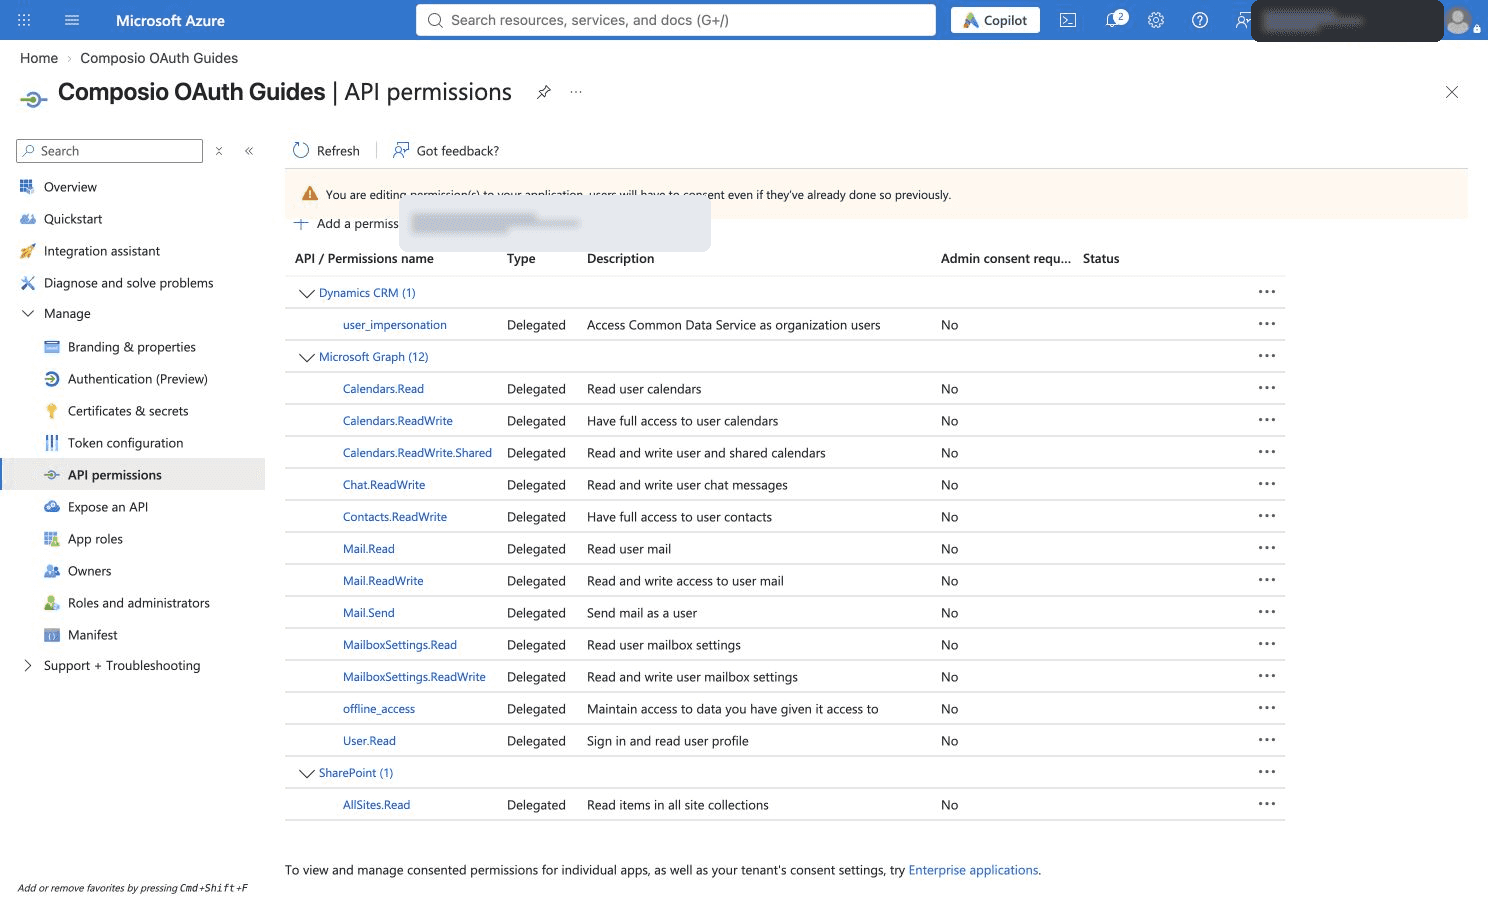
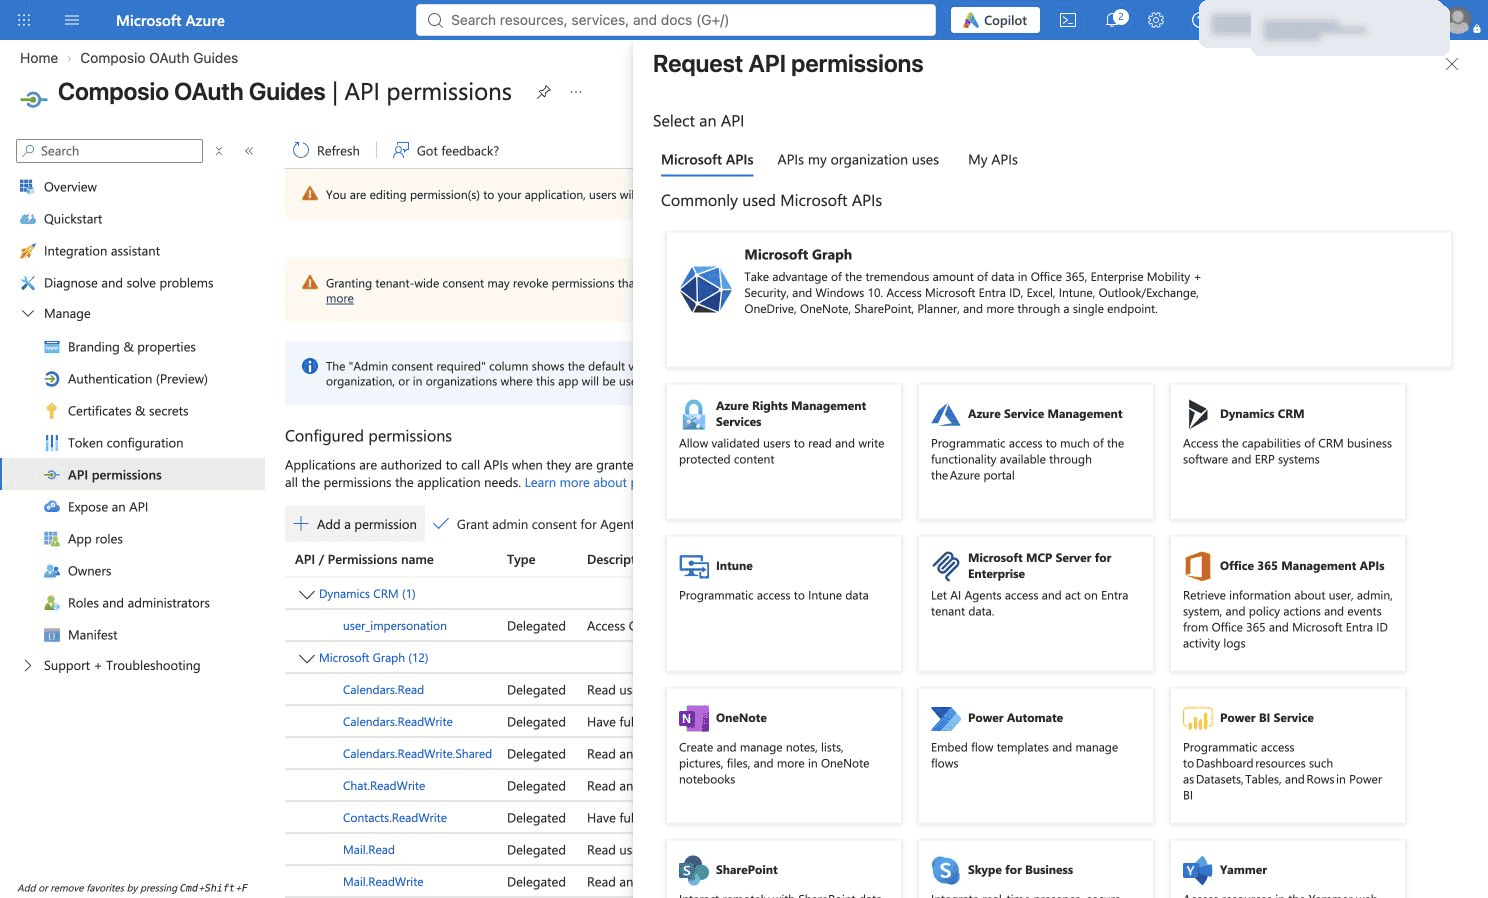
2. Select Azure Service Management under Microsoft APIs.
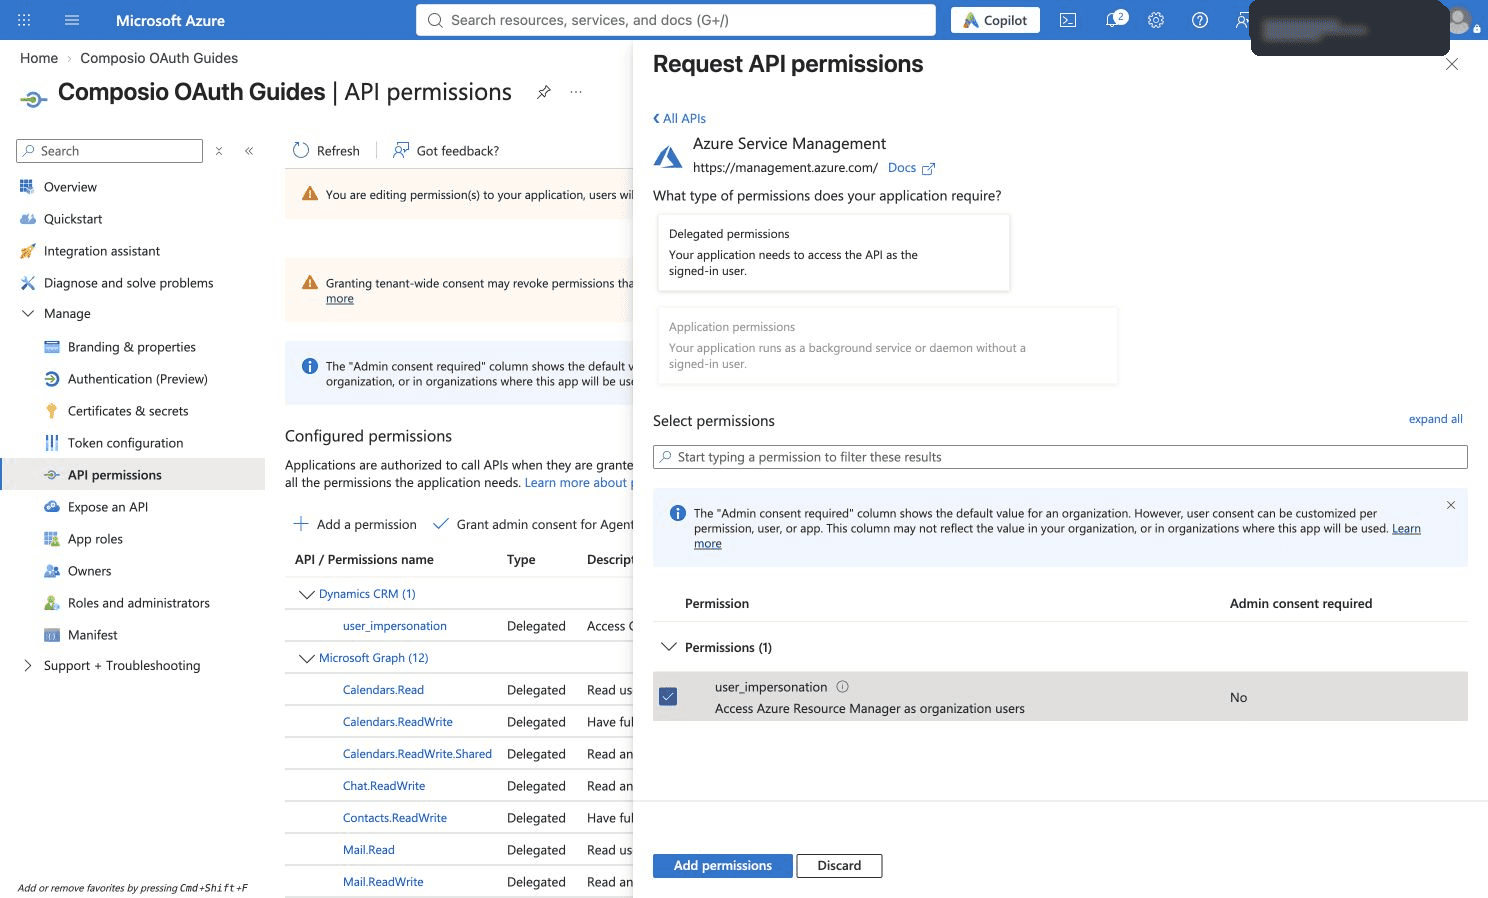
3. Choose Delegated permissions. Choose the delegated permissions needed for the operations your integration will use. Then click Add permissions.
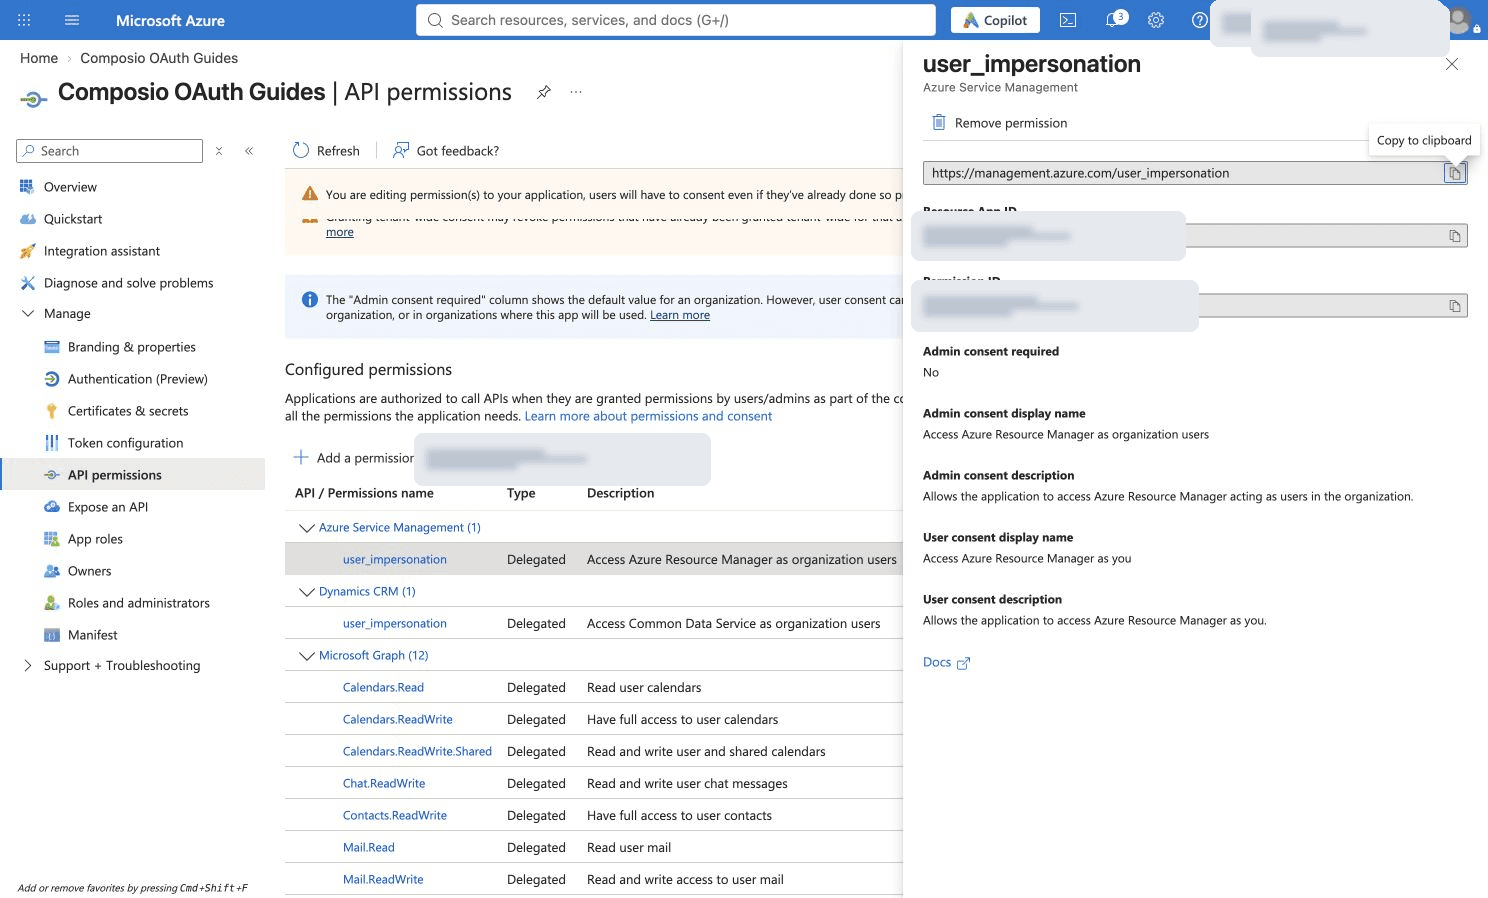
Permission reference. Activity Log access uses the Azure Resource Manager delegated permission user_impersonation. The request uses https://management.azure.com/user_impersonation; offline_access supports continued access. Azure roles still control access to subscription logs. Choose permissions for your workflow; the screenshots are examples. Microsoft permission reference.
4. Review the configured permission. It allows the app to act with the signed-in account’s existing Azure permissions. It does not create a log-reading role or limit an account’s broader Azure rights to Activity Log reads. Use an account with permissions suited to the integration. Tenant policy may require administrator approval.
Part 2: Connect Azure Monitor Activity Log in Composio
Step 1: Copy the Azure Subscription ID
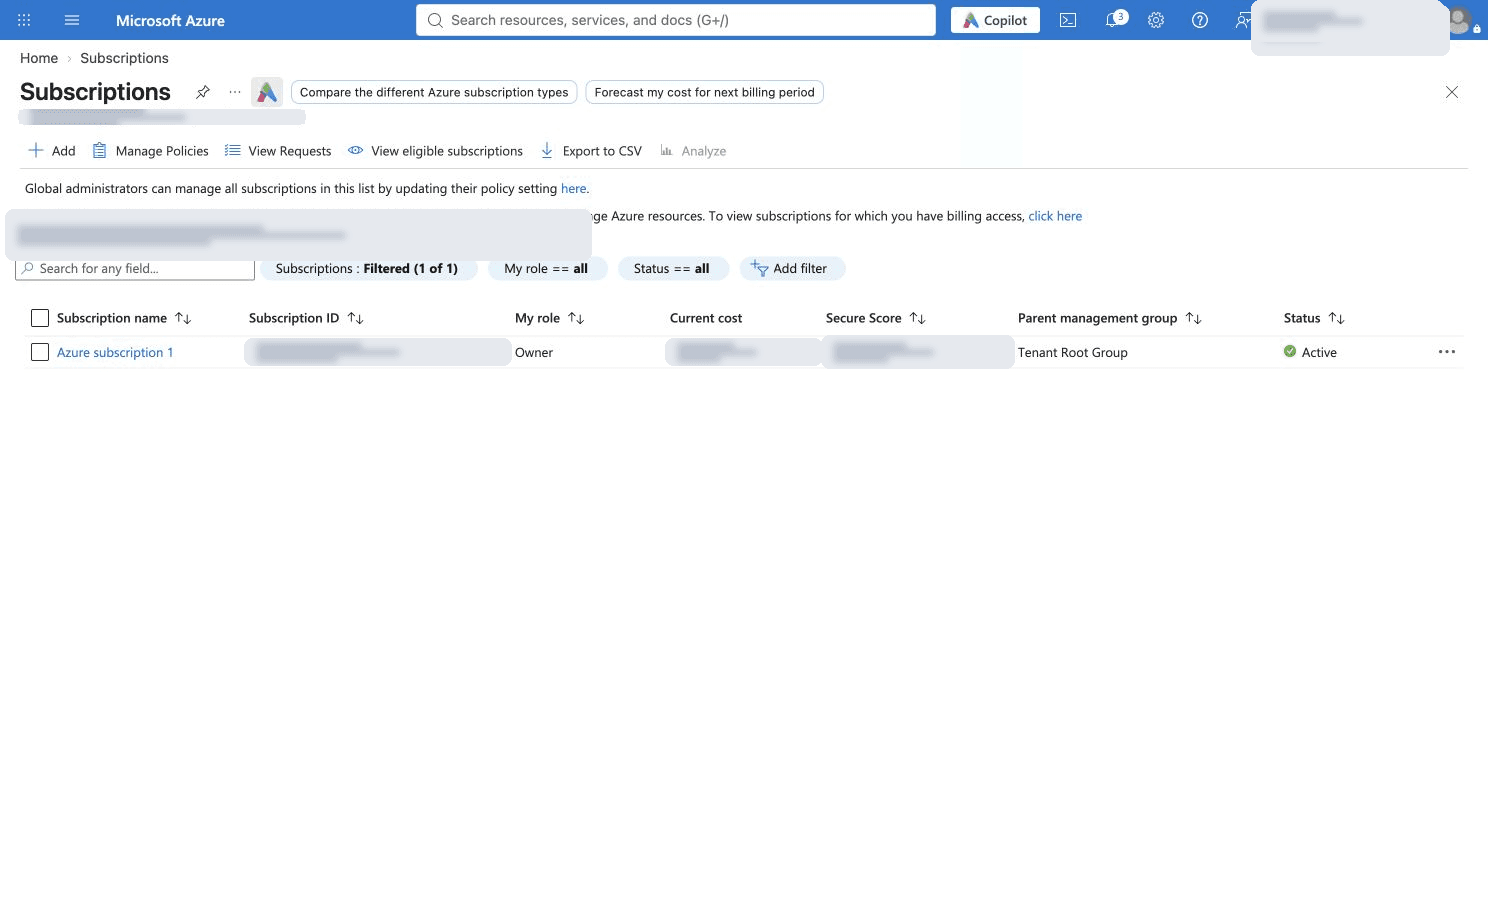
1. In the Azure portal, open Subscriptions and identify the subscription whose Activity Log you want to use. Copy its Subscription ID from the list, or select the subscription and copy it from Overview. Use an account with Activity Log read access, such as Monitoring Reader. The screenshot censors that ID, billing figures and the security score.
Step 2: Create an Auth Config
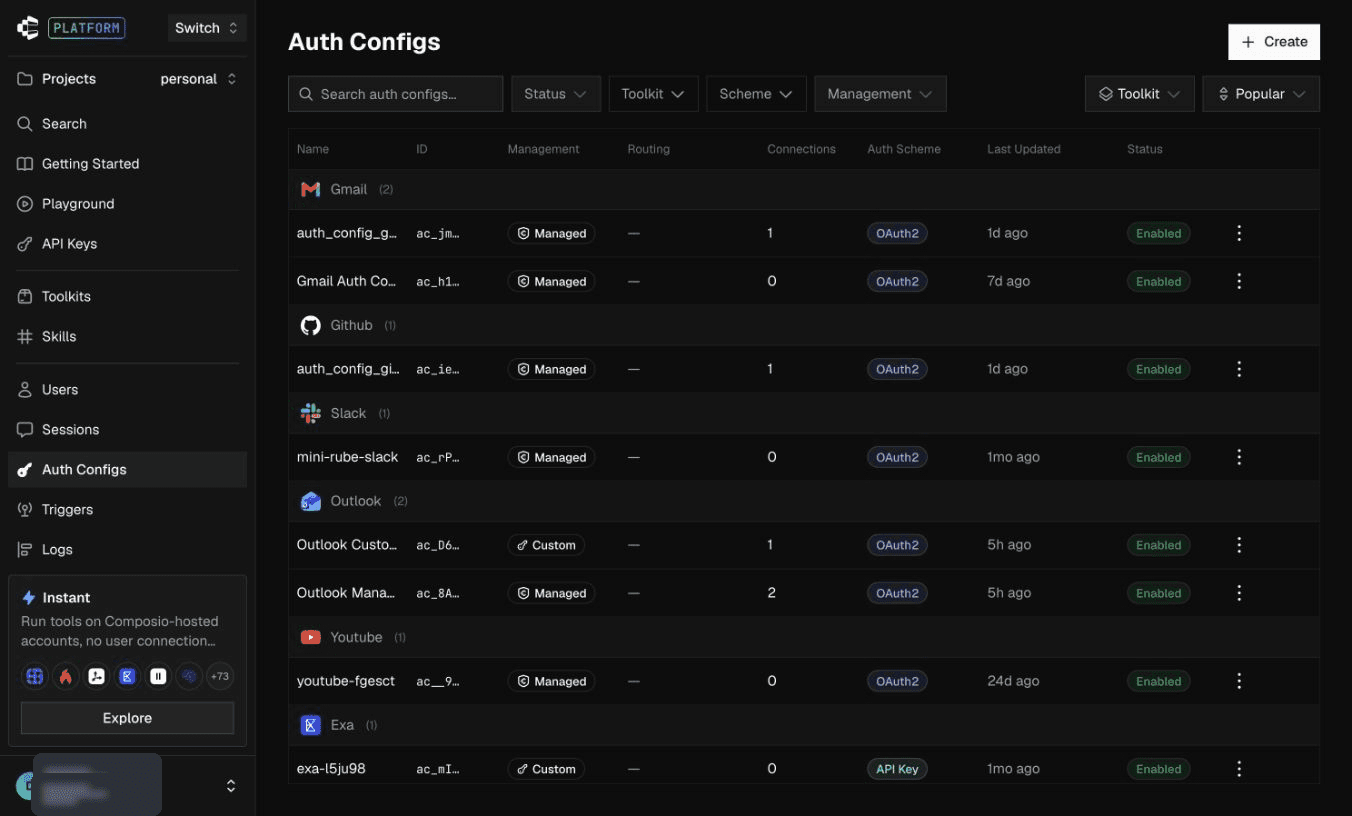
1. Open the Composio platform, go to Auth Configs and click Create.
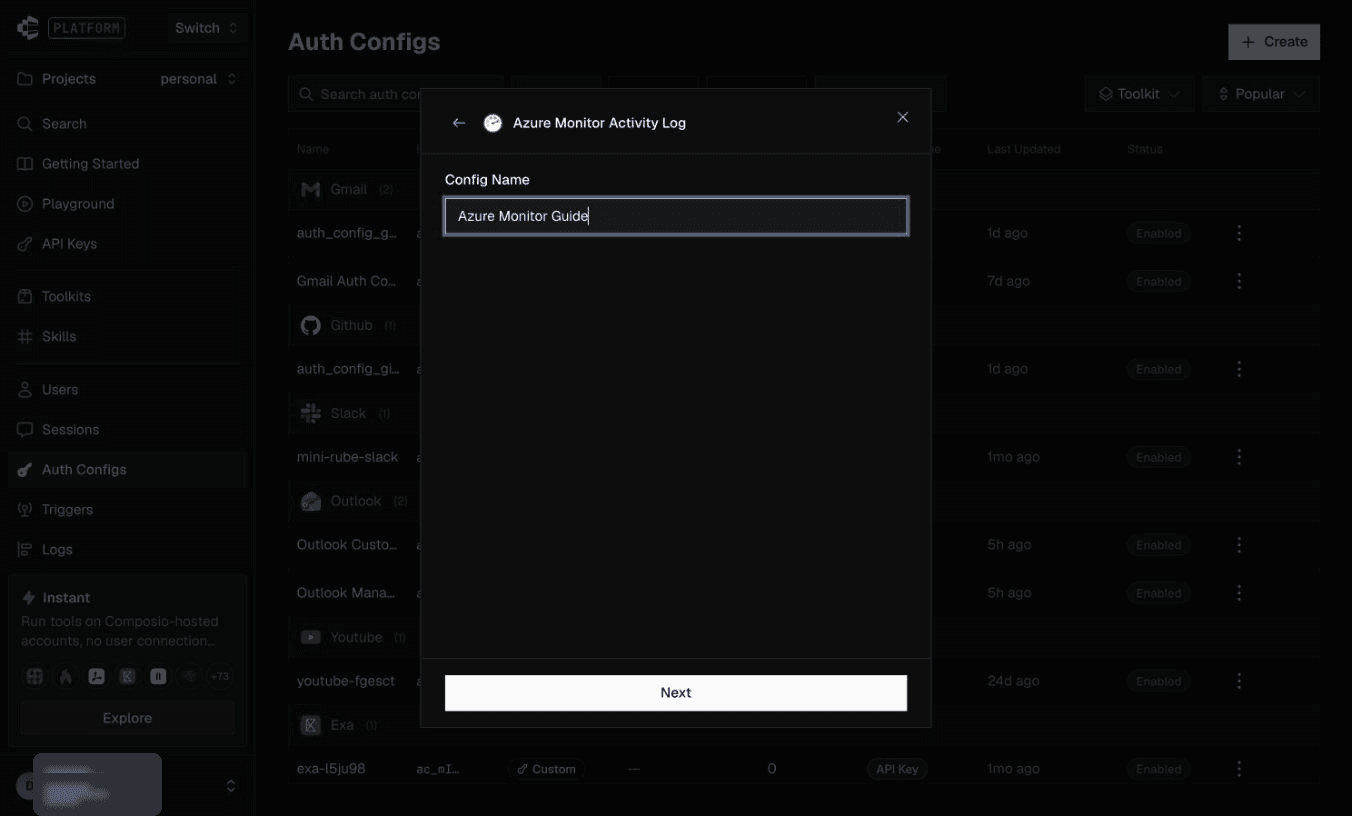
2. Search for and select Azure Monitor Activity Log.

3. Enter a Config Name, such as Azure Monitor Guide, and click Next.
Step 3: Enter Your OAuth Credentials
1. Select OAuth 2.0. Enter your app’s Client id and client-secret Value. These inputs are intentionally empty in the screenshot for privacy.
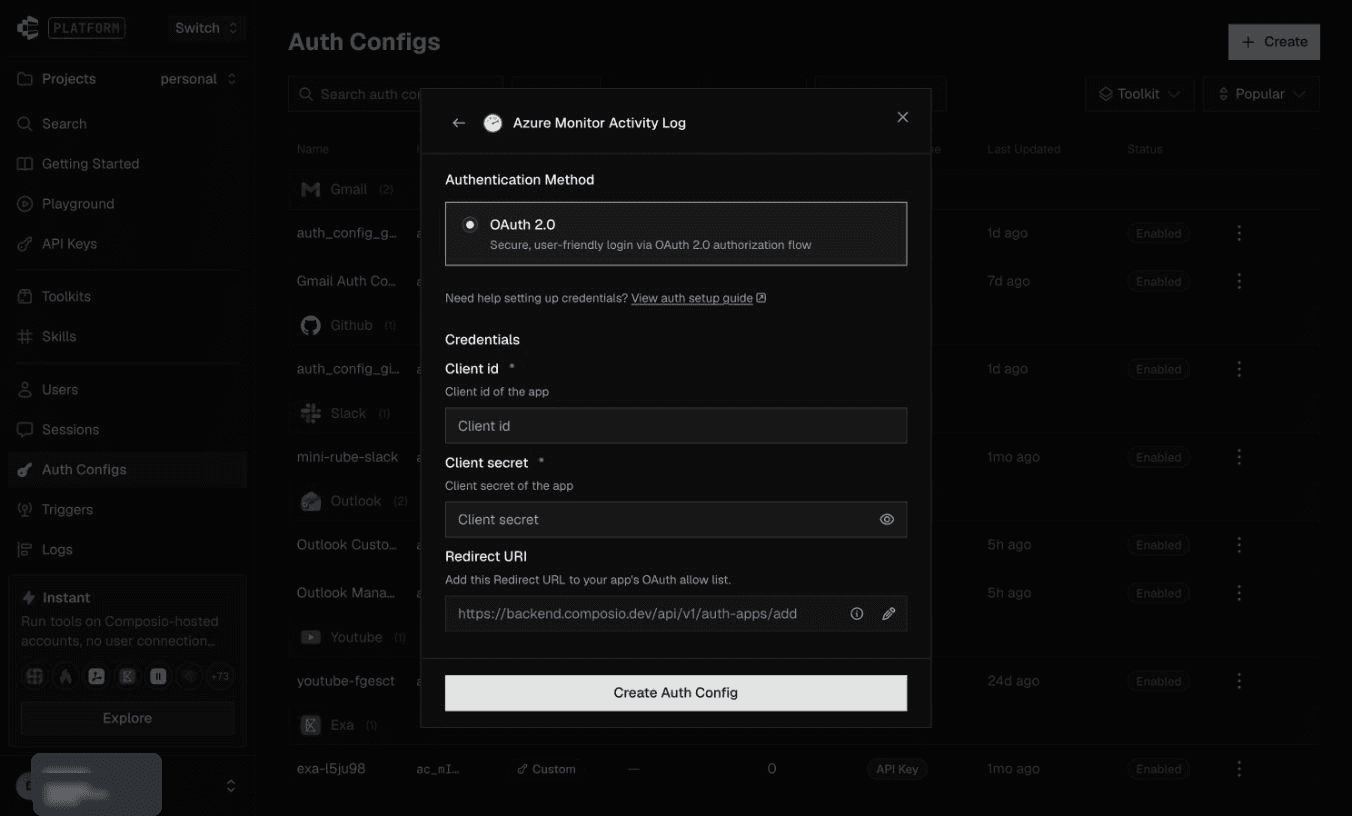
2. Keep the Redirect URI identical to the registered Web callback. Under Scopes, choose permissions required by your integration and supported by your app registration. Click Create Auth Config.
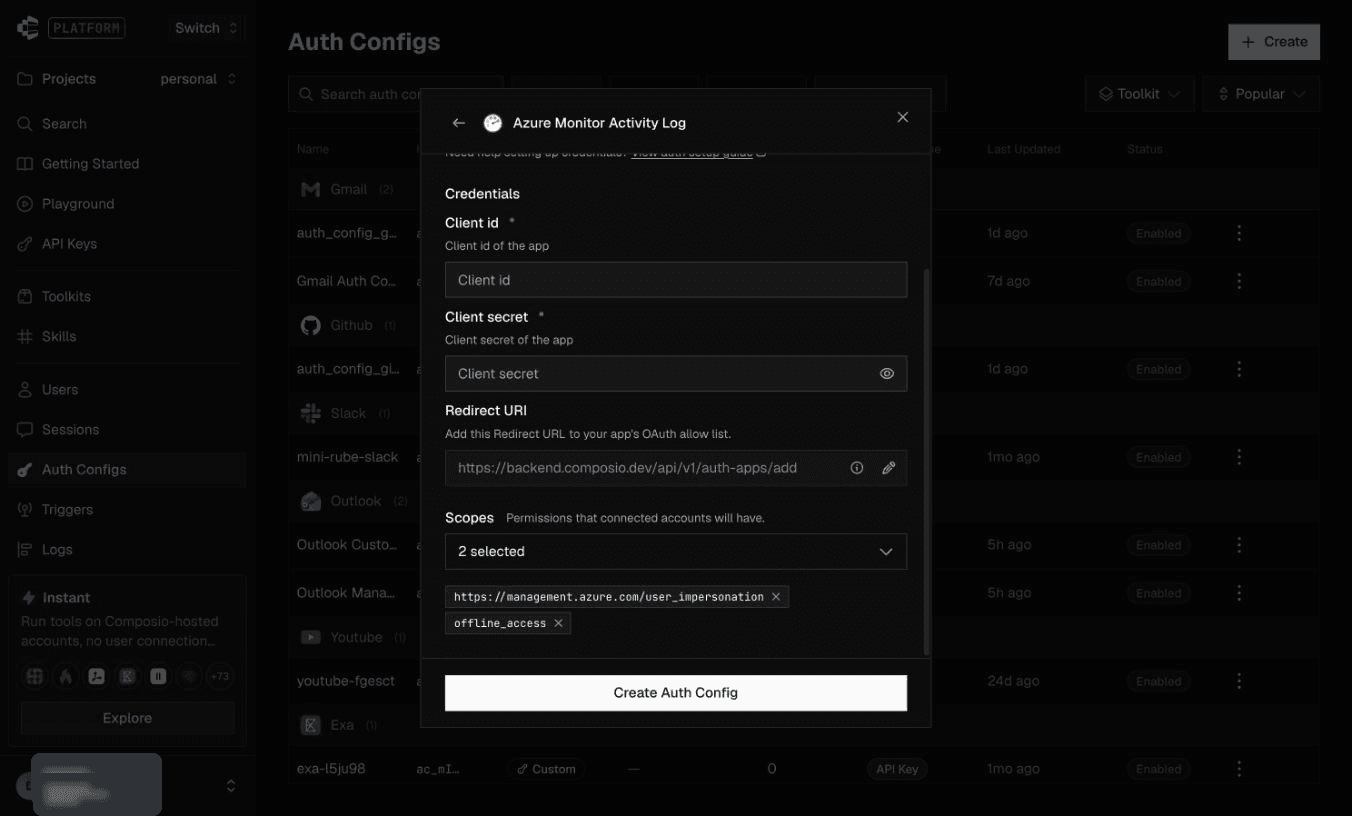
Step 4: Connect the Subscription
1. Open the auth config and click Connect Account.
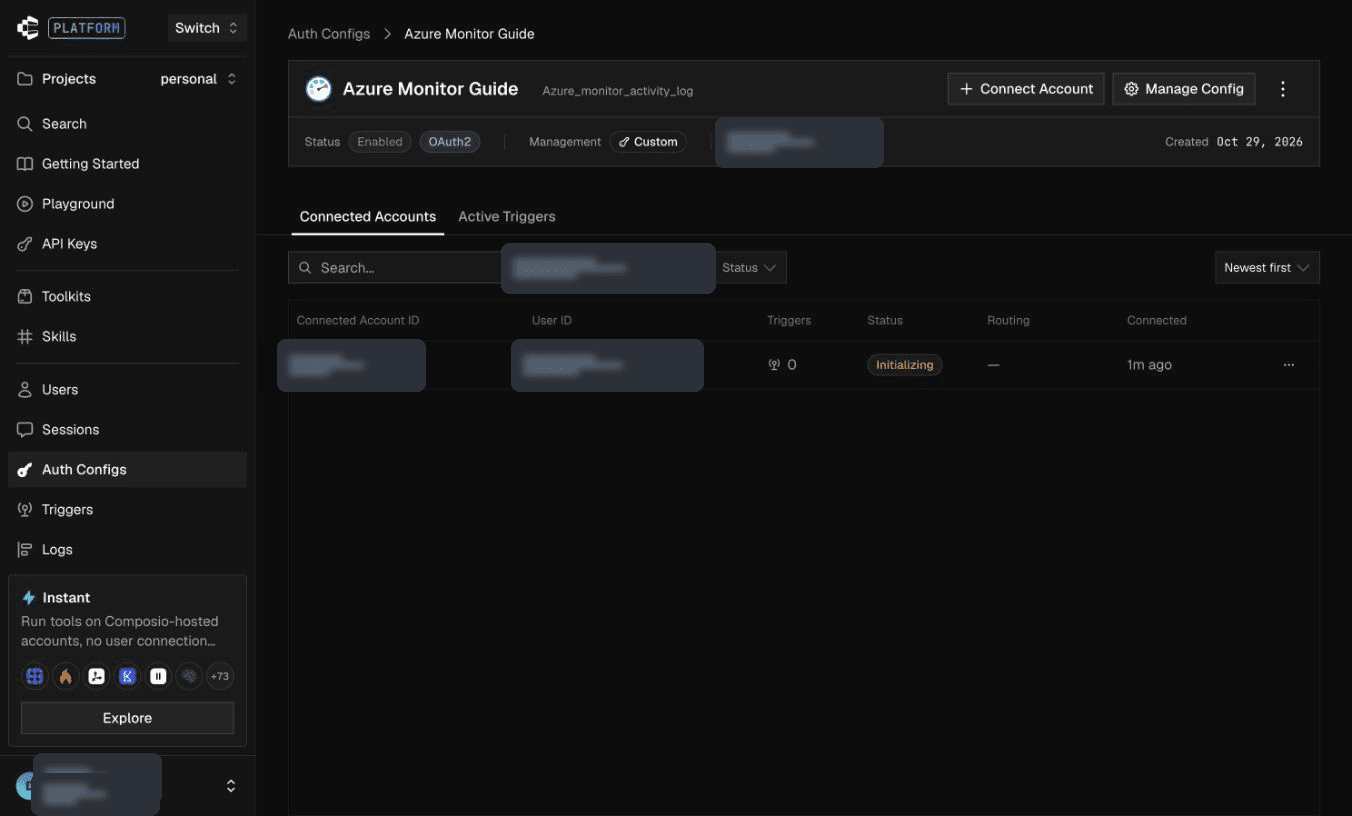
2. Paste the subscription GUID you copied in Step 1 into Azure Subscription ID, then click Connect Account. The Microsoft account you select next must have Activity Log read permission on that subscription.
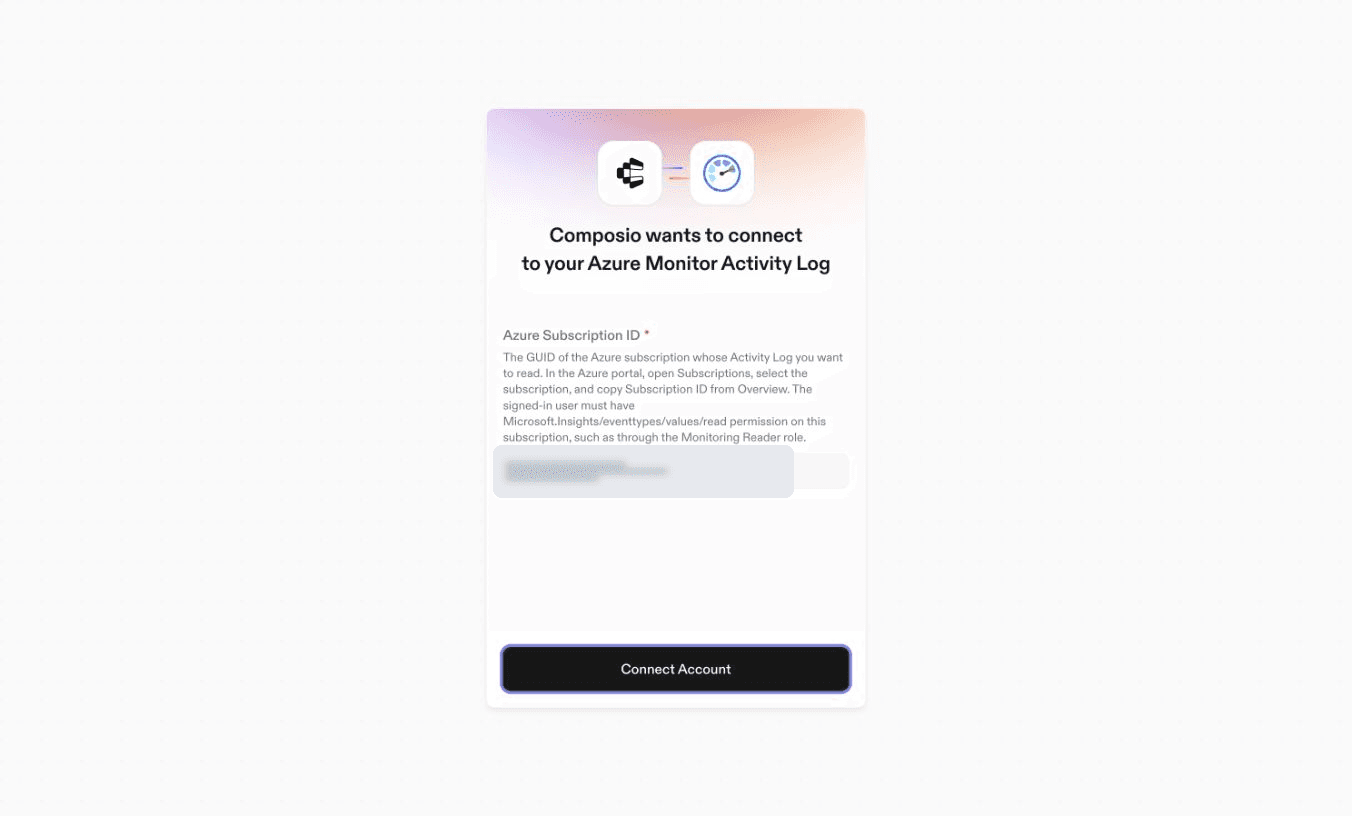
Step 5: Sign in and Review Permissions
1. Select the Microsoft account with the required subscription access and sign in.

2. Review the app name and Azure Resource Manager access, then click Accept if approved. Leave organization-wide consent unchecked unless an administrator intends tenant-wide approval.
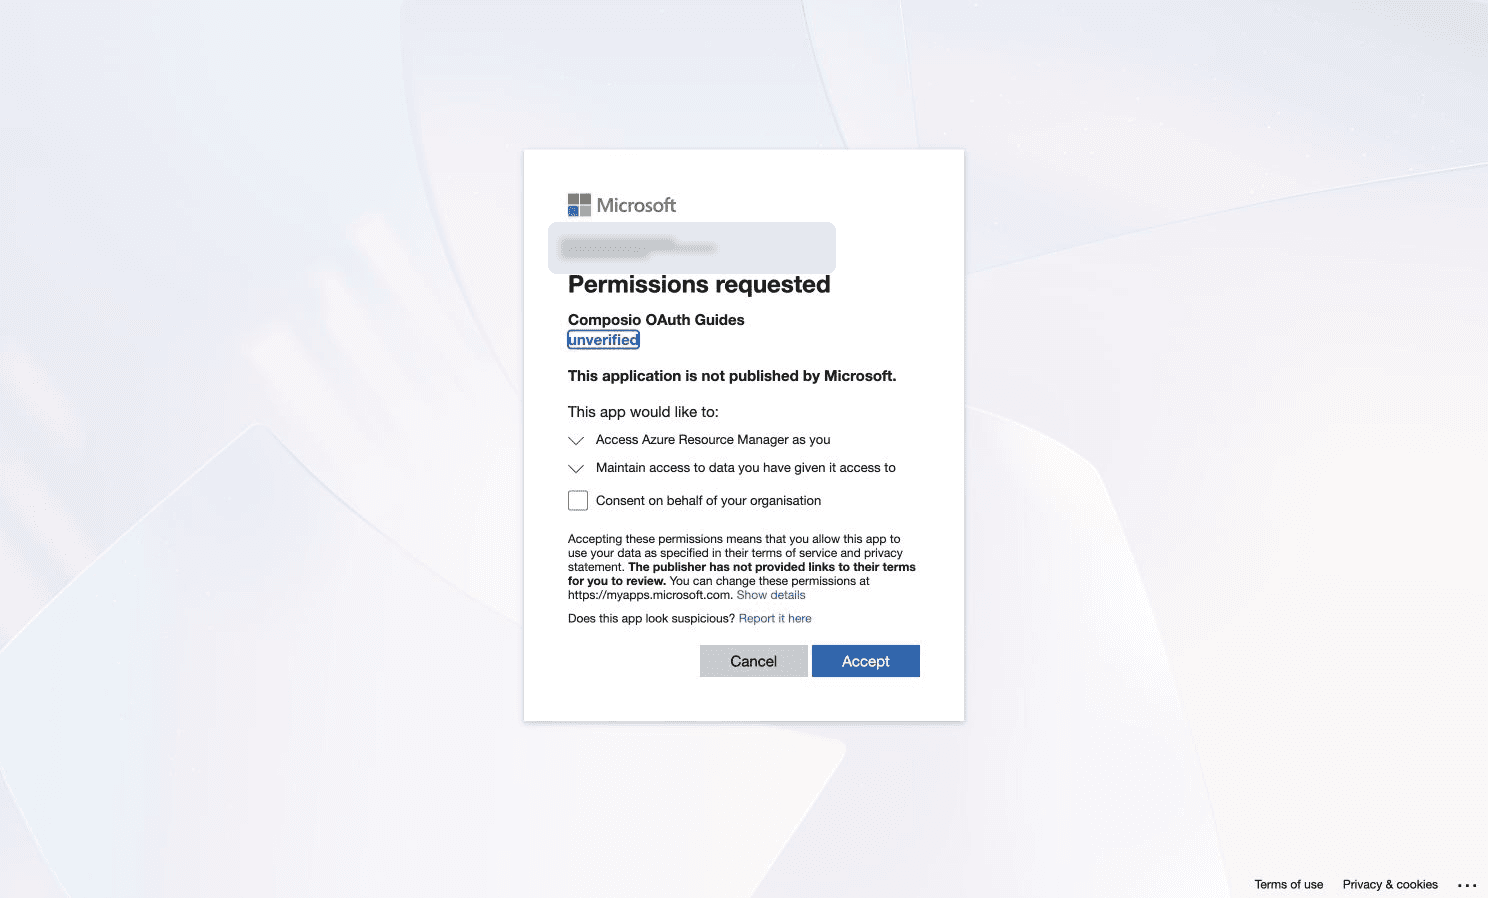
3. Wait for Composio’s successful connection page.

Step 6: Confirm the Connected Account Is Active
1. Return to the auth config’s Connected Accounts tab and check Active on the account row. The auth config’s Enabled state is separate. Azure RBAC continues to determine which subscription logs the account can read.
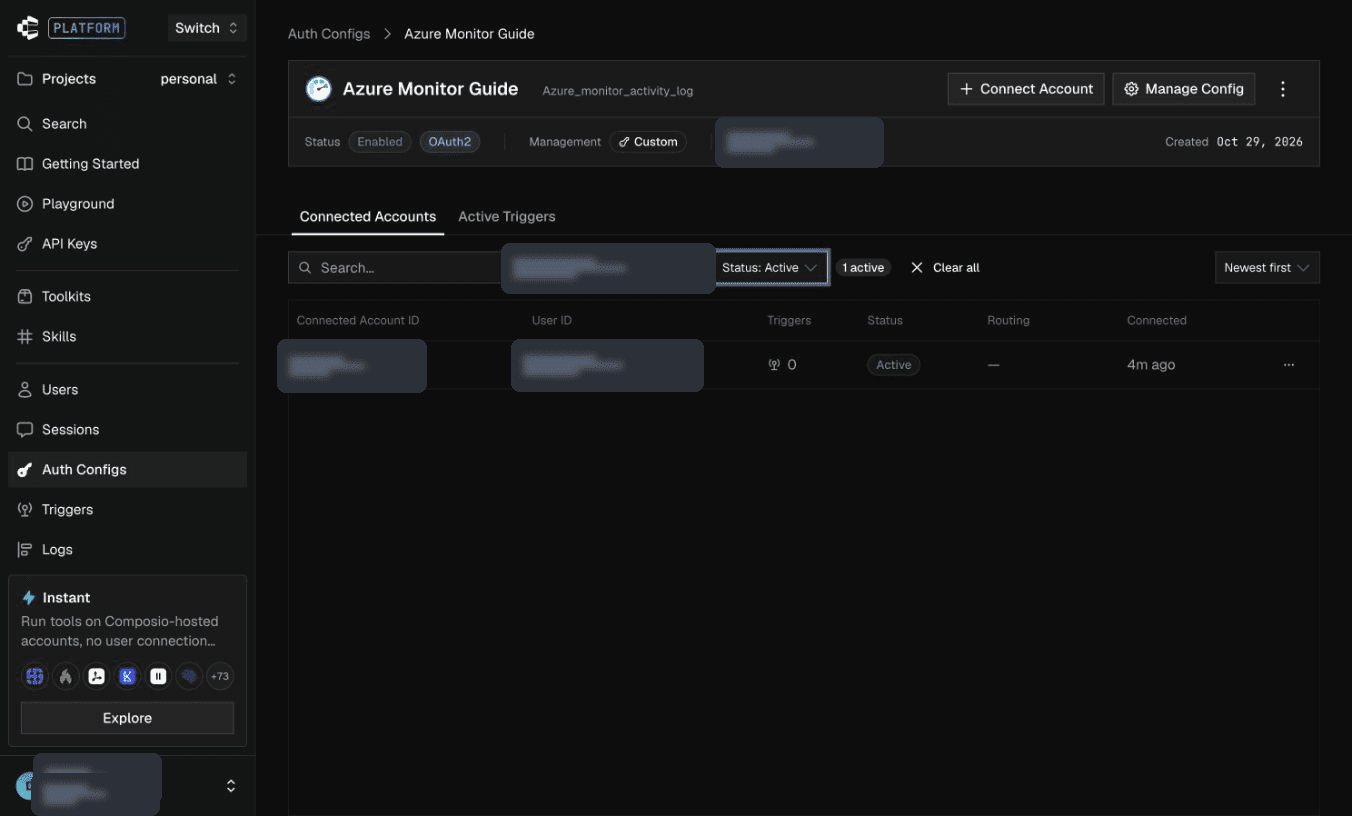
Copy the Auth Config ID from Composio and use it in your application’s integration setup.